
FlowName
 123wwwa/flowname
Next-generation JavaScript identifier recovery with LLMs.
ai-assisted-reversingai-securitycode-analysis+3
123wwwa/flownameNext-generation JavaScript identifier recovery with LLMs.
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
 rin449/bhpai
Multi-format malware analysis platform combining a stealth Ring-3 Windows sandbox, static PE/PDF analyzers, ransomware key recovery, and an AI…
 mandiant/stringsifter
A machine learning tool that ranks strings based on their relevance for malware analysis.
 neuromancer/rats-re
Reconstructs legacy Windows binaries into C source by pairing Ghidra decompiler exports with local LLMs, producing compile-checked candidates and…
 hydradragonantivirus/hydradragonav-mobile
Android Antivirus which doesn't require root, adb, ca install and cloud with many features and ways to detect more zero-day malware
 c3rb3ru5d3d53c/binlex
A Binary Genetic Traits Lexer Framework
 jhuapl/codecut
A Ghidra plugin for locating object file boundaries.
 google/oss-fuzz-gen
LLM powered fuzzing via OSS-Fuzz.
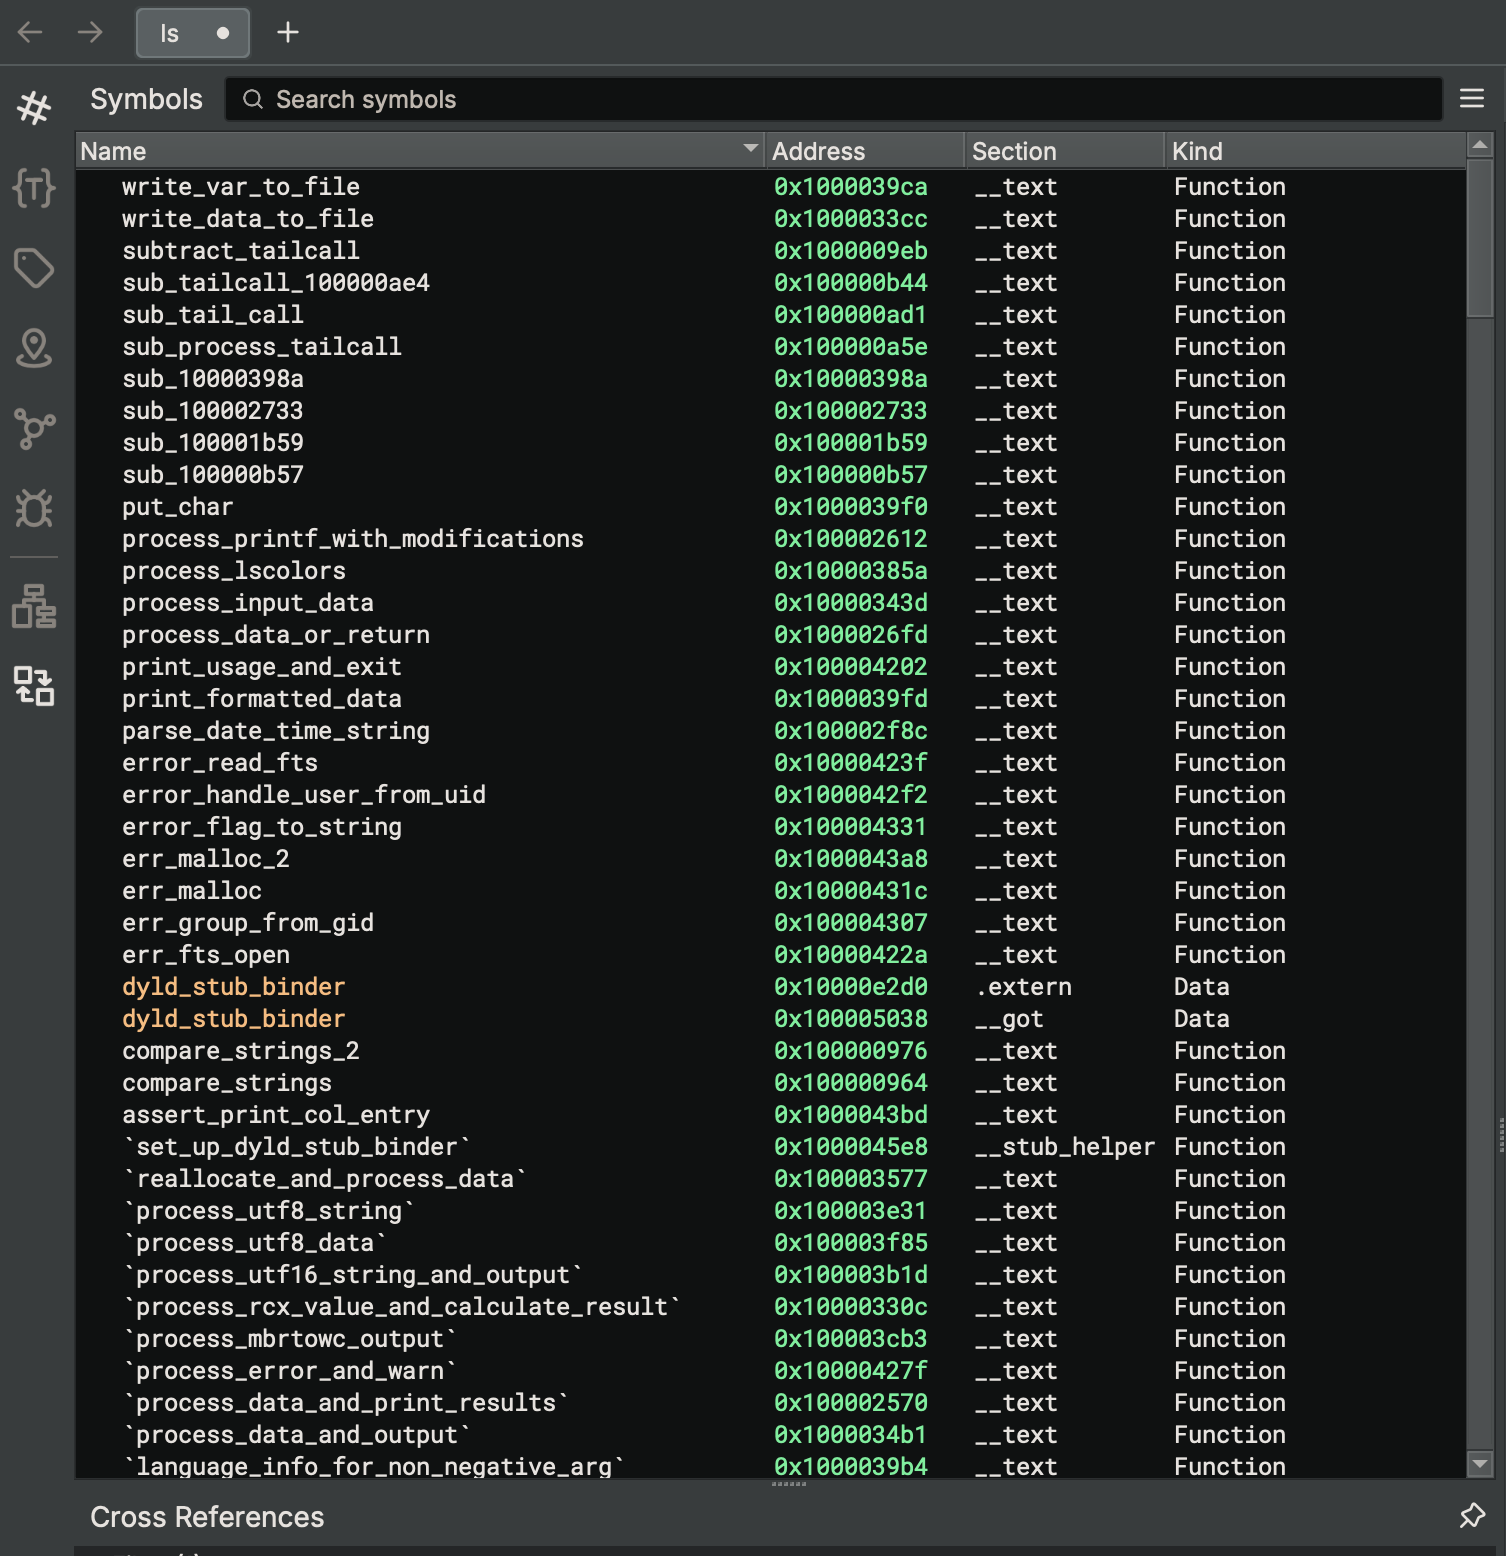 ahaggard2013/binaryninja-ollama
Plugin for Binary Ninja that integrates local Ollama models to rename functions and variables in decompiled HLIL code, preserving privacy by keeping…
 lt-asset/resym
For our CCS24 paper 🏆 "ReSym: Harnessing LLMs to Recover Variable and Data Structure Symbols from Stripped Binaries" by Danning Xie, Zhuo Zhang, Nan…
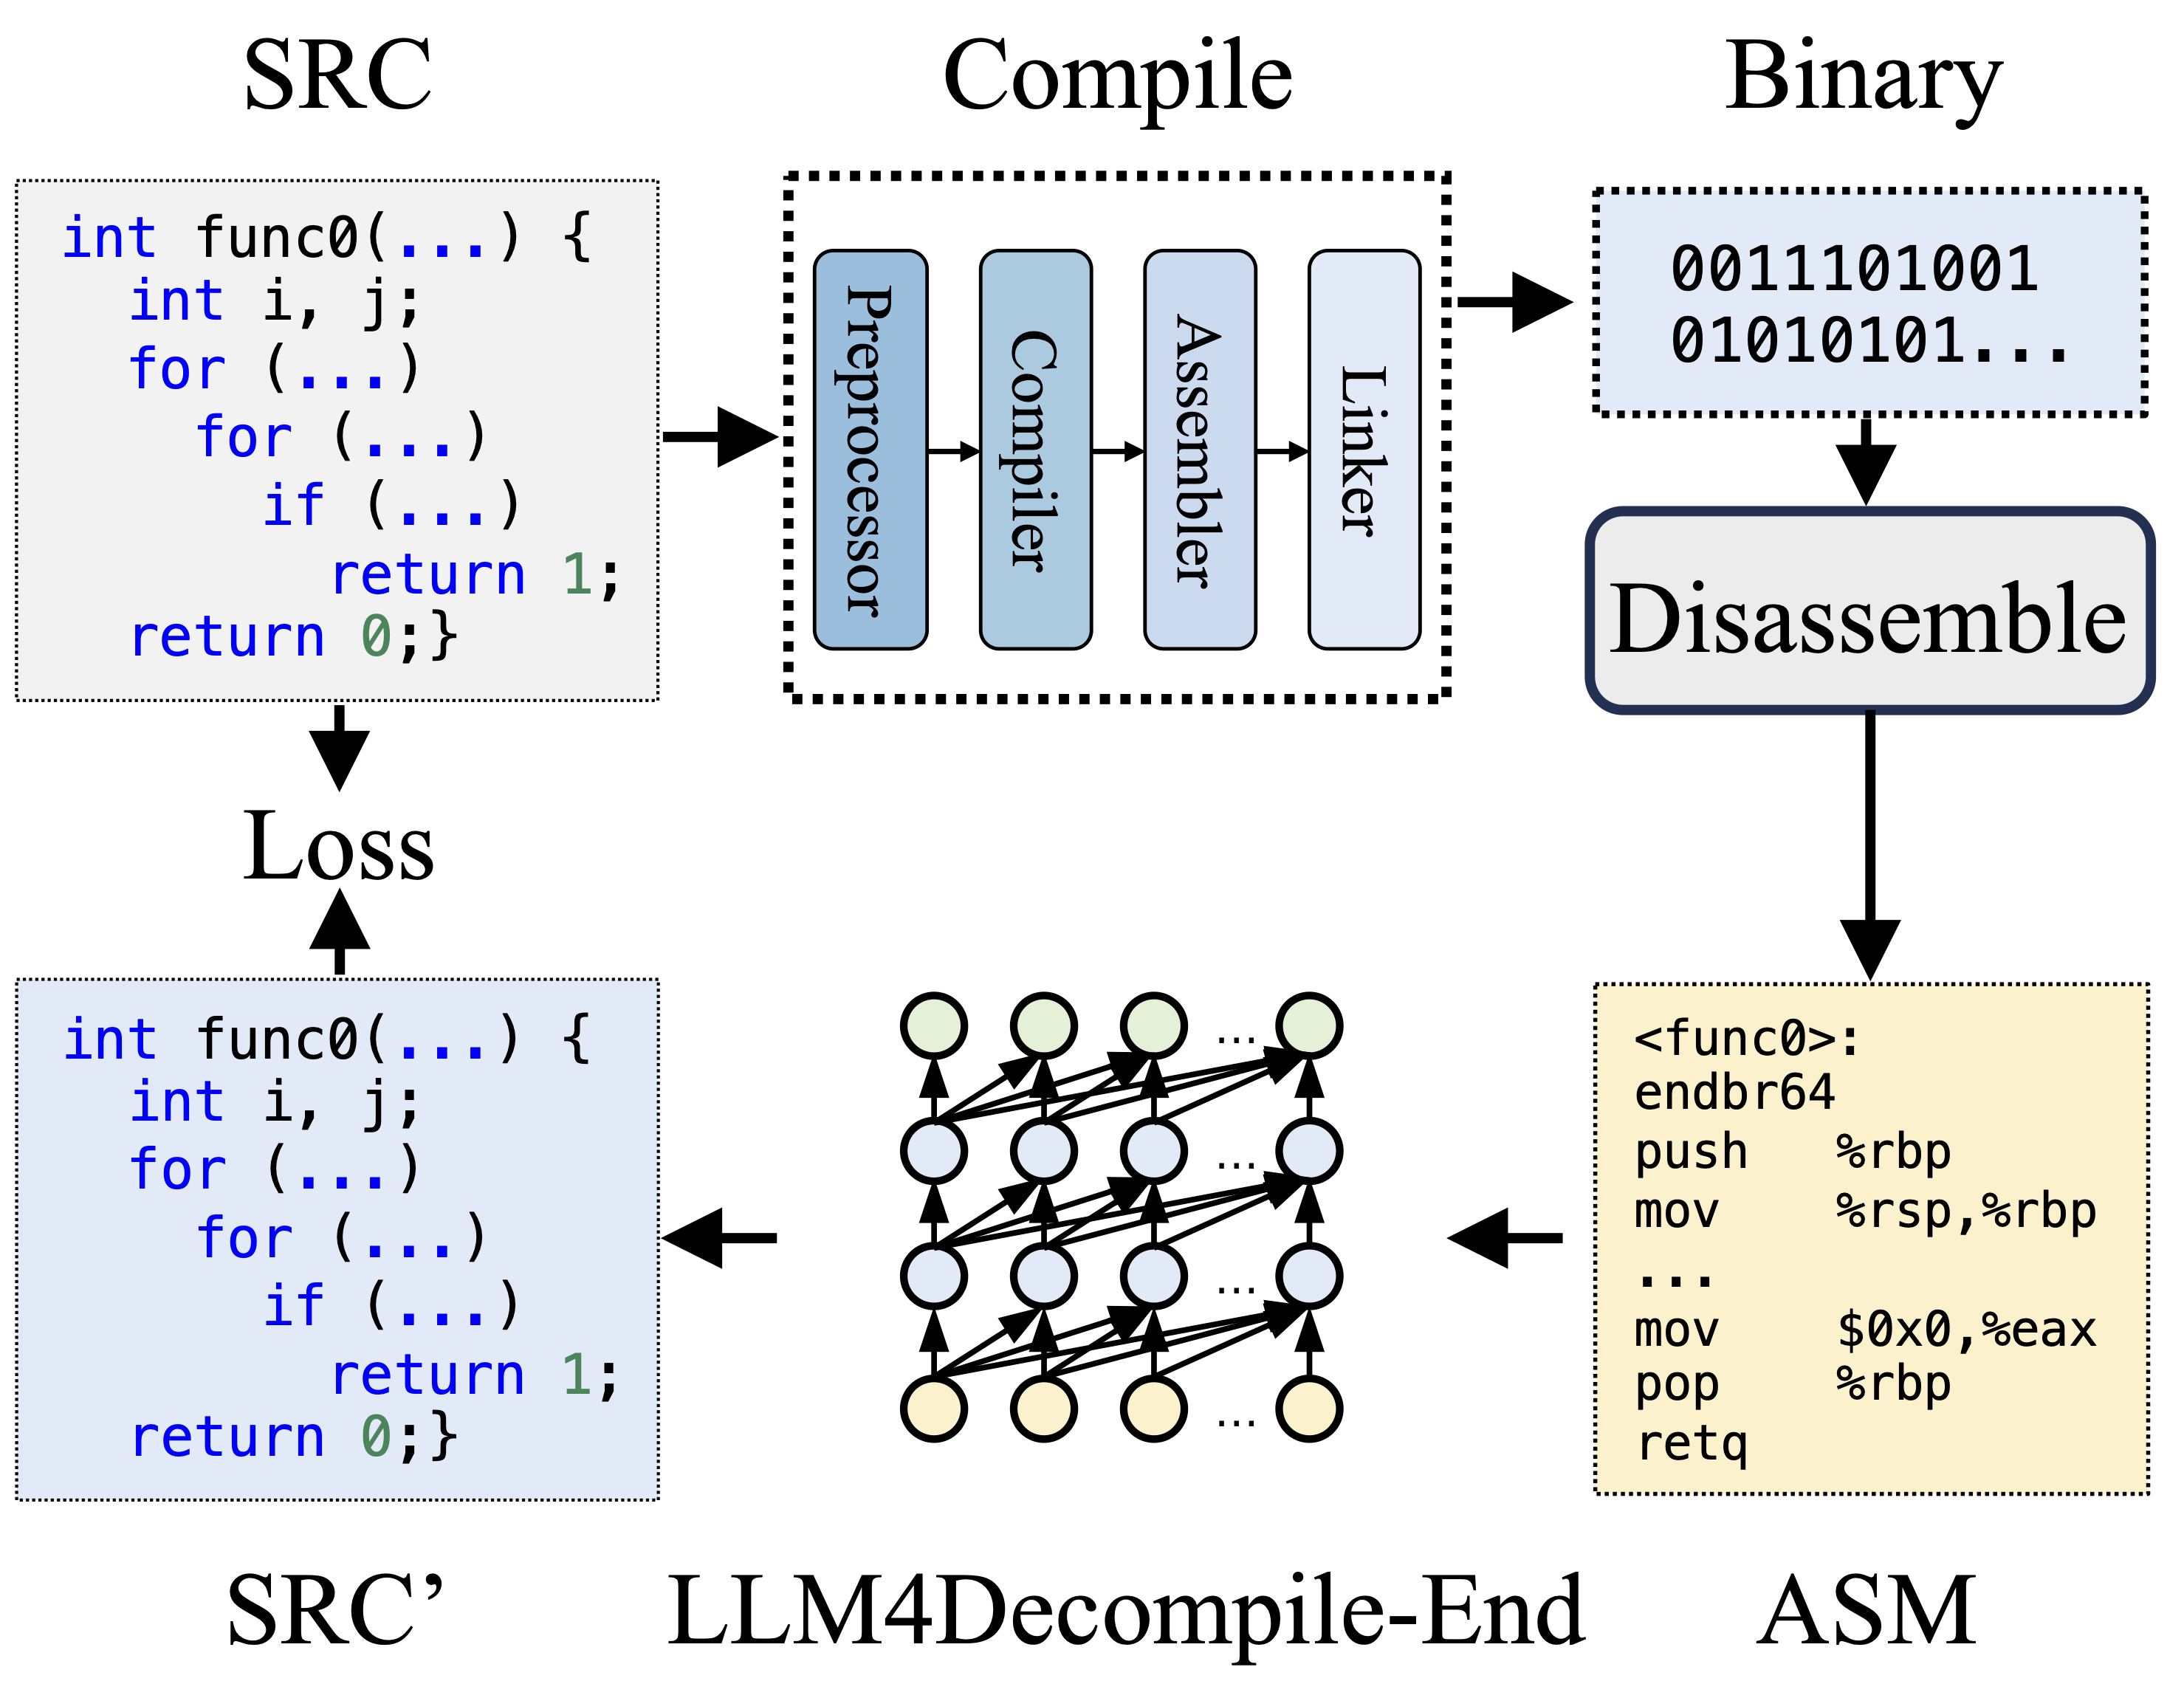 albertan017/llm4decompile
Reverse Engineering: Decompiling Binary Code with Large Language Models
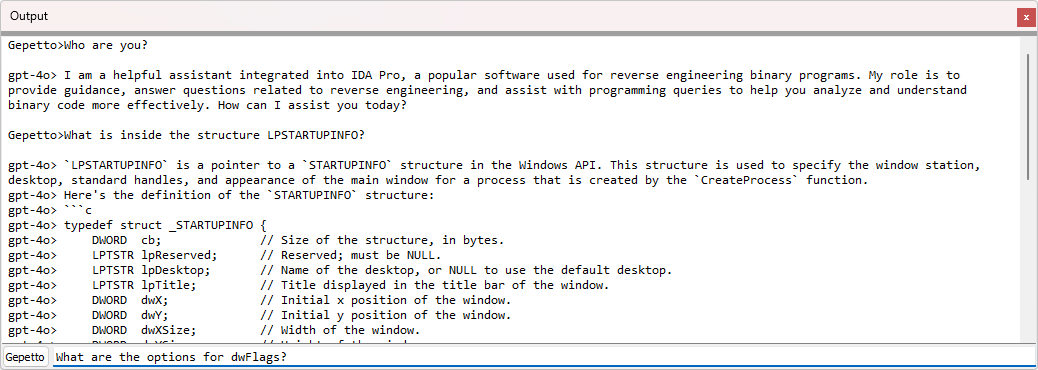 justicerage/gepetto
IDA plugin which queries language models to speed up reverse-engineering
 zhengxr930/maleval
Official code for the ISSTA 2026 paper: Is "Knowing It’s Malicious" Enough? Evaluating LLMs for Fine-Grained Malware Behavior Auditing
 whatishope/bido
Image-based Android malware detection framework tackling obfuscation and concept drift. Includes curated datasets and Python code for training…
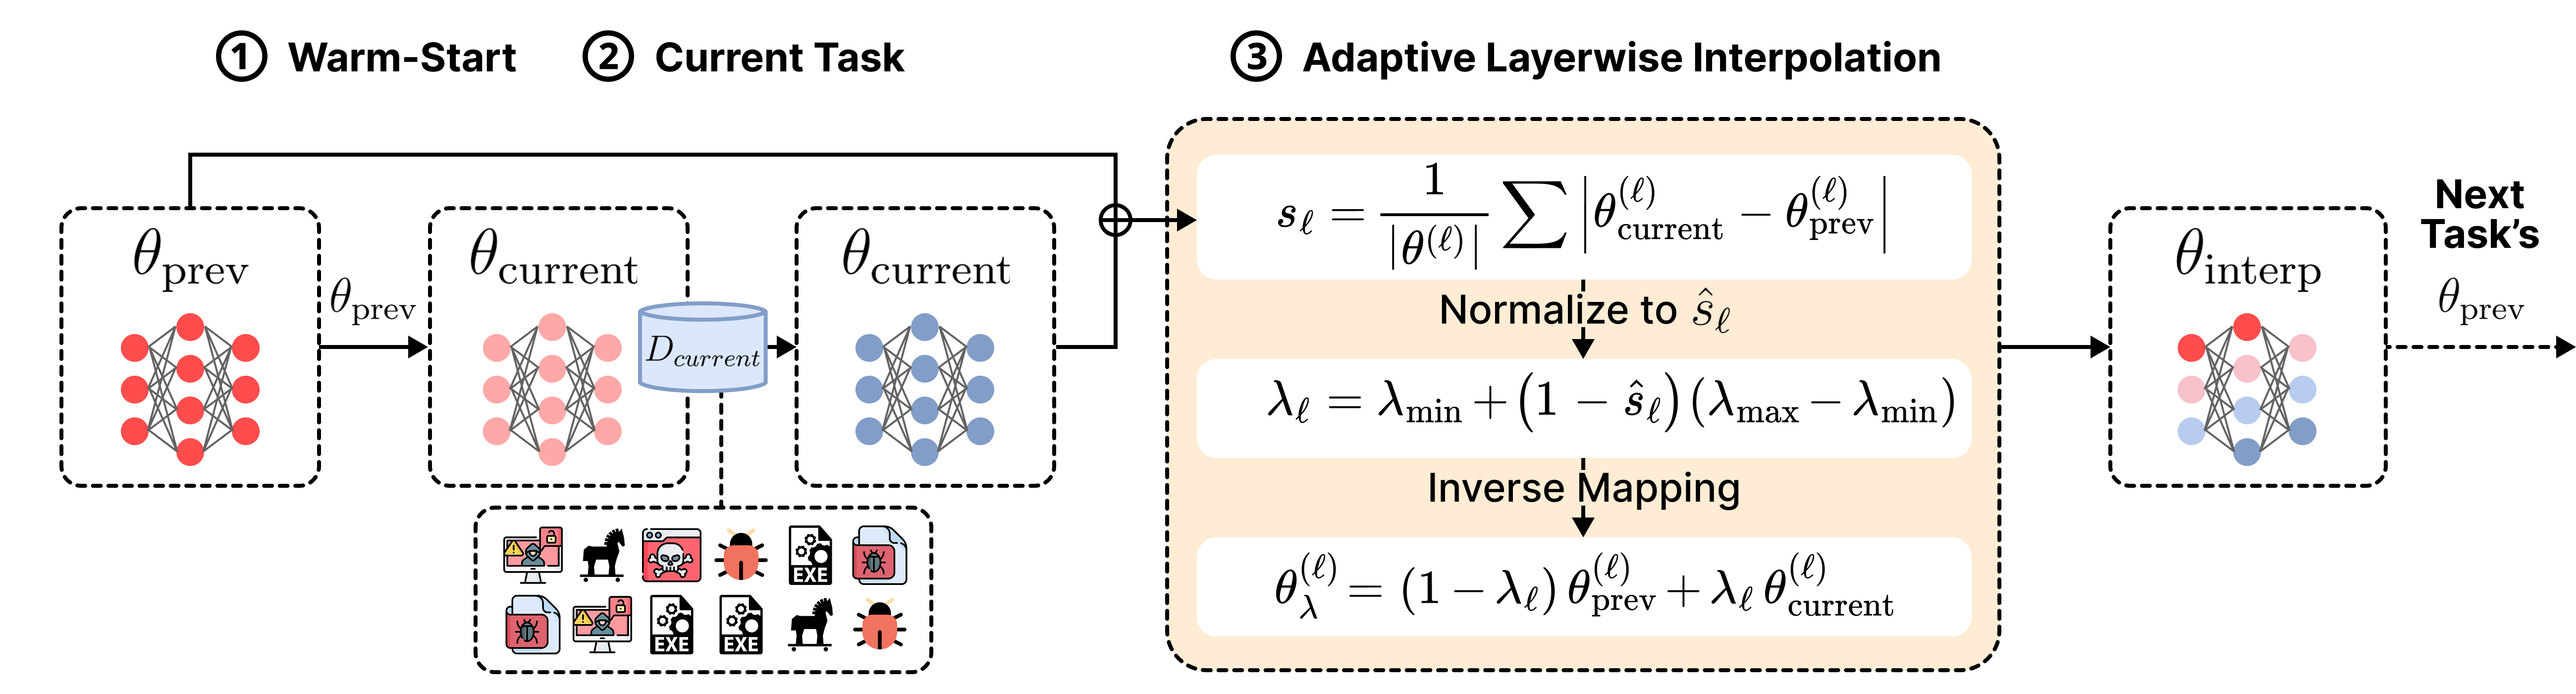 iqsec-lab/freemoca
Memory-free continual learning framework for malware classification using mode connectivity-based interpolation. Supports class-incremental and…
 trustedsec/ts_llmlib
Python library for local LLM-powered security analysis with Ghidra binary analysis, C/C++ vulnerability scanning, and MCP tool integration for…