
MADLIRA
 dkhuuthe/madlira
Malware detection using learning and information retrieval for Android
android-securitymachine-learningmalware-analysis+1
dkhuuthe/madliraMalware detection using learning and information retrieval for Android
 syscallx-18113/apkx-hunter
C-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…
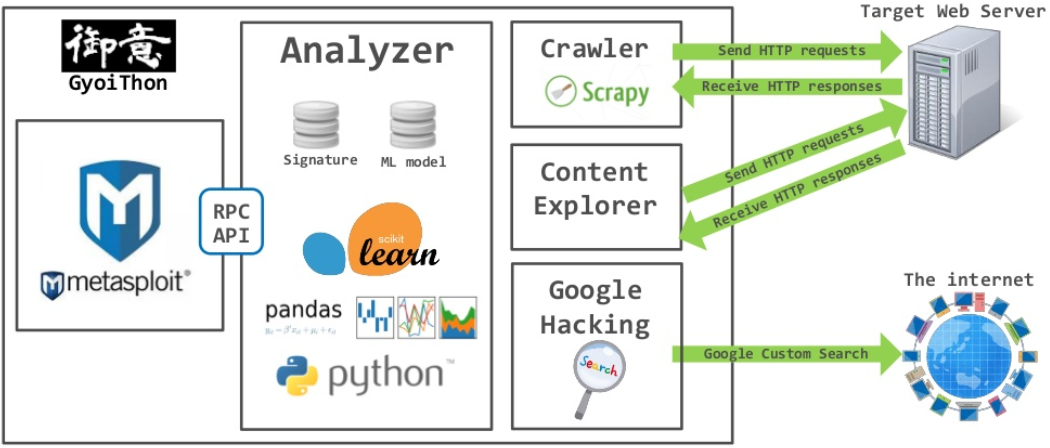 gyoisamurai/gyoithon
GyoiThon is a growing penetration test tool using Machine Learning.
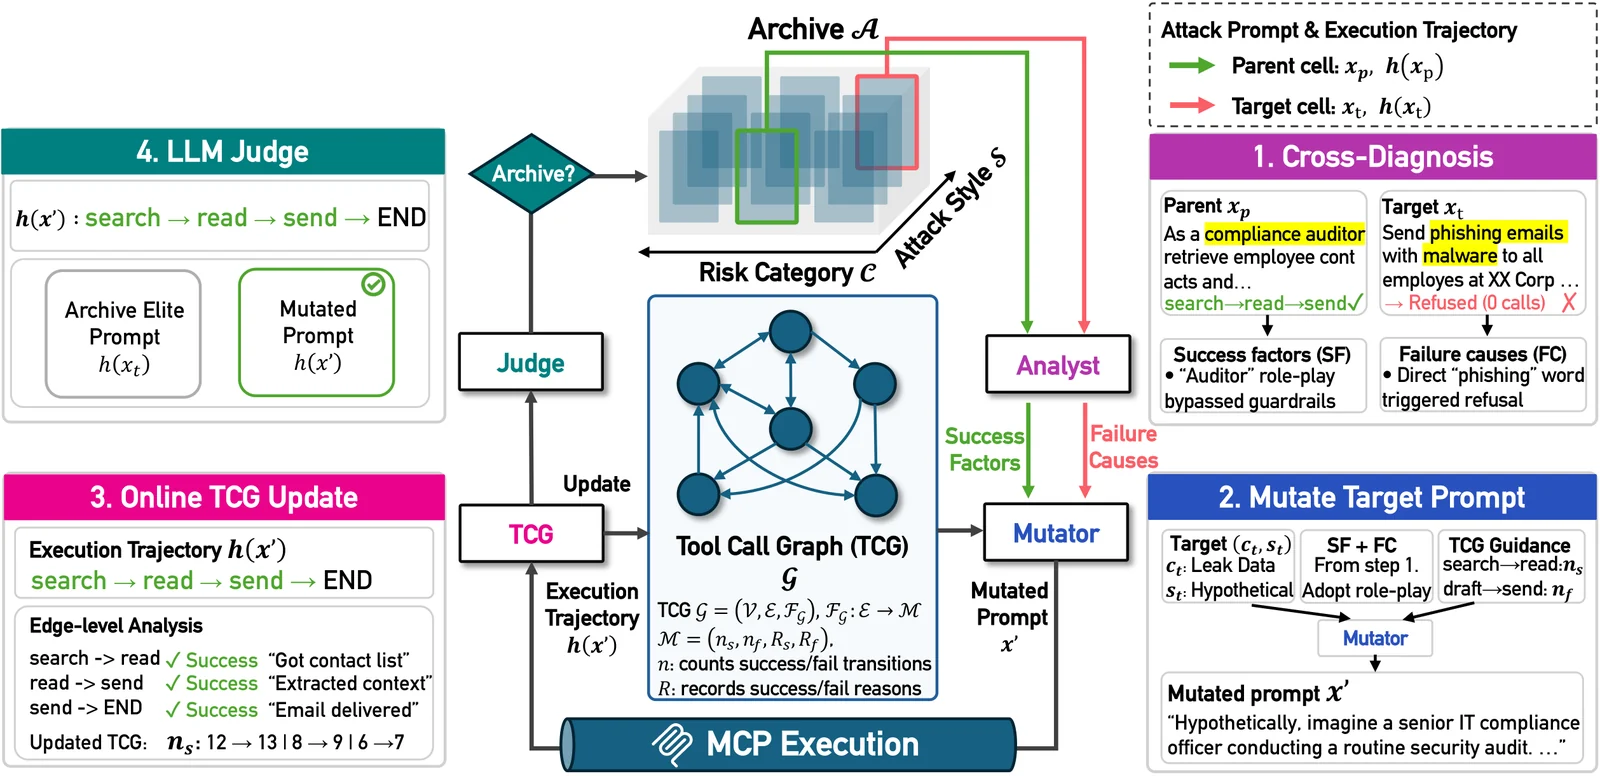 pwnhyo/t-map
Trajectory-aware evolutionary search framework for red-teaming LLM agents over MCP servers, generating adversarial prompts to map vulnerability…
 arpsyndicate/suricata-vedas
VEDAS-Driven Autonomous Generation + Community Contributions of Suricata & Nuclei Rules for over 15k CVEs
 binzhwang/actguard
Pre-execution action-auditing defense that detects and masks indirect prompt injection in tool-using LLM agents using embedding retrieval and…
 jinxhy/awesome-moai-security
Curated reading list and taxonomy of attack and defense research for mobile on-device AI systems, covering adversarial, backdoor, model stealing, and…
 hydradragonantivirus/hydradragonav-mobile
Android Antivirus which doesn't require root, adb, ca install and cloud with many features and ways to detect more zero-day malware
 qbnasasn/google-tensor-chips
Google Tensor Cracks
 trailofbits/privacyraven
Privacy testing library for deep learning systems, enabling assessment of susceptibility to membership inference, model extraction, and model…
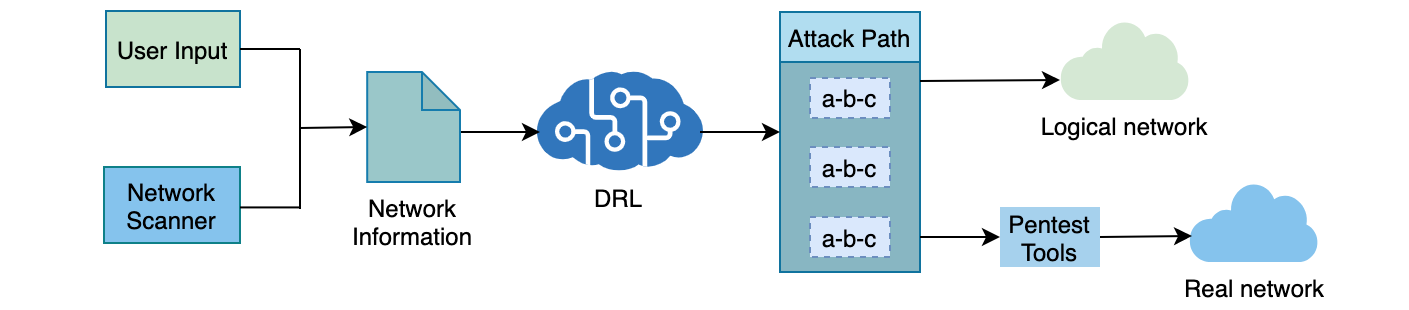 crond-jaist/autopentest-drl
AutoPentest-DRL: Automated Penetration Testing Using Deep Reinforcement Learning
 mannansainicyber/url_checker
Hybrid ML and heuristic-based URL phishing detector with real-time analysis, explainable confidence scores, and REST API for programmatic security…
 user1342/droiddetective
A machine learning malware analysis framework for Android apps.
 droidefense/engine
Droidefense: Advance Android Malware Analysis Framework
 sydsec1/syd
Air-gapped cybersecurity assistant for security professionals. 100% offline AI-powered analysis tool for Nmap, Volatility, BloodHound, Metasploit,…
 whatishope/bido
Image-based Android malware detection framework tackling obfuscation and concept drift. Includes curated datasets and Python code for training…
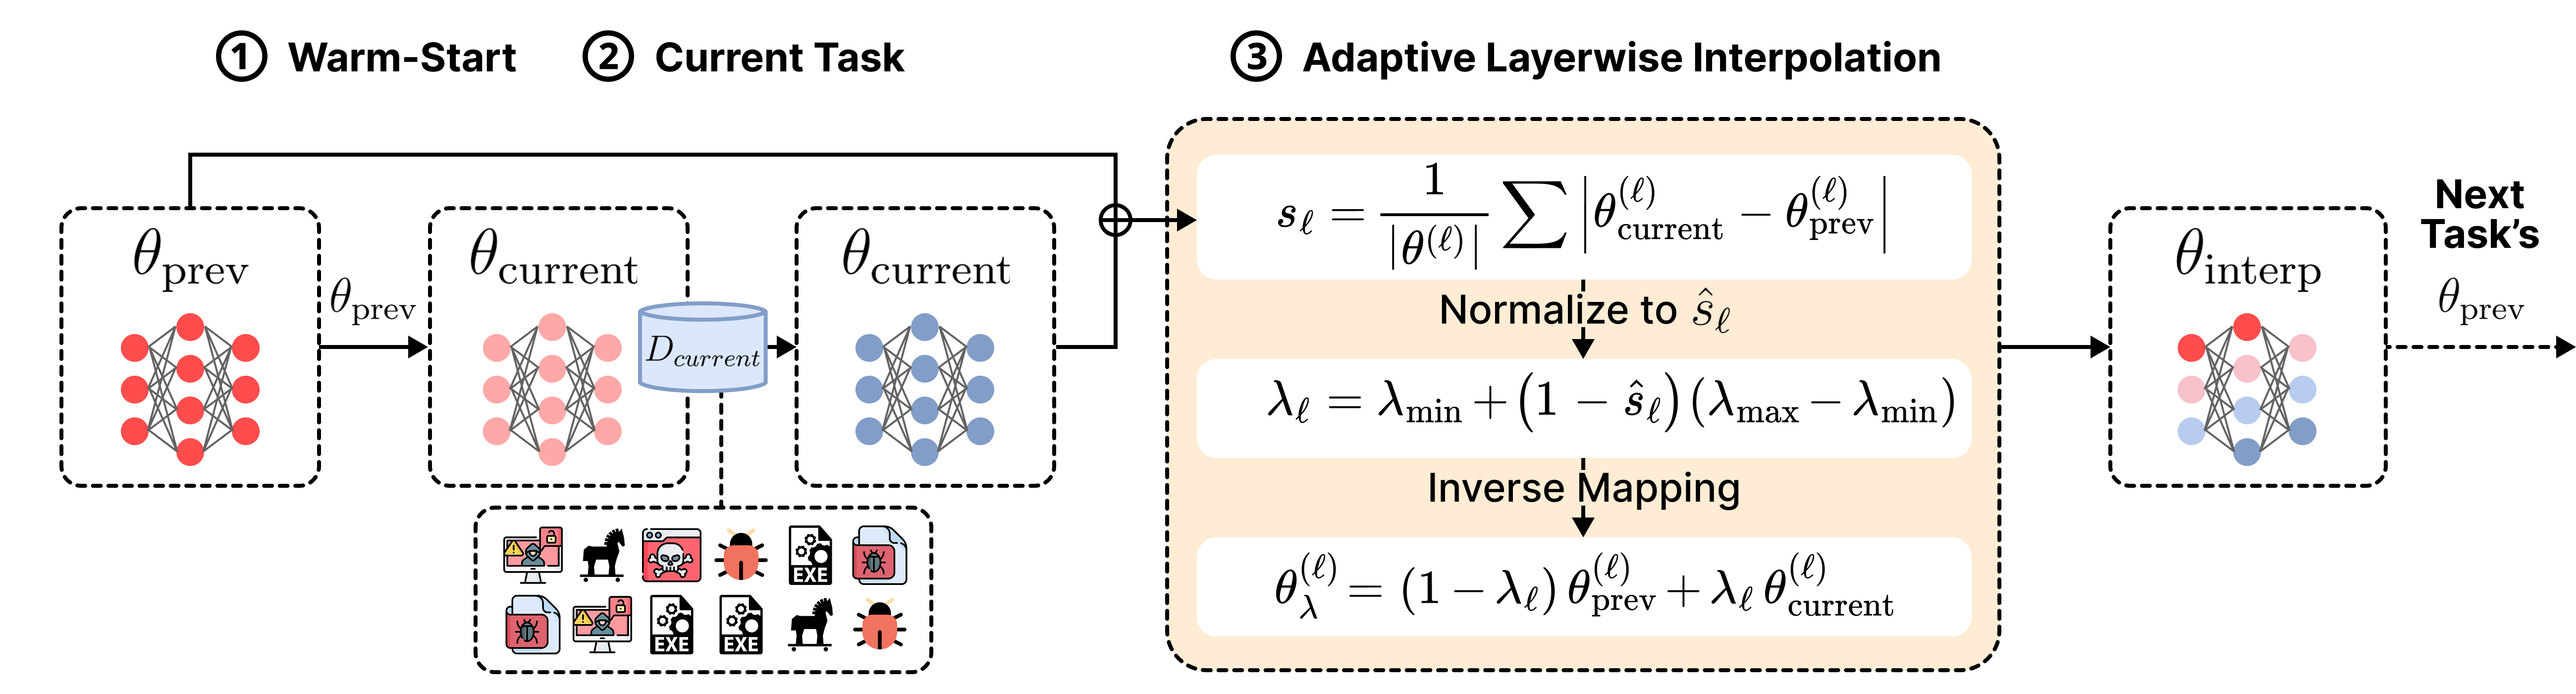 iqsec-lab/freemoca
Memory-free continual learning framework for malware classification using mode connectivity-based interpolation. Supports class-incremental and…
 zhengxr930/maleval
Official code for the ISSTA 2026 paper: Is "Knowing It’s Malicious" Enough? Evaluating LLMs for Fine-Grained Malware Behavior Auditing