rootly-graphify-importer

Turn Rootly incidents, alerts, and teams into a queryable knowledge graph. Visualize service dependencies, on-call coverage gaps, and cross-incident…

Turn Rootly incidents, alerts, and teams into a queryable knowledge graph. Visualize service dependencies, on-call coverage gaps, and cross-incident…

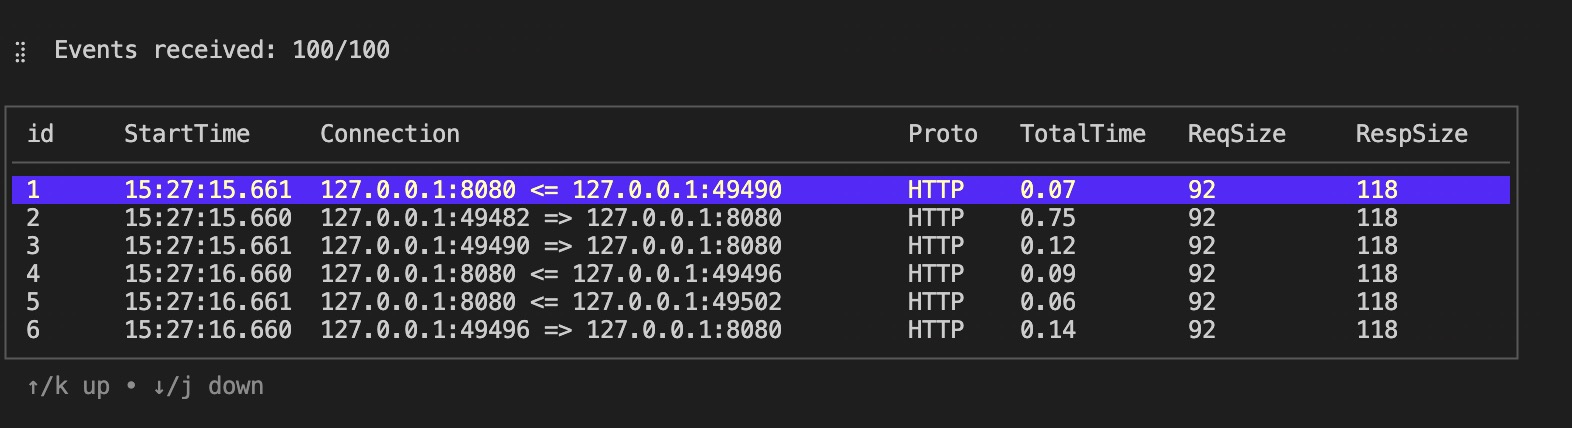
Kyanos is a networking analysis tool using eBPF. It can visualize the time packets spend in the kernel, capture requests/responses, makes…

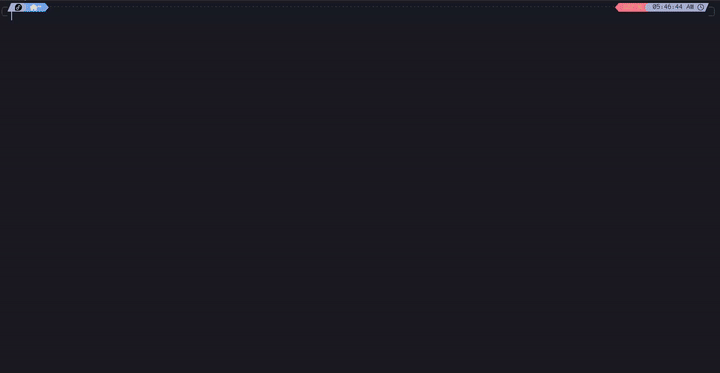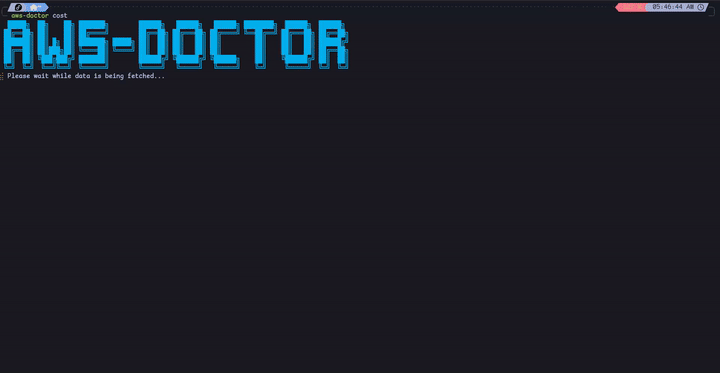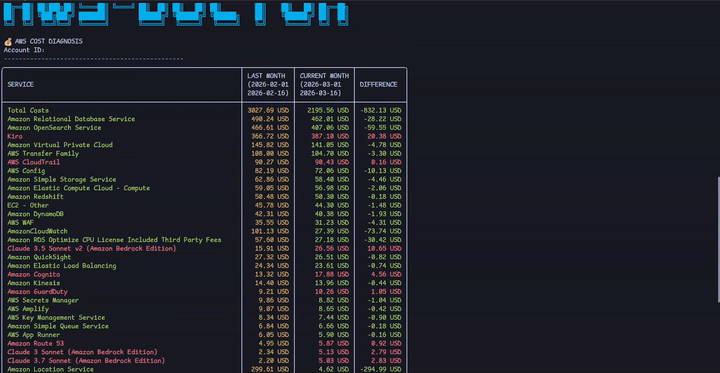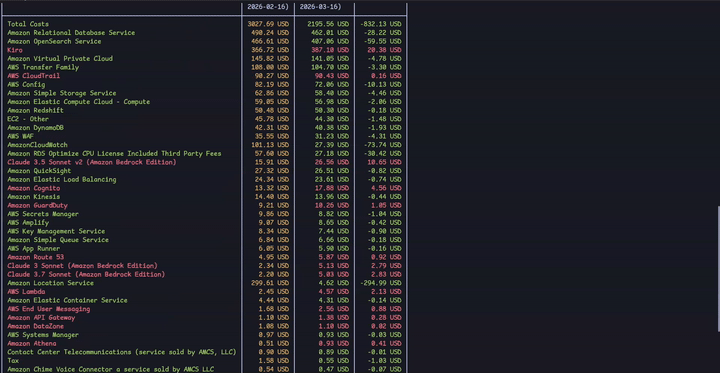
Powerful open-source CLI to audit security, costs, and best practices in AWS. 🩺 ☁️

SkyWrapper helps to discover suspicious creation forms and uses of temporary tokens in AWS

Analyse SQL injection attempts in web server logs

Analyzes Nginx access logs to detect SQL injection, scanner tools, webshells, and exploitation attempts, aiding system administrators in server…

Wazuh detection rules for CVE-2026-73570, an OS command injection in Zimbra Collaboration Suite, monitoring web access logs and zimbra.log for…

Proof-of-concept exploit for CVE-2020-35488, a denial-of-service vulnerability in NXLOG Community Edition via crafted syslog payloads causing…

Proof-of-concept exploit for CVE-2019-17041, a buffer overflow in rsyslog's parser, demonstrating remote code execution.

Provides upgrade and mitigation instructions for Apache Log4j vulnerability CVE-2021-44228 in Remote Syslog products, including version checks and…

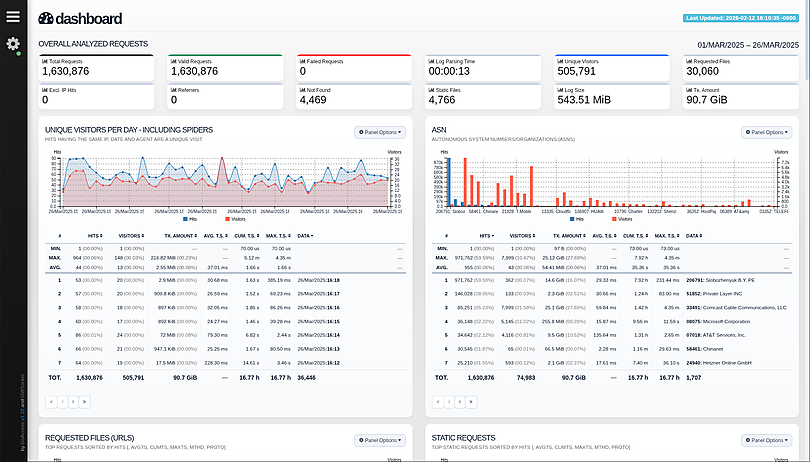
GoAccess is a real-time web log analyzer and interactive viewer that runs in a terminal in *nix systems or through your browser.

🍯 T-Pot - The All In One Multi Honeypot Platform 🐝

Multi-threaded Windows event log forensics timeline generator and threat hunting tool with full Sigma rule support, producing CSV/JSON timelines for…

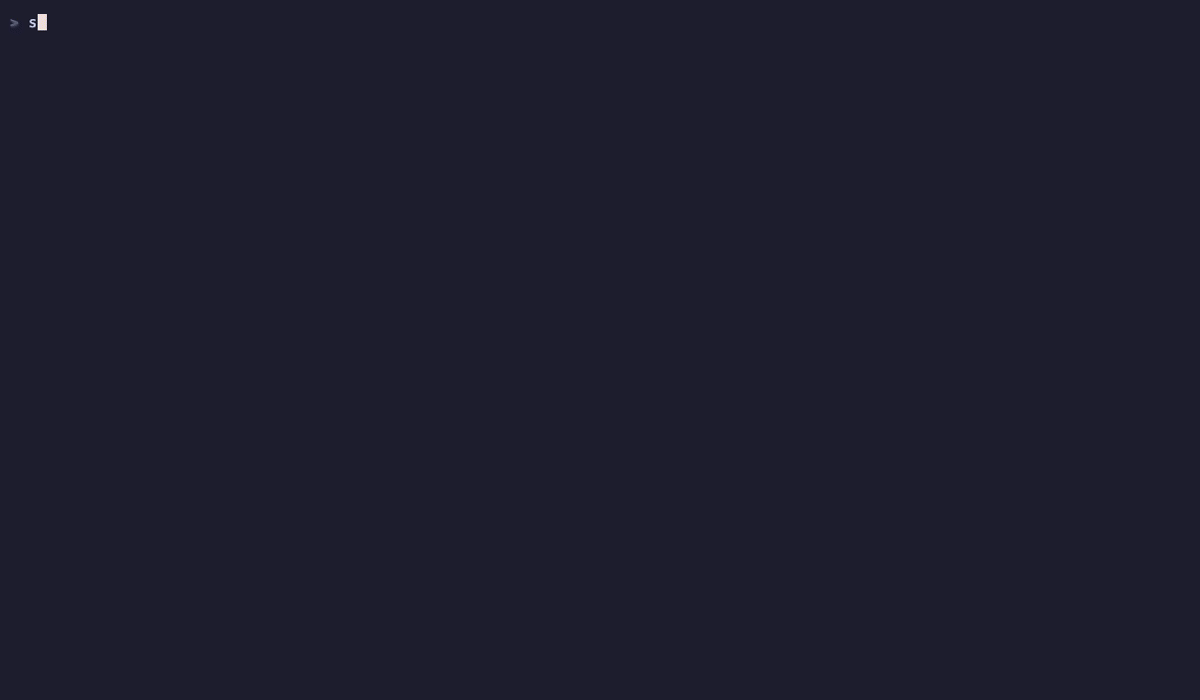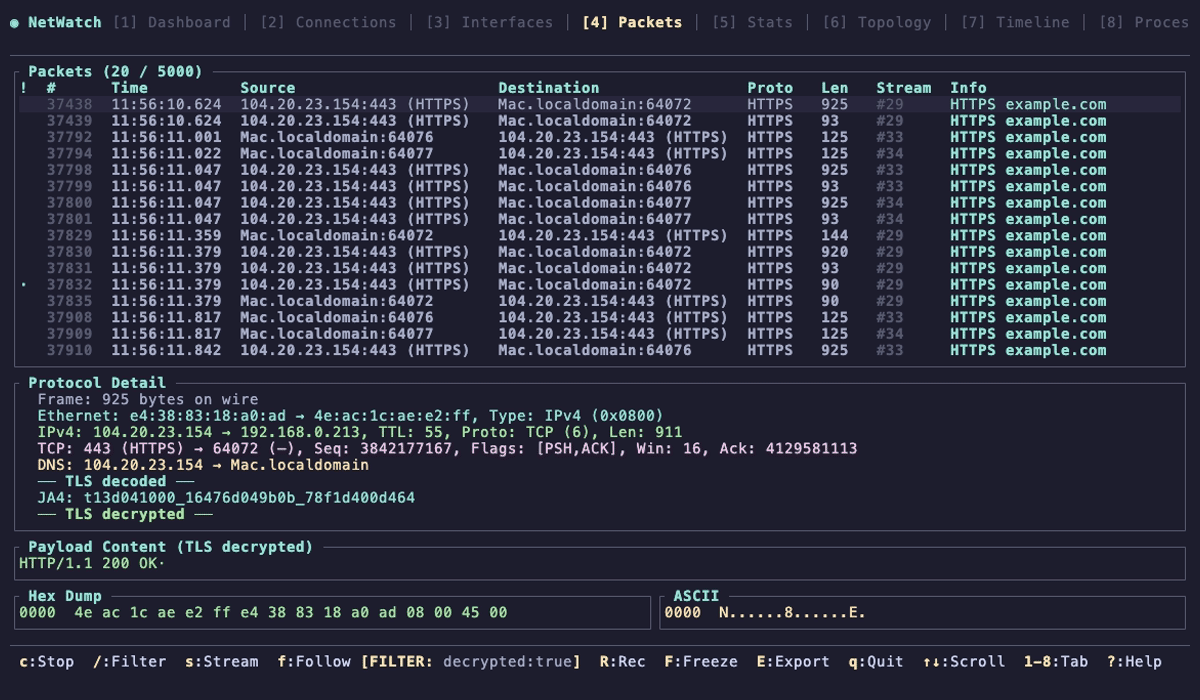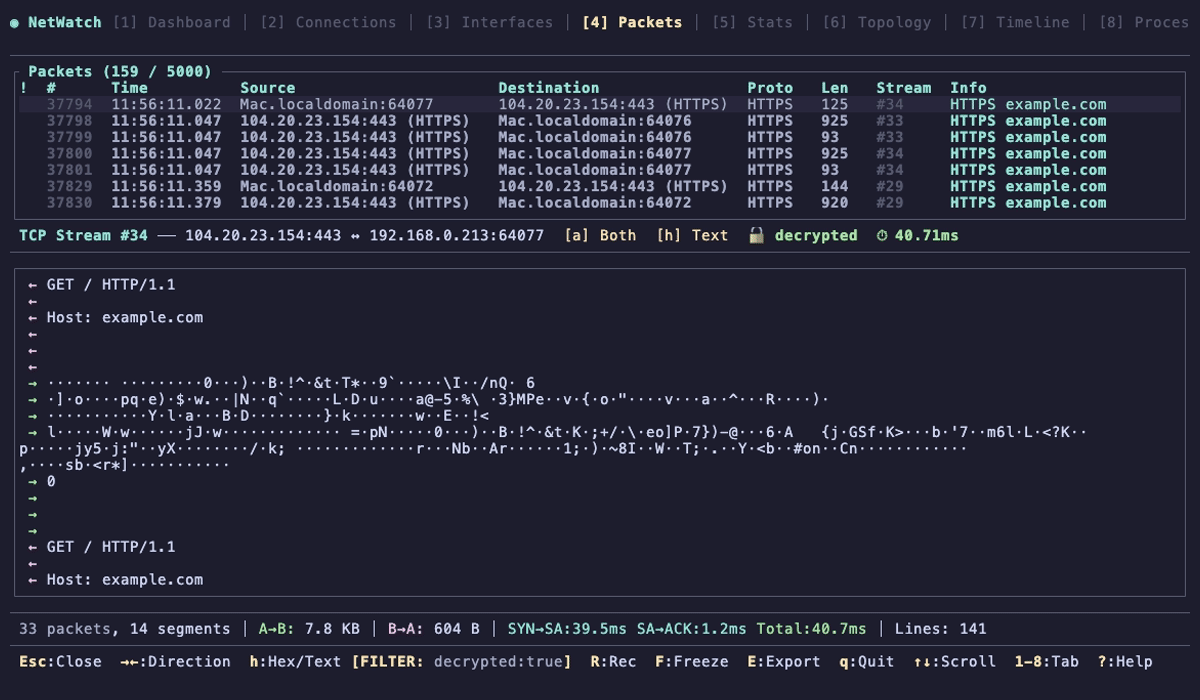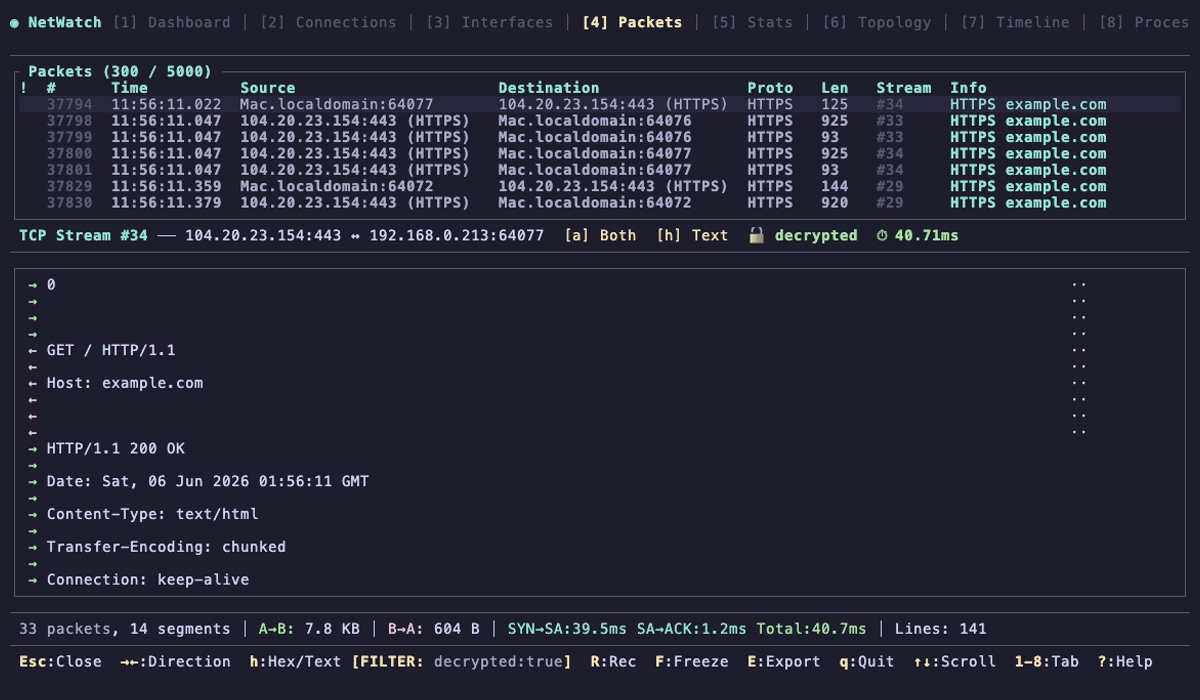
Real-time network diagnostics in your terminal. One command, zero config, instant visibility.

Self-hostable AI SOC that fuses security alerts, auto-triages via agentic AI, runs MITRE ATT&CK investigations, and logs every agent decision in a…

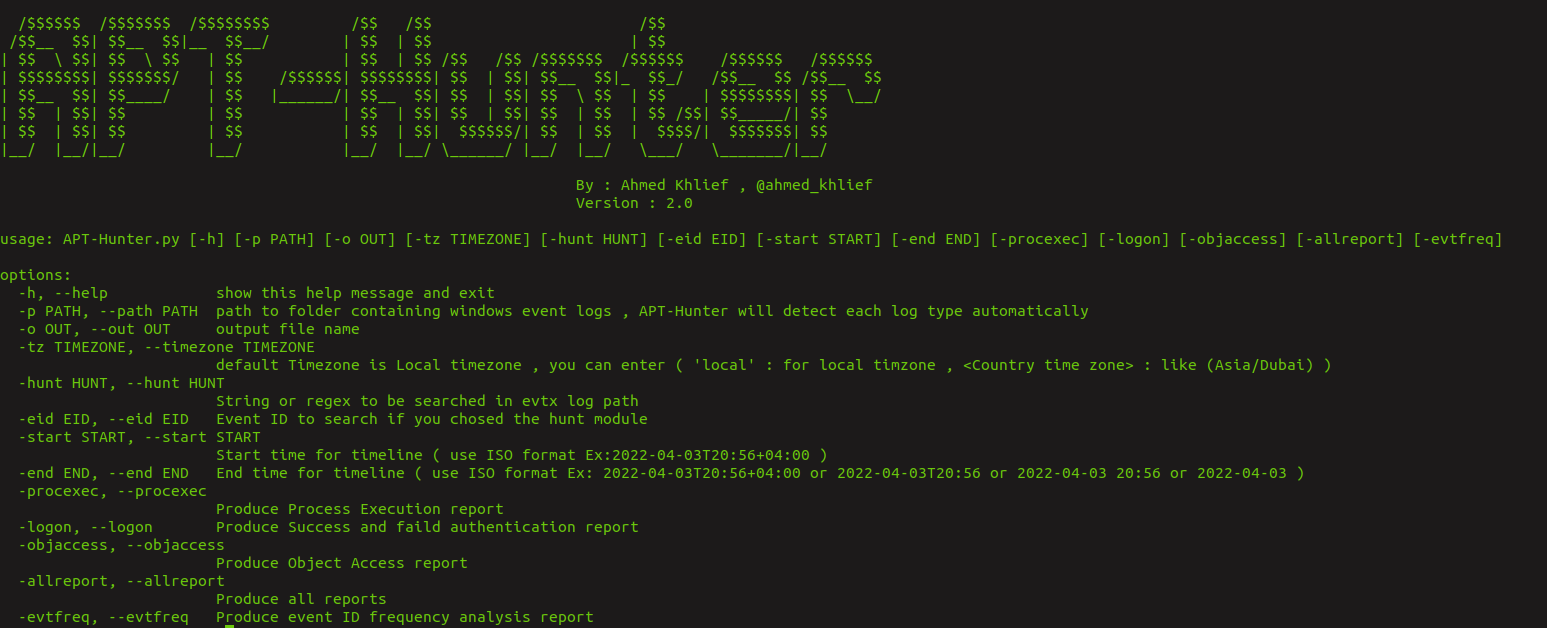
APT-Hunter is Threat Hunting tool for windows event logs which made by purple team mindset to provide detect APT movements hidden in the sea of…

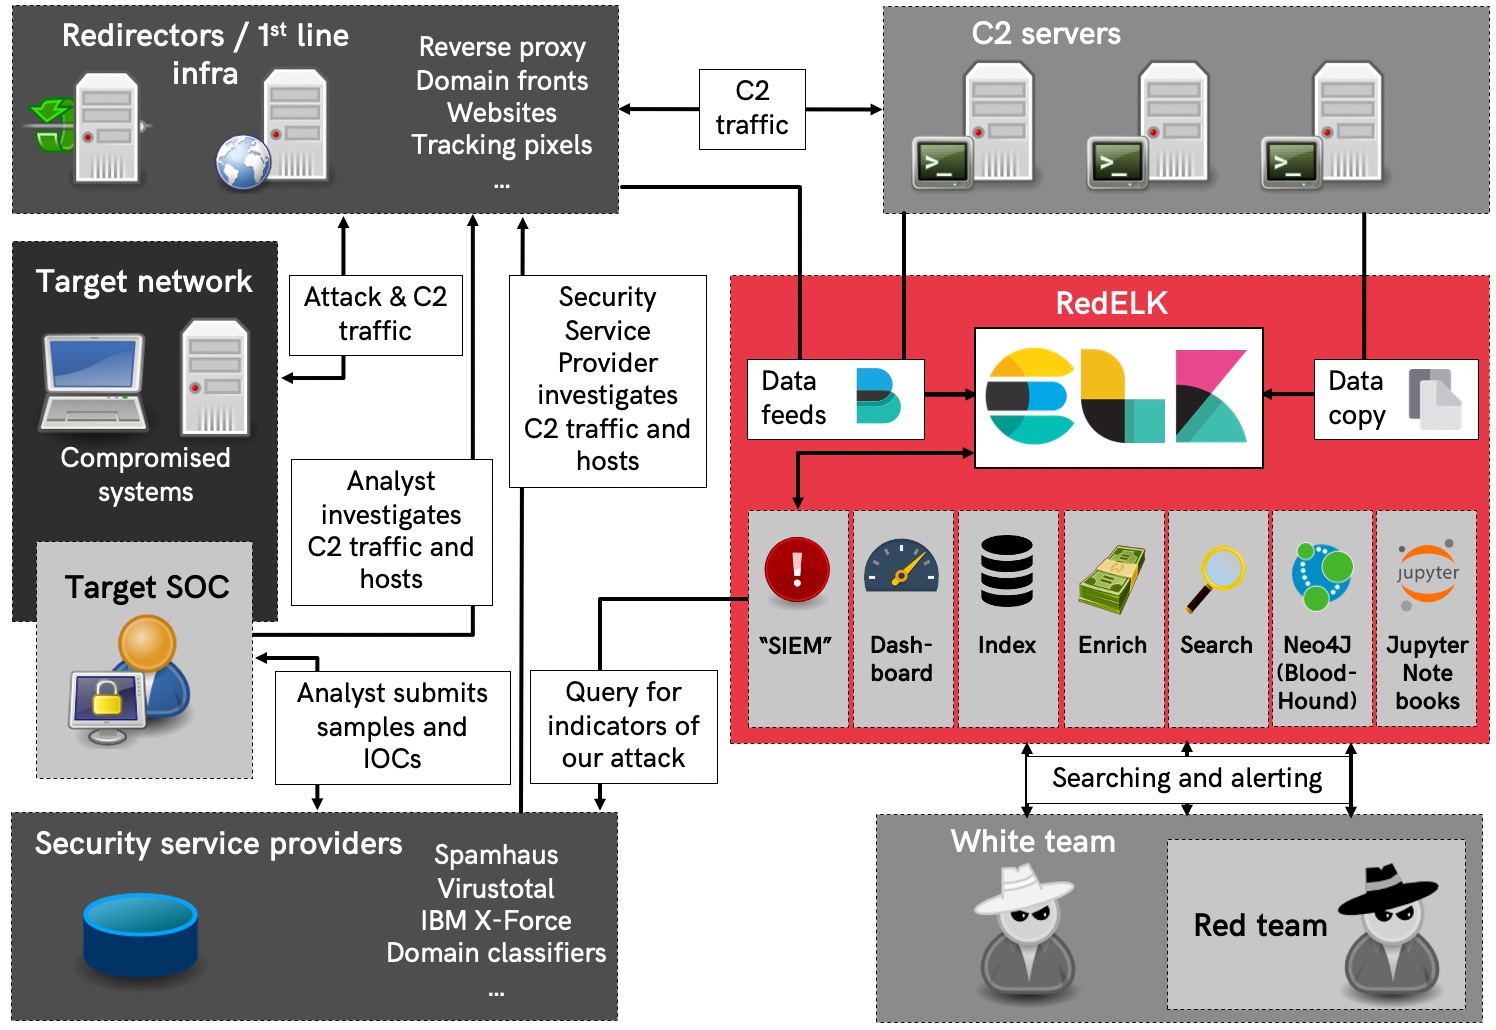
Red Team's SIEM - tool for Red Teams used for tracking and alarming about Blue Team activities as well as better usability in long term operations.

Advanced Sysmon ATT&CK configuration focusing on Detecting the Most Techniques per Data source in MITRE ATT&CK, Provide Visibility into Forensic…