
log4shell_sentinel
 ossie-git/log4shell_sentinel
A Smart Log4Shell/Log4j/CVE-2021-44228 Scanner
container-securityforensicsincident-response+3
13
ossie-git/log4shell_sentinelA Smart Log4Shell/Log4j/CVE-2021-44228 Scanner
 withsecurelabs/detectree
Interactive data visualization tool for blue teams to analyze detection data, understand relationships, reduce alert fatigue, and improve incident…
 emrekybs/mrhandler
SSH-based Linux incident response tool that executes diagnostic commands to collect network configs, logs, user accounts, and processes, then…
 t0pcyber/hawk
Powershell Based tool for gathering information related to O365 intrusions and potential Breaches
 hestat/drupal-check
Tool to dive Apache logs for evidence of exploitation of CVE-2018-7600
 pathtofile/sealighter
ETW and WPP tracing tool for security research. Subscribes to multiple providers, auto-parses events to JSON, and supports advanced filtering,…
 jsa2/east
Extensible Azure Security Tool - Documentation
 withsecurelabs/remotepspy
Live monitoring tool for remote PowerShell sessions using ETW to capture and decode WinRM/PSRP protocol, providing command execution traces and…
 emrekybs/nginxhunter
Analyzes Nginx access logs to detect SQL injection, scanner tools, webshells, and exploitation attempts, aiding system administrators in server…
 0x0v1/audix
Audix is a PowerShell tool to quickly configure the Windows Event Audit Policies for security monitoring
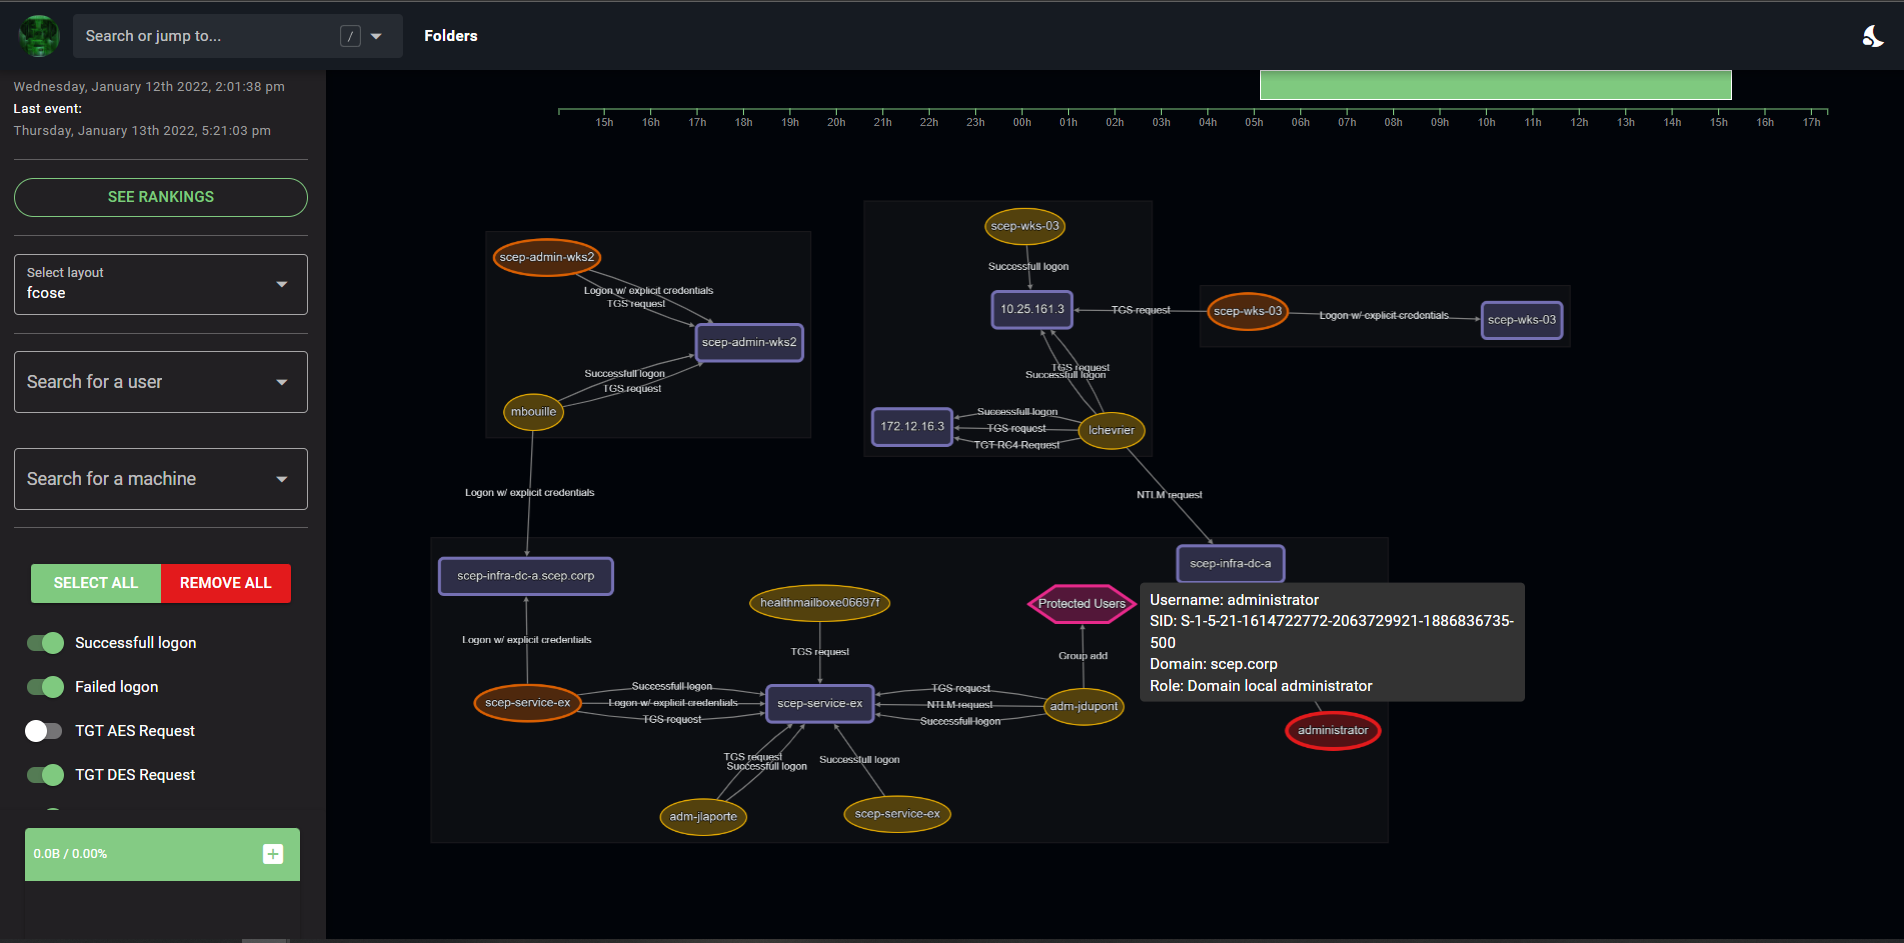
 ait-aecid/logdata-anomaly-miner
This tool parses log data and allows to define analysis pipelines for anomaly detection. It was designed to run the analysis with limited resources…
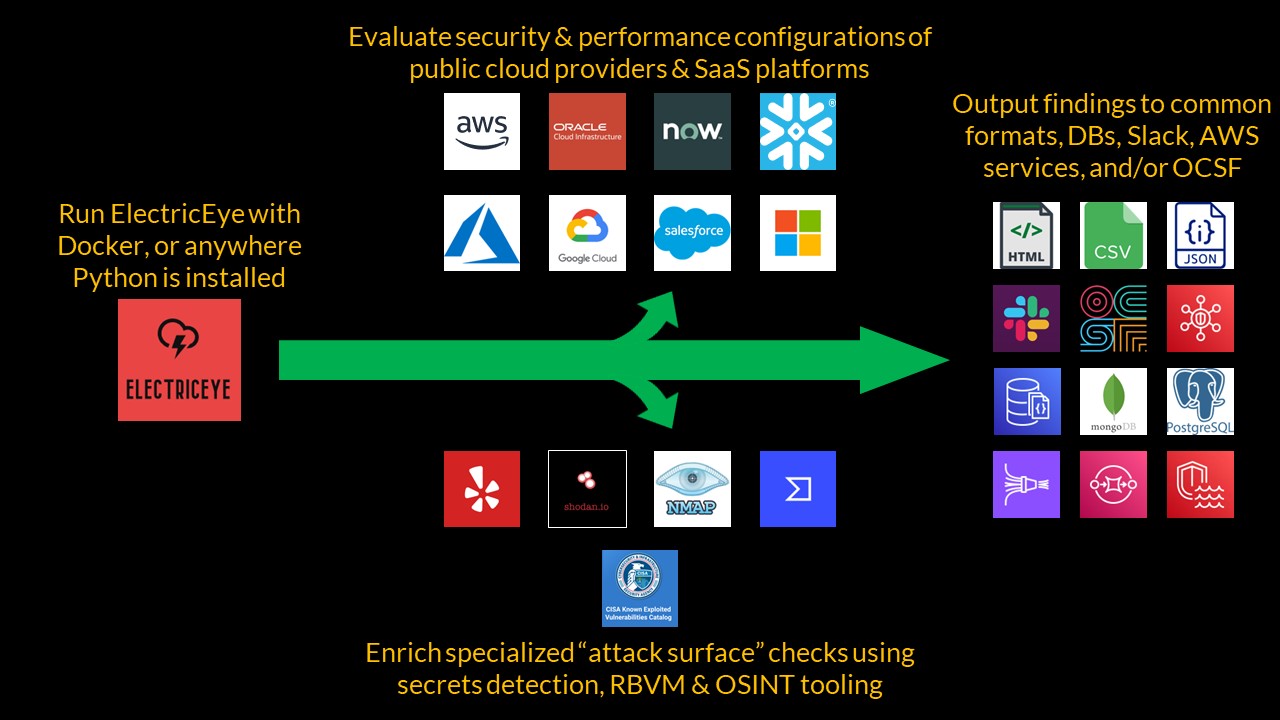 jonrau1/electriceye
ElectricEye is a multi-cloud, multi-SaaS Python CLI tool for Asset Management, Security Posture Management & Attack Surface Monitoring supporting…
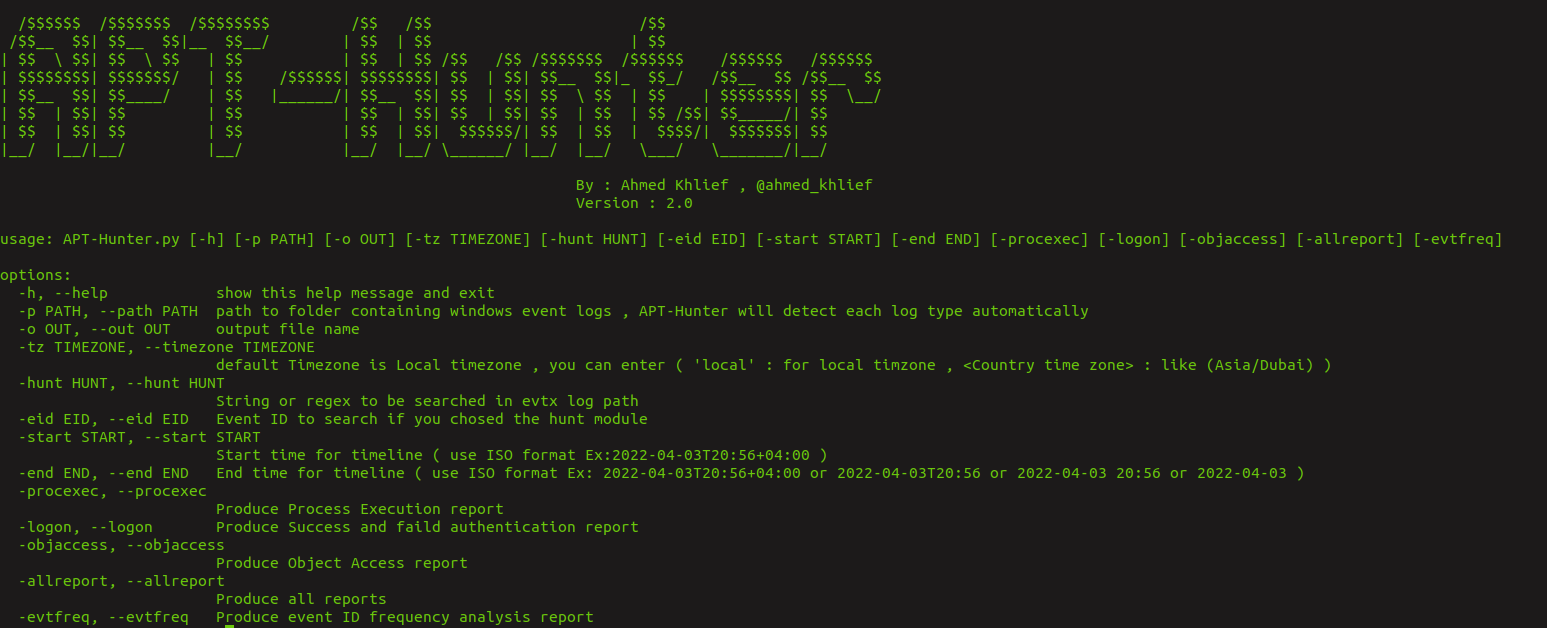 ahmedkhlief/apt-hunter
APT-Hunter is Threat Hunting tool for windows event logs which made by purple team mindset to provide detect APT movements hidden in the sea of…
 invictus-ir/alfa
Automated forensic analysis tool for Google Workspace audit logs. Acquires all log types, maps events to MITRE ATT&CK Cloud Framework, and identifies…
 k3rnix/portguard
USB port access control tool for Debian with whitelist management, automatic background scanning daemon, and CLI interface to block or allow USB…
 google/timesketch
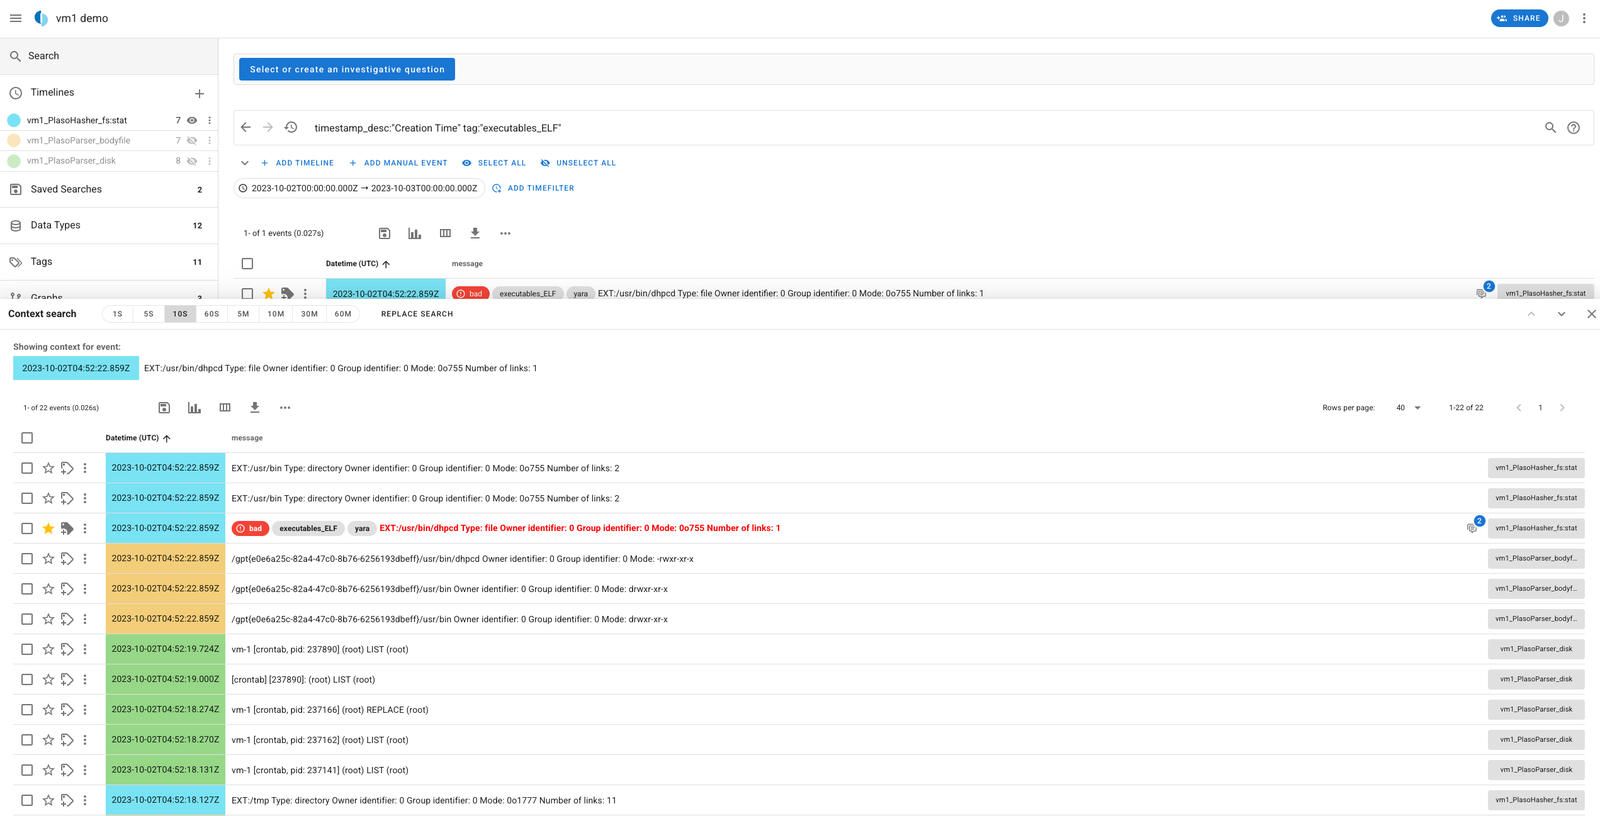
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
 abdulrhmanalfaifi/fennec
Artifact collection tool for *nix systems