

teleport
 gravitational/teleport
The easiest, and most secure way to access and protect all of your infrastructure.
api-securityauthentication-authorizationcloud-security+7
21.0k
gravitational/teleportThe easiest, and most secure way to access and protect all of your infrastructure.
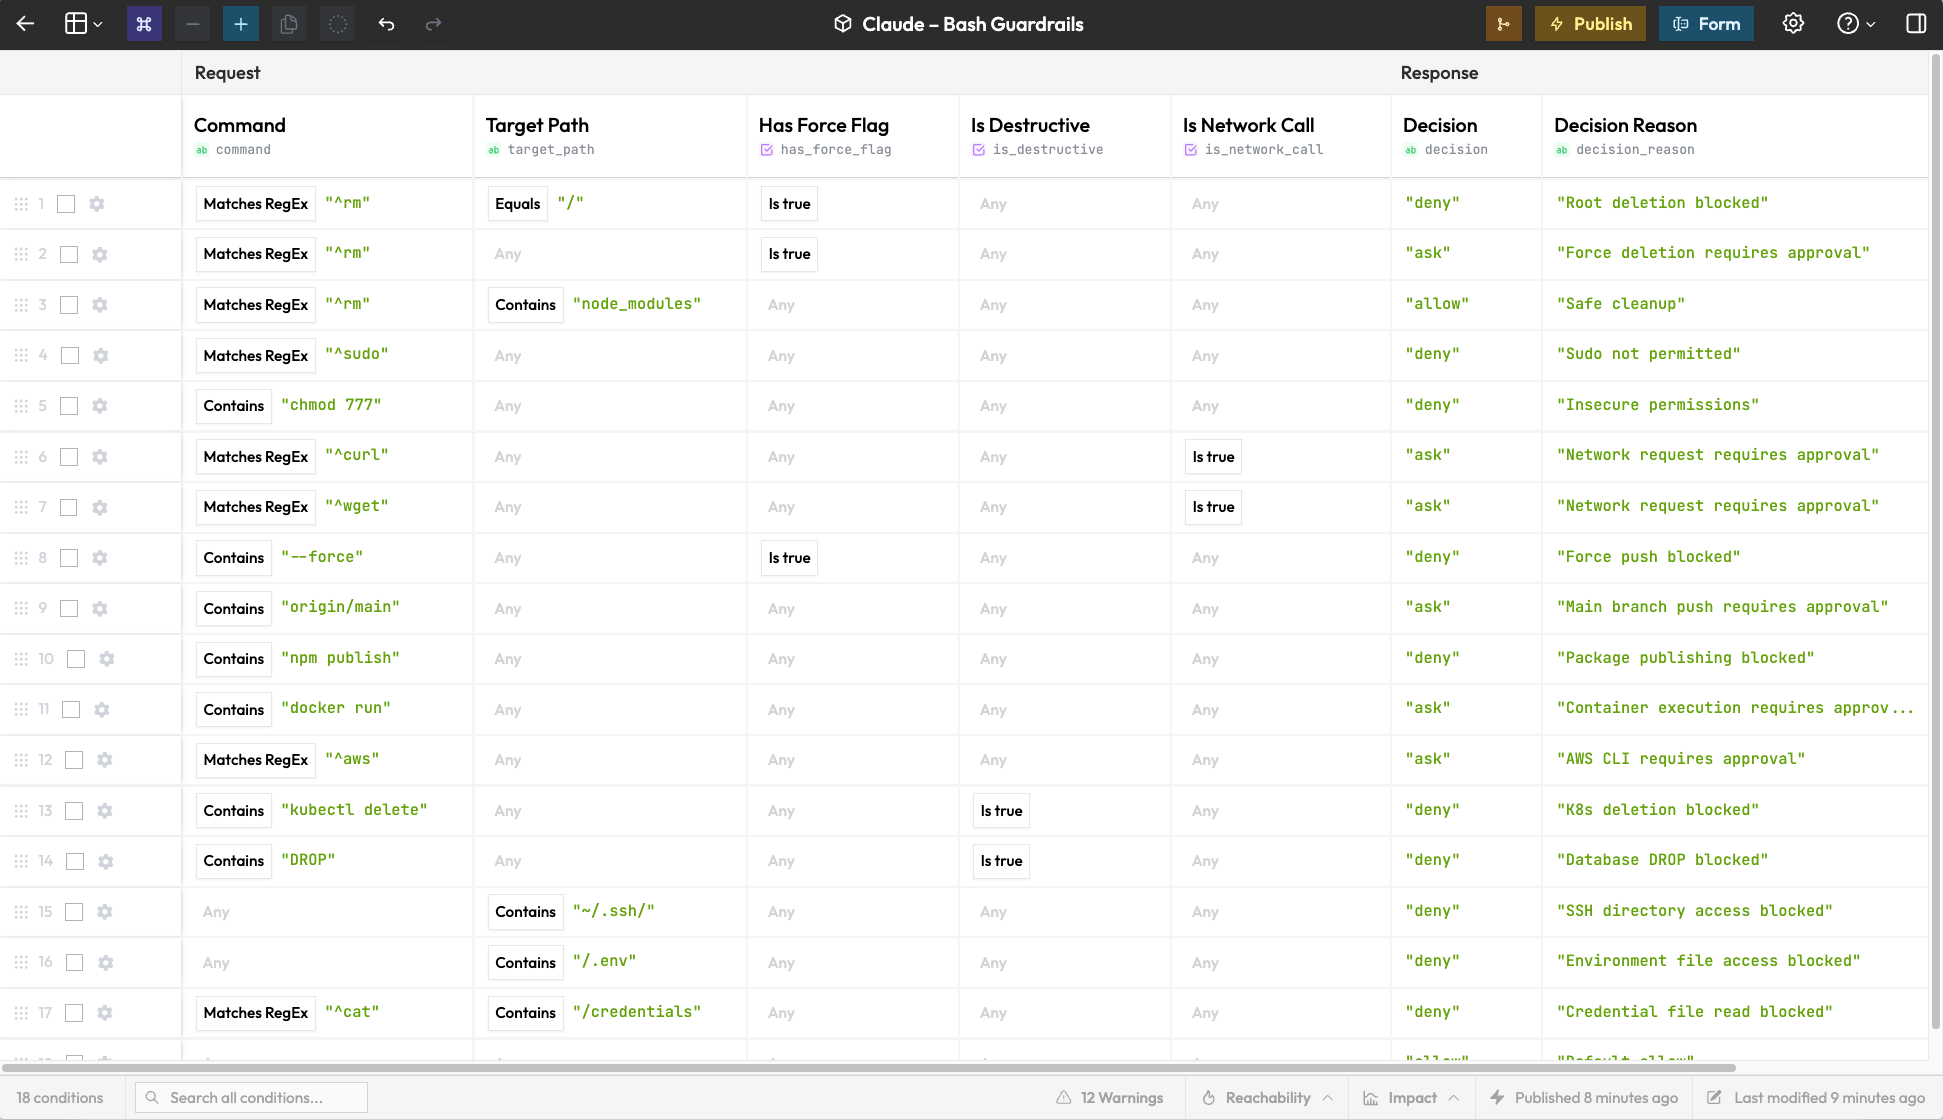 rulebricks/claude-code-guardrails
Real-time guardrails for Claude Code tool calls.
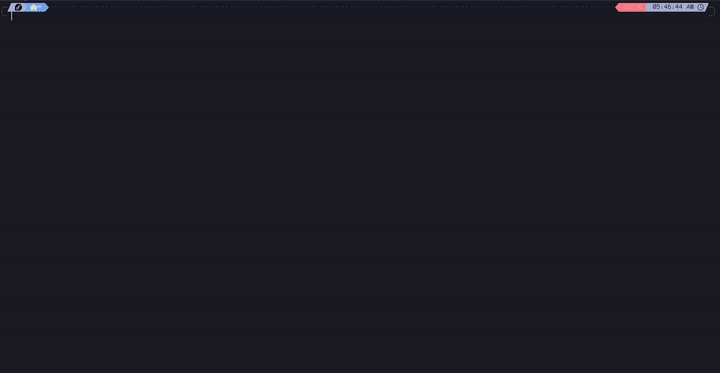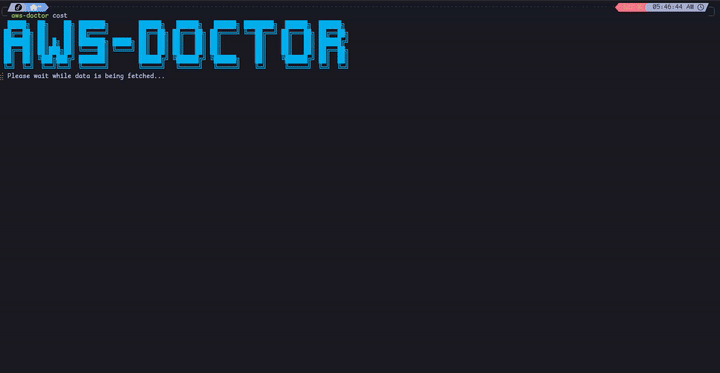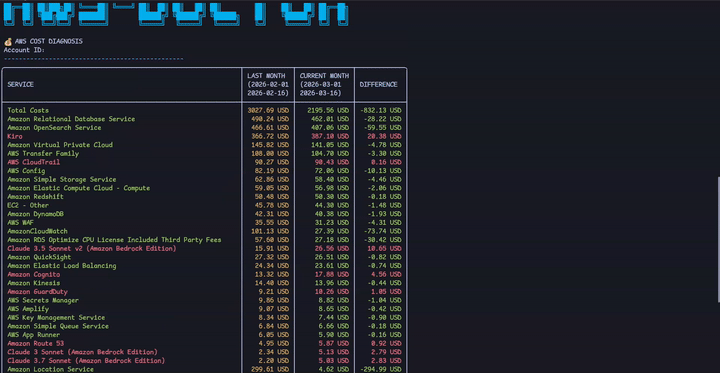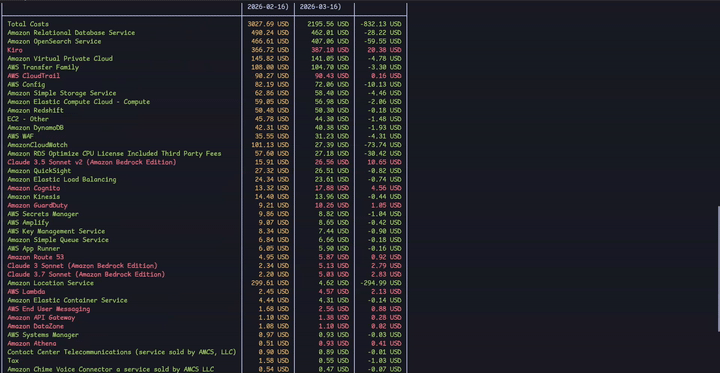 elc0mpa/aws-doctor
Powerful open-source CLI to audit security, costs, and best practices in AWS. 🩺 ☁️
 sap8899/reportly
AzureAD/EntraID user activity reporter for blue teams. Input a suspicious user and time frame to receive a detailed report of user info, actions, and…
 adamwhitehat/judge-jury-and-executable
A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…
 activecm/rita
Real Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.
 purp1ew0lf/blue-team-notes
You didn't think I'd go and leave the blue team out, right?
 gopasteverything/gpewebdefender
Lightweight web-attack monitor. One Go binary + SQLite. Not OSSEC, not a WAF.
 thomaspoppelgaard/netscaler-ctx697096-checker
Read-only checker for Citrix NetScaler CTX697096 (CVE-2026-88771–88778): verifies build, CVE preconditions and upgrade risks, and sweeps public IoCs…
 owasp/honeypot-project
Deploy web honeypots to capture emerging attack data, analyze ModSecurity audit logs via ELK, and share threat intelligence with MISP for…
 preflightsh/preflight
Go-based CLI tool that scans codebases for launch readiness, detecting missing configuration, security hygiene issues, secret leaks, and integration…
 wortell/log4j
Repo containing all info, scripts, etc. related to CVE-2021-44228
 sreckoskocilic/envocabulary
Trace every shell environment variable to its exact file and line origin. Audit shell configs for dead entries, duplicates, and orphaned files across…
 ziad-hsn/cpra
CPRA is a high-performance infrastructure monitoring system designed for platform teams managing large-scale microservice architectures. Built on…
 gmh5225/gatekeeper
Self-hosted SSH access gateway in Go with OIDC/LDAP auth, RBAC, MFA, session recording, audit export, encryption at rest, IP rules, and policy…
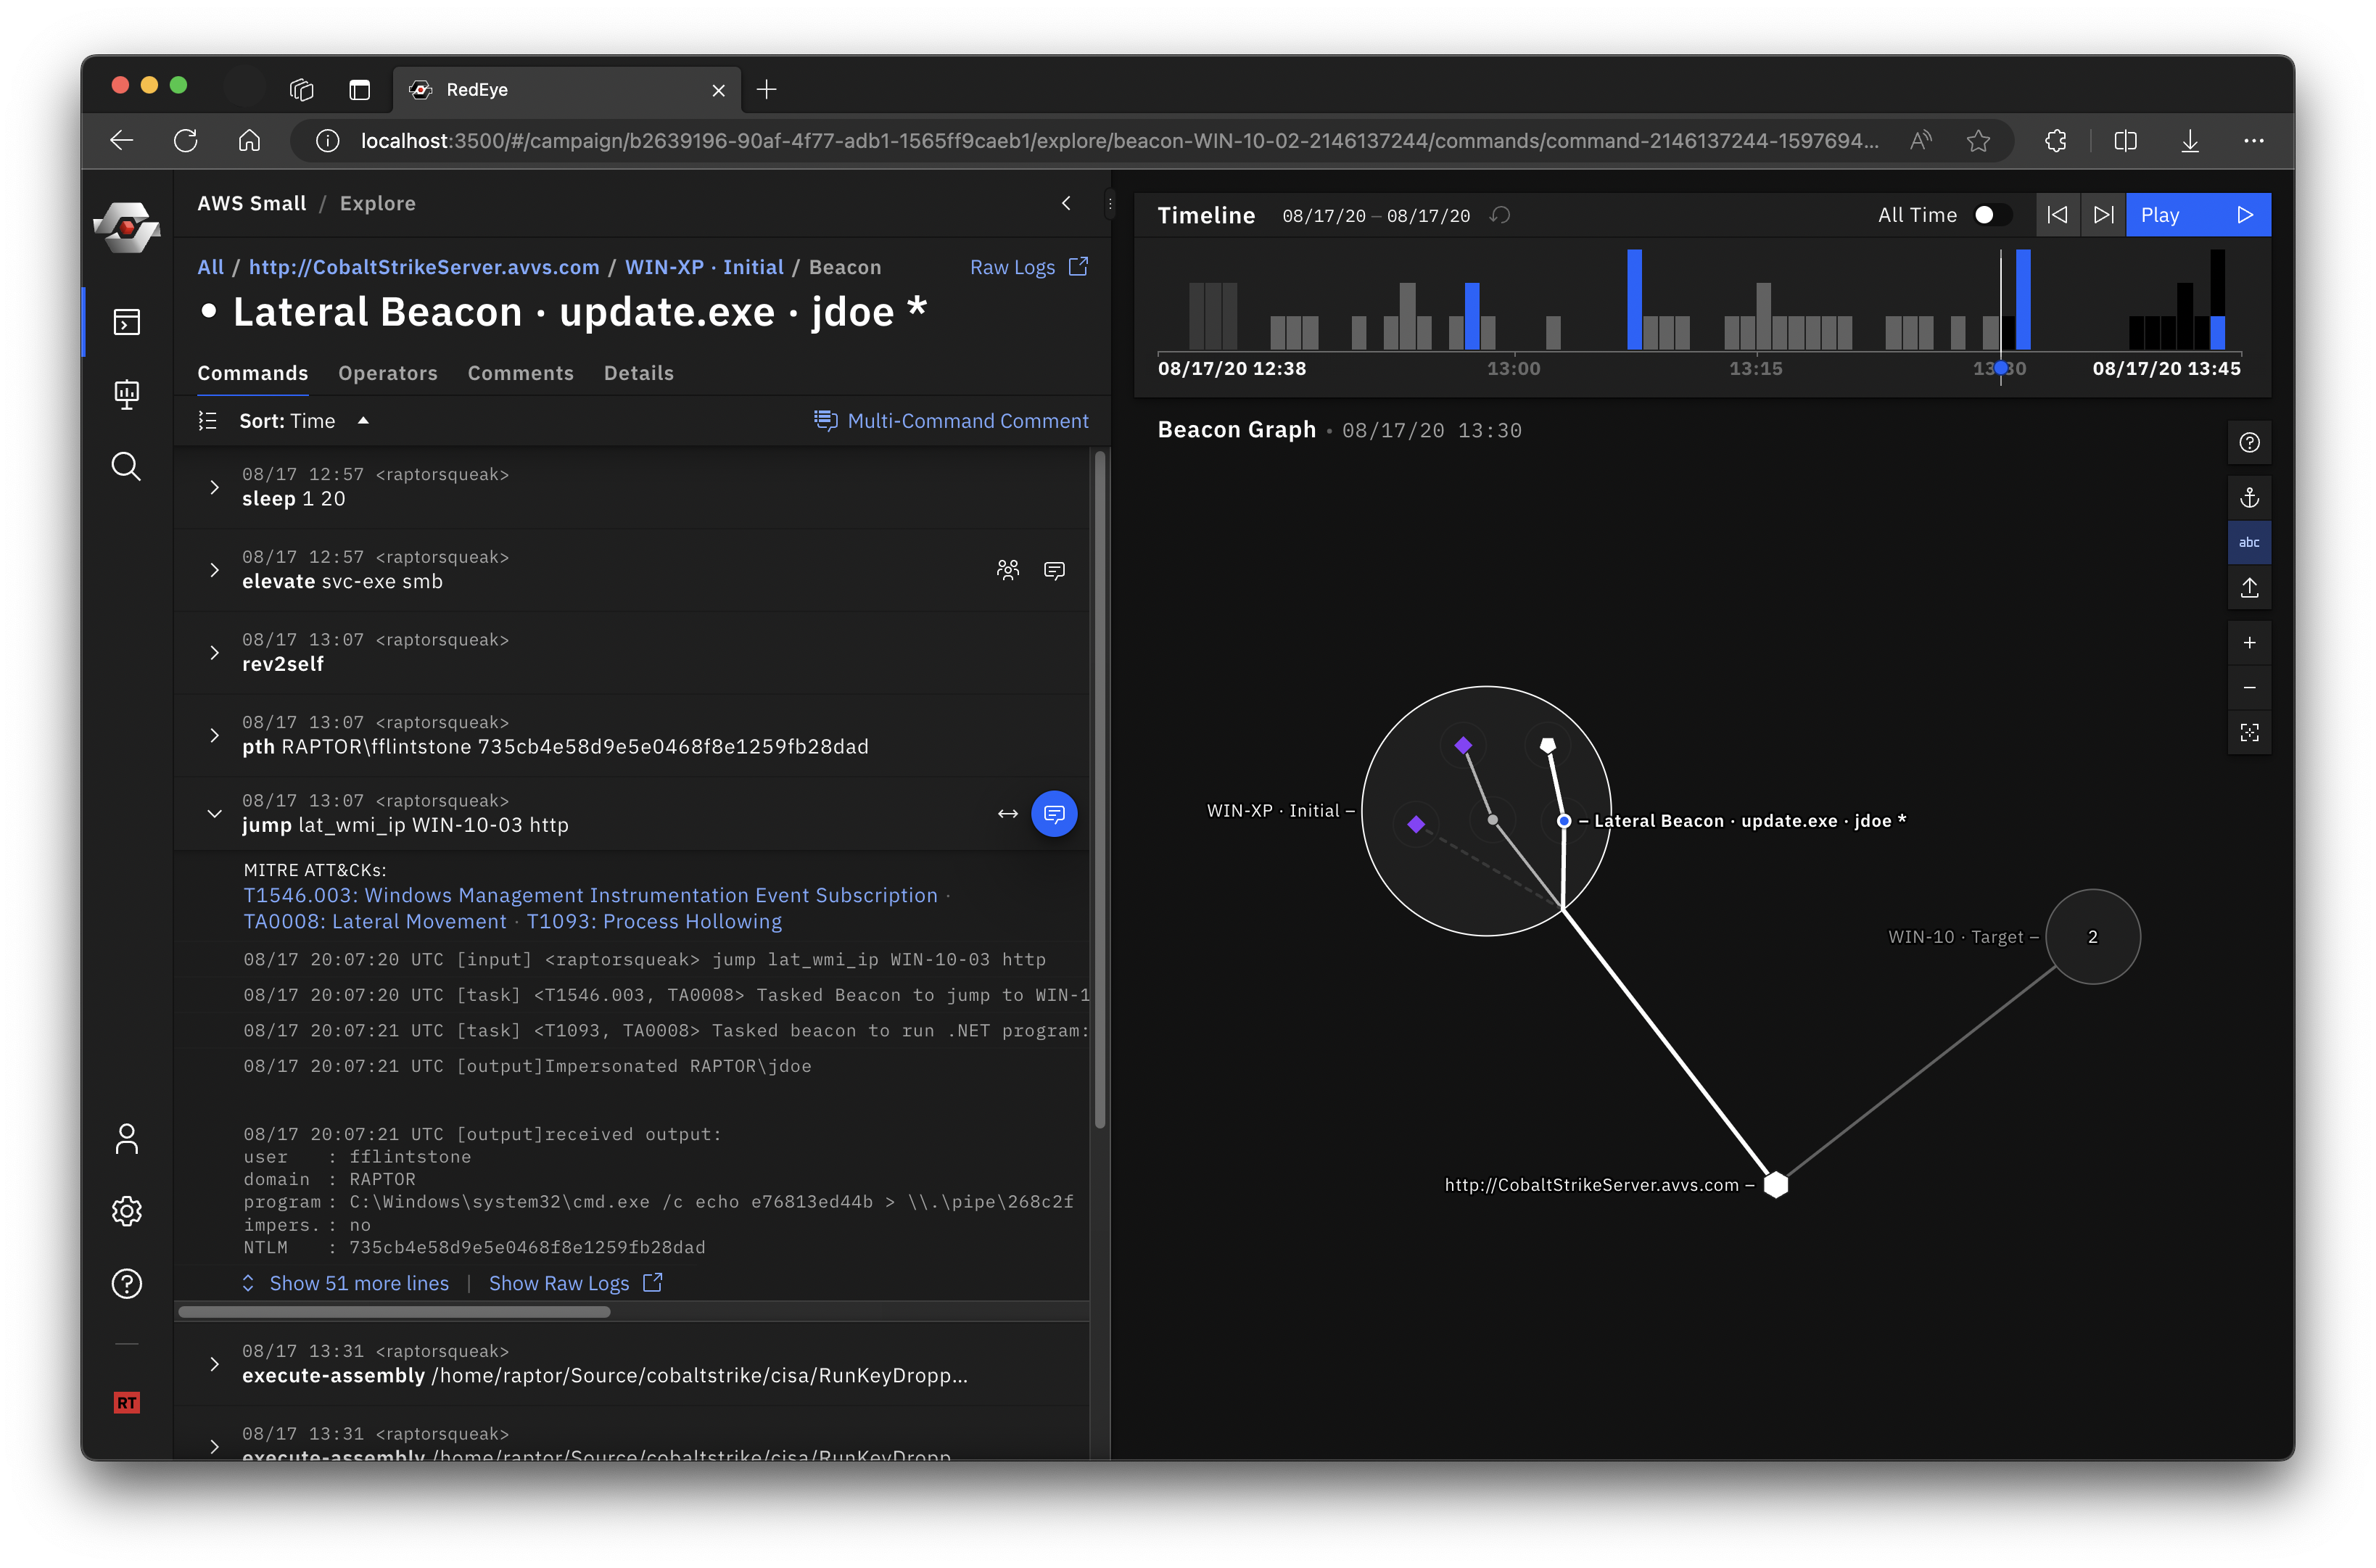 cisagov/redeye
RedEye is a visual analytic tool supporting Red & Blue Team operations
 cyb3rmik3/kql-threat-hunting-queries
A repository of KQL queries focused on threat hunting and threat detecting for Microsoft Sentinel & Microsoft XDR (Former Microsoft 365 Defender).
 schira4396/vcenterkiller
一款针对Vcenter的综合利用工具,包含目前最主流的CVE-2021-21972、CVE-2021-21985以及CVE-2021-22005、One Access的CVE-2022-22954、CVE-2022-22972/31656以及log4j,提供一键上传webshell,命令执行或者上传…