
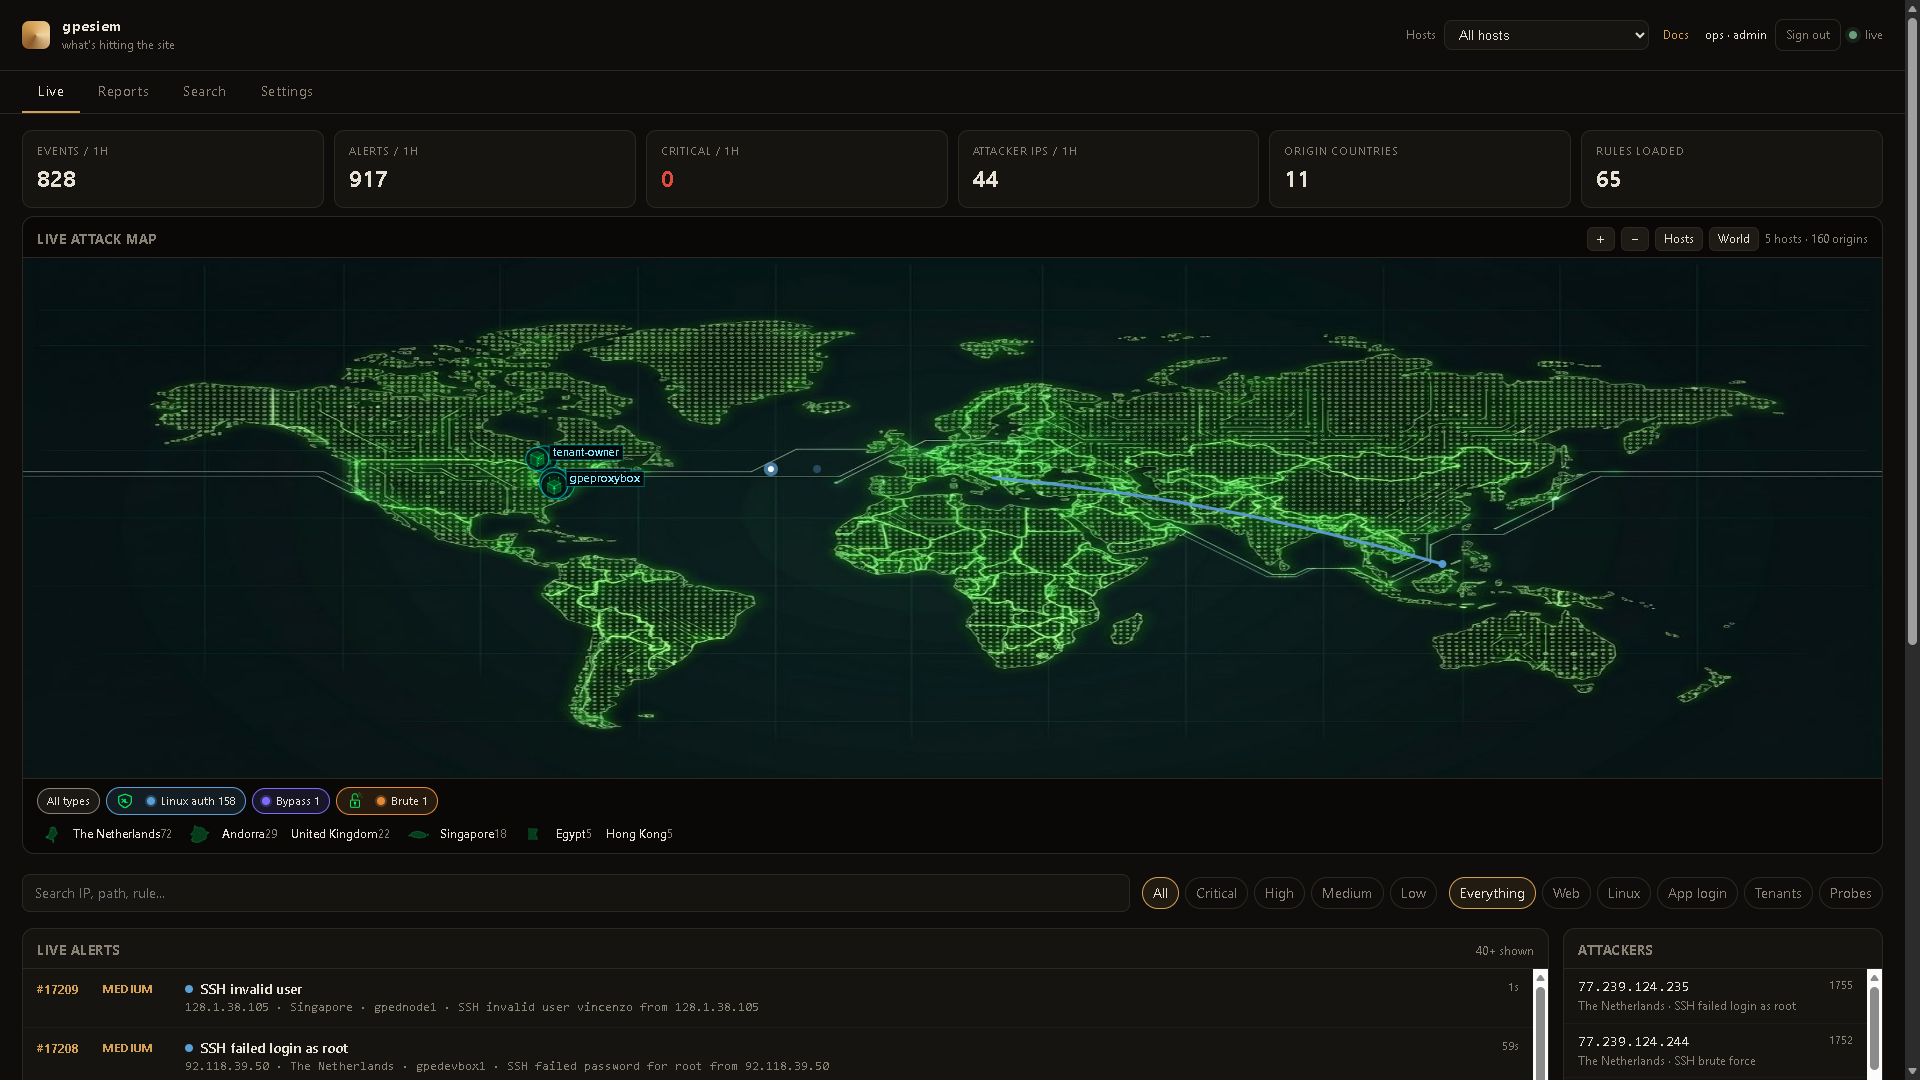
GPEWebDefender
 theretardedelon/gpewebdefender
Lightweight web-attack monitor. One Go binary + SQLite. Not OSSEC, not a WAF.
anomaly-detectiondefensive-toolsintrusion-detection+2
2
theretardedelon/gpewebdefenderLightweight web-attack monitor. One Go binary + SQLite. Not OSSEC, not a WAF.
 sleuthco/clawshield-public
Security proxy for AI agents. Scans every message for prompt injection, PII, and secrets. Defense-in-depth: Go proxy + iptables firewall + eBPF…
 phpboyscout/go/redact
Strip credential-like content from free-form strings before they reach logs or telemetry. Part of the phpboyscout Go toolkit. ·…
 gravitational/teleport
The easiest, and most secure way to access and protect all of your infrastructure.
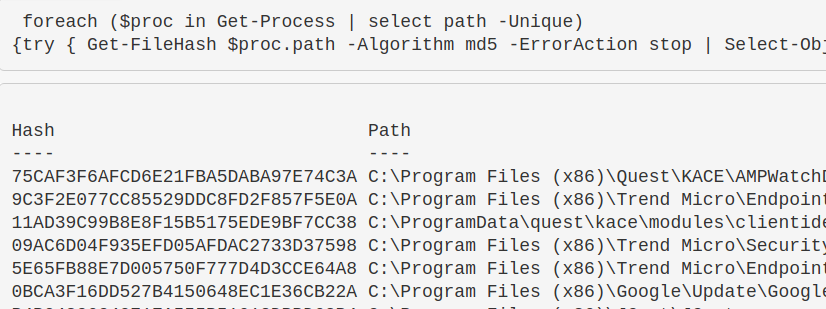 purp1ew0lf/blue-team-notes
You didn't think I'd go and leave the blue team out, right?
 fksvs/siper
XDP Based Lightweight and Fast Firewall
 runreveal/sigmalite
Go library for parsing and executing Sigma detection rules against log entries, supporting field modifiers, CIDR matching, and custom field resolvers…
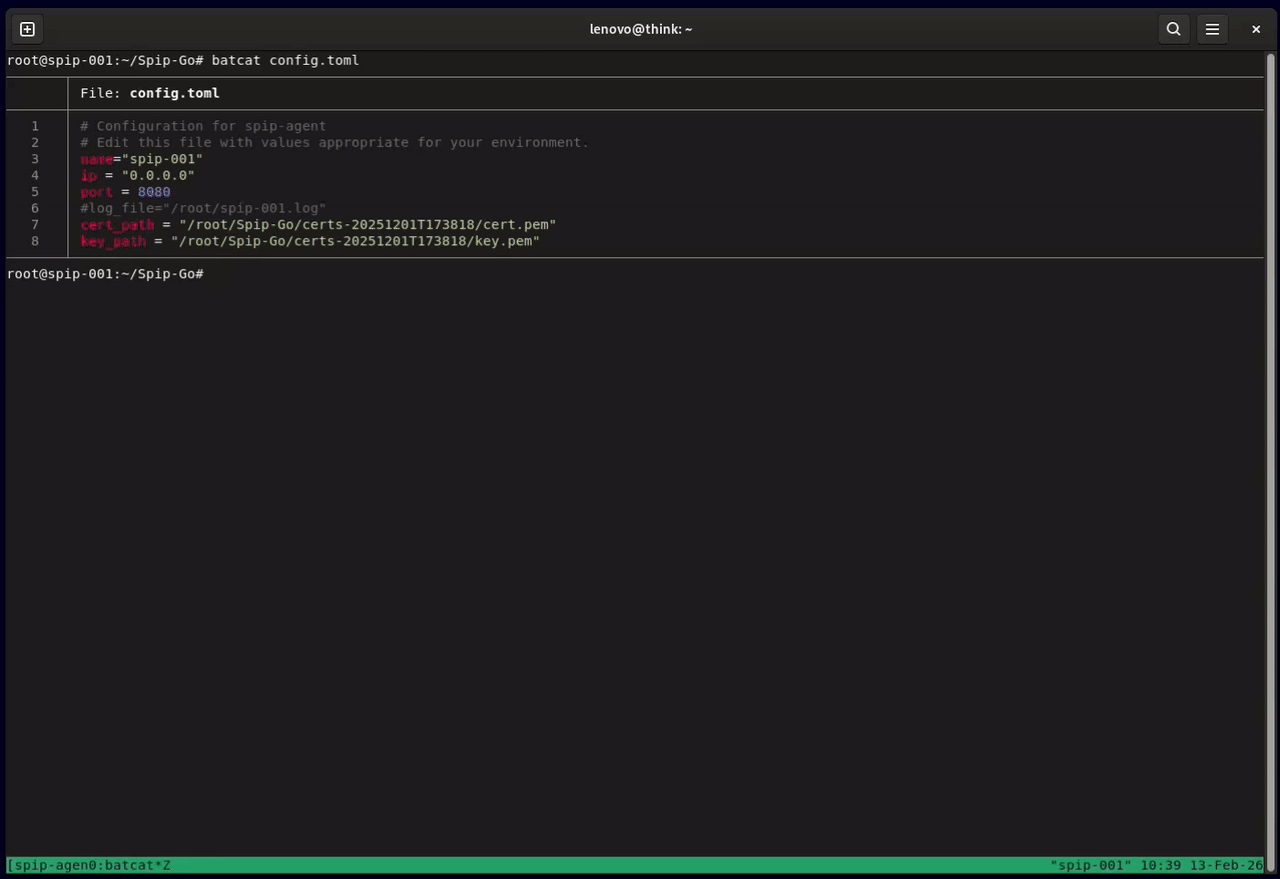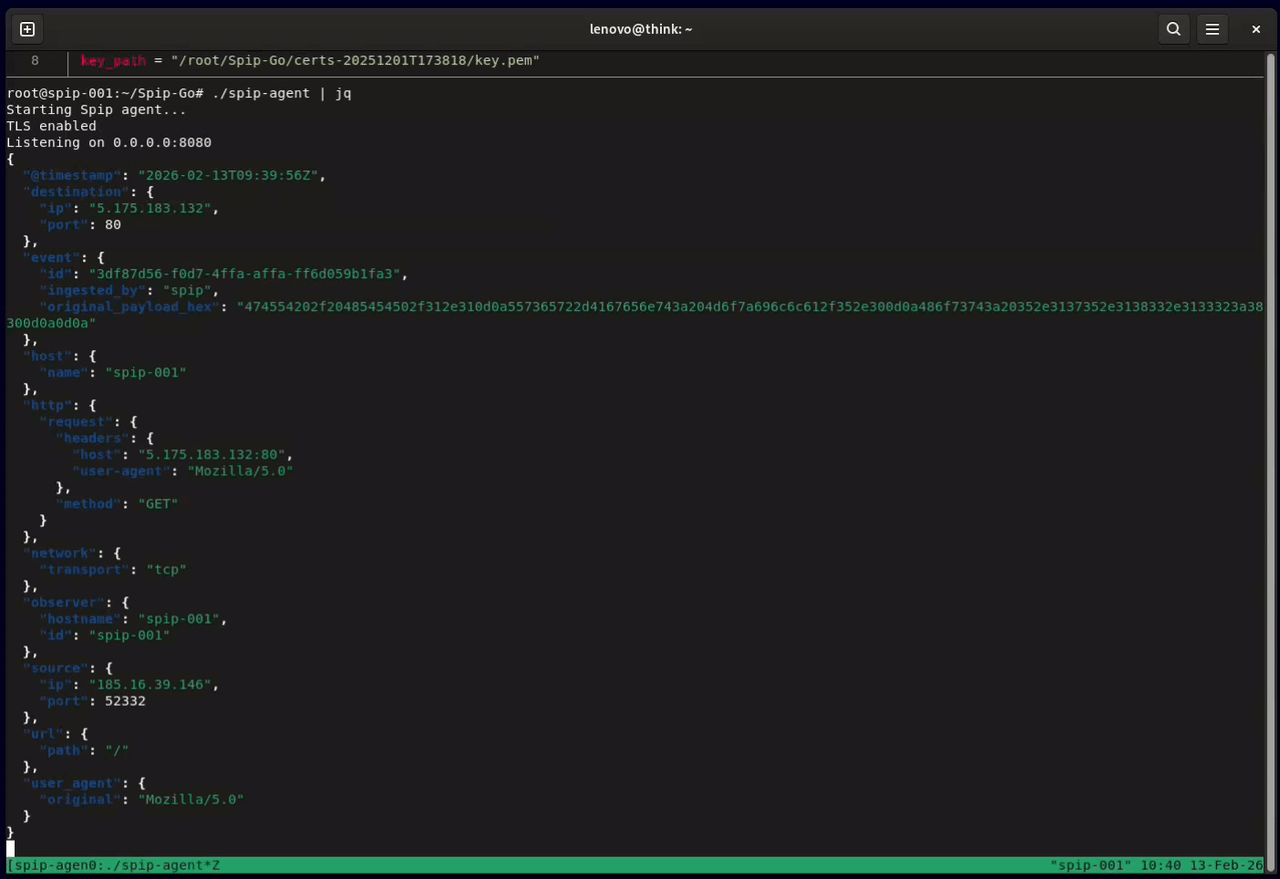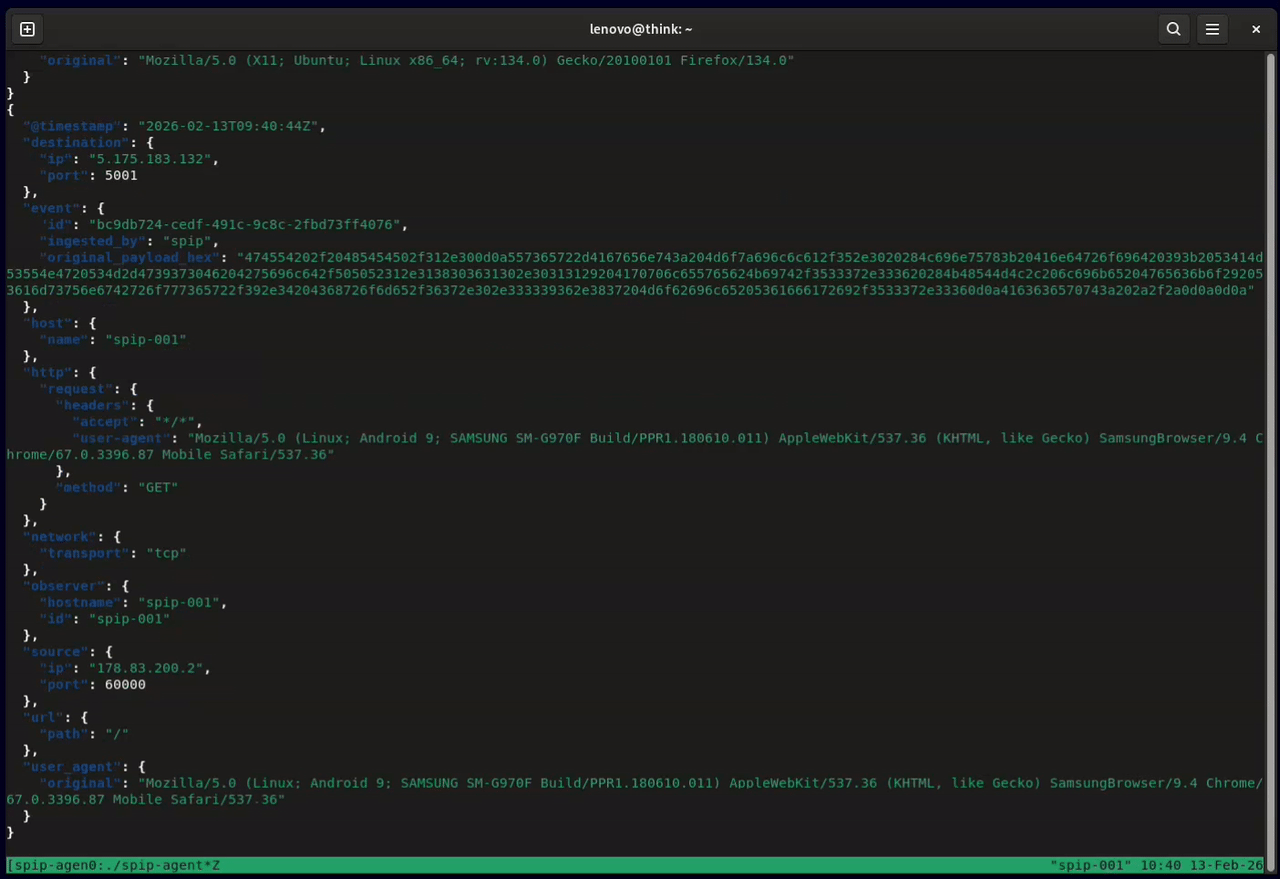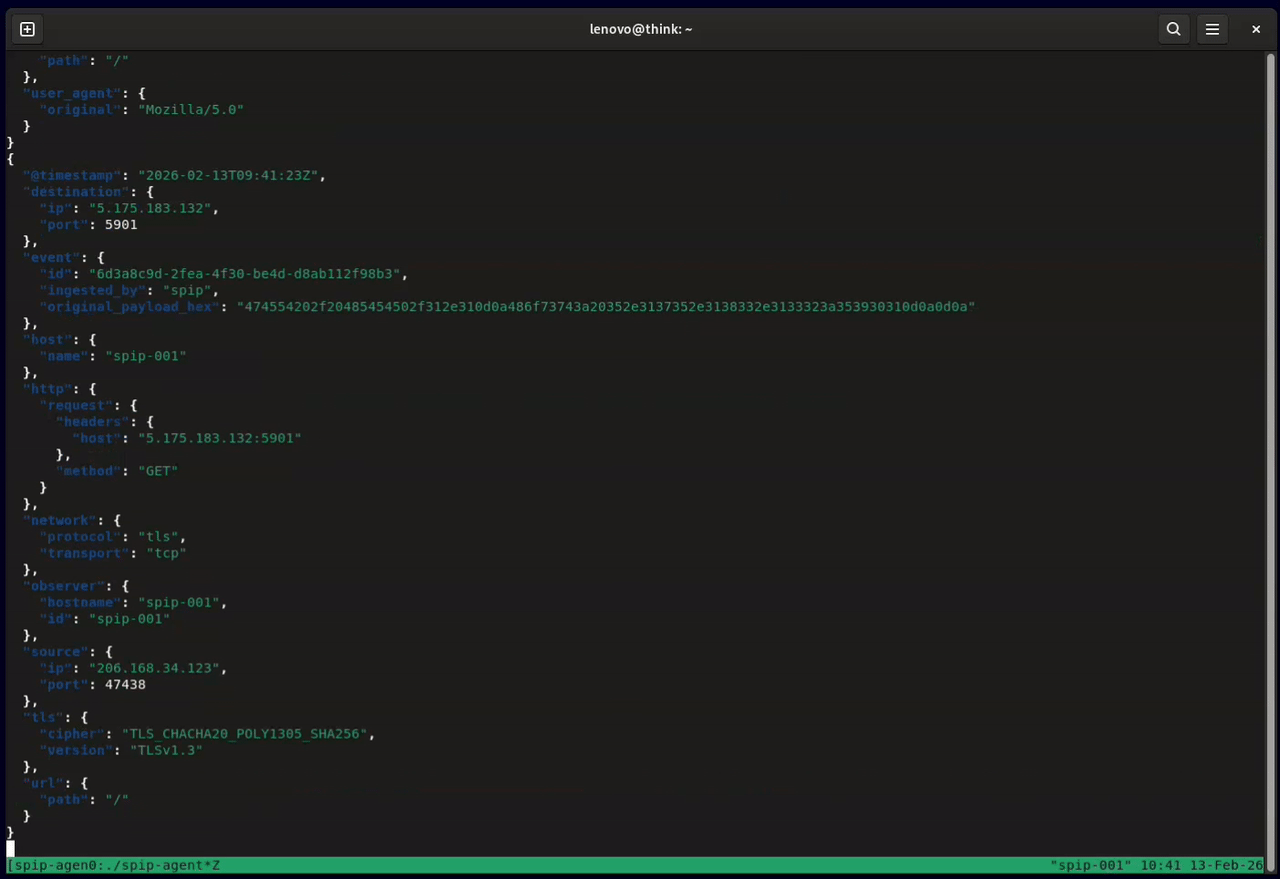 honeylabshq/spip-go
Spip network sensor written in Go
 1-bit-wonder/kestrel
Single-host runtime-security dashboard on eBPF — Go agent + SvelteKit. Live process tree, network map, and rule-based alerts for plain Linux hosts.
 gmh5225/gatekeeper
Self-hosted SSH access gateway in Go with OIDC/LDAP auth, RBAC, MFA, session recording, audit export, encryption at rest, IP rules, and policy…
 schira4396/vcenterkiller
一款针对Vcenter的综合利用工具,包含目前最主流的CVE-2021-21972、CVE-2021-21985以及CVE-2021-22005、One Access的CVE-2022-22954、CVE-2022-22972/31656以及log4j,提供一键上传webshell,命令执行或者上传…
 activecm/rita
Real Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.
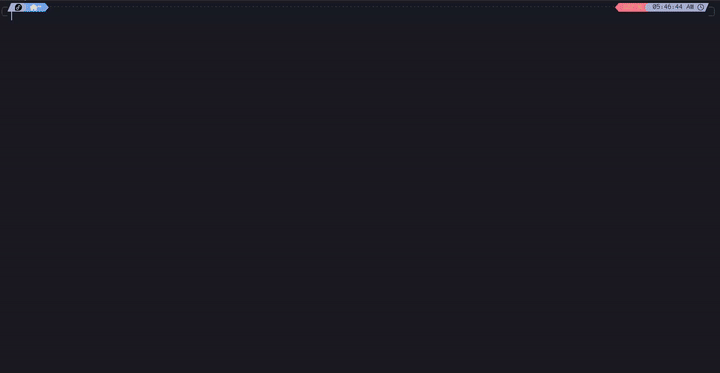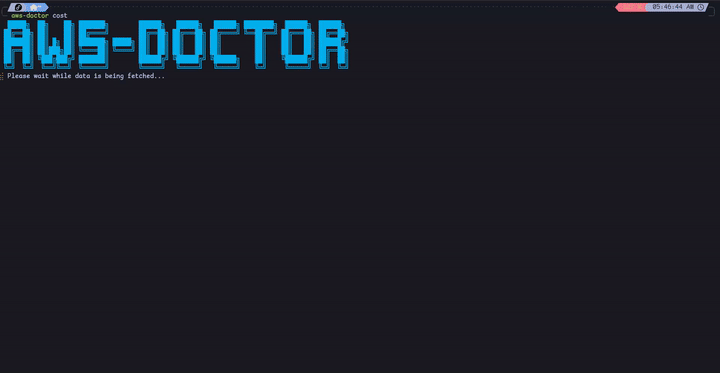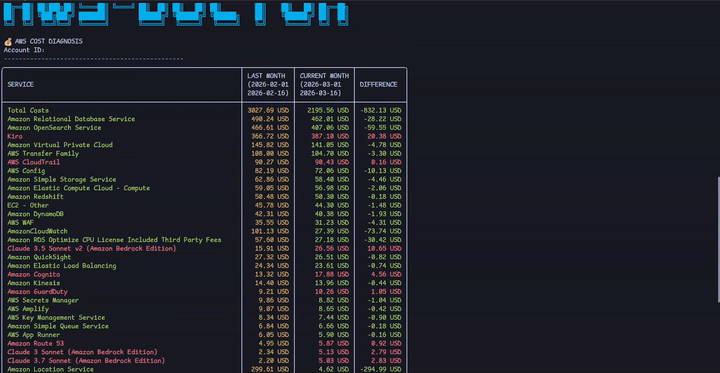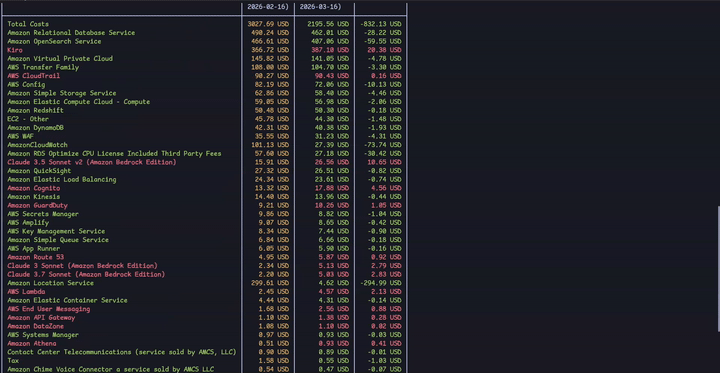 elc0mpa/aws-doctor
Powerful open-source CLI to audit security, costs, and best practices in AWS. 🩺 ☁️
 the-infra-company/kcatcher
Catch what's lurking in your Kafka clusters.
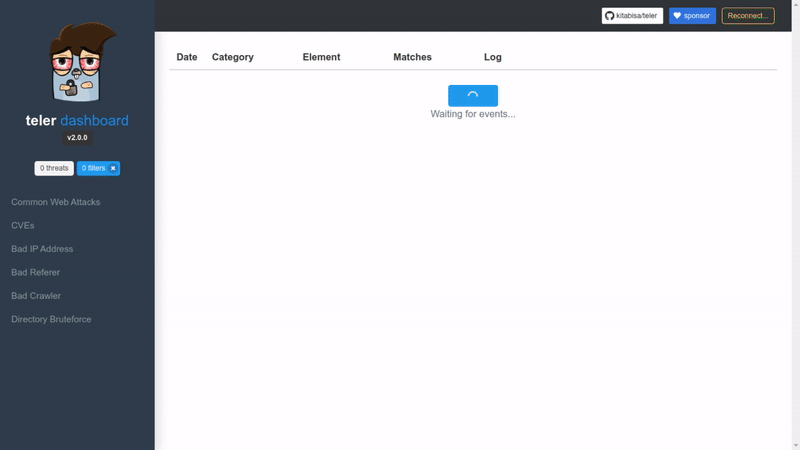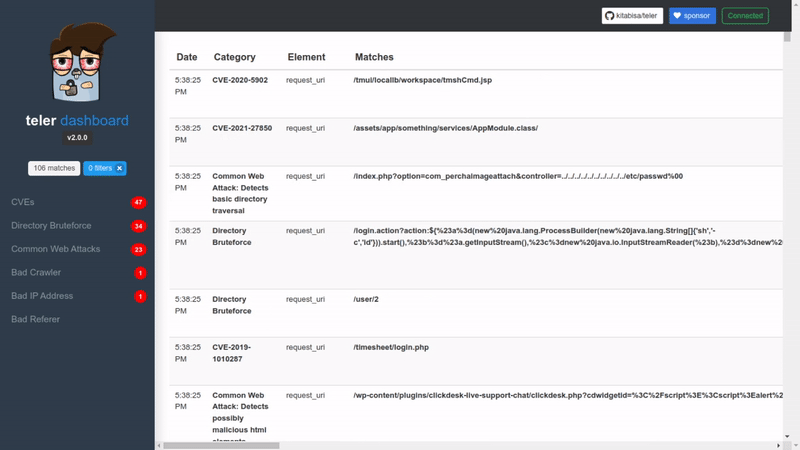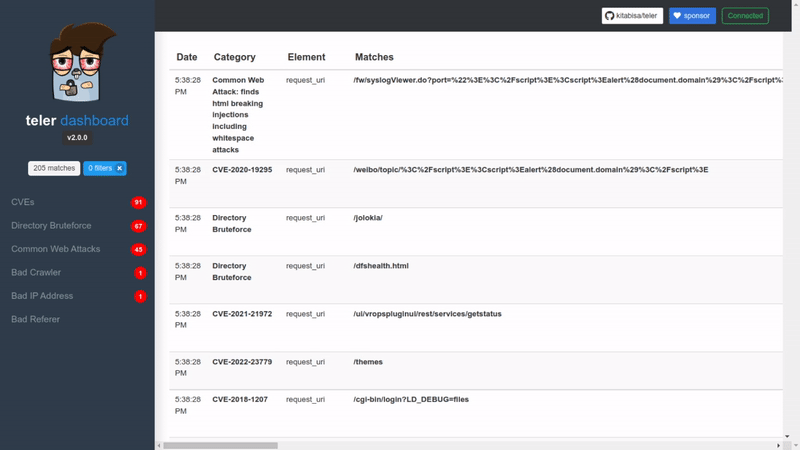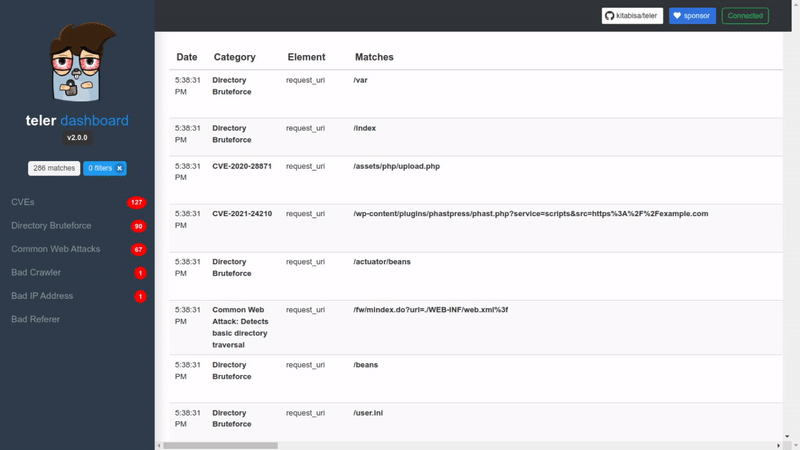 teler-sh/teler
Real-time HTTP Intrusion Detection
 kubeshark/kubeshark
eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…
 oisf/suricata
Open-source network IDS/IPS/NSM engine for real-time traffic inspection, intrusion detection and prevention, protocol analysis, and rule-based threat…
 ntop/ntopng
Web-based Traffic and Cybersecurity Network Traffic Monitoring