Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
662 results
awesome-incident-response preview

awesome-incident-response

GitHubmeirwah/awesome-incident-response

Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…

curated-resourcesdigital-forensicsdisk-forensics+9
9.4k
2 months ago
graylog2-server preview

graylog2-server

GitHubgraylog2/graylog2-server

Centralized log management platform for collecting, indexing, and analyzing streaming logs, with alerting and event correlation for security…

defensive-toolsincident-responseintrusion-detection+1
8.2k2 days ago
professional-services preview

professional-services

GitHubgooglecloudplatform/professional-services

Collection of Google Cloud solution examples and operational utilities for audit log monitoring, DLP de-identification, encryption key management,…

anomaly-detectionchaos-engineeringcloud-security+5
3.1k6 days ago
timesketch preview

timesketch

GitHubgoogle/timesketch

Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…

data-recoverydigital-forensicsdisk-forensics+7
3.4k2 days ago
Malcolm preview

Malcolm

GitHubcisagov/malcolm

Containerized network traffic analysis suite ingesting PCAP, Zeek logs, and Suricata alerts for automated normalization, enrichment, and correlation…

digital-forensicsdns-analysisforensics+9
2.5k12 days ago
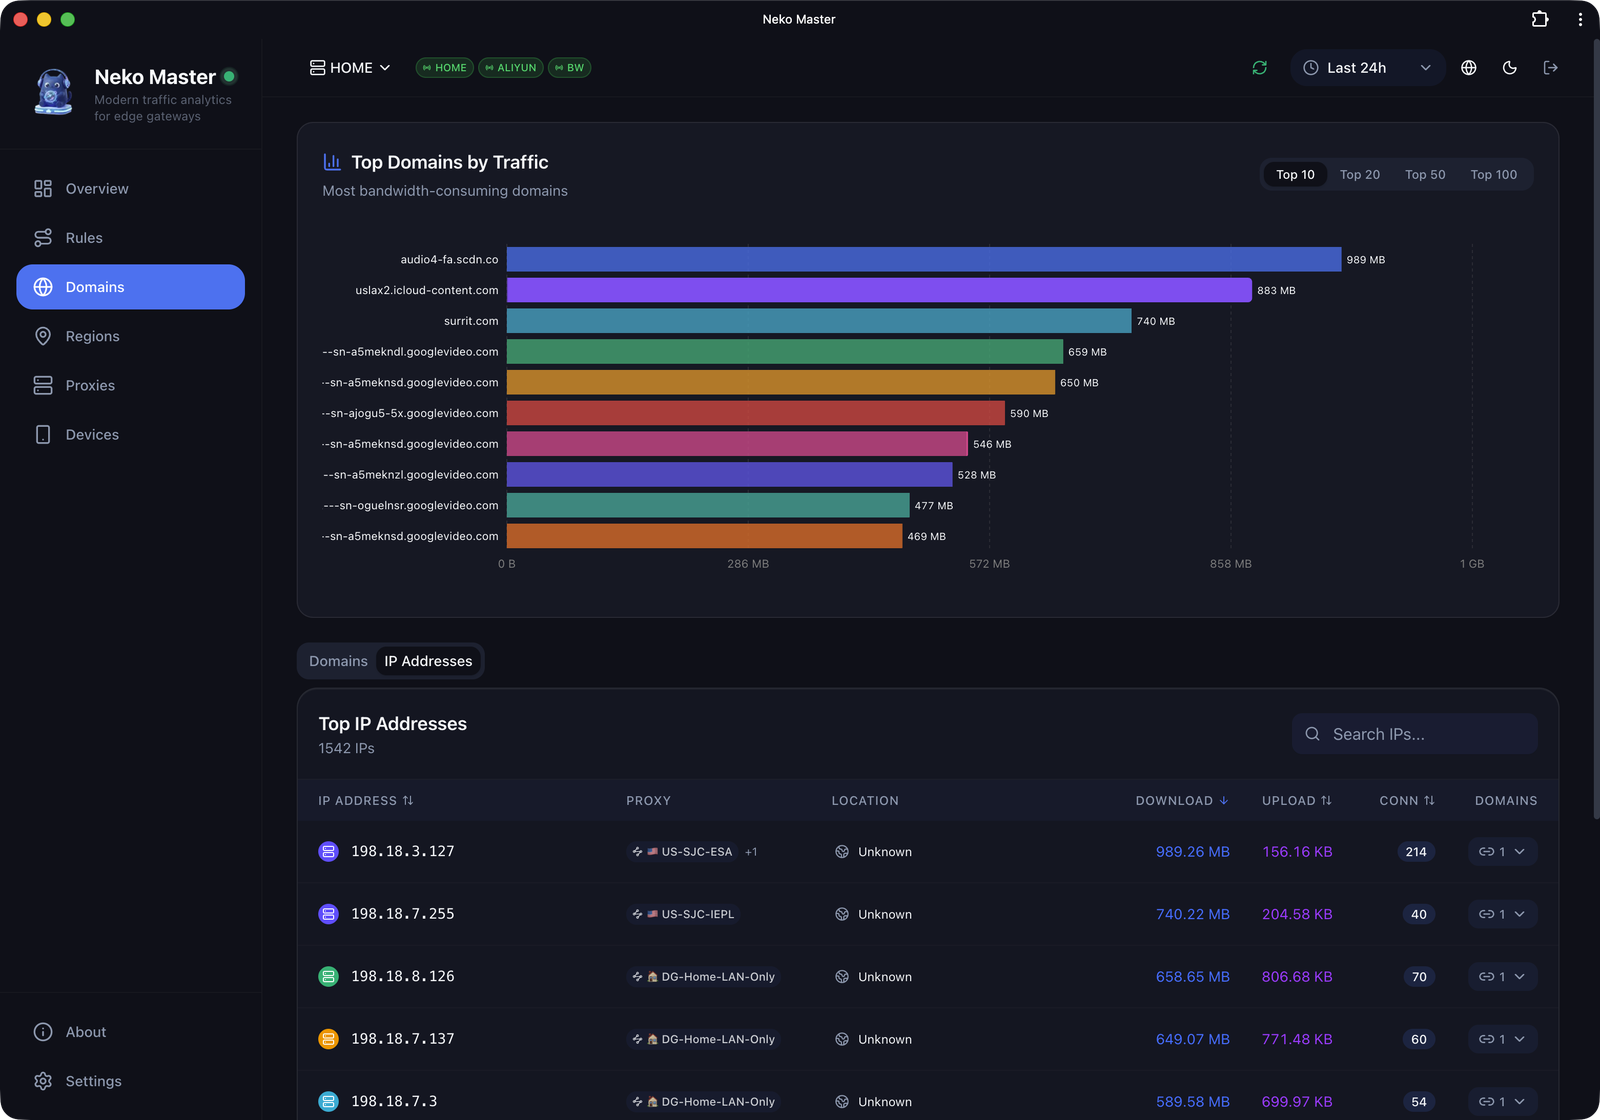
neko-master preview

neko-master

GitHubforu17/neko-master

A modern and elegant dashboard for network traffic visualization and analysis.

information-gatheringlog-analysisnetwork-mapping+3
4.1k3 days ago
KQL-threat-hunting-queries preview

KQL-threat-hunting-queries

GitHubcyb3rmik3/kql-threat-hunting-queries

A repository of KQL queries focused on threat hunting and threat detecting for Microsoft Sentinel & Microsoft XDR (Former Microsoft 365 Defender).

ctfcurated-resourceseducation+4
7994 days ago
OSSEM preview

OSSEM

GitHubotrf/ossem

Community-driven project for documenting, standardizing, and modeling security event logs to improve detection analytics and data normalization…

curated-resourceseducationlog-analysis+1
1.3k3 years ago
kunai preview

kunai

GitHubkunai-project/kunai

eBPF-based Linux security monitor and threat hunter providing chronologically ordered, container-aware events with on-host correlation for incident…

container-securitydefensive-toolsforensics+3
1.1k3 days ago
evtx preview

evtx

GitHubomerbenamram/evtx

A Fast (and safe) parser for the Windows XML Event Log (EVTX) format

digital-forensicsforensicsincident-response+1
9664 days ago
tenzir preview

tenzir

GitHubtenzir/tenzir

Collect, parse, normalize, aggregate, store, query, and route security telemetry data at scale using pipeline-based dataflows for threat detection…

incident-responselog-analysisnetwork-security+1
7621 day ago
awesome-soc-analyst preview

awesome-soc-analyst

GitHubletsdefend/awesome-soc-analyst

Useful resources for SOC Analyst and SOC Analyst candidates.

curated-resourcesdigital-forensicseducation+6
1.0k3 years ago
LOLRMM preview

LOLRMM

GitHubmagicsword-io/lolrmm

Curated catalog of Remote Monitoring and Management tools abused by threat actors, with YAML profiles, Sigma detection rules, and API access for…

curated-resourcesdefensive-toolseducation+6
4036 days ago
CVE-2021-44228-Scanner preview

CVE-2021-44228-Scanner

GitHublogpresso/cve-2021-44228-scanner

Vulnerability scanner and mitigation patch for Log4j2 CVE-2021-44228

configuration-auditingincident-responselog-analysis+3
8624 years ago
Incident-Response-Powershell preview

Incident-Response-Powershell

GitHubbert-janp/incident-response-powershell

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…

digital-forensicsdisk-forensicsforensics+6
8214 months ago
rita preview

rita

GitHubactivecm/rita

Real Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.

anomaly-detectioncommand-and-controldns-analysis+4
6593 months ago
L3MON preview

L3MON

GitHubd3vl/l3mon

Web-based network monitoring system providing real-time bandwidth tracking, server performance metrics, and customizable alerts for proactive network…

log-analysisnetwork-mappingnetwork-security
2973 years ago
Adama preview

Adama

GitHubrandomuserid/adama

Searches For Threat Hunting and Security Analytics

incident-responselog-analysisthreat-feeds-aggregators+1
2371 year ago
Previous1…567…37Next