
quietos-sentinel
 jondean213-pixel/quietos-sentinel
Sentinel — DeanWay Labs' inbound governor. Guards what an AI agent hears: world content is data, never orders. The mirror of QuietOS.
ai-securitydefensive-toolsincident-response+2
2
jondean213-pixel/quietos-sentinelSentinel — DeanWay Labs' inbound governor. Guards what an AI agent hears: world content is data, never orders. The mirror of QuietOS.
 jithinkrishnanrs/gitlab-cve-2026-85706-ioc
CVE-2026-85706 — GitLab Path Traversal IOC Scanner & Detection Toolkit. Detect and hunt for exploitation of the critical unauthenticated GitLab CE/EE…
 corelight/extendintel
This package extends the Intel package to log more fields
 virologi-info/papercut-toolkit
#PaperCut CVE-2026-81578 + CVE-2026-82078 Defense Toolkit 2 3 A **defensive** toolkit to check and understand exposure to the chained
 confused-binary/waf-fu
Terminal UI for browsing and replaying AWS WAF v2 logs from CloudWatch, S3, and the sampling API, with YAML filtering, auth detection, and…
 danielwep/cve-netscalerfilesystemcheck
This script checks the Citrix Netscaler if it has been compromised by CVE-2019-19781 attacks and collects all file system information
 adham504/sentinelthread-forensics
High-speed Windows forensic triage platform that orchestrates the Hayabusa engine to transform raw EVTX logs into prioritized threat timelines with…
 vdisec/cve-2019-19871-auditguide
Audit Guide for the Citrix ADC Vulnerability CVE-2019-19871. Collected from multiple sources and threat assessments. Will be updated as new methods…
 phpboyscout/go/redact
Strip credential-like content from free-form strings before they reach logs or telemetry. Part of the phpboyscout Go toolkit. ·…
 3tternp/cve-2026-41940---cpanel-whm-check
This is the office check script provided by cPanel for all the users who are using cPanel
 corelight/zeek-endpoint-enrichment-conn
Enrich the conn.log with EDR data
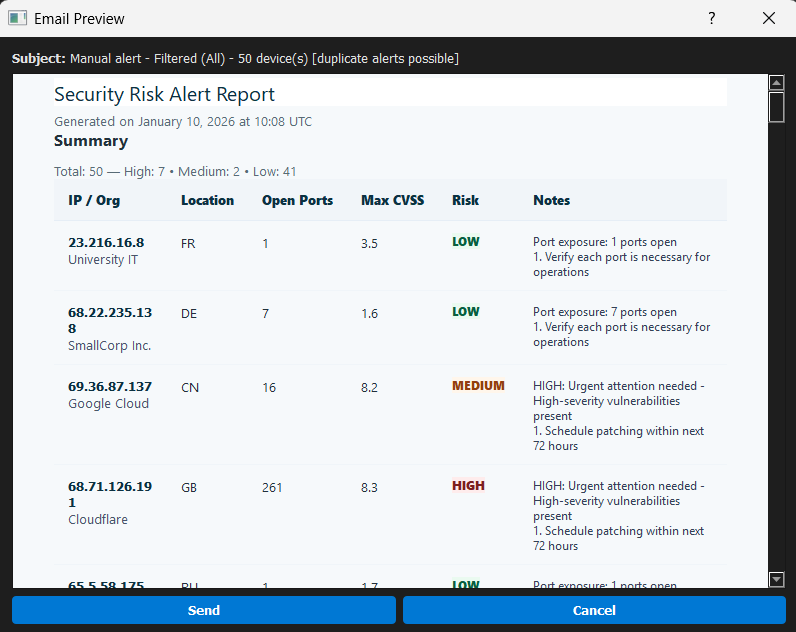 eclipsemanic/threatsentry-ai
ThreatSentry AI is an intelligent threat hunting dashboard that leverages machine learning to proactively identify and prioritize risks in your…
 mrk336/cluster-chaos-exploiting-cve-2025-59359-for-kubernetes-takeover
A hands-on forensic walkthrough of CVE-2025-59359, a critical OS command injection flaw in Chaos-Mesh. Learn how attackers hijack Kubernetes clusters…
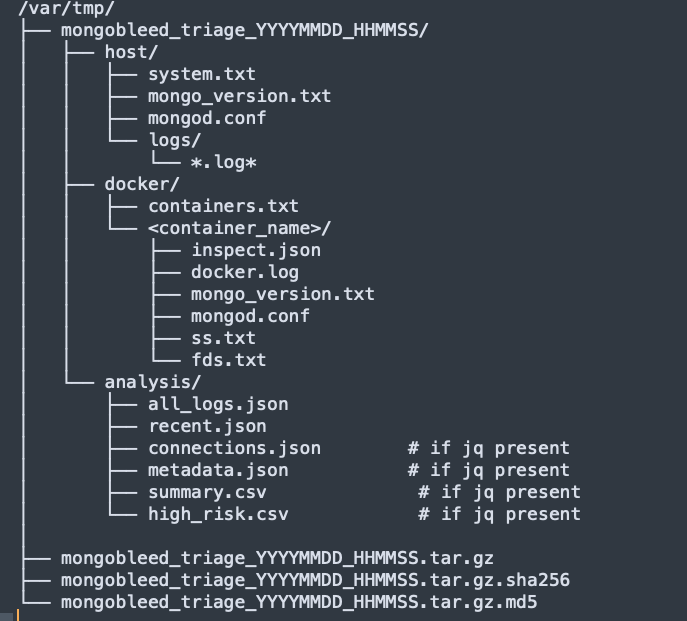 jemhadar/mongobleed-dfir-triage-script-cve-2025-14847
The script focuses on safe artifact acquisition first, followed by optional on-host analysis, and produces a portable, hashed forensic archive…
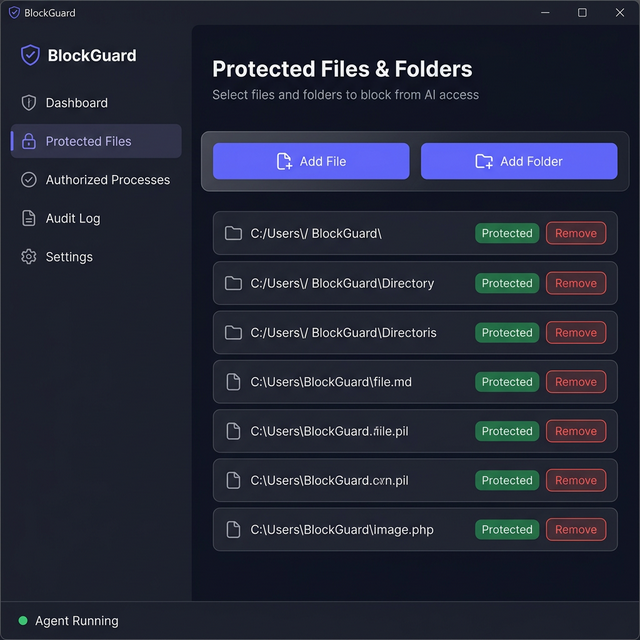 m2l33k/blockguard
BlockGuard is a Windows Data Loss Prevention (DLP) agent that intercepts and controls file access at the process level. It ensures that only…
 s0/rsyslog-librelp-cve-2018-1000140-fixed
Patch for CVE-2018-1000140 in rsyslog's librelp library, fixing a remote code execution vulnerability in the reliable event logging protocol…
 l4r1k/citrixnetscaleranalysis
🔬 Jupyter notebook to help automate some of the forensic analysis related to Citrix Netscalers compromised via CVE-2019-19781
 alexpena5635/cve-2021-44228_scanner-main-modified-
Scans jar, war, and ear files for the presence of JndiLookup.class to detect applications vulnerable to CVE-2021-44228 (Log4Shell).