cve-2019-6340-bits
 josehelps/cve-2019-6340-bits
Bits generated while analyzing CVE-2019-6340 Drupal RESTful RCE
exploitationinformation-gatheringlog-analysis+3
josehelps/cve-2019-6340-bitsBits generated while analyzing CVE-2019-6340 Drupal RESTful RCE
 randomrobbiebf/cve-2023-47668
Restrict Content <= 3.2.7 - Information Exposure via legacy log file
 intel-xeon/cve-2021-44228---detection-with-powershell
PowerShell-based scanner to detect Log4j CVE-2021-44228 vulnerability by searching directories and log files for exploitation indicators.
 rv4l3r3/log4v-vuln-check
This script is used to perform a fast check if your server is possibly affected by CVE-2021-44228 (the log4j vulnerability).
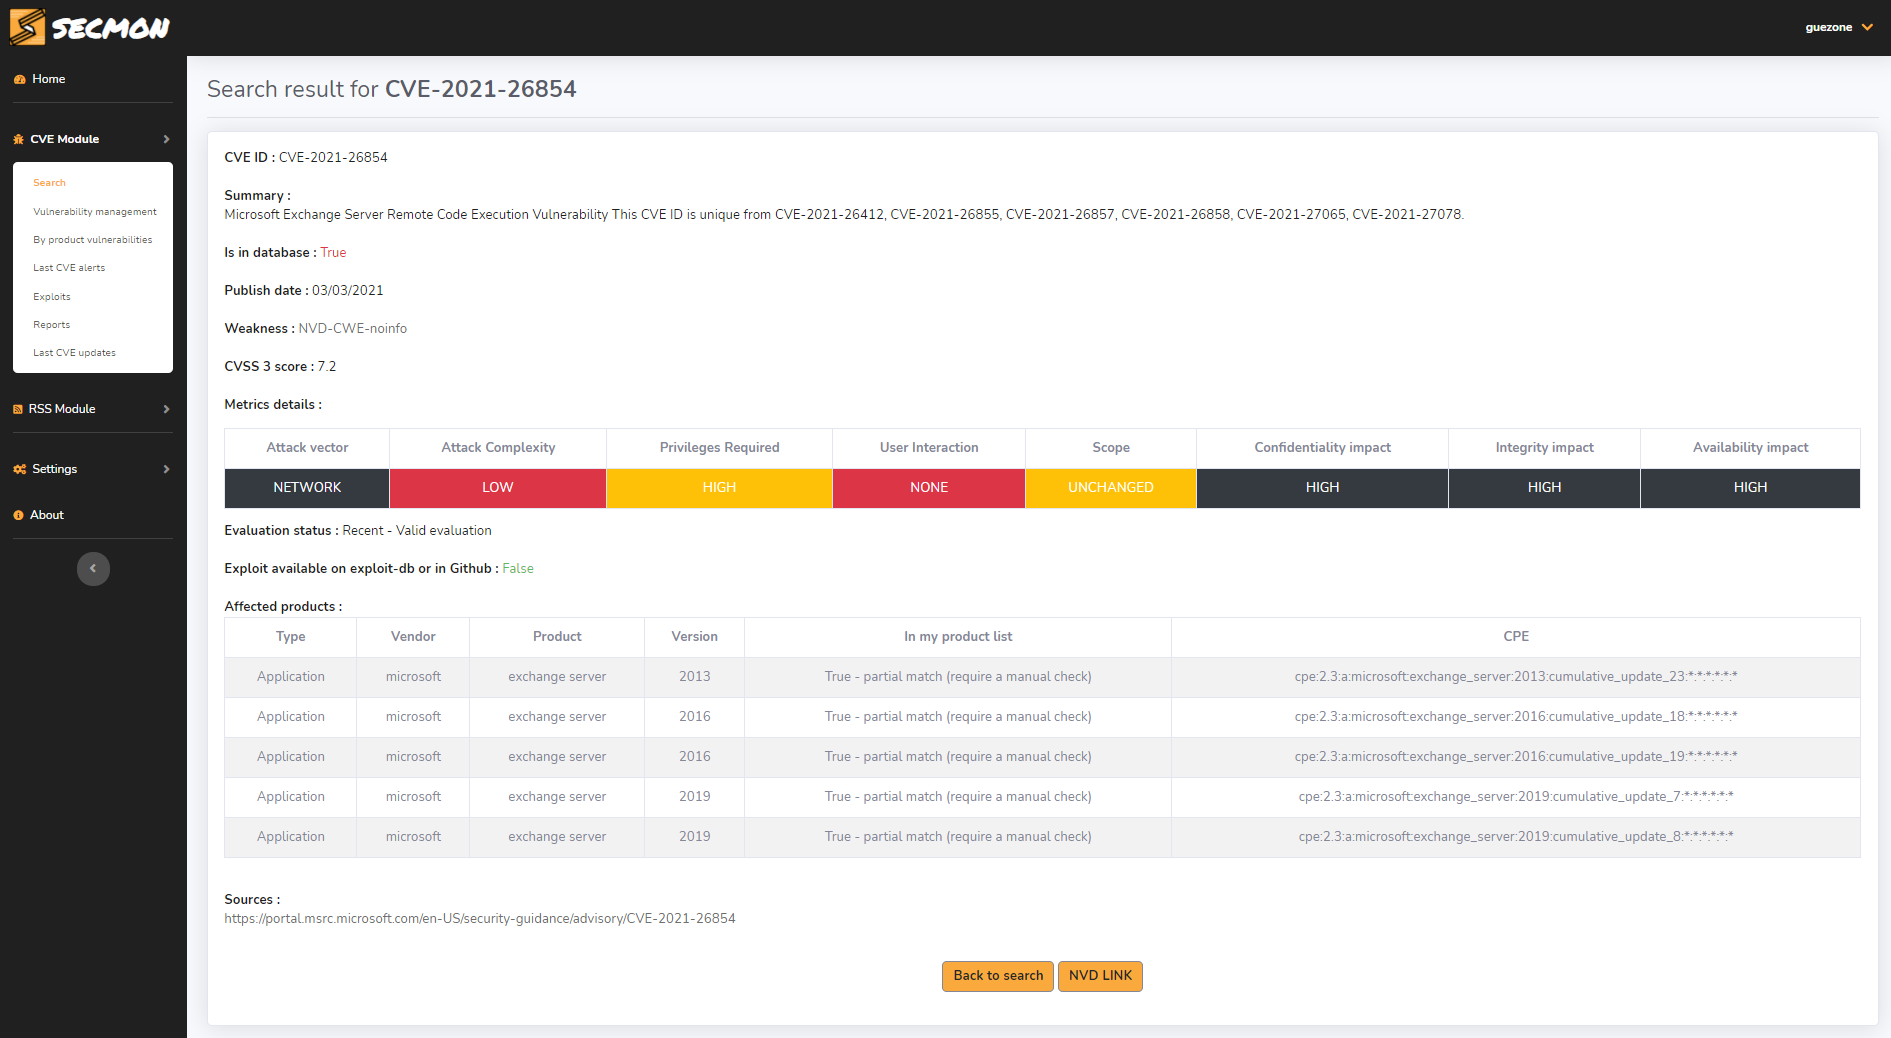 alb-uss/secmon
SECMON is a web-based tool for the automation of infosec watching and vulnerability management with a web interface.
 phpatch/weblogchecker
Free access-log compromise analyzer: webshell interactions, exploitation patterns and brute-force bursts in your Apache/nginx logs - severity,…
 0xajstrike/opcuatrap
High-interaction OPC UA honeypot for ICS/SCADA — multi-profile (oil & gas, water, power grid), live process simulation, per-session threat scoring,…
 dragon-lady/netward-standalone
User-space bot and DDoS deflection for small HTTP services
 tnich/honssh
HonSSH is designed to log all SSH communications between a client and server.
 g0tmi1k/kippo-g0tmi1k
Medium-interaction SSH honeypot that logs brute force attacks and full attacker shell interactions, with customization options to reduce…
 playtikaoss/leaktopus
Automated secret and leak detection scanner for GitHub and paste sites, with heuristic filtering, IOL enrichment via Shhgit/TruffleHog, and ELK-based…
 kolya5544/bearftp
Honeypot FTP server written in .NET Core (C#) for both Linux and Windows.
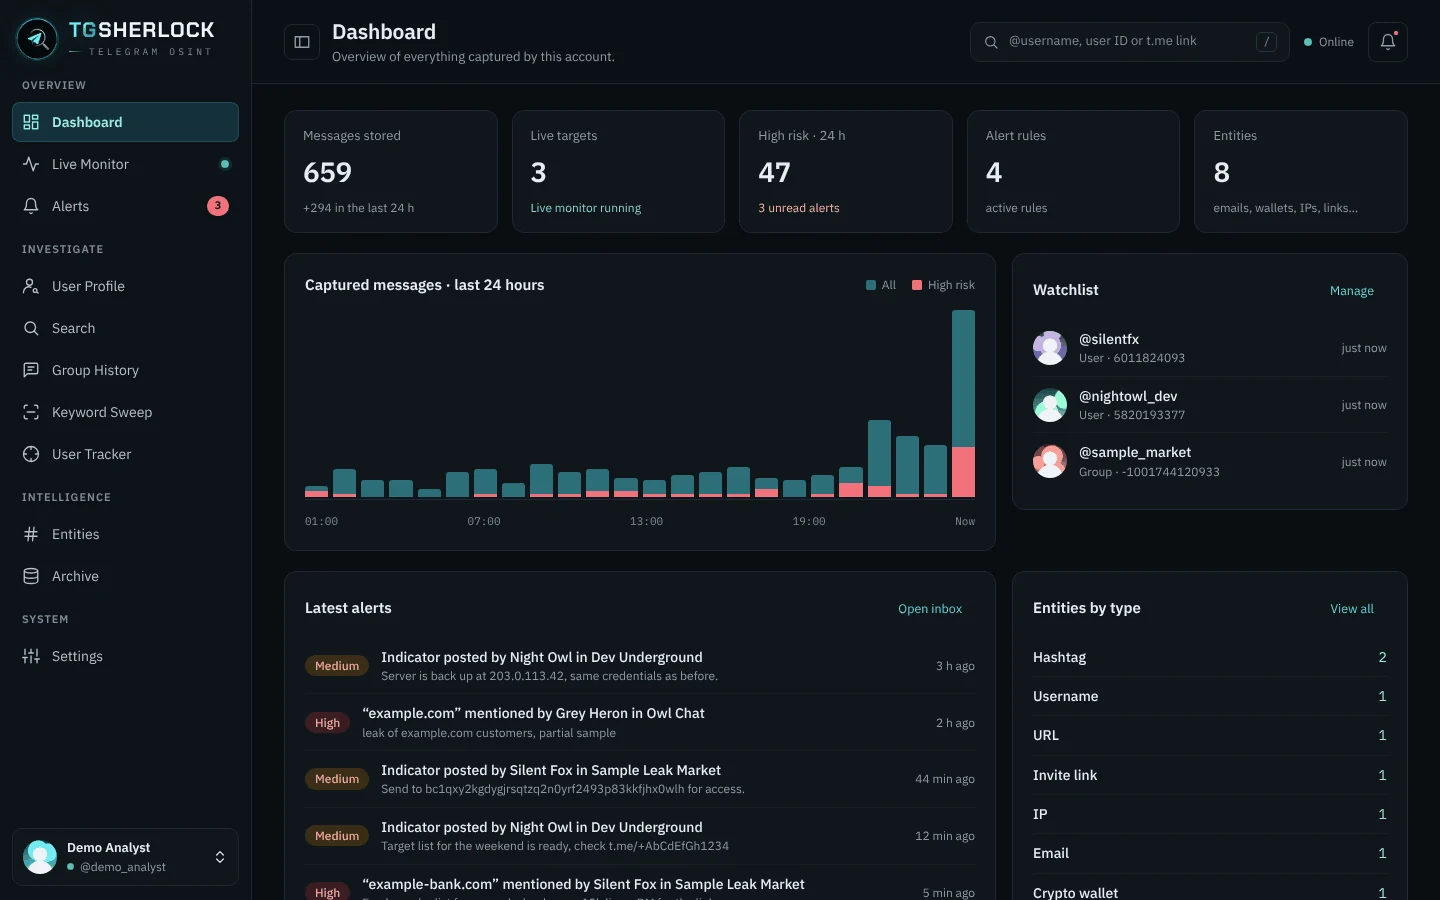 emrekybs/tgsherlock
Telegram OSINT tool for user, group and message investigation