
VISION-ProcMon
 forensicxlab/vision-procmon
A ProcessMonitor visualization application written in rust.
digital-forensicslog-analysismalware-analysis
forensicxlab/vision-procmonA ProcessMonitor visualization application written in rust.
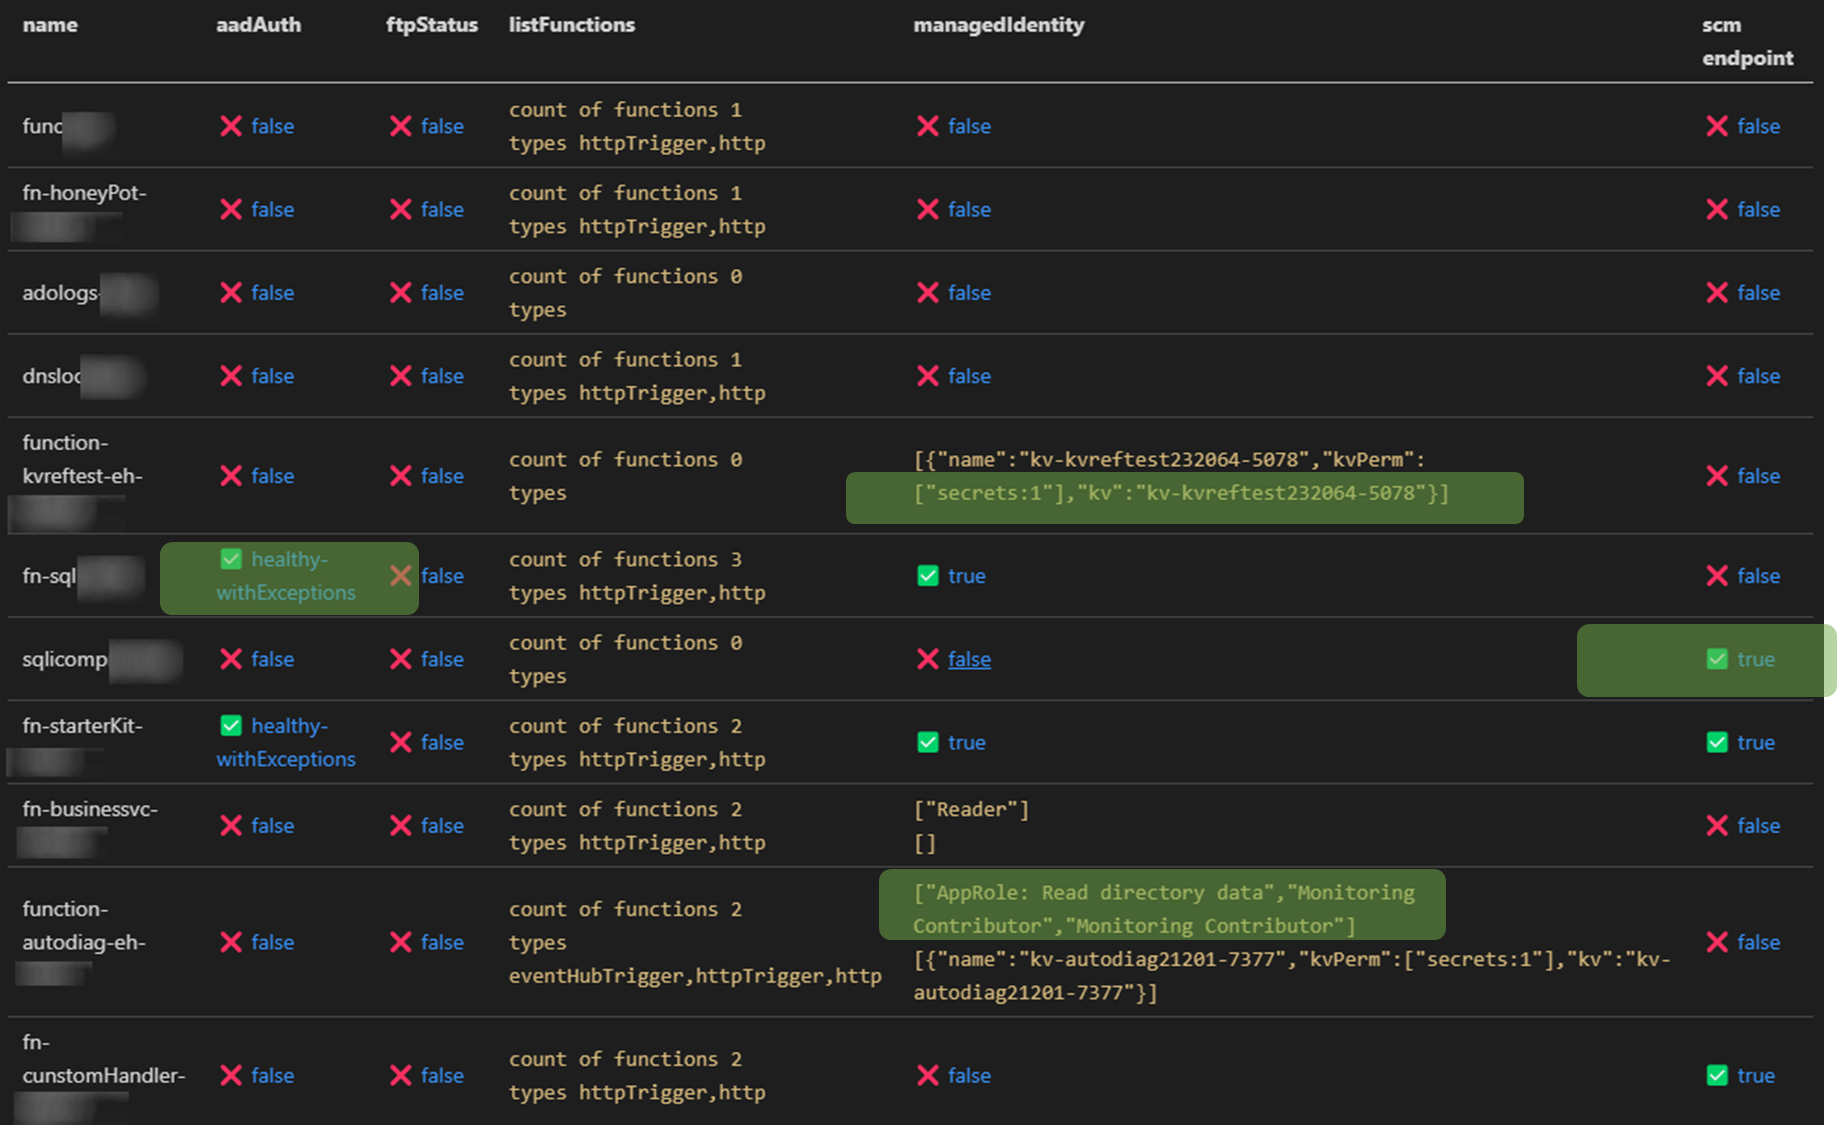 jsa2/east
Extensible Azure Security Tool - Documentation
 imthenachoman/how-to-secure-a-linux-server
Step-by-step guide for hardening a Linux server, covering SSH security, firewalls, intrusion detection, auditing, and system configuration to reduce…
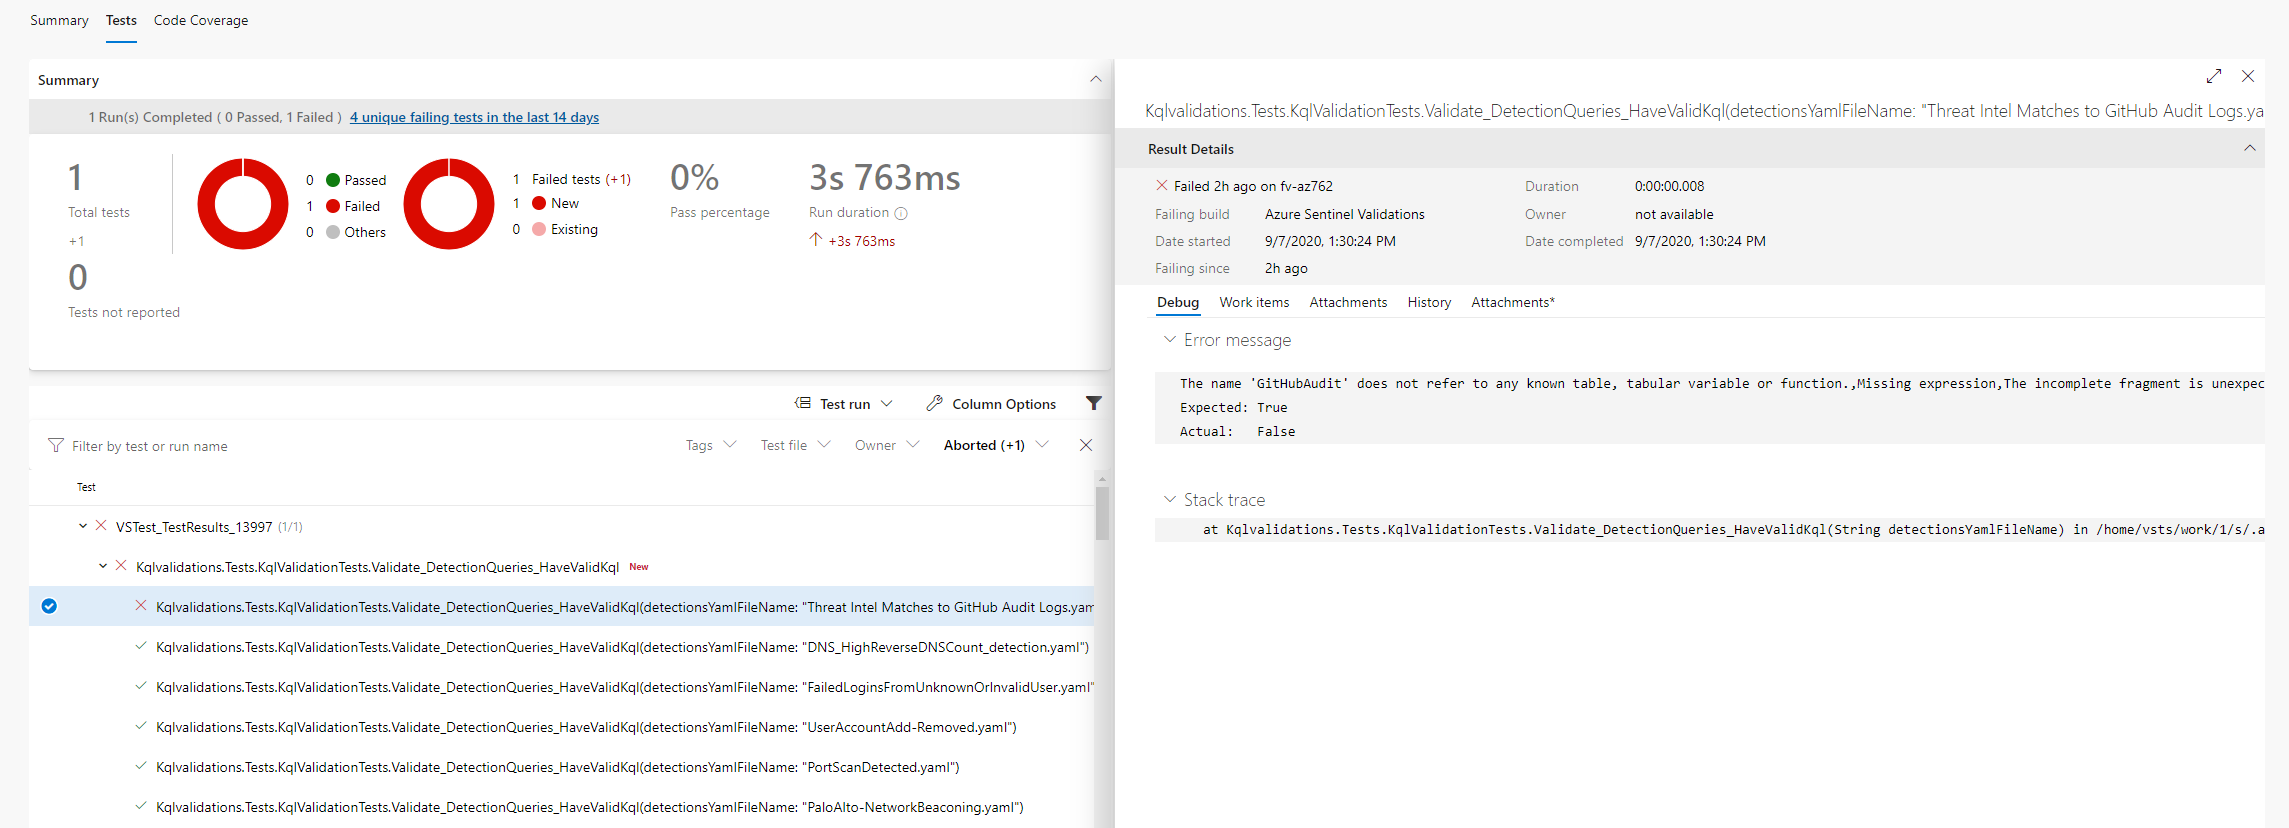 azure/azure-sentinel
Cloud-native SIEM for intelligent security analytics for your entire enterprise.
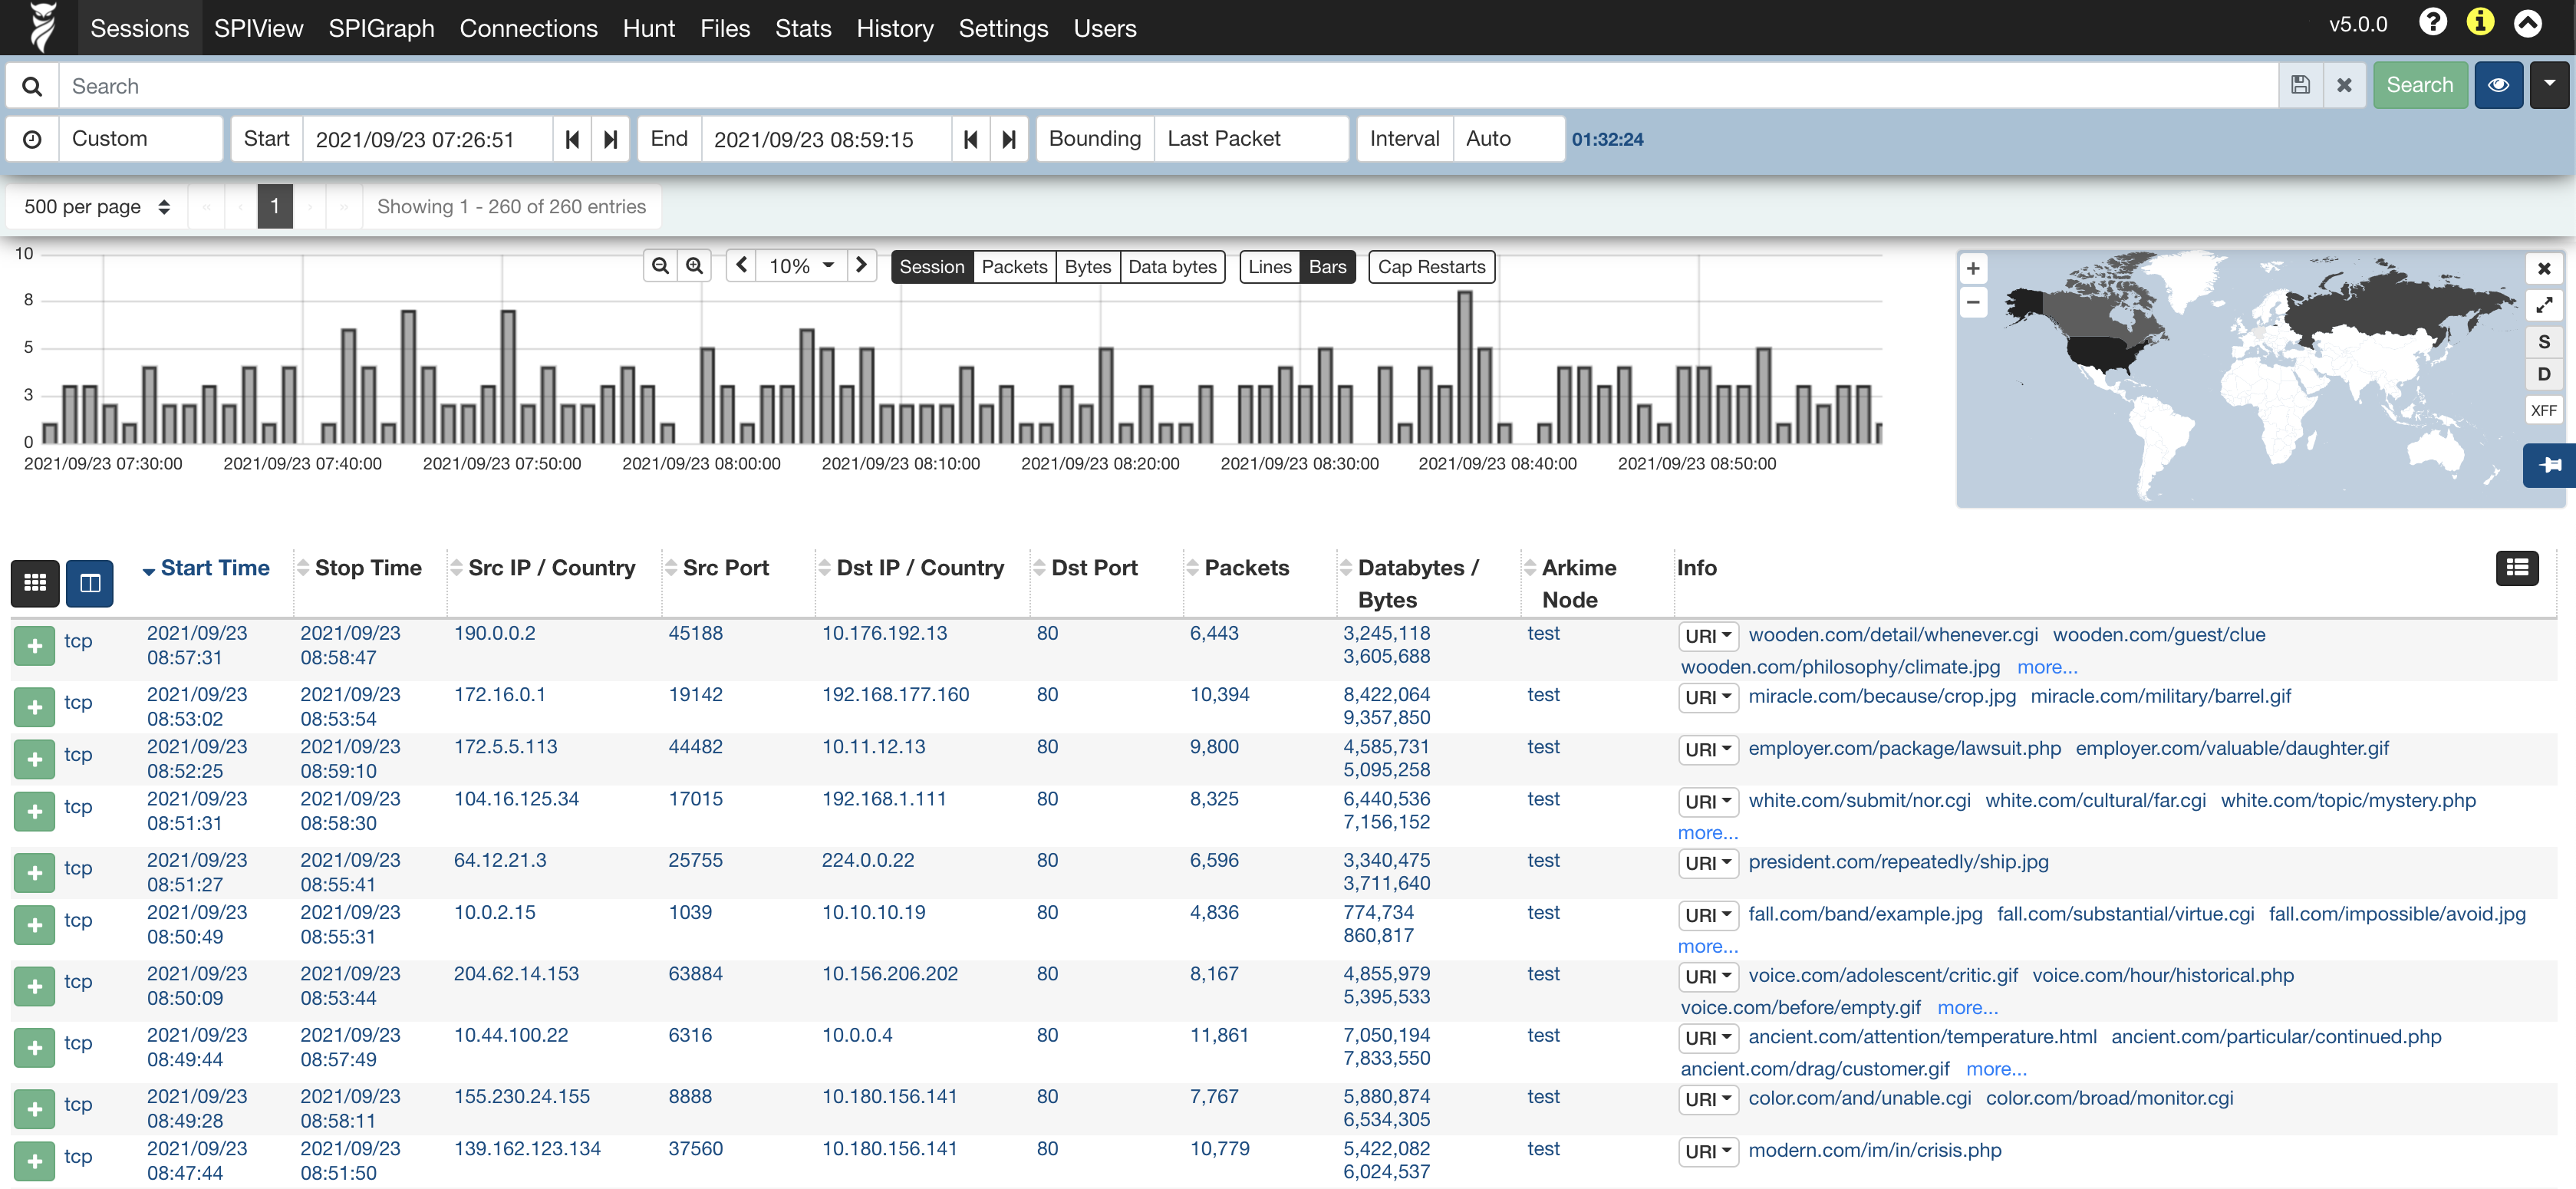 arkime/arkime
Arkime is an open source, large scale, full packet capturing, indexing, and database system.
 clong/detectionlab
Automate the creation of a lab environment complete with security tooling and logging best practices
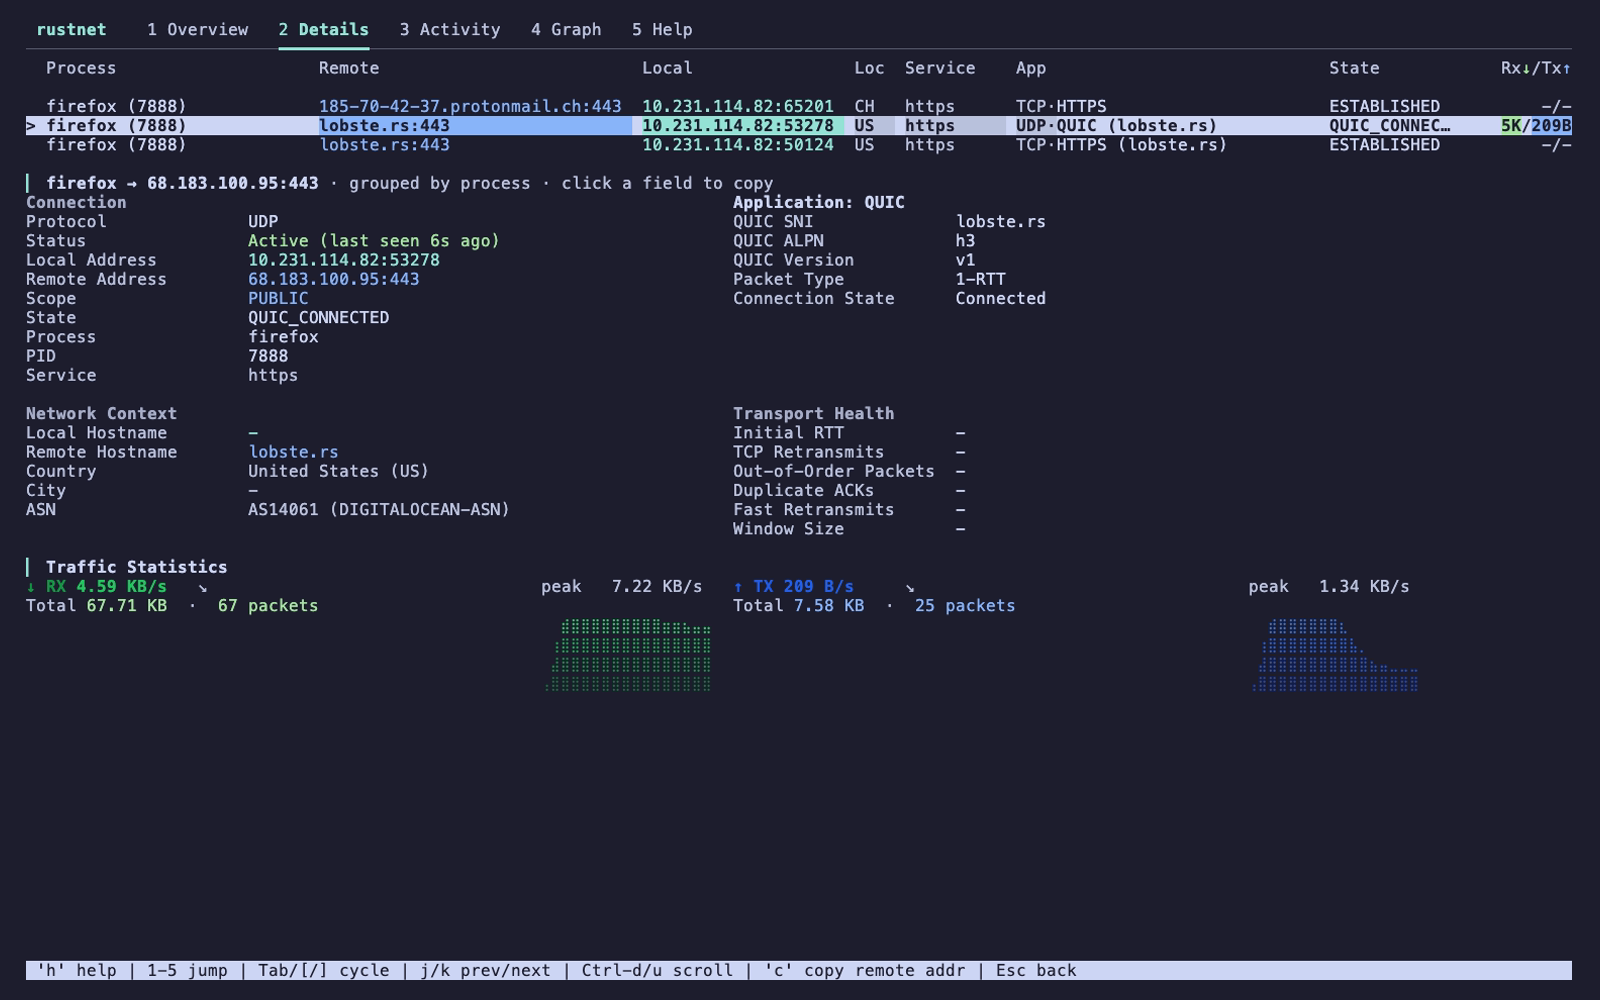 domcyrus/rustnet
Per-process network monitoring for your terminal with deep packet inspection. Cross-platform, sandboxed.
 withsecureopensource/chainsaw
Rapidly Search and Hunt through Windows Forensic Artefacts
 yamato-security/hayabusa
Multi-threaded Windows event log forensics timeline generator and threat hunting tool with full Sigma rule support, producing CSV/JSON timelines for…
 log2timeline/plaso
Digital forensics engine that parses logs, files, and system artifacts to build super timelines, enabling chronological event correlation for…
 jpcertcc/logontracer
Investigate malicious Windows logon by visualizing and analyzing Windows event log
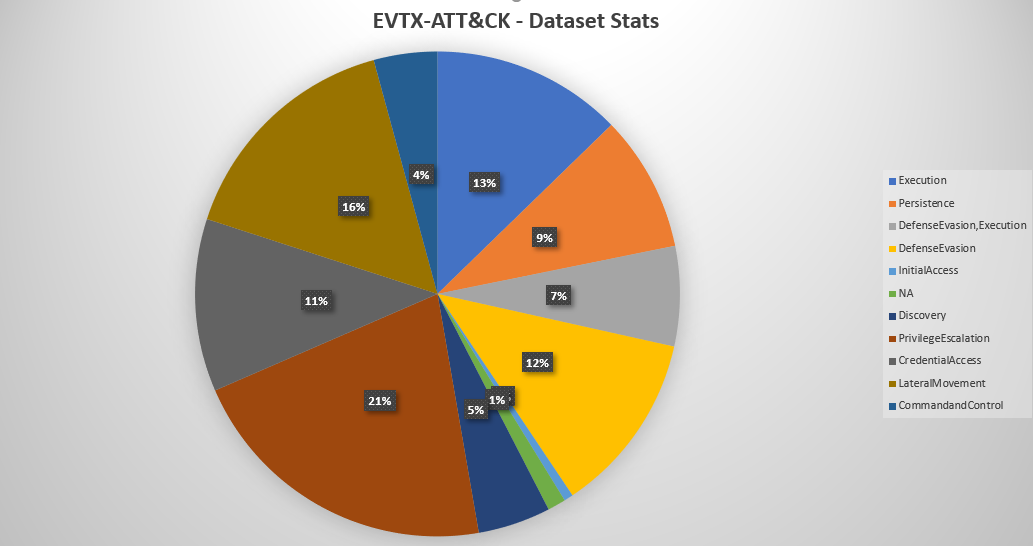 sbousseaden/evtx-attack-samples
Curated collection of Windows EVTX attack samples mapped to MITRE ATT&CK techniques, designed for testing detection scripts, DFIR training, and…
 sans-blue-team/deepbluecli
PowerShell-based threat hunting tool that analyzes Windows Event Logs to detect malicious activity including credential attacks, obfuscated commands,…
 abrignoni/ileapp
Parses iOS and iPadOS forensic extractions into HTML, TSV, timeline, KML, and LAVA reports with modular artifact discovery and encrypted iTunes…
 mattnotmax/cyberchef-recipes
A list of cyber-chef recipes and curated links
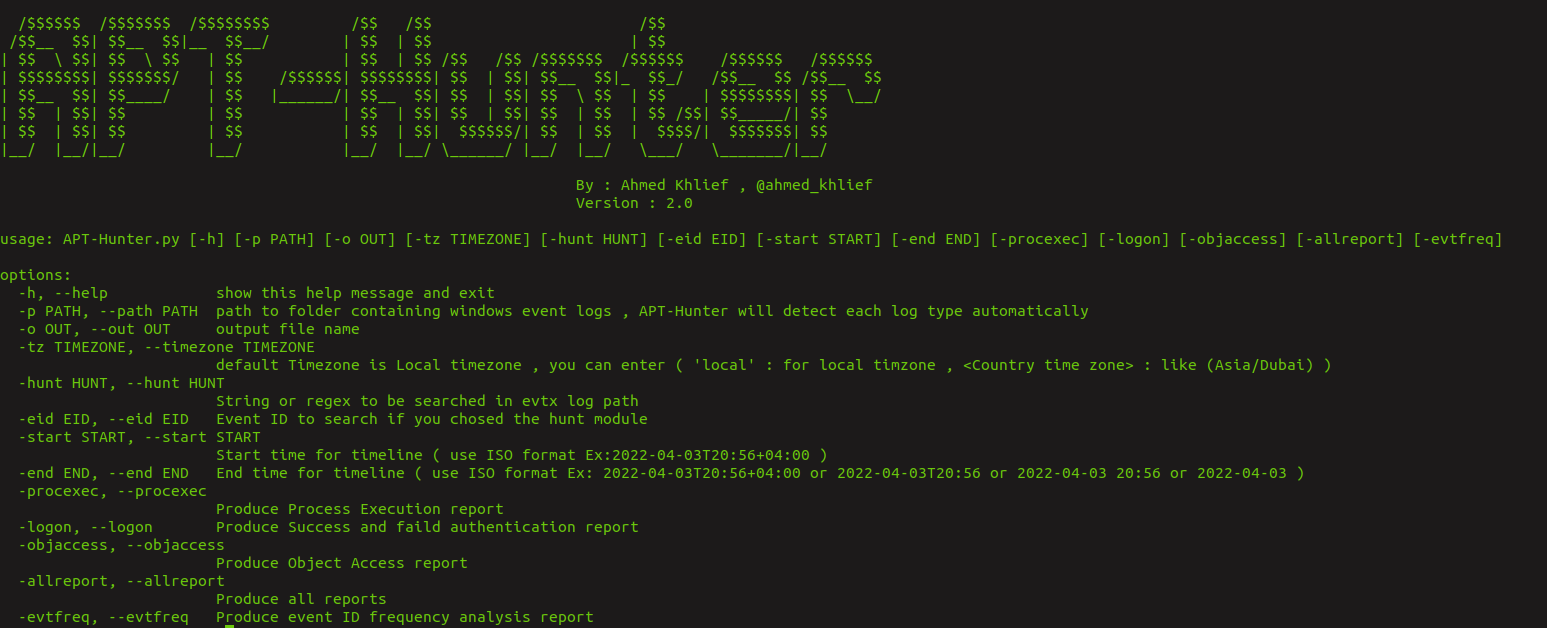 ahmedkhlief/apt-hunter
APT-Hunter is Threat Hunting tool for windows event logs which made by purple team mindset to provide detect APT movements hidden in the sea of…
 paulsec/awesome-windows-domain-hardening
A curated list of awesome Security Hardening techniques for Windows.
 digitalruby/ipban
Automated IP ban service that detects failed login attempts from event logs and files, blocking attackers on Windows and Linux via firewall…