
envocabulary
 sreckoskocilic/envocabulary
Trace every shell environment variable to its exact file and line origin. Audit shell configs for dead entries, duplicates, and orphaned files across…
configuration-auditingdigital-forensicsforensics+3
3
sreckoskocilic/envocabularyTrace every shell environment variable to its exact file and line origin. Audit shell configs for dead entries, duplicates, and orphaned files across…
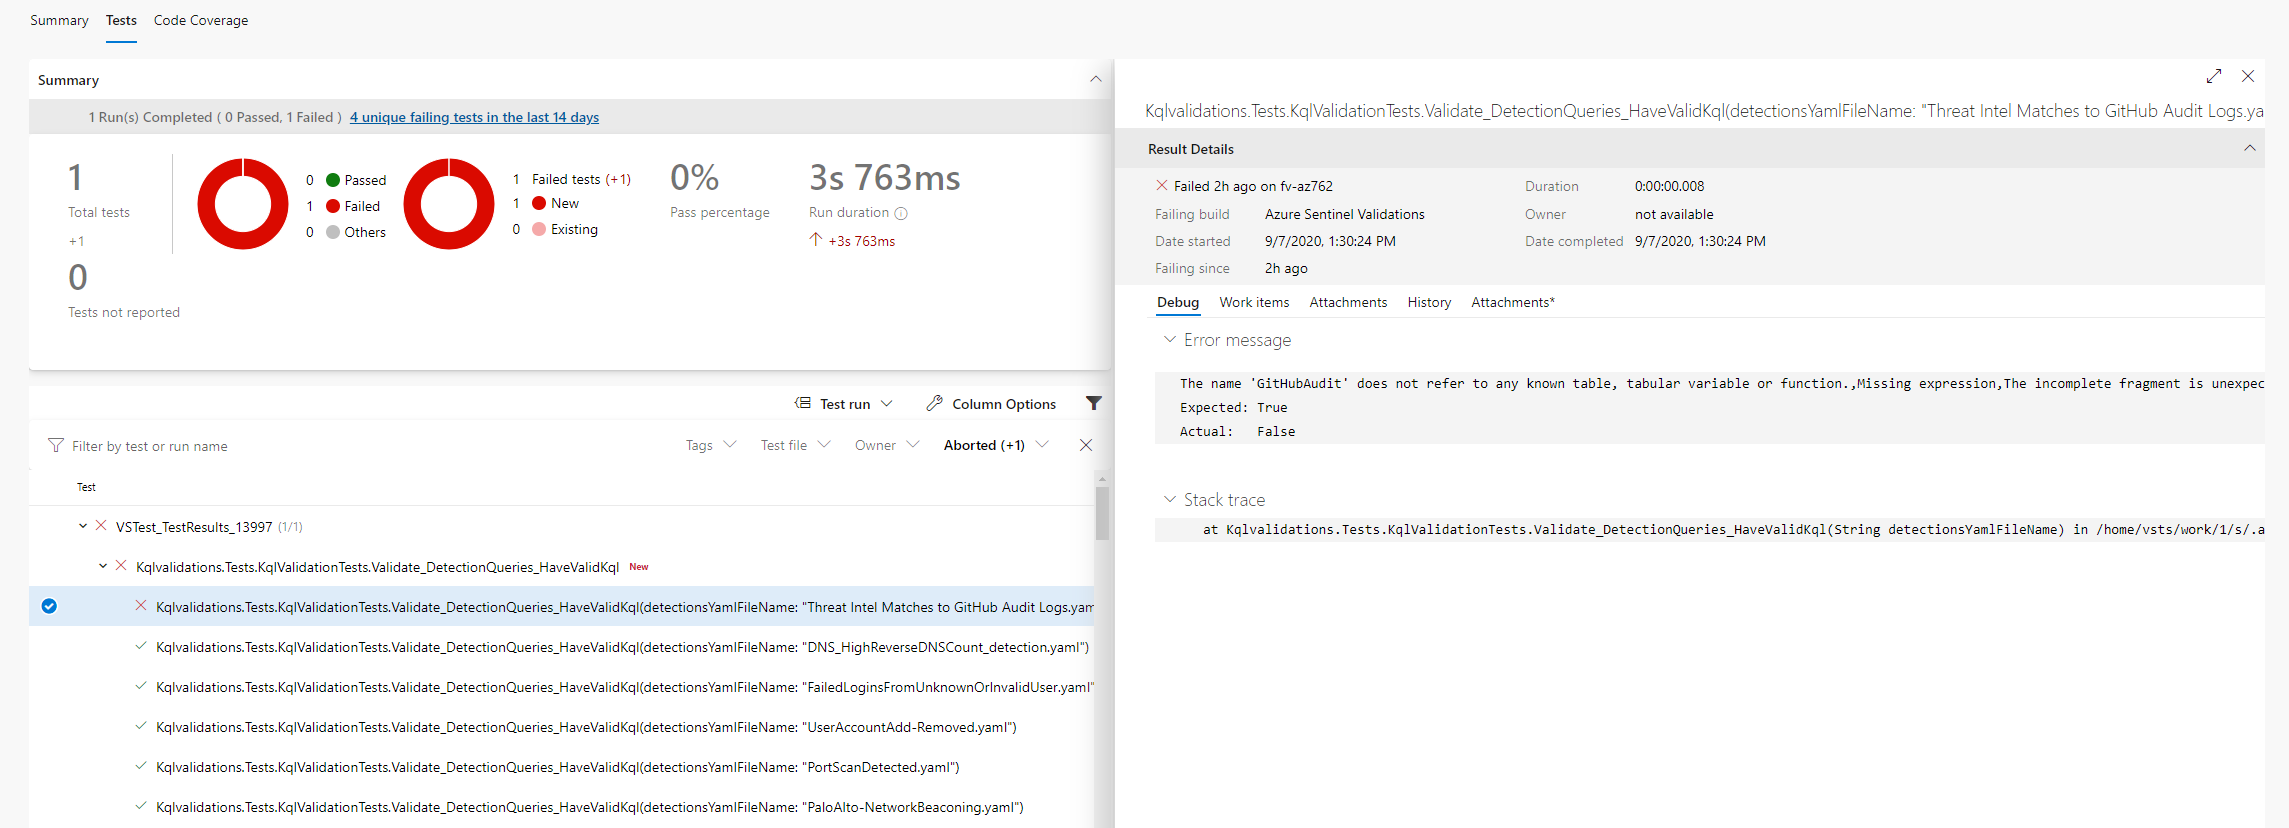 azure/azure-sentinel
Cloud-native SIEM for intelligent security analytics for your entire enterprise.
 grafana/loki
Horizontally scalable, multi-tenant log aggregation system that indexes labels instead of full text, integrates with Grafana, and is optimized for…
 elastic/detection-rules
Develop, validate, and publish SIEM detection rules for Elastic Security, with Python CLI tooling, KQL parsing, Kibana integration, and packaged…
 zeek/zeek
Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.
 abrignoni/ileapp
Parses iOS and iPadOS forensic extractions into HTML, TSV, timeline, KML, and LAVA reports with modular artifact discovery and encrypted iTunes…
 pii-shield/pii-shield
Zero-code K8s sidecar for log sanitization. Detects secrets via Entropy Analysis, preserves JSON integrity, and redacts PII deterministically. 🛡️
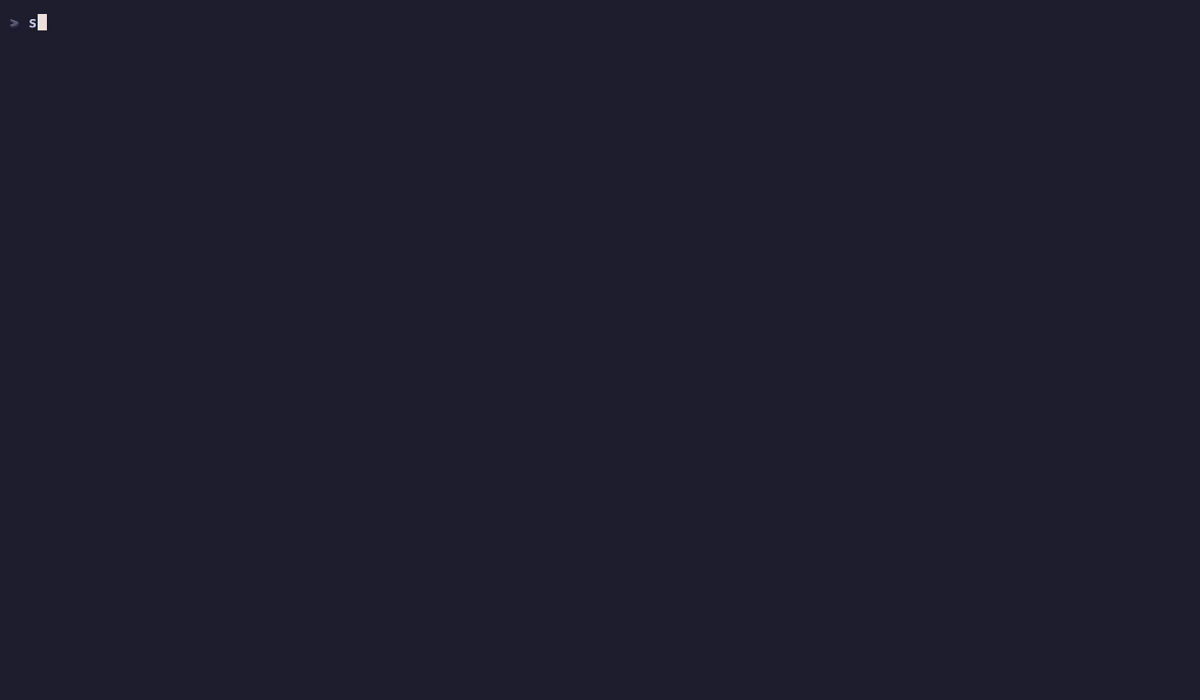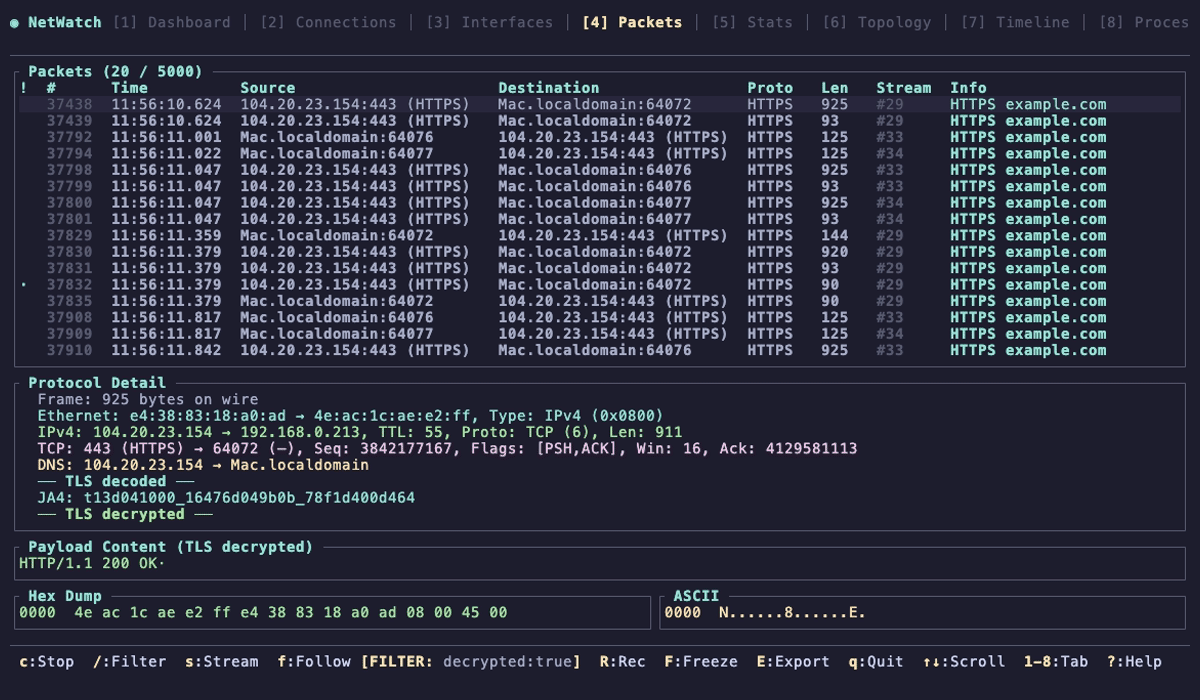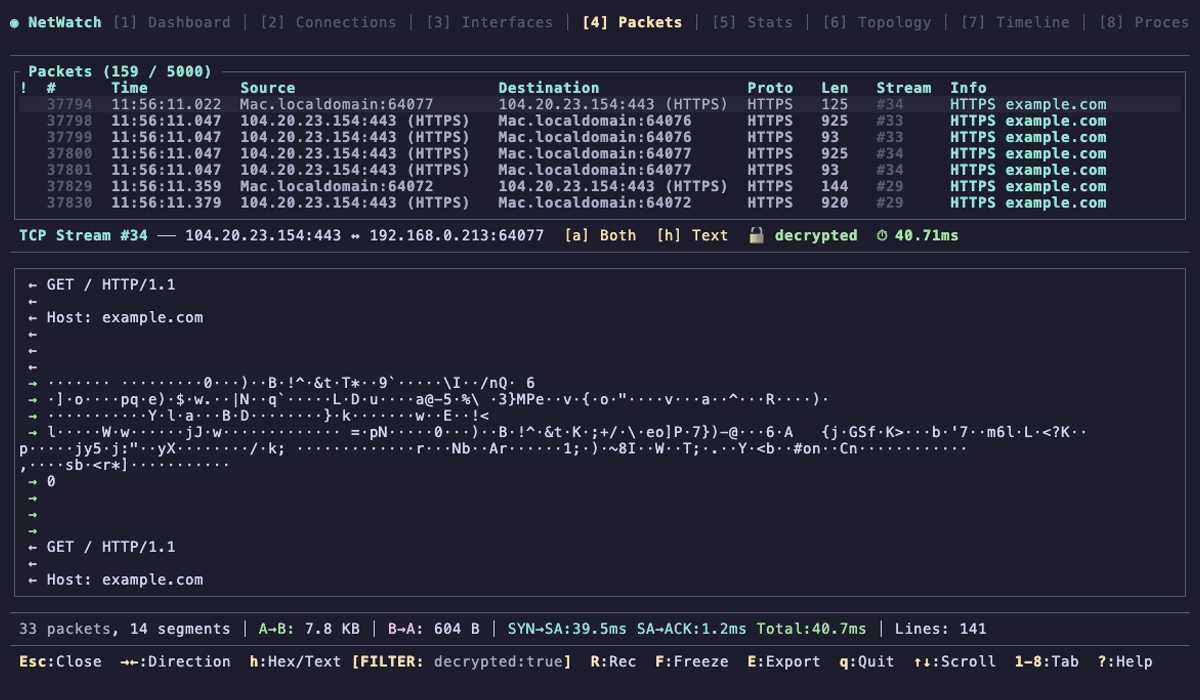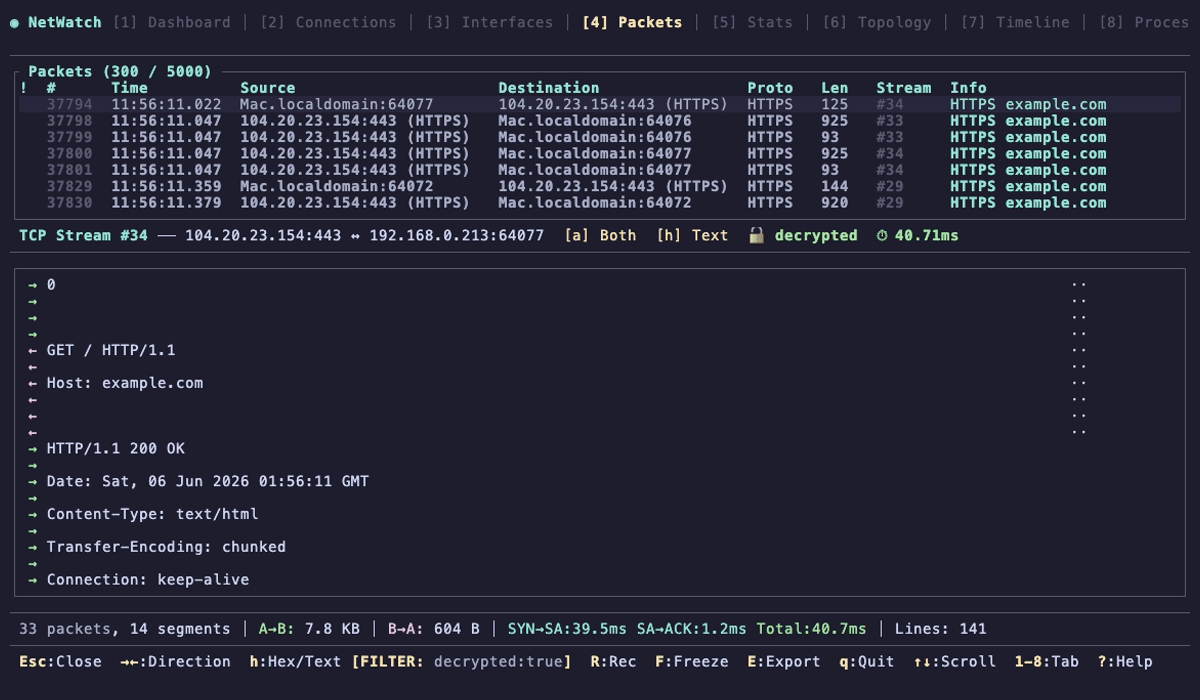 matthart1983/netwatch
Real-time network diagnostics in your terminal. One command, zero config, instant visibility.
 byteray-labs/query-hub
CQL Hub is an open repository of detection and hunting queries for CrowdStrike NextGen SIEM and Falcon LogScale. All queries stored here are…
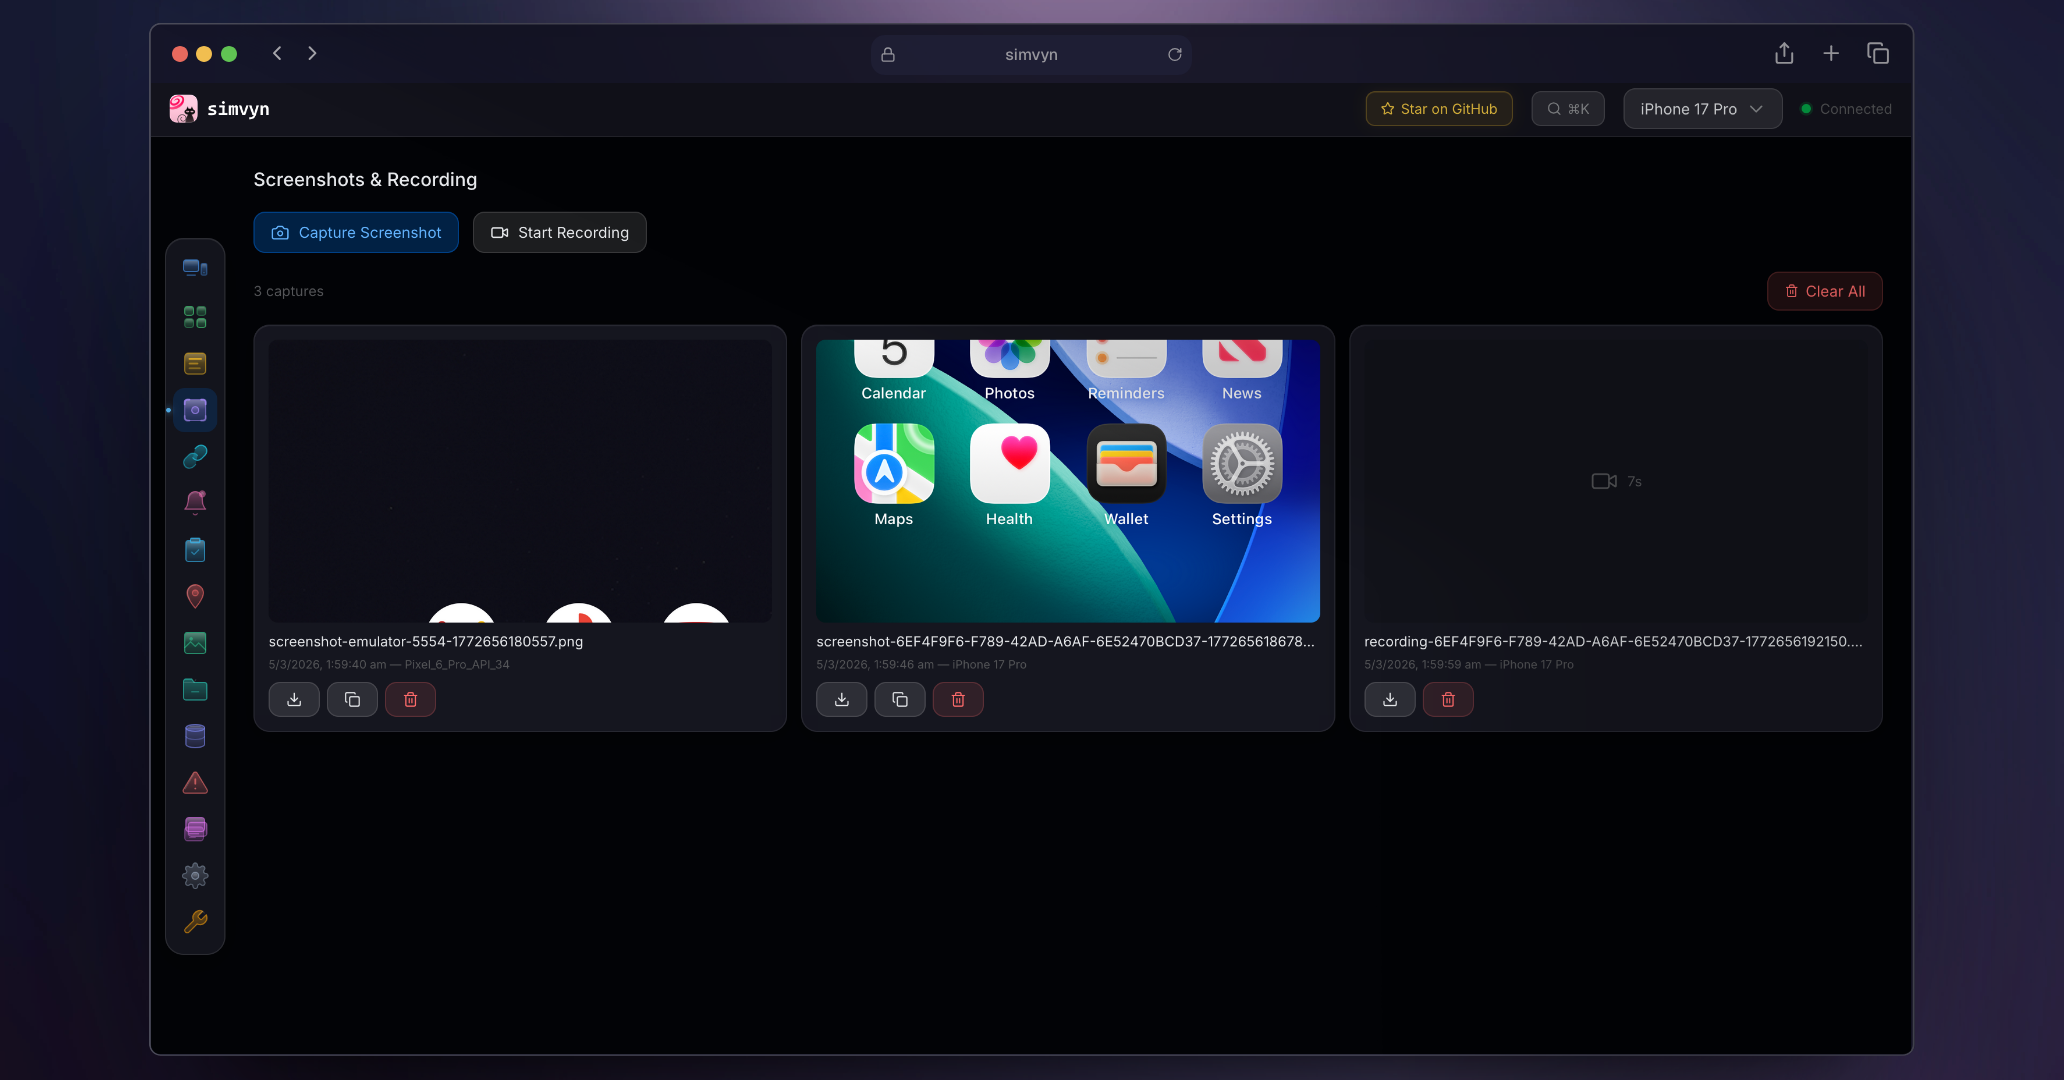 pranshuchittora/simvyn
Universal mobile devtool for Agents & Humans - control iOS Simulators, Android Emulators, and real devices from a single dashboard and CLI
 log2timeline/plaso
Digital forensics engine that parses logs, files, and system artifacts to build super timelines, enabling chronological event correlation for…
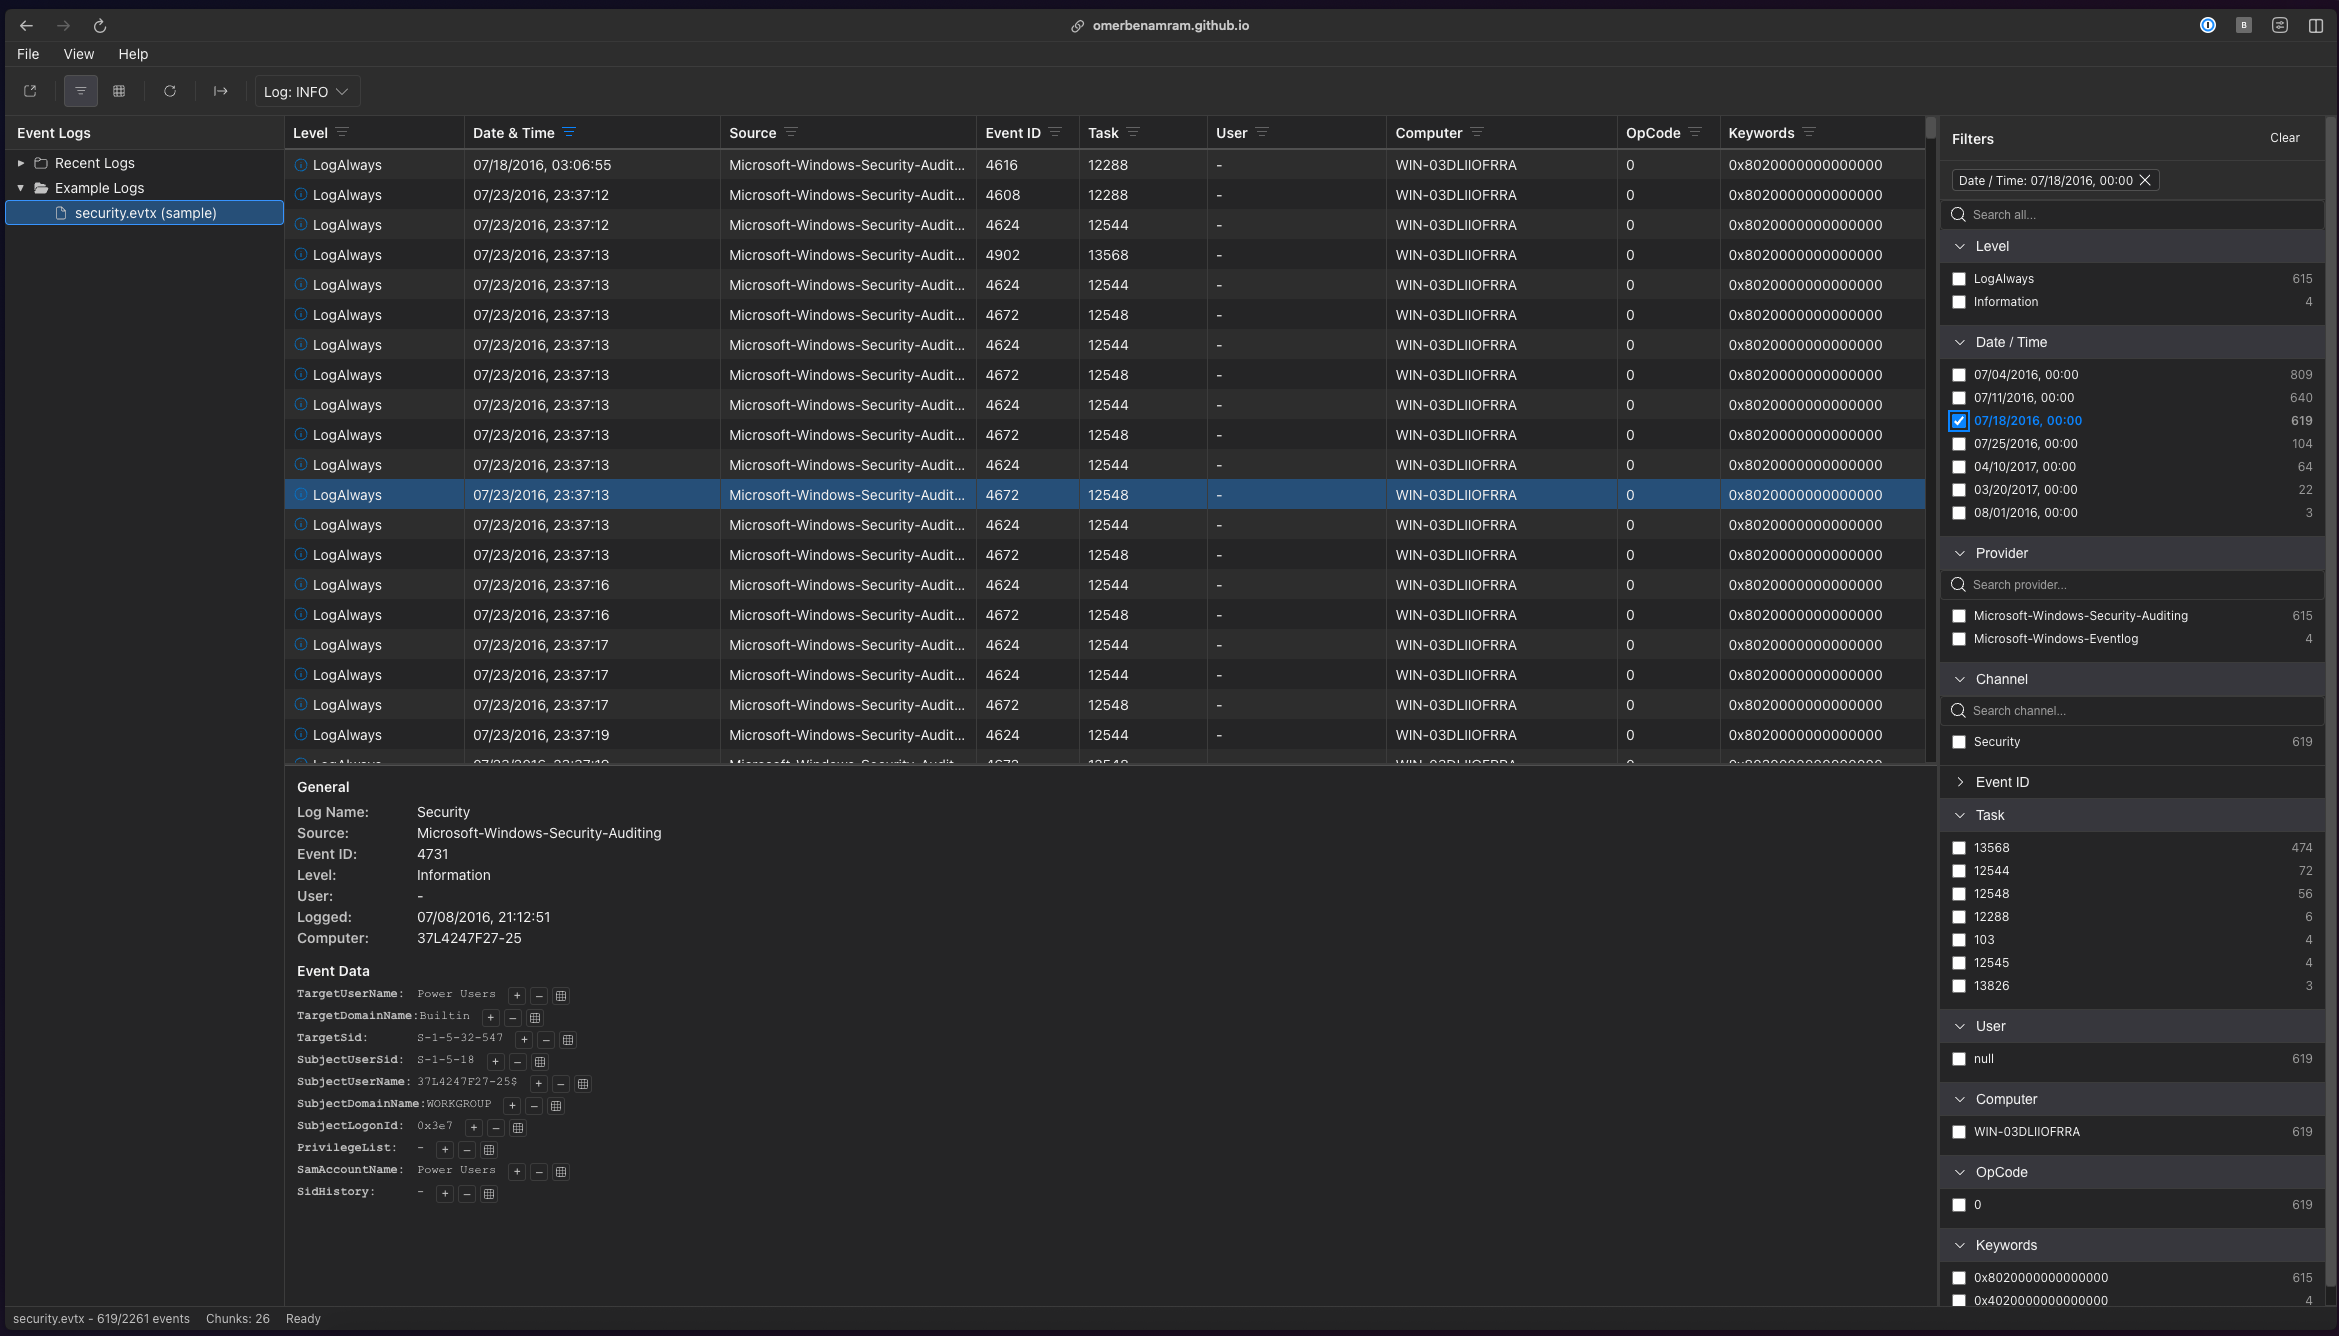 omerbenamram/evtx
A Fast (and safe) parser for the Windows XML Event Log (EVTX) format
 jithinkrishnanrs/cve-2026-86218-n-central-ioc-toolkit
Defensive IOC and detection toolkit for CVE-2026-86218, a critical pre-auth RCE in N-able N-central. Includes IOCs, log scanner, Sigma, Splunk,…
 jithinkrishnanrs/gitlab-cve-2026-85706-ioc
CVE-2026-85706 — GitLab Path Traversal IOC Scanner & Detection Toolkit. Detect and hunt for exploitation of the critical unauthenticated GitLab CE/EE…
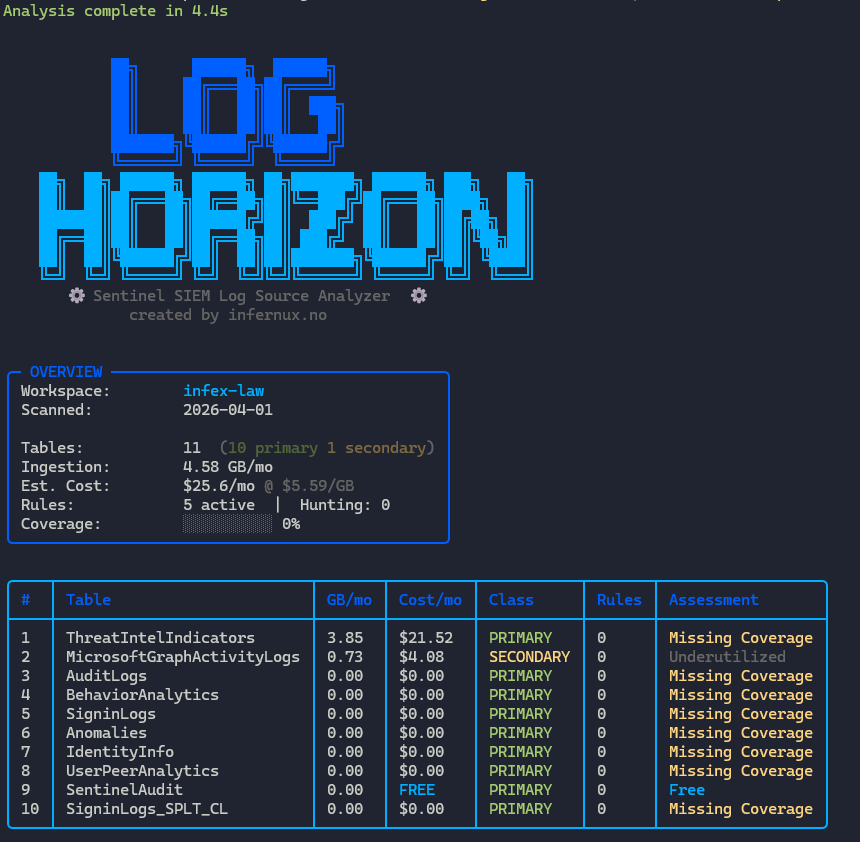 lnfernux/log-horizon
Microsoft Sentinel SIEM Log Source Analyzer
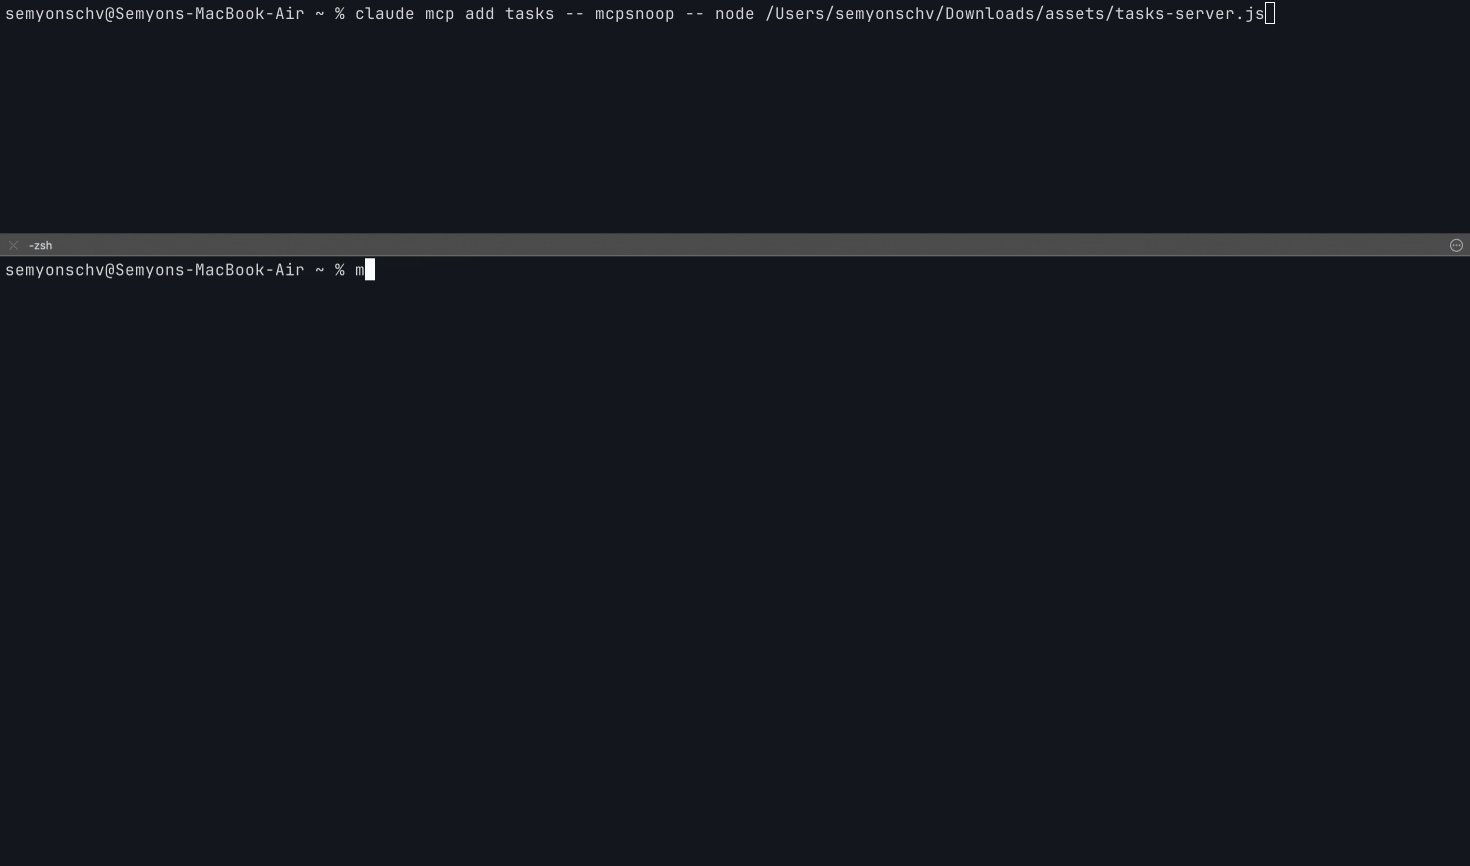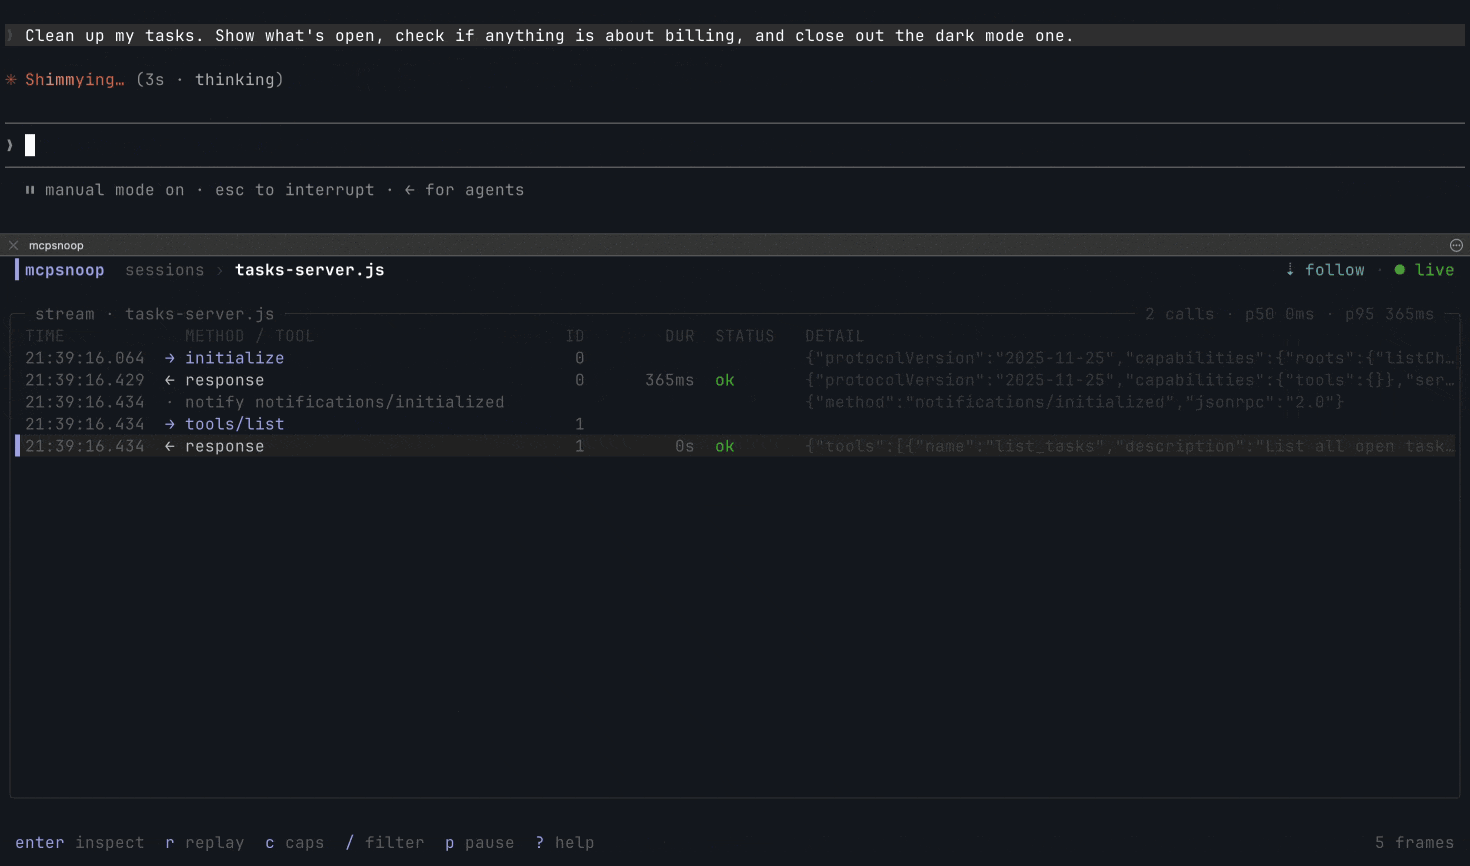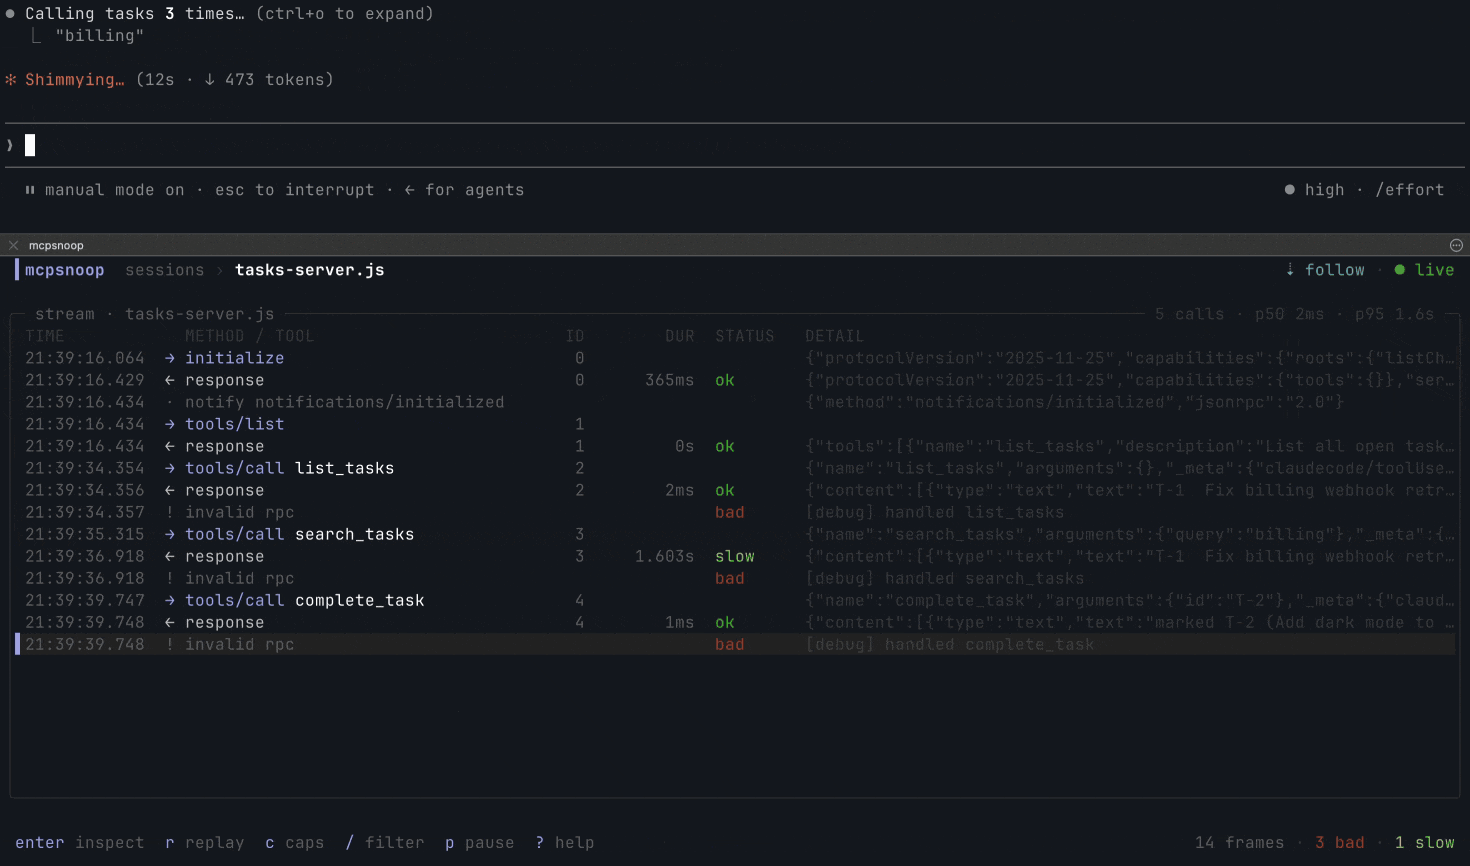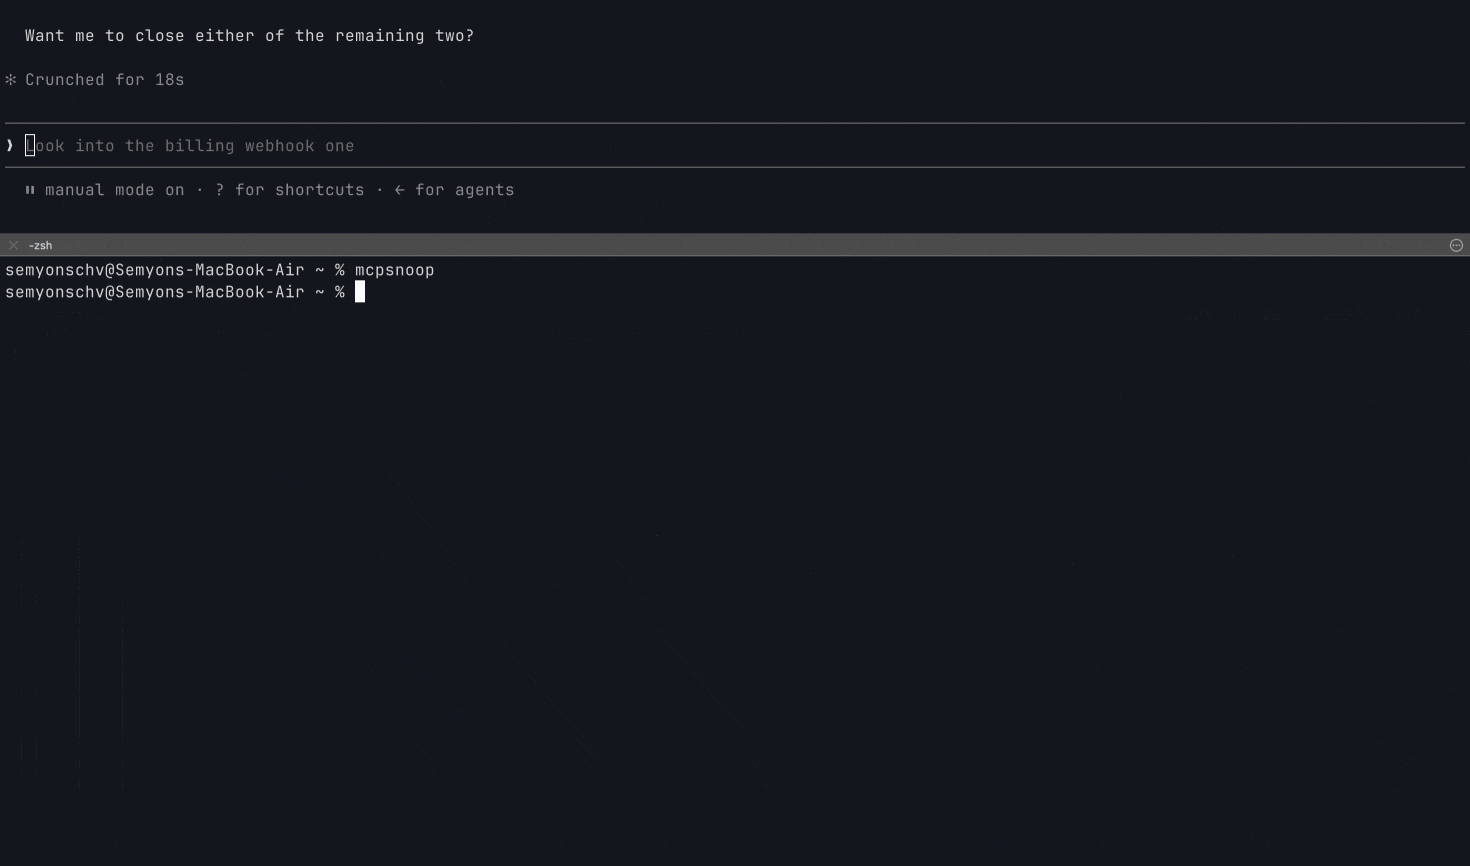 kerlenton/mcpsnoop
Wireshark for MCP. A transparent proxy that shows every real tool call between your AI client and your MCP servers, live in your terminal.
 karim852/kage-dfir-toolkit
Windows host DFIR triage console that chains artefact collection, Sigma-correlated timelines, YARA scans, socket and account inspection, indicator…