
Agentic-Evidence
 owasp/agentic-evidence
OWASP reference project for agentic AI security evidence: correlates agent execution, identity, tool calls, and authorization decisions into…
ai-securityanomaly-detectioncurated-resources+6
2
owasp/agentic-evidenceOWASP reference project for agentic AI security evidence: correlates agent execution, identity, tool calls, and authorization decisions into…
 owasp/the-agents-epistemic-baggage
An audit-oriented risk model for how agent-generated inferences can change epistemic status, gain operational authority, and influence later…
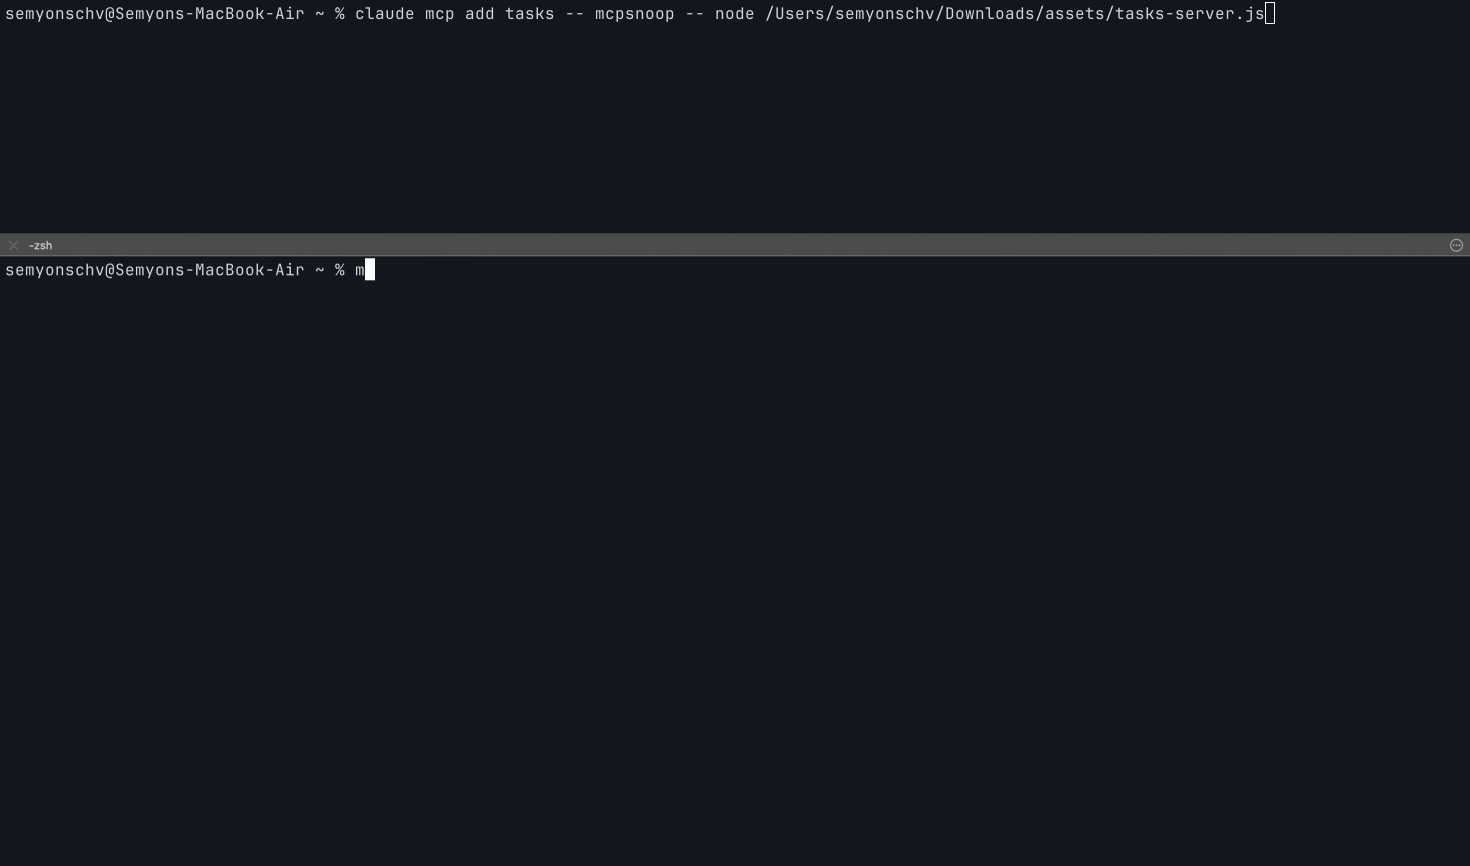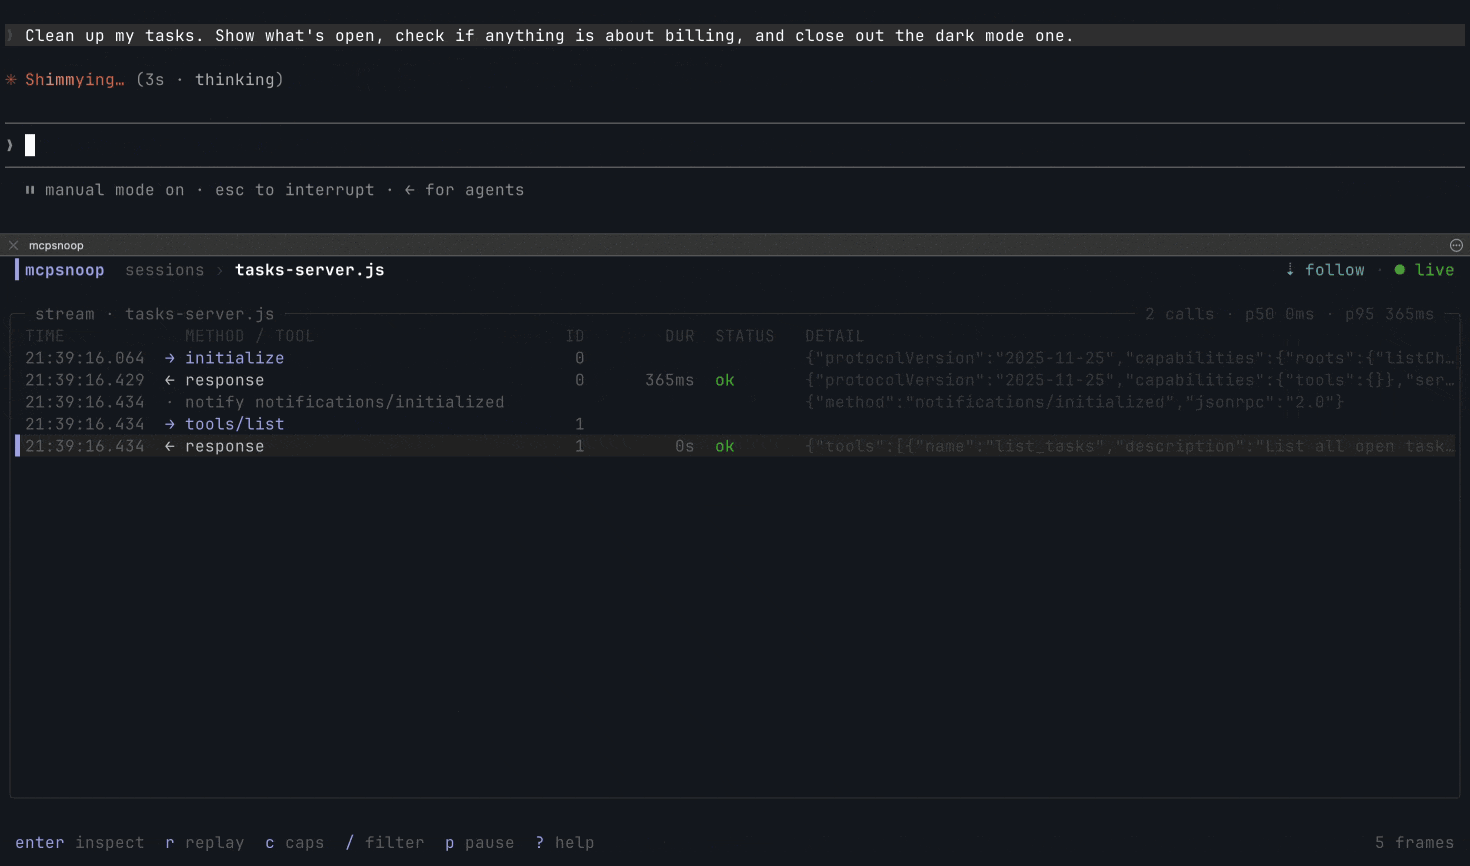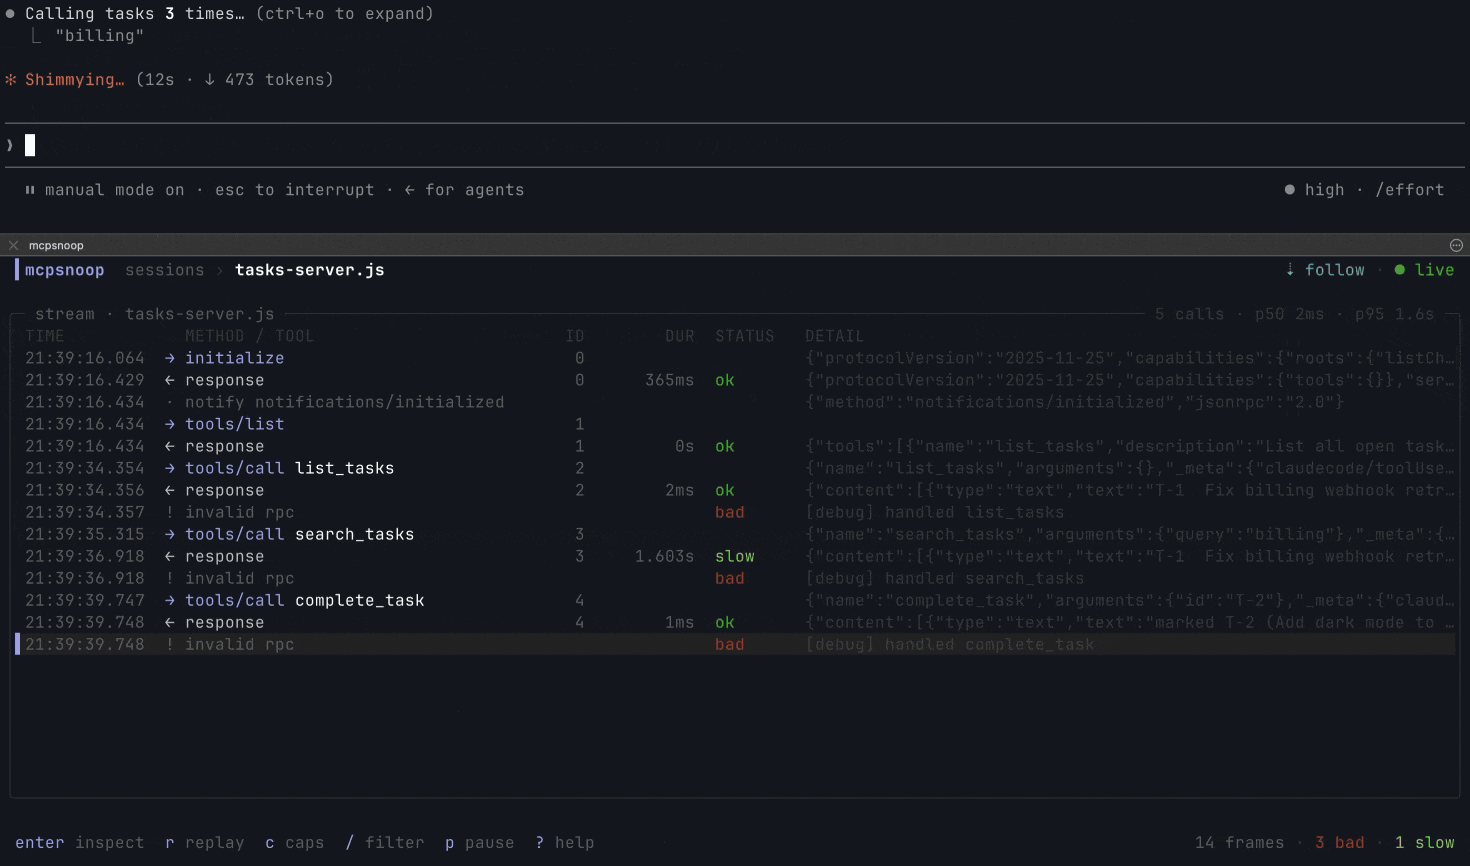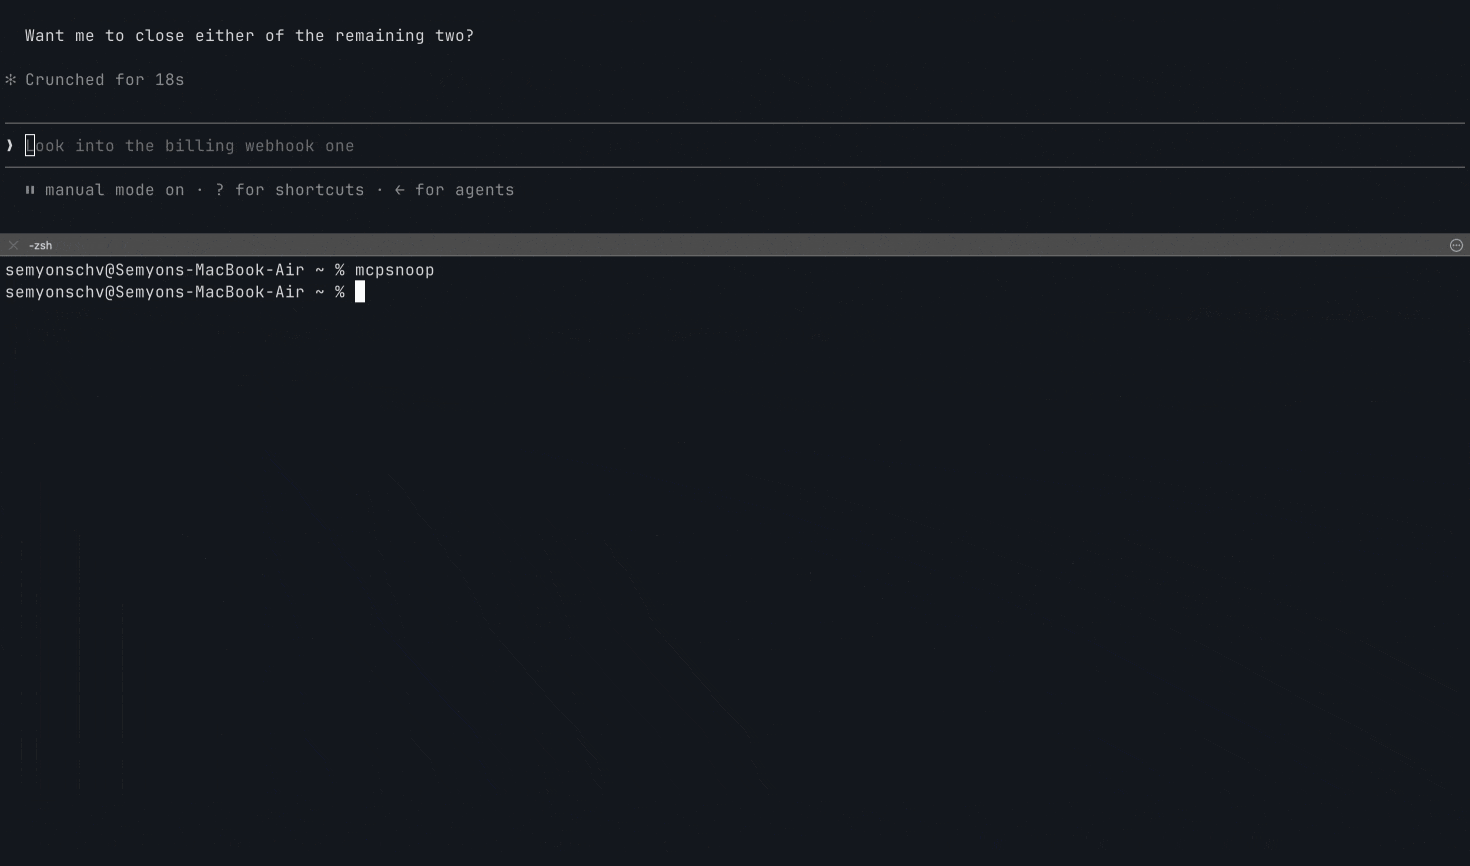 kerlenton/mcpsnoop
Wireshark for MCP. A transparent proxy between your AI client and MCP server. Watch every call live in your terminal, fail CI on what it finds,…
 owasp/piihunter
Scans PostgreSQL databases and Jira issues for PII using regex, NER/ML, and optional self-hosted LLM detection, with redacted reports and audit…
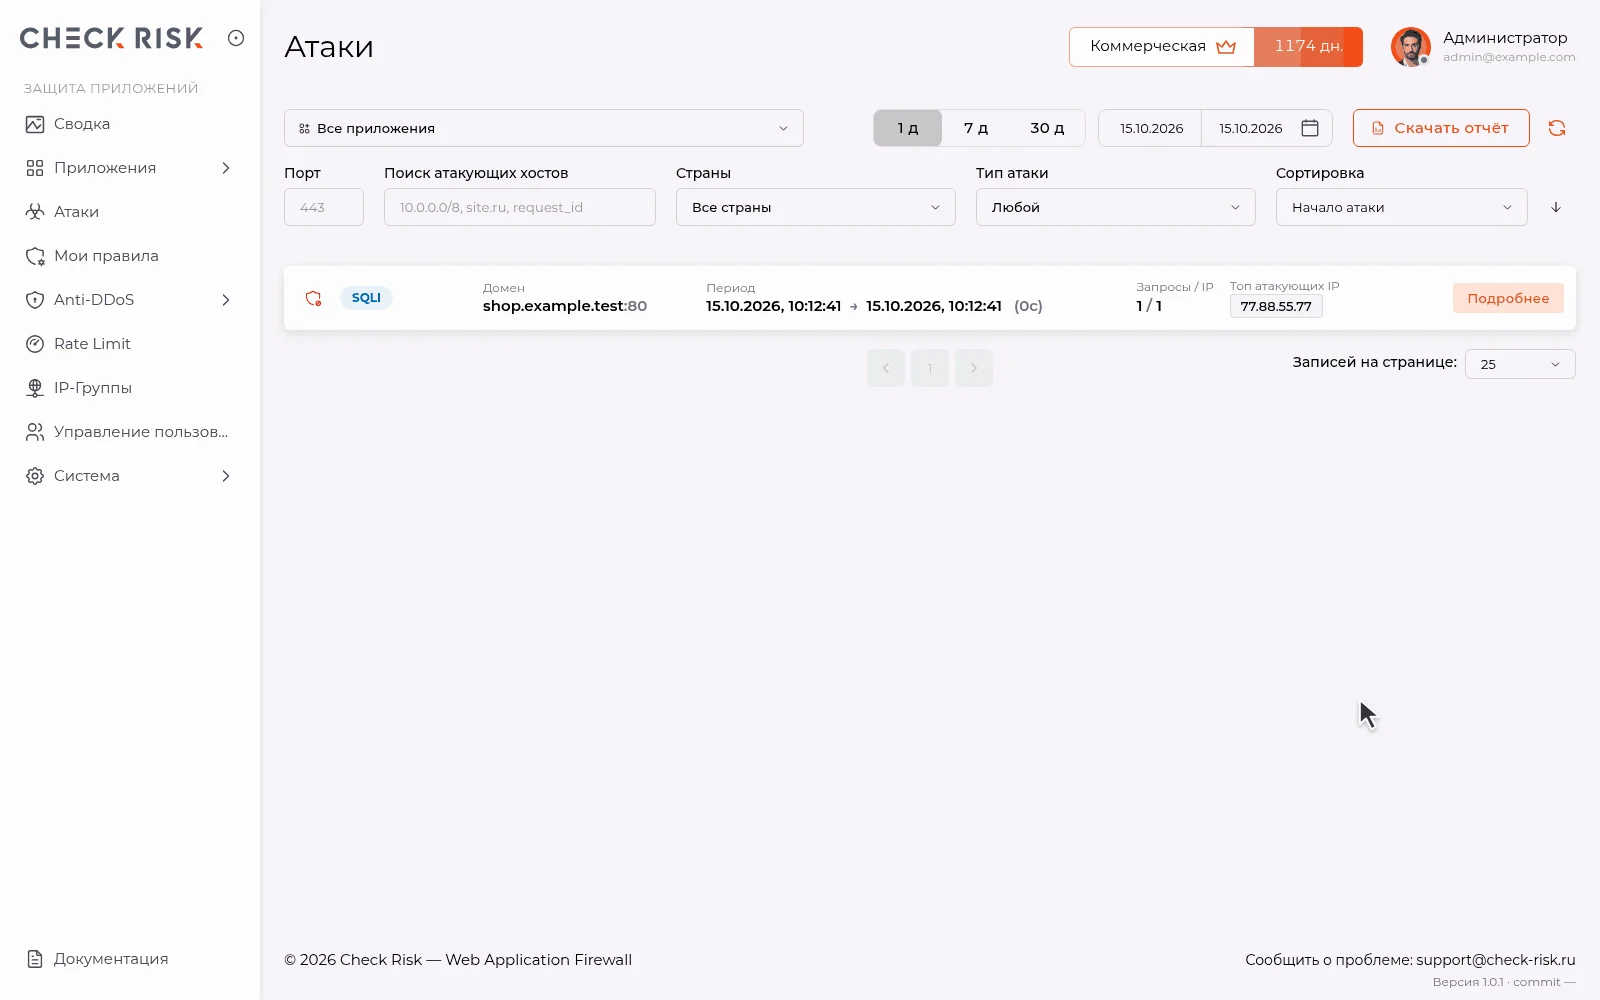 check-risk-waf/check-risk-waf
Reverse-proxy web application firewall with WAF, anti-bot and anti-DDoS protection at L3/L4/L7, custom rules, rate limiting, geo/IP filtering and…
 jay123anta/laravel-threat-detection
Passive Laravel middleware that detects and logs SQL injection, XSS, RCE, bot scanners, and 175+ attack patterns. Features a built-in dashboard,…
 owasp/honeypot-project
Deploy web honeypots to capture emerging attack data, analyze ModSecurity audit logs via ELK, and share threat intelligence with MISP for…
 j-dahl7/mcp-attack-detection-sentinel
Sentinel detection lab for MCP attack chains: CVE-2026-26118 SSRF token theft, tool poisoning, cross-server exfiltration, identity post-exploitation.…
 tieupham267/log4shell-coraza
Log4Shell (CVE-2021-44228) defense lab — nginx + Coraza WAF dynamic module + OWASP CRS v4. Educational use only.
 d0rb/packetpirate
A headless , scriptable, command-line based MITM proxy designed for network traffic interception, analysis, and modification on Windows systems.
 axselll/cve-2025-20384
Proof-of-concept demonstrating log injection and poisoning in Splunk via crafted URL parameters, highlighting OWASP log injection risks.
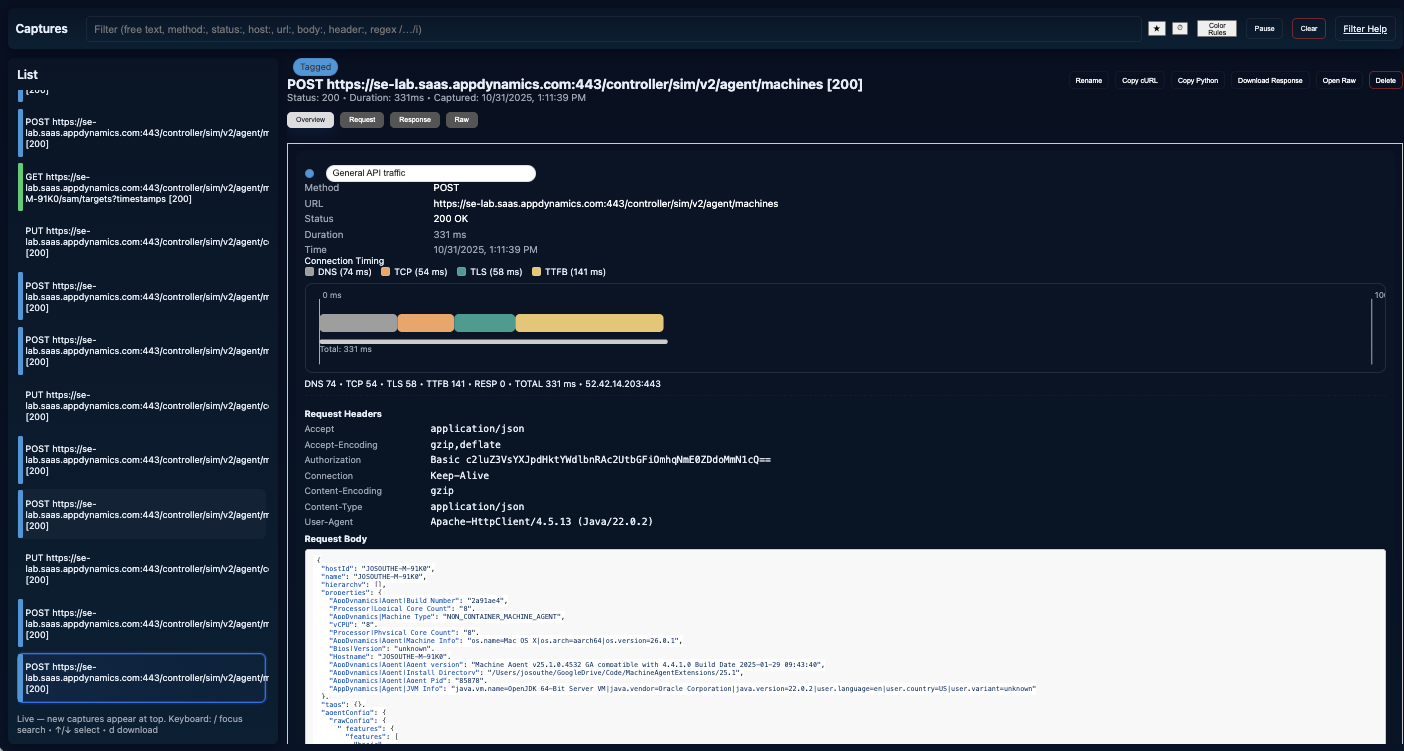 jbsouthe/http-breakout-proxy
HTTP Proxy Analysis for reverse engineering protocol communication
 owasp/python-honeypot
OWASP Honeypot, Automated Deception Framework.
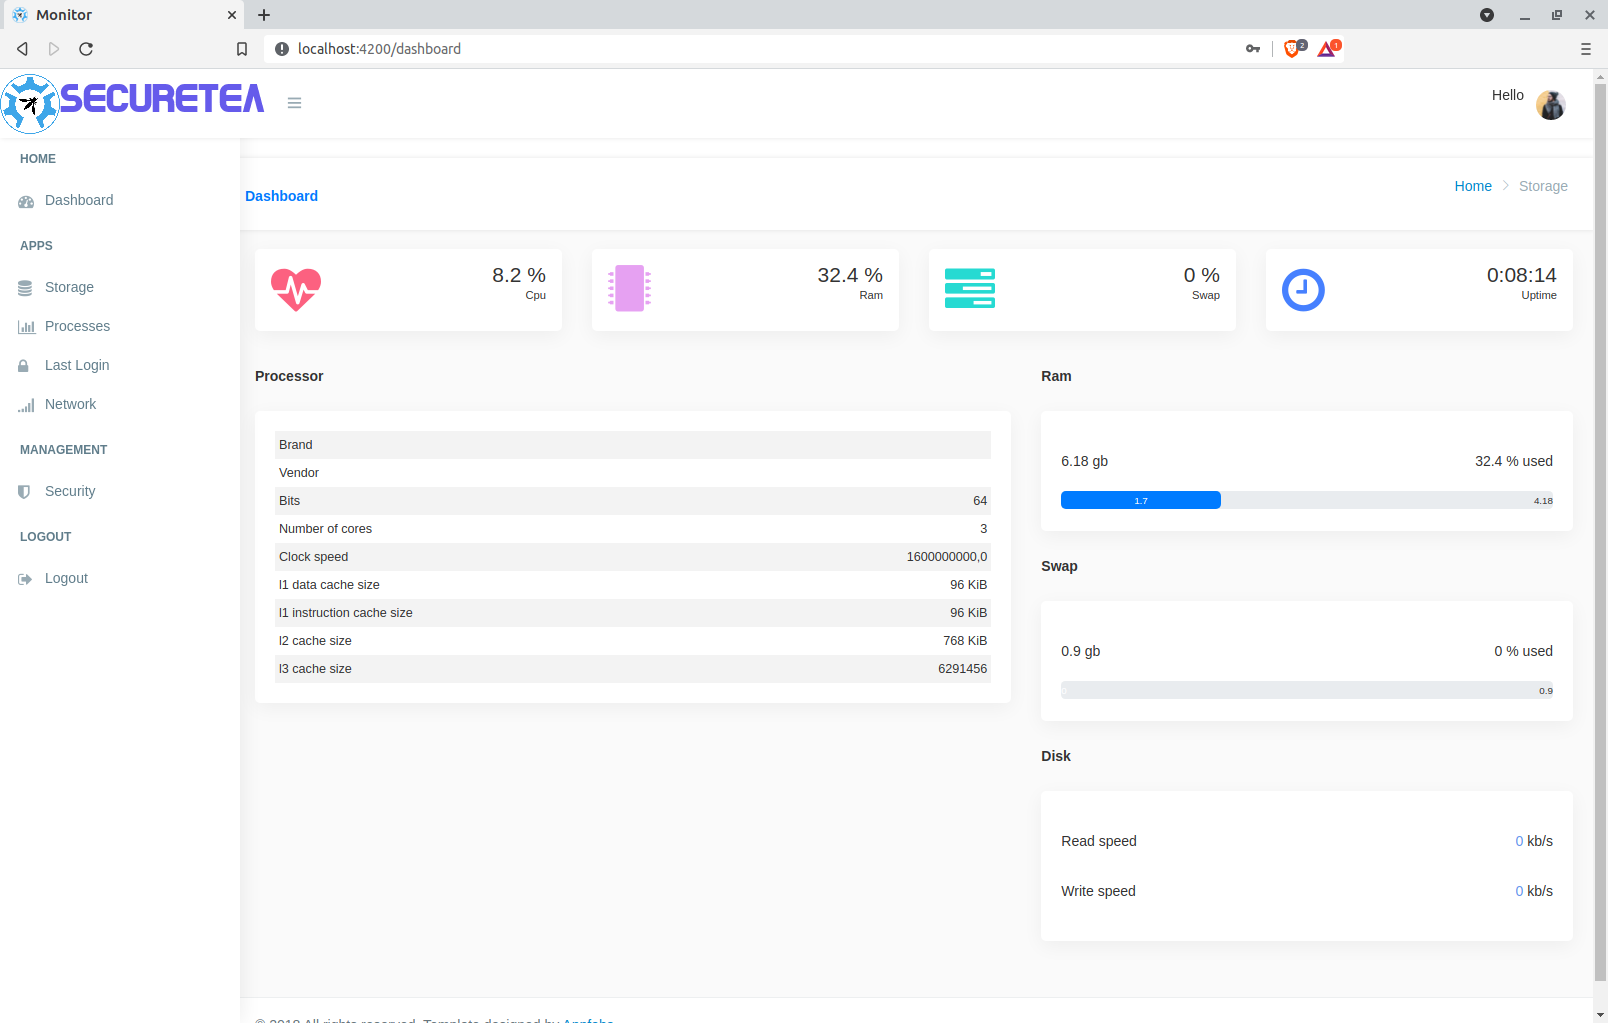 owasp/securetea-project
The OWASP SecureTea Project provides a one-stop security solution for various devices (personal computers / servers / IoT devices)
 mthbernardes/artlas
Apache Real Time Logs Analyzer System