
ModSecurity
 owasp-modsecurity/modsecurity
ModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…
anti-botapi-securitydefensive-tools+7
9.7k
owasp-modsecurity/modsecurityModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…
 dragon-lady/netward-standalone
User-space bot and DDoS deflection for small HTTP services
 oscerd/cve-2026-85260
Runnable Spring Boot and Quarkus reproducer for CVE-2026-85260, demonstrating camel-mllp PHI logging in affected versions and suppression after the…
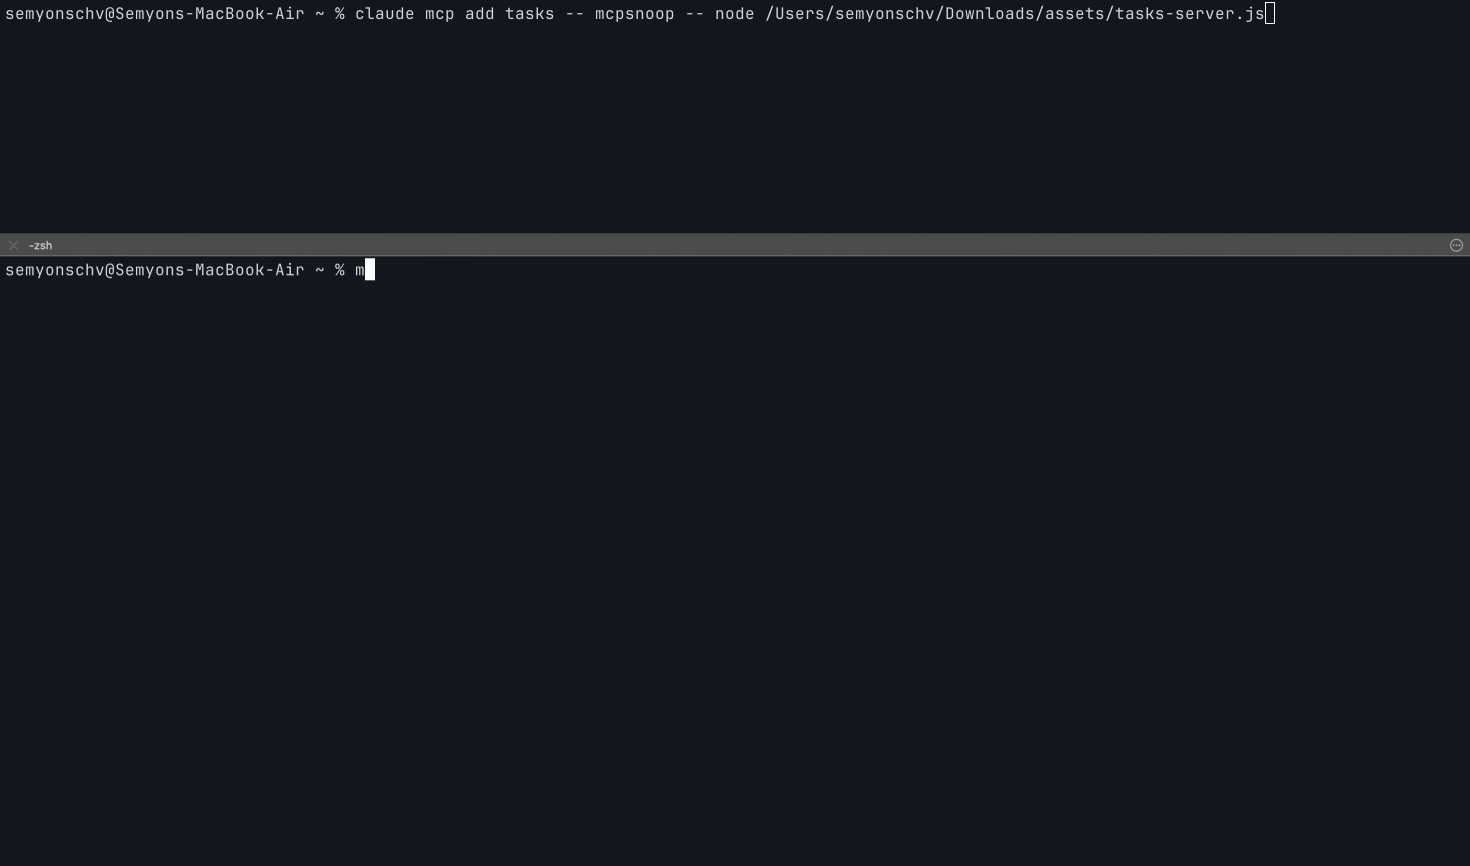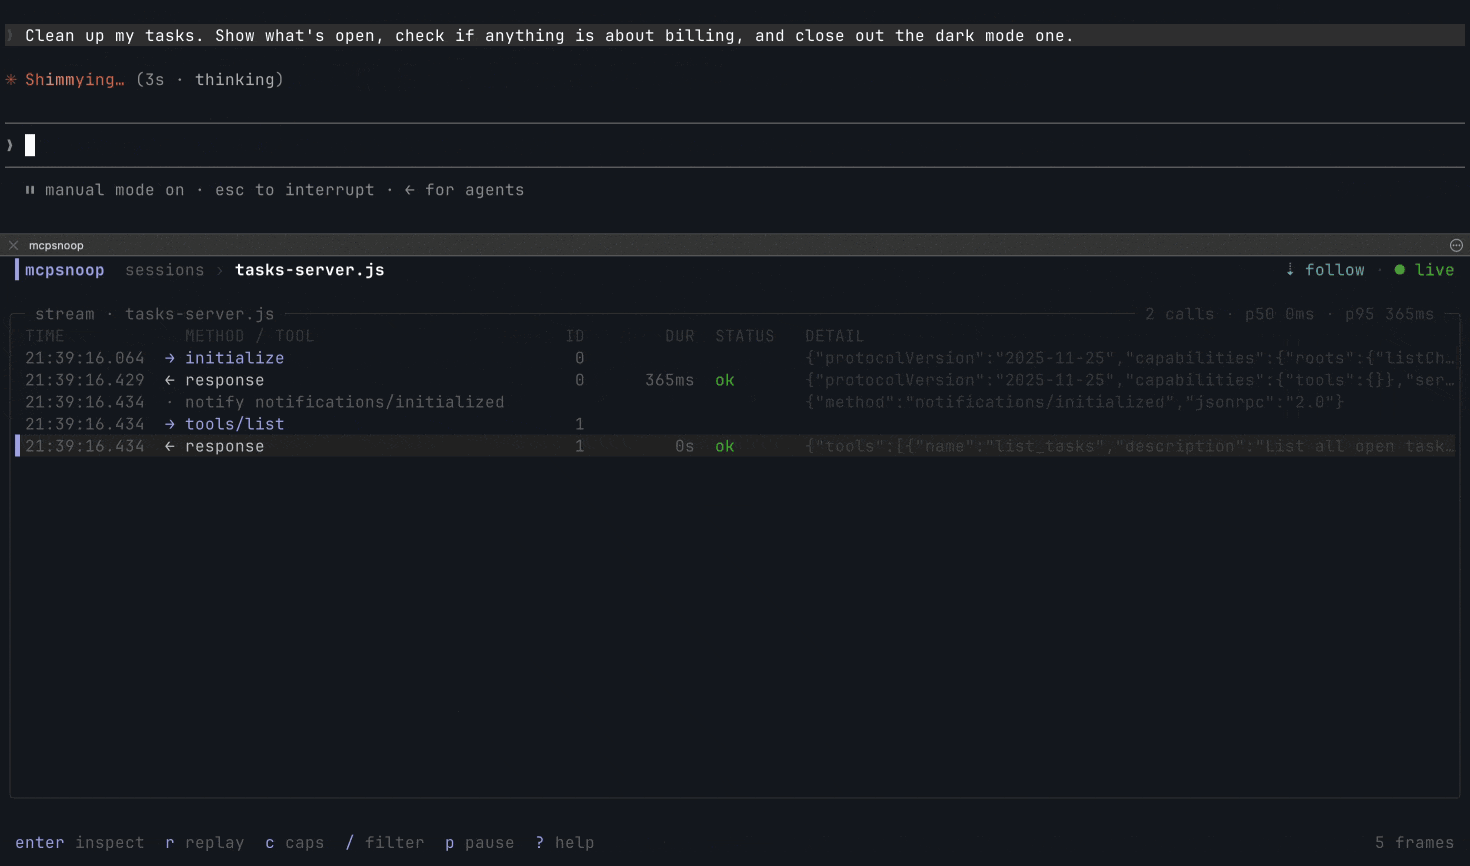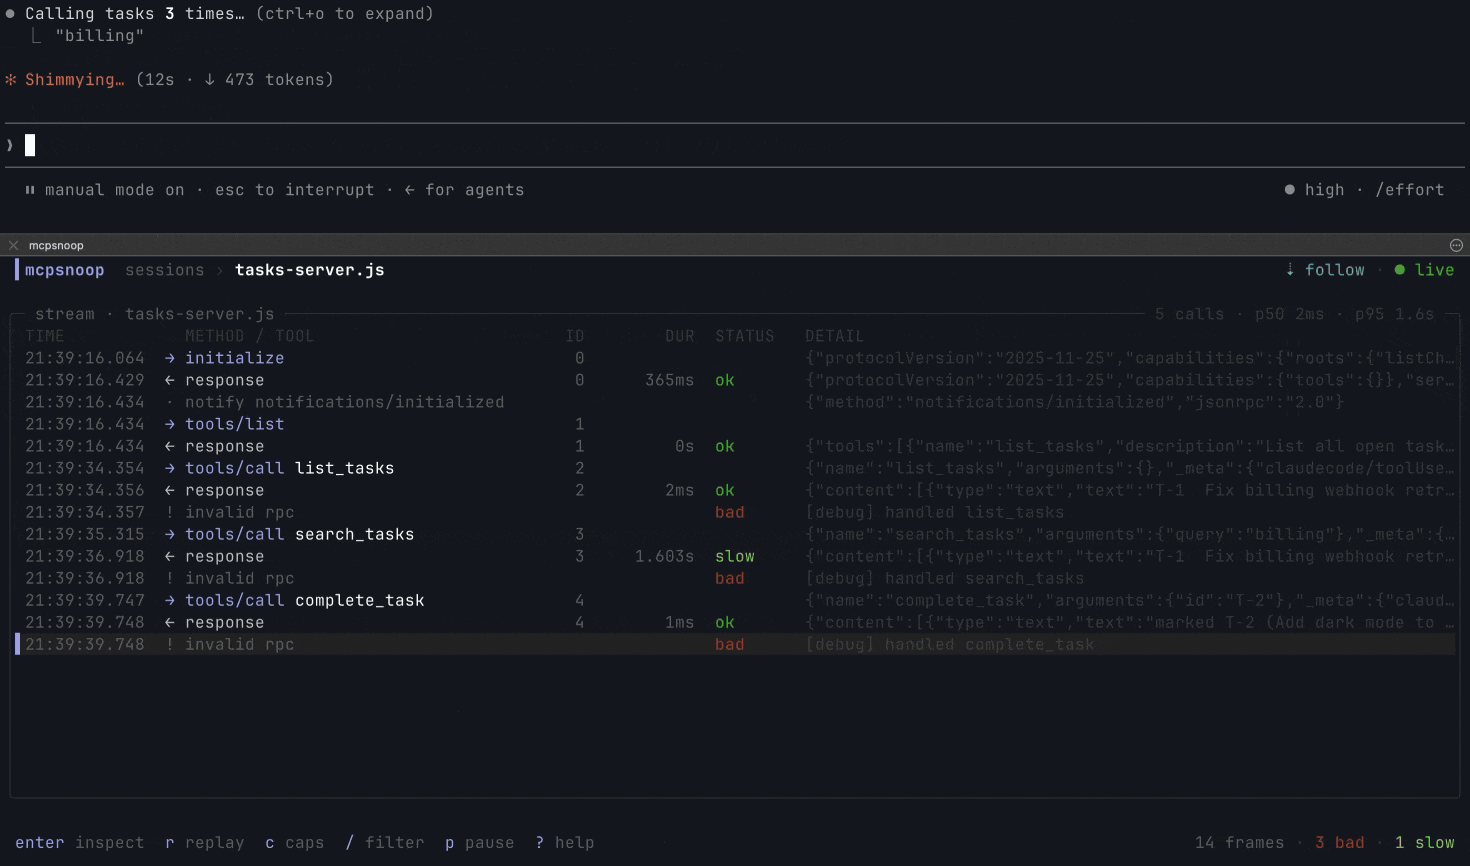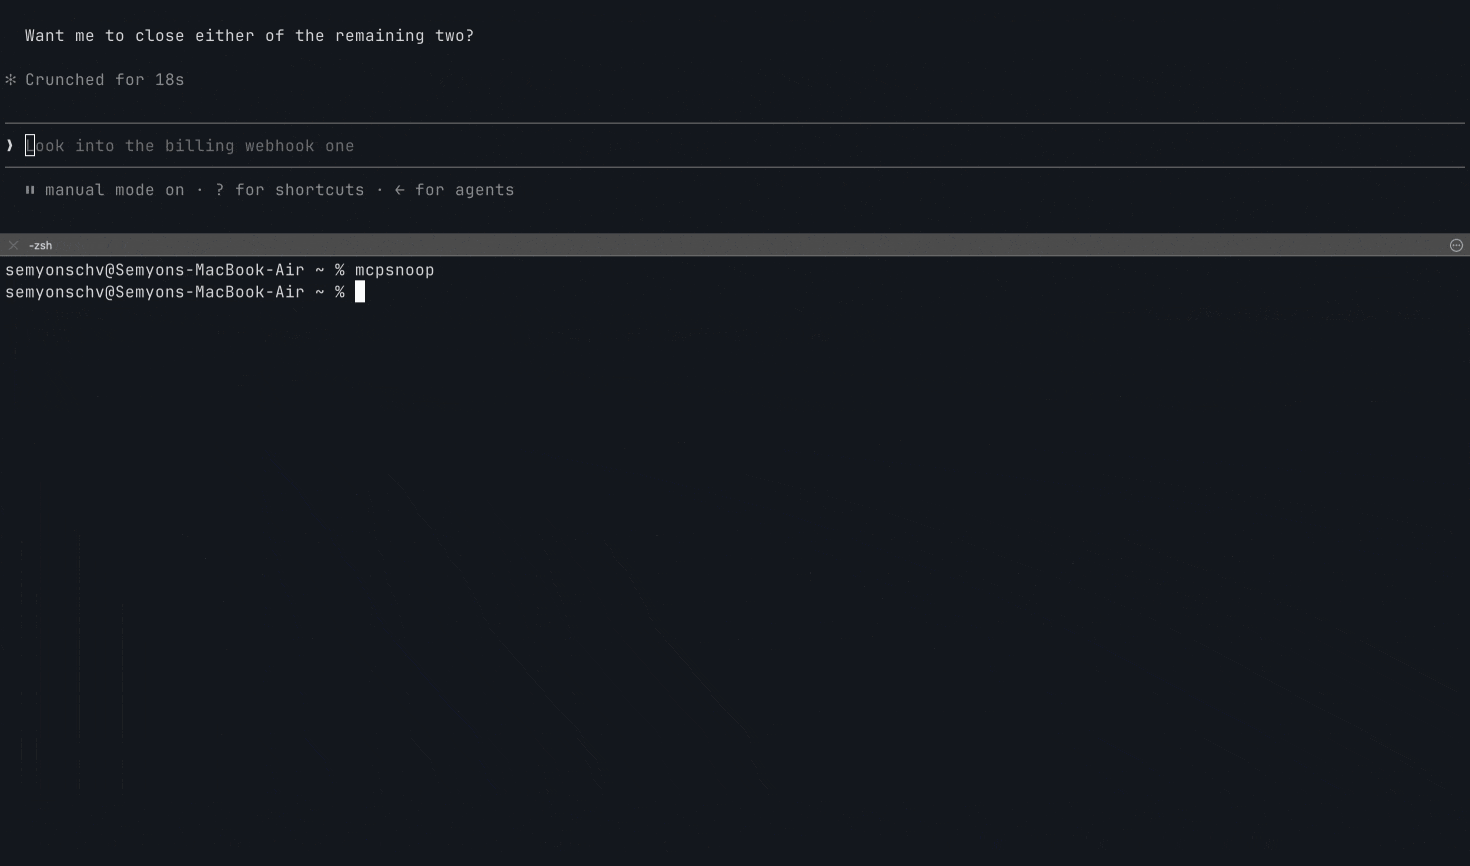 kerlenton/mcpsnoop
Wireshark for MCP. A transparent proxy between your AI client and MCP server. Watch every call live in your terminal, fail CI on what it finds,…
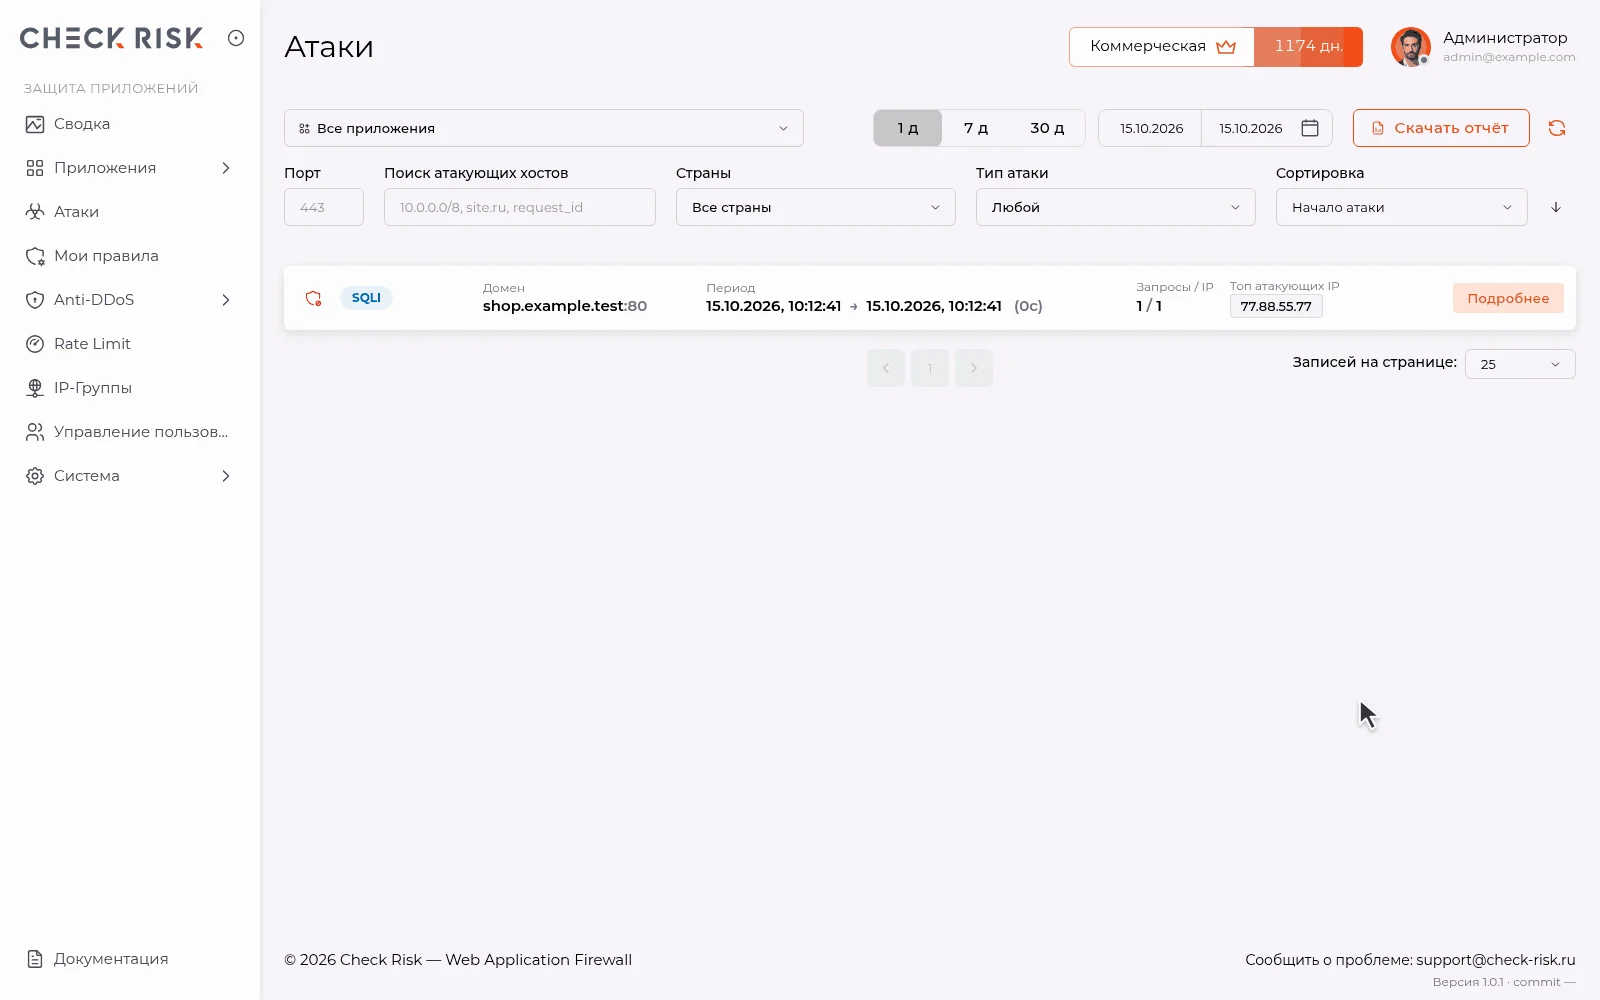 check-risk-waf/check-risk-waf
Reverse-proxy web application firewall with WAF, anti-bot and anti-DDoS protection at L3/L4/L7, custom rules, rate limiting, geo/IP filtering and…
 cmpnn-romain/cve-2024-27198_lab
Lab for the CVE-2024-27198
 confused-binary/waf-fu
Terminal UI for browsing and replaying AWS WAF v2 logs from CloudWatch, S3, and the sampling API, with YAML filtering, auth detection, and…
 icemoonhsv/tats
Analyze and track OAuth 2.0, OIDC, and Microsoft Entra ID tokens from Burp, mitmproxy, or Chrome DevTools captures. Visualize token lifecycles,…
 wattocyber/masq
Live recon and posture auditing for AI agent infrastructure: scans MCP configs, session logs, and APIs for secrets, poisoned catalogs, and CoT leaks.
 kaleth4/cve-2026-64638
Technical analysis and defensive mitigation for a WordPress Core pre-auth XSS-to-RCE chain, including sanitizer bypass, DOM clobbering, JSONP abuse,…
 glebusalt/cybersecurity_portfolio
Практические кейсы по информационной безопасности: развёртывание SIEM Wazuh и эксплуатация CVE-2021-41773
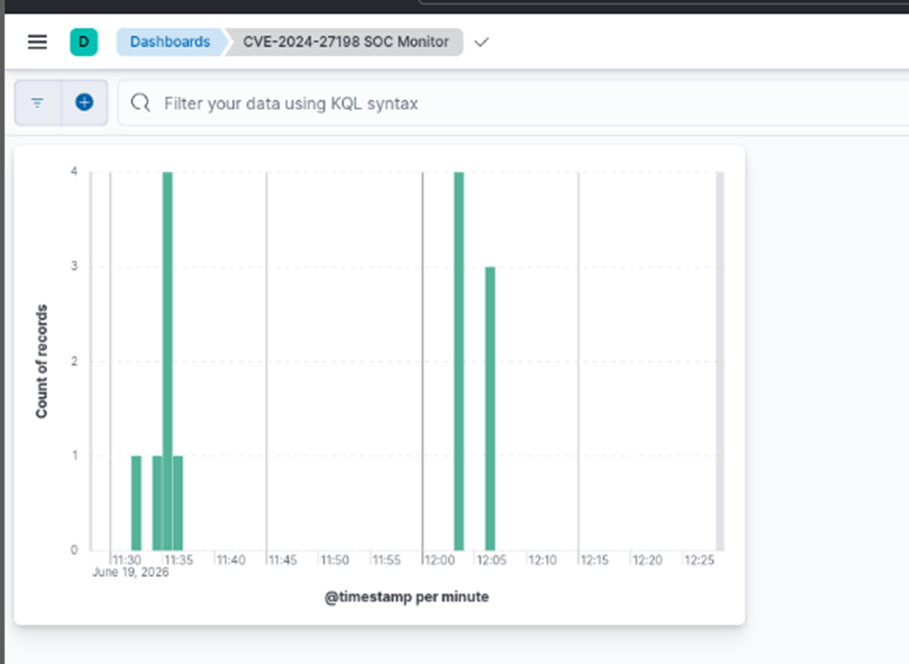 ptd200110/cve-2024-27198-soc-lab
SOC detection and incident response lab simulating CVE-2024-27198 authentication bypass in JetBrains TeamCity. Includes ELK SIEM, Suricata IDS, Sigma…
 ne0zer01/cve-2024-27198_lab
Docker-based lab for CVE-2024-27198 TeamCity authentication bypass. Includes exploit reproduction, IoC hunting with Sigma/Suricata rules, and…
 joaoreis13/flight-risk
Security toolkit for CVE-2025-55182 (React2Shell) — scan, detect, correlate, and test React Server Components RCE vulnerability
 d0rb/packetpirate
A headless , scriptable, command-line based MITM proxy designed for network traffic interception, analysis, and modification on Windows systems.
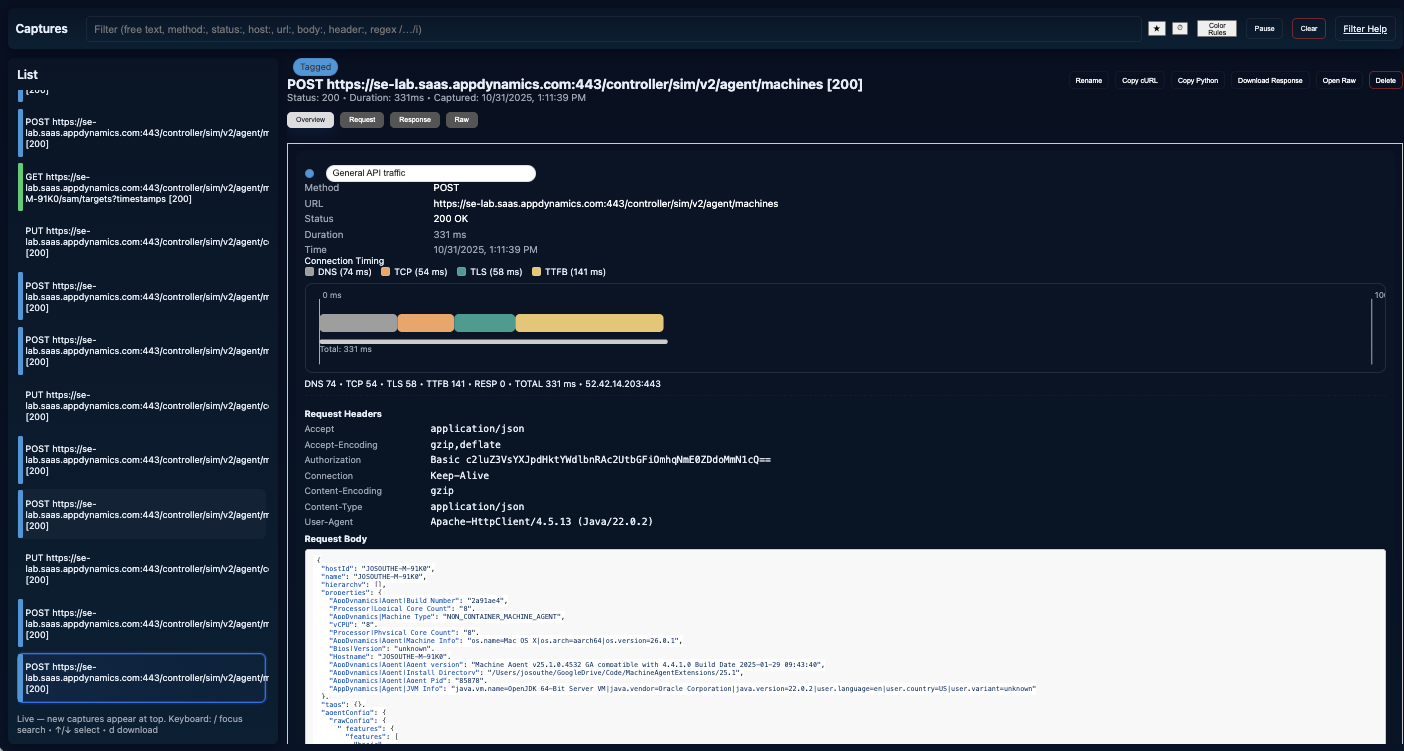 jbsouthe/http-breakout-proxy
HTTP Proxy Analysis for reverse engineering protocol communication
 cherrling/cve-2025-56499
Proof-of-concept exploit for CVE-2025-56499, demonstrating arbitrary file read via missing path validation in mihomo's rule-provider configuration,…
 zephrfish/cve-2025-53770-scanner
ToolShell scanner - CVE-2025-53770 and detection information