CVE-2025-61882-Oracle-E-Business-Suite-Pre-Auth-RCE-Exploit

A critical pre-authentication Remote Code Execution (RCE) flaw in Oracle E-Business Suite (versions 12.2.3 - 12.2.14) allows attackers to gain full…

A critical pre-authentication Remote Code Execution (RCE) flaw in Oracle E-Business Suite (versions 12.2.3 - 12.2.14) allows attackers to gain full…

Add POST body excerpt to Bro's HTTP log

ModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…

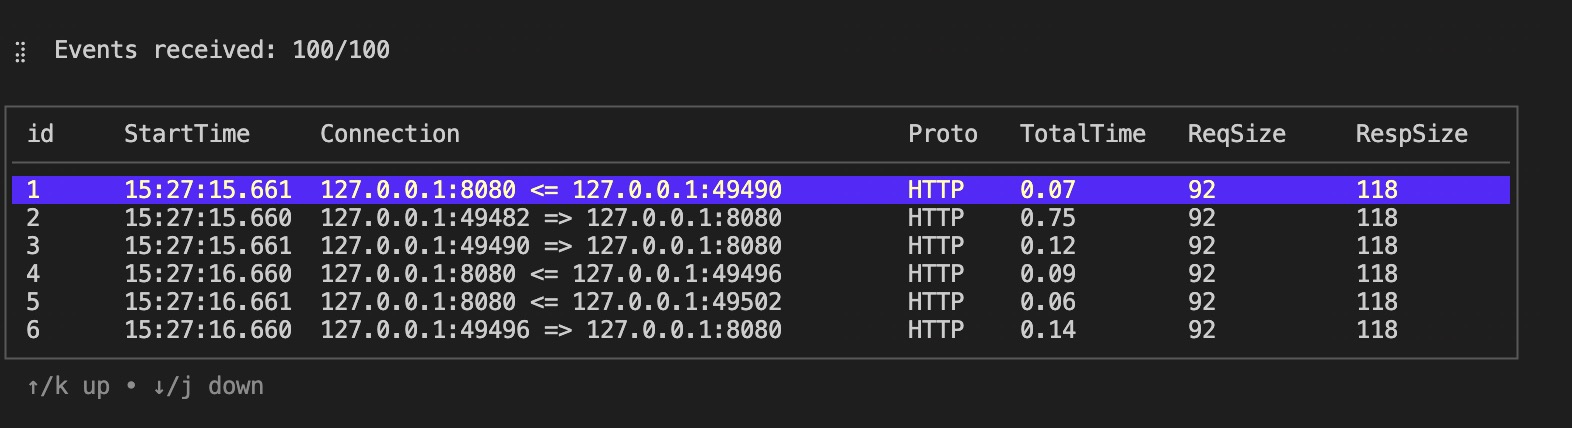
Kyanos is a networking analysis tool using eBPF. It can visualize the time packets spend in the kernel, capture requests/responses, makes…

PEAK Baseline Threat Hunt dashboards for Security Onion 3.0 — covering DNS, HTTP, TLS, SMB, Kerberos, SSH, RDP, DCE/RPC, LDAP, Modbus, DNP3,…

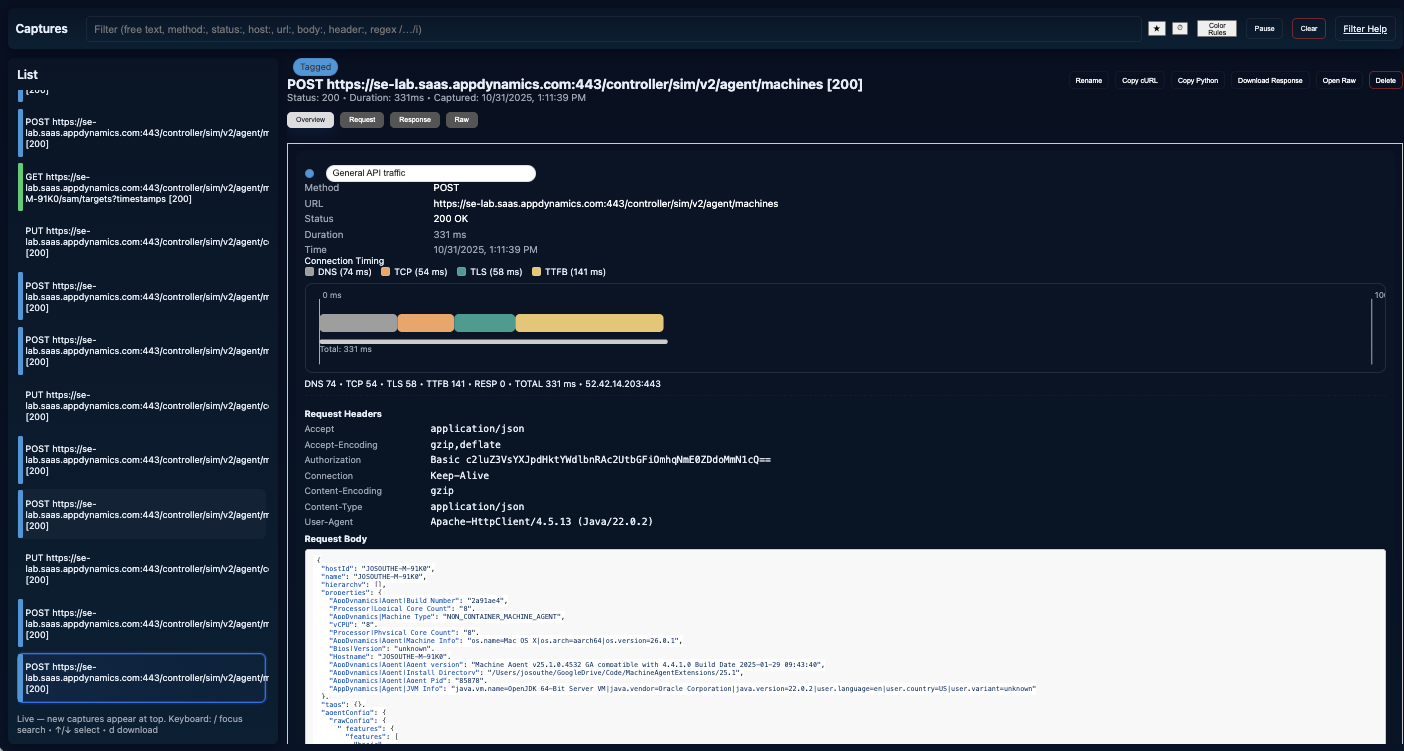
HTTP Proxy Analysis for reverse engineering protocol communication

Sigma rule for detecting CVE-2025-29927 exploitation via suspicious x-middleware-subrequest HTTP headers in Next.js applications, with detection…

Zeek package for detecting Log4j CVE-2021-44228 exploit attempts via HTTP header payloads, LDAP Java class downloads, and second-stage Java class…

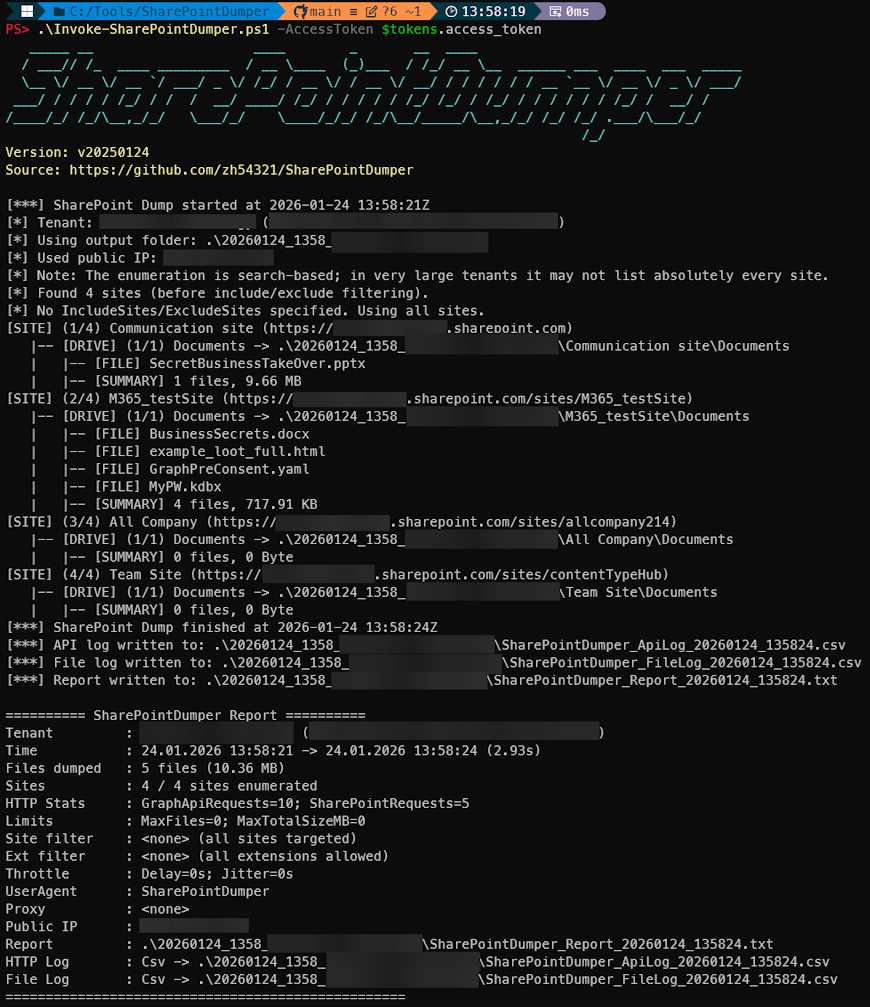
PowerShell SharePoint extraction + auditing tool for red/blue/purple teams. Enumerates all SharePoint sites/drives a user can access via Microsoft…

Blue Team lab focused on analyzing Apache web access logs to detect directory brute forcing and web scanning activity.

Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…

Open-source IDS/IPS and WAF engine that analyzes logs and HTTP requests to detect and block malicious IPs, leveraging a crowdsourced community…

Dockerized honeypot for CVE-2021-44228.

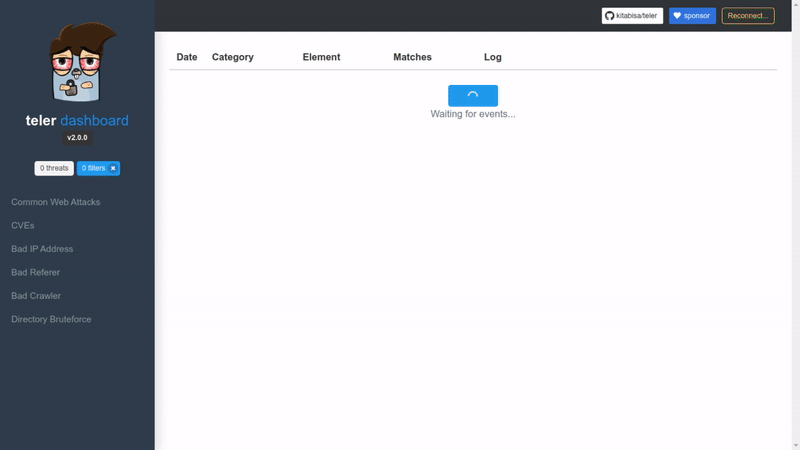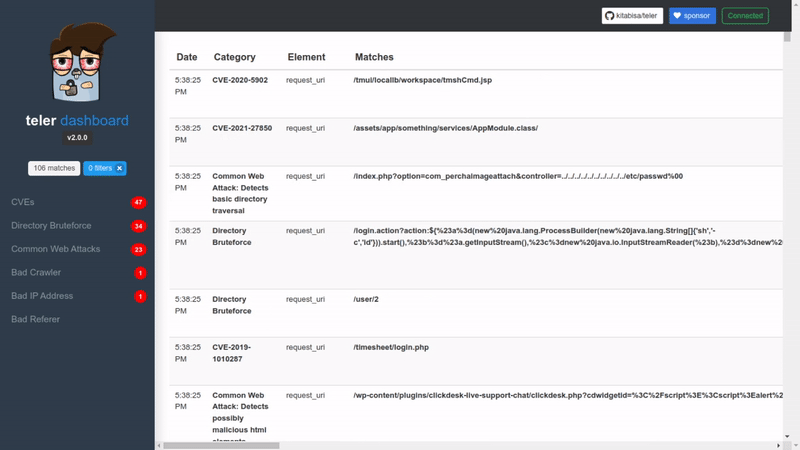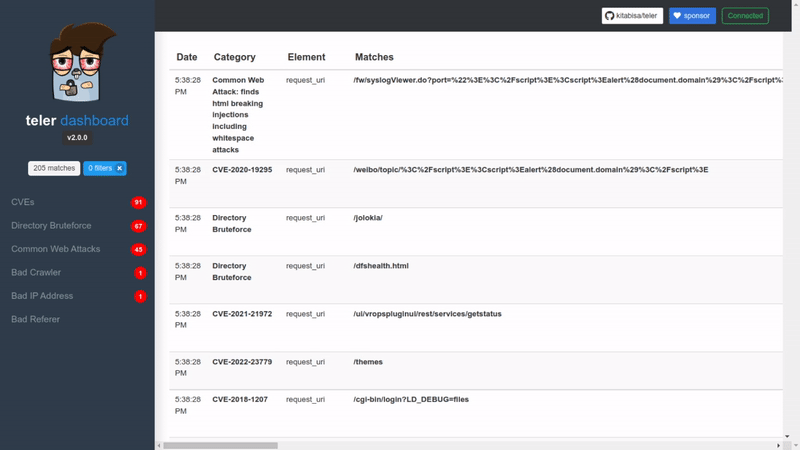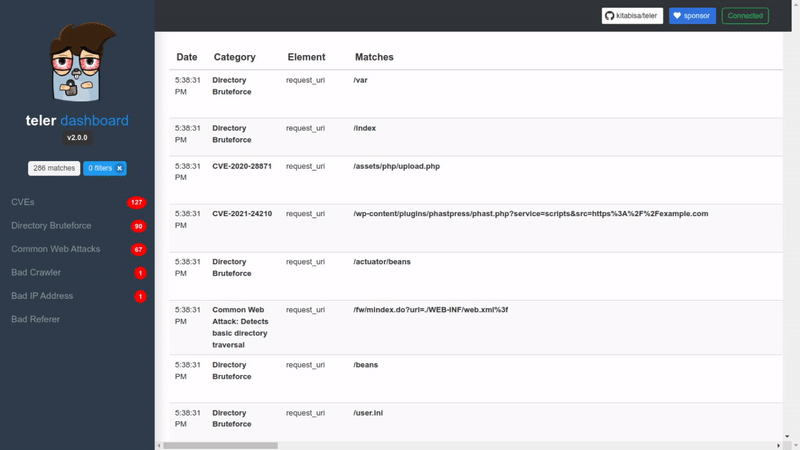
Real-time HTTP Intrusion Detection