
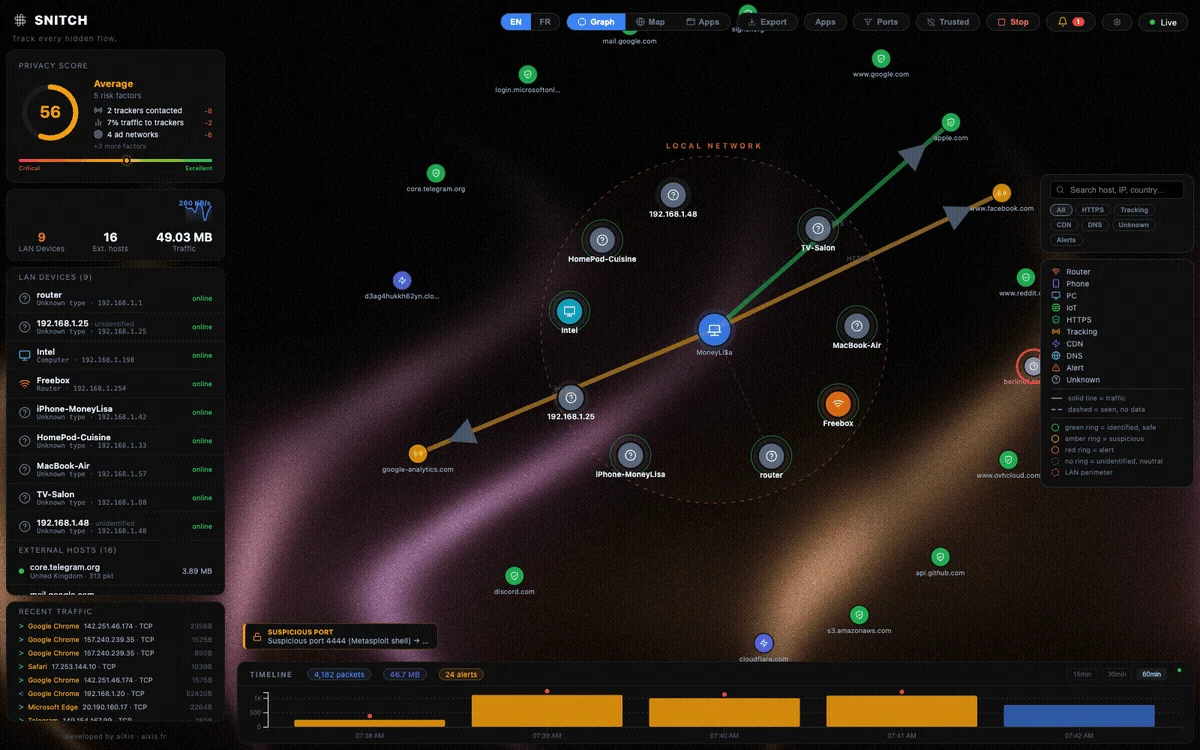
Snitch
 aixisstudio/snitch
Real-time network monitor + outbound firewall — see & block every connection. Privacy-first, local-first, Rust fleet agent, SIEM exports, 8…
anomaly-detectiondefensive-toolsdns-analysis+6
681
aixisstudio/snitchReal-time network monitor + outbound firewall — see & block every connection. Privacy-first, local-first, Rust fleet agent, SIEM exports, 8…
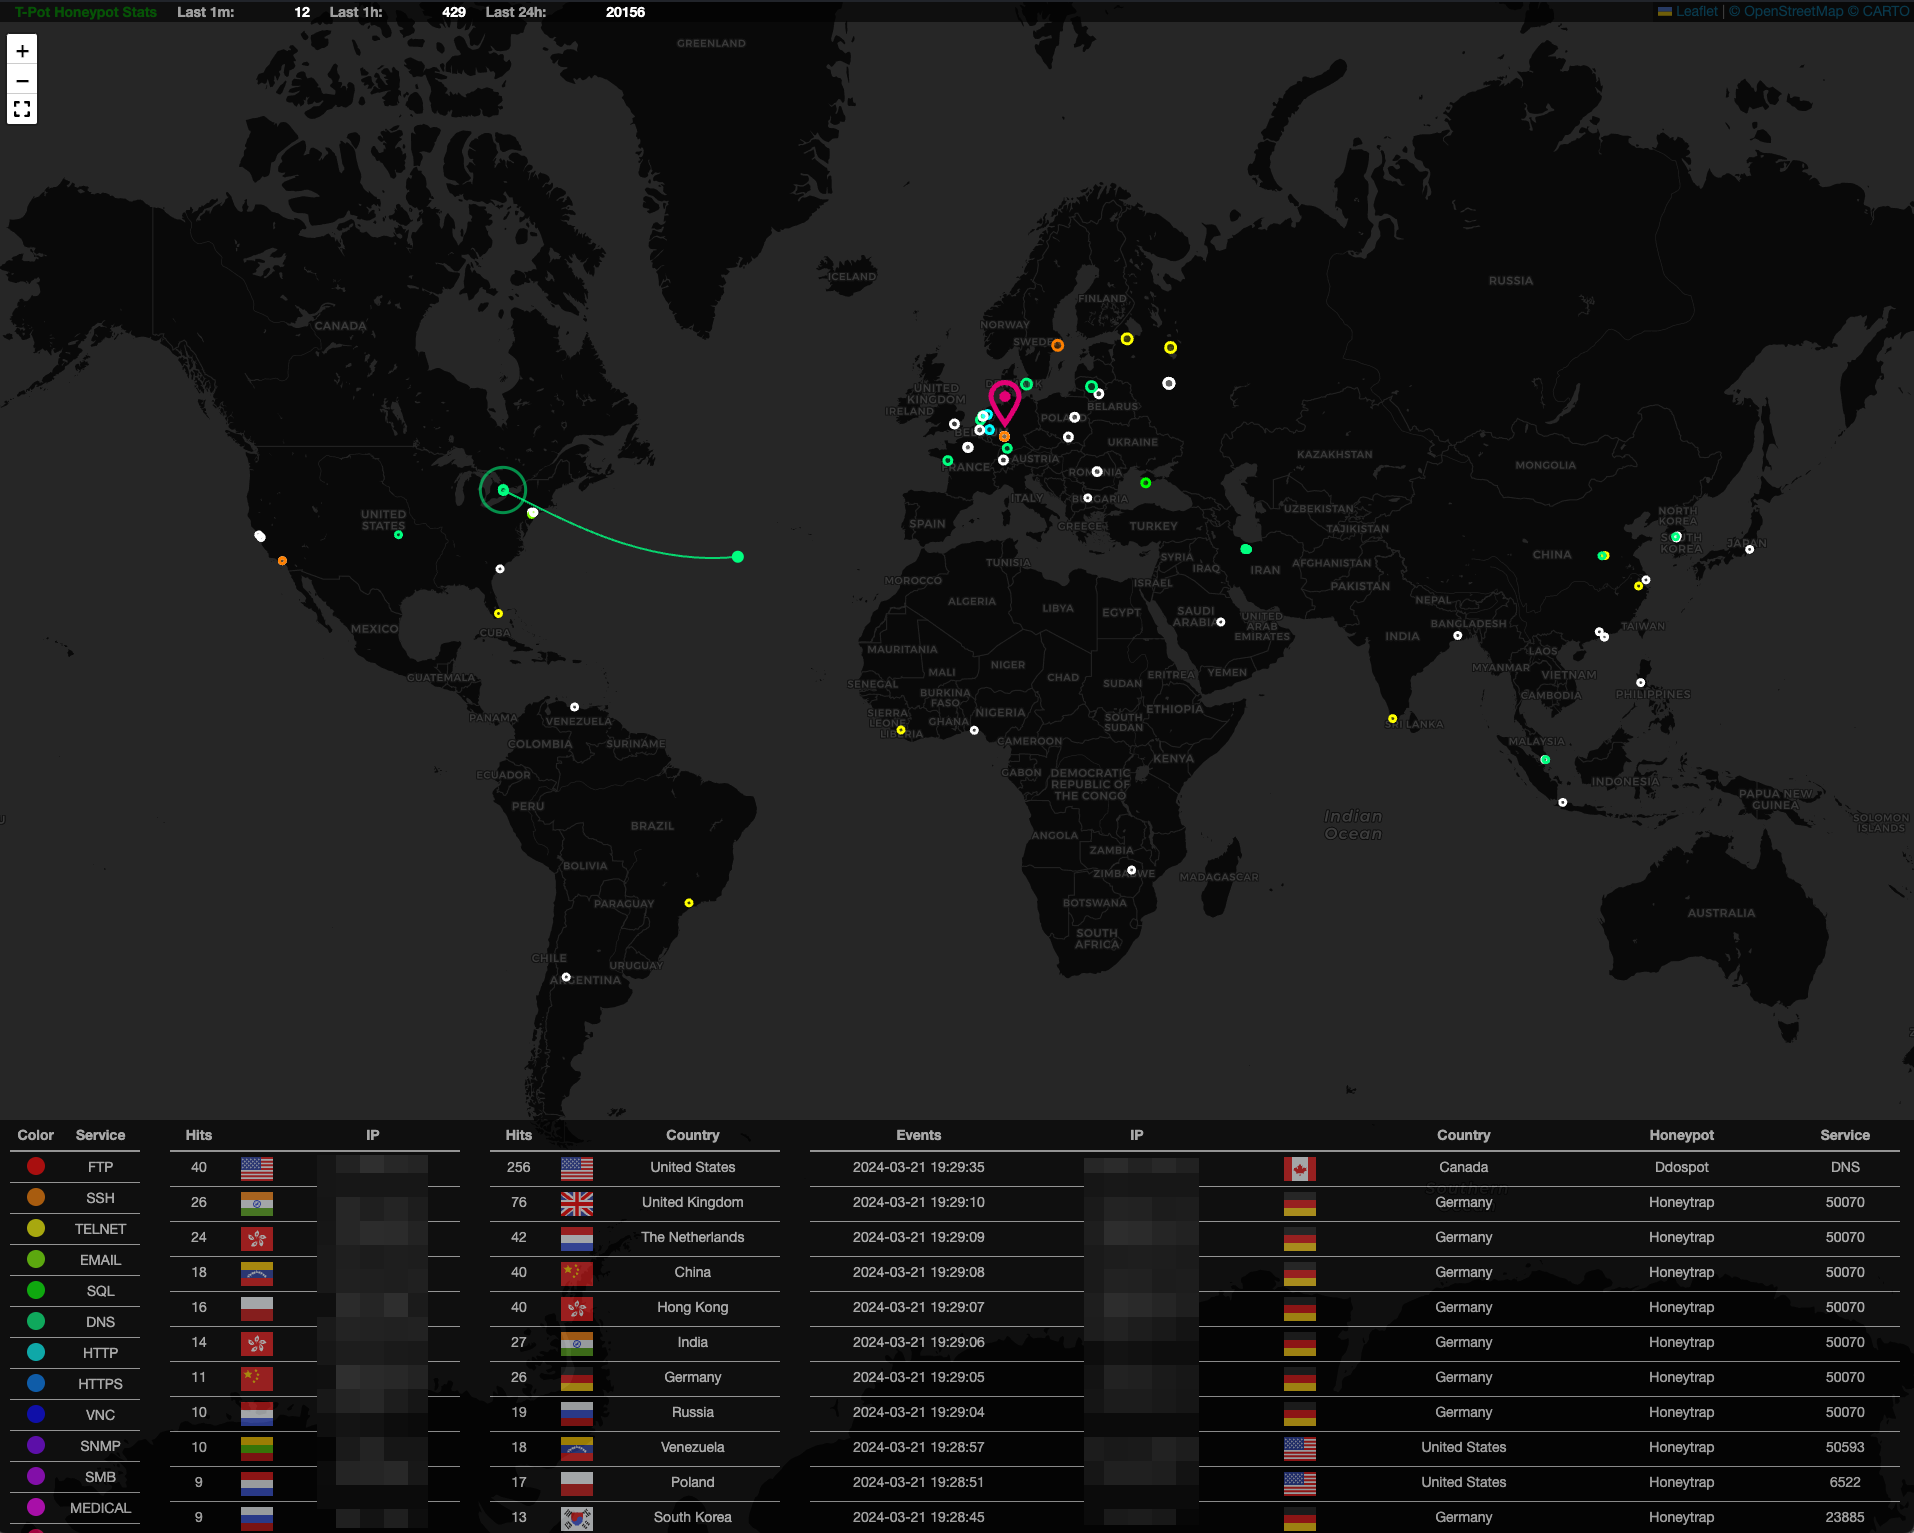 telekom-security/tpotce
🍯 T-Pot - The All In One Multi Honeypot Platform 🐝
 devinblack001/ddos-reduction-system
Adaptive two-stage Layer 4 DDoS mitigation gateway using behavioral traffic analysis, Random Forest classification, and kernel-level ipset/iptables…
 usarmyresearchlab/dshell
Dshell is a network forensic analysis framework.
 kerlenton/mcpsnoop
Wireshark for MCP. A transparent proxy between your AI client and MCP server. Watch every call live in your terminal, fail CI on what it finds,…
 bert-janp/entratrace
Defensive research tool that documents observable API endpoints and user agents of offensive tooling targeting Microsoft Entra ID, supporting…
 ivankovic/stop-bots
Automate stopping bad bots from accessing your server
 abdaullahag/threatlens
Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…
 meirwah/awesome-incident-response
Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…
 gopasteverything/gpewebdefender
Lightweight web-attack monitor. One Go binary + SQLite. Not OSSEC, not a WAF.
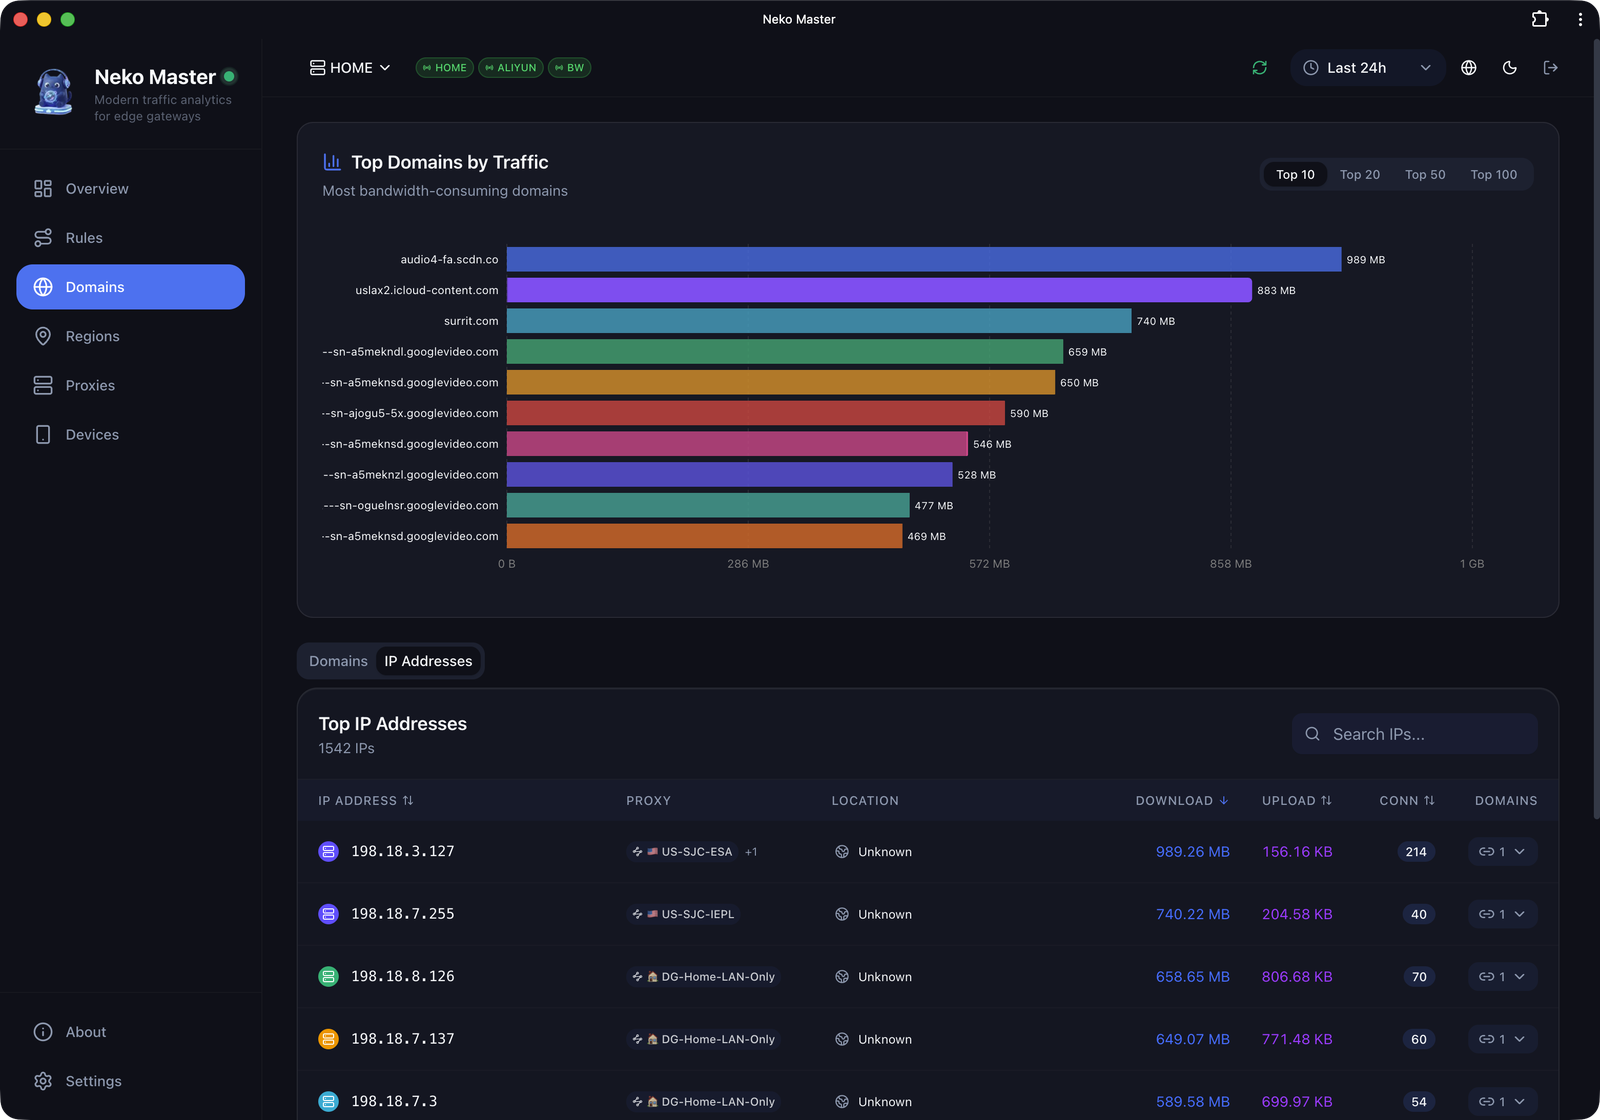 foru17/neko-master
A modern and elegant dashboard for network traffic visualization and analysis.
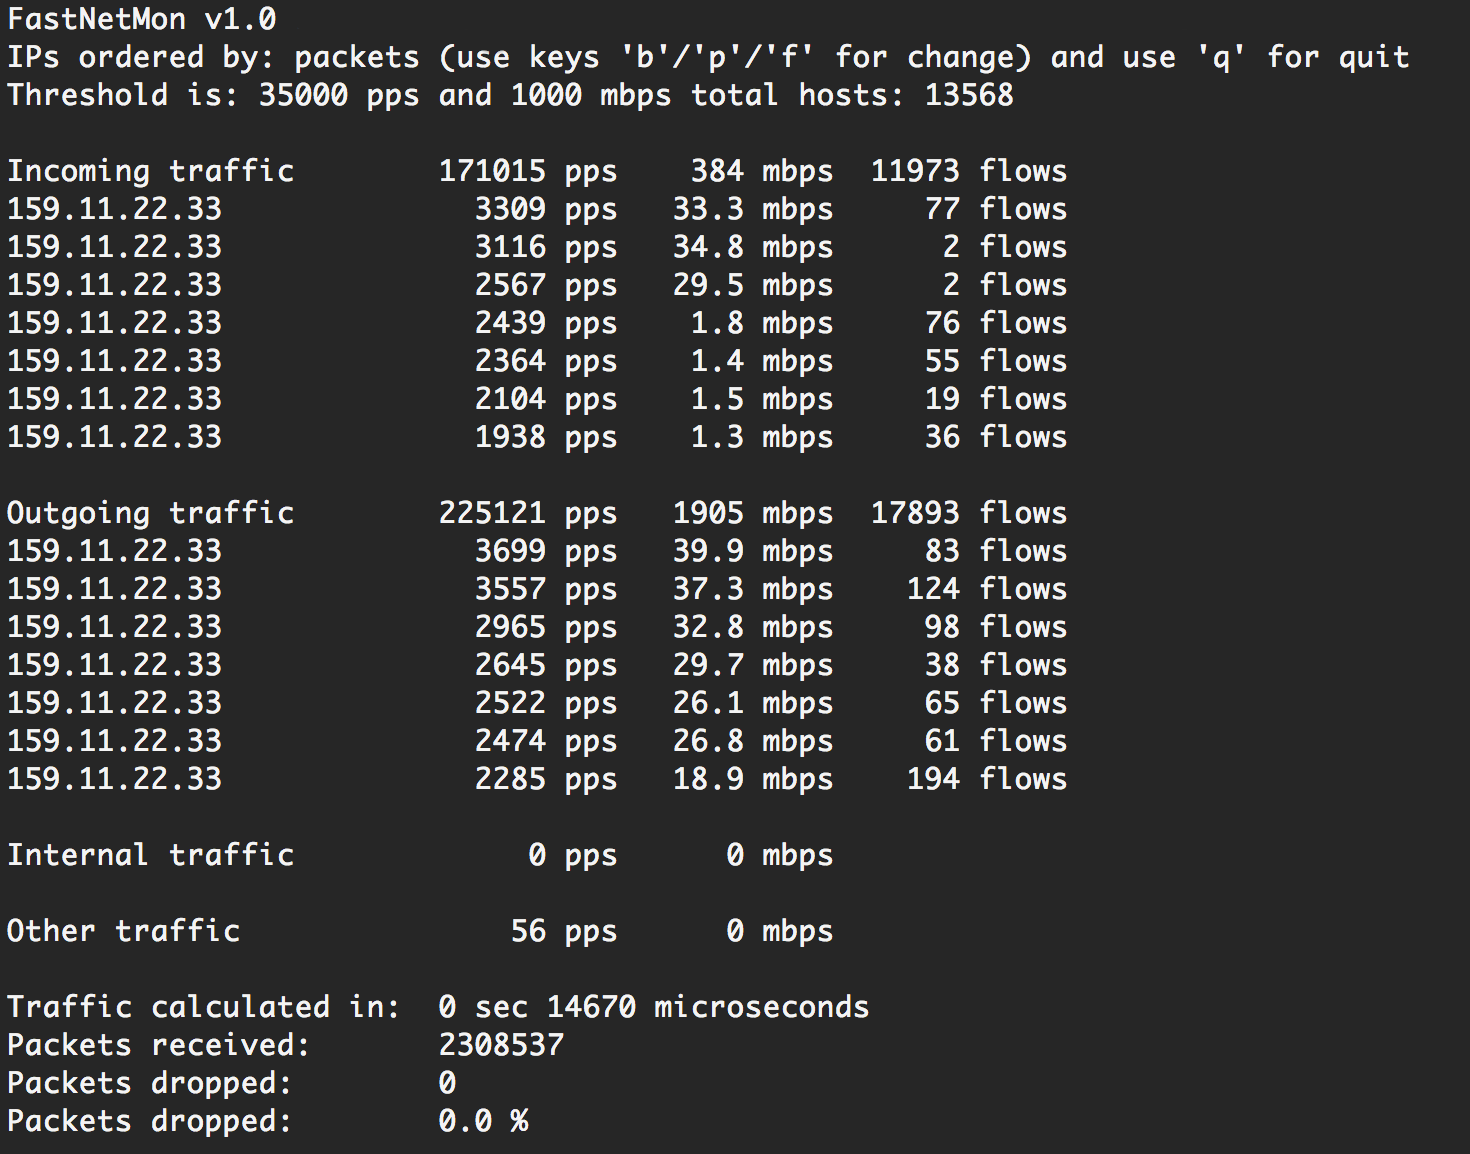 pavel-odintsov/fastnetmon
Very fast DDoS sensor with sFlow/Netflow/IPFIX/SPAN support
 ethan-andrews/threatintel-aggregator
Self-hosted threat intelligence platform — feed aggregation, AI triage, MITRE ATT&CK coverage, and Sentinel-integrated detection engineering. Runs…
 jev-sec/jev-ids
Blazing-Fast Token-Efficient Intrusion Detection System (IDS) based on TypeSafe's Jev.
 imthenachoman/how-to-secure-a-linux-server
Step-by-step guide for hardening a Linux server, covering SSH security, firewalls, intrusion detection, auditing, and system configuration to reduce…
 gitlab-security-oss/tldr
Sigma-based detection rules, log queries, atomic tests, and response procedures for monitoring and threat hunting in GitLab environments.
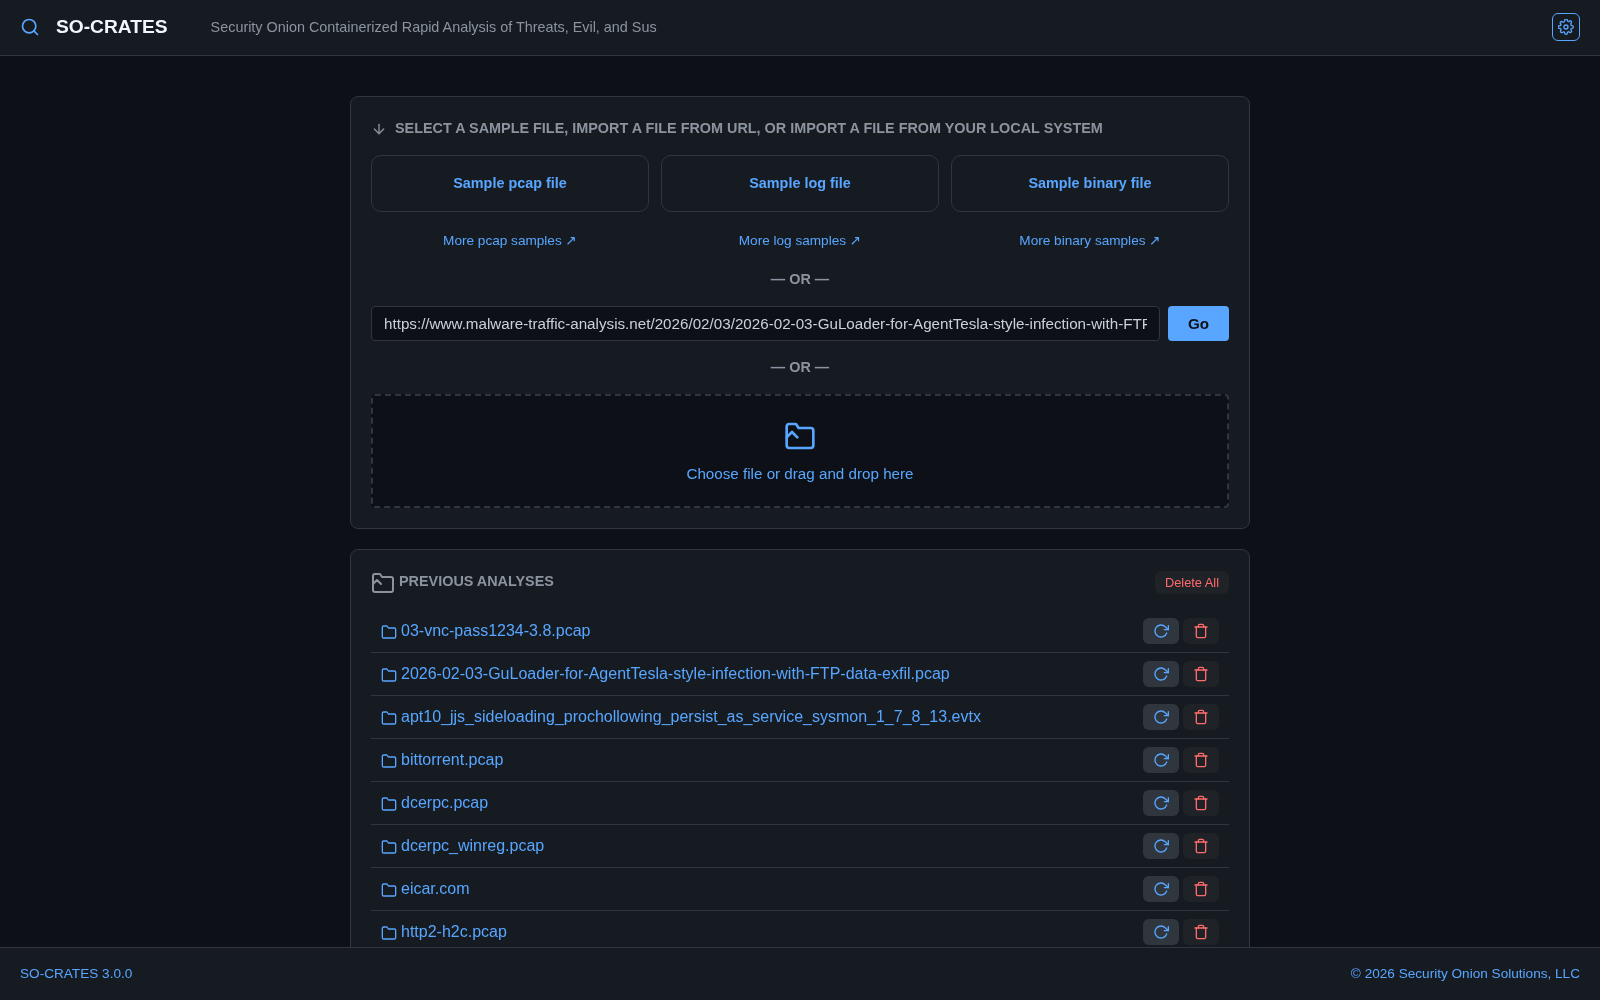 dougburks/so-crates
SO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!
 niffyhunt/wraithwall-toolkit
Deception-engineering tools pulled from a production platform that takes live attacker traffic, supply-chain canary tokens, honeypot logs → MITRE…