Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
96 results
Incident-Response-Powershell preview

Incident-Response-Powershell

GitHubbert-janp/incident-response-powershell

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…

digital-forensicsdisk-forensicsforensics+6
812
3 months ago
IfritProxy preview

IfritProxy

GitHub0tsystemspublicrepos/ifritproxy

IFRIT is an AI-powered reverse proxy that intercepts incoming requests in real time, classifying each one as legitimate or malicious. Legitimate…

ai-securitydefensive-toolsids-ips-evasion+7
17 months ago
CyberDefense-Lab preview

CyberDefense-Lab

GitHubumidguluzada/cyberdefense-lab

A complete Blue Team Cybersecurity Lab featuring pfSense, Suricata, and ELK Stack for network monitoring and threat detection.

educationids-ips-evasionintrusion-detection+5
61 month ago
ThreatIntel-Aggregator preview

ThreatIntel-Aggregator

GitHubethan-andrews/threatintel-aggregator

Self-hosted threat intelligence platform — feed aggregation, AI triage, MITRE ATT&CK coverage, and Sentinel-integrated detection engineering. Runs…

ai-securitydefensive-toolsincident-response+7
144 days ago
MacOSThreatTrack preview

MacOSThreatTrack

GitHubab2pentest/macosthreattrack

Bash tool used for proactive detection of malicious activity on macOS systems.

digital-forensicsincident-responseinformation-gathering+1
3911 months ago
awesome-incident-response preview

awesome-incident-response

GitHubmeirwah/awesome-incident-response

Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…

curated-resourcesdigital-forensicsdisk-forensics+9
9.4k2 months ago
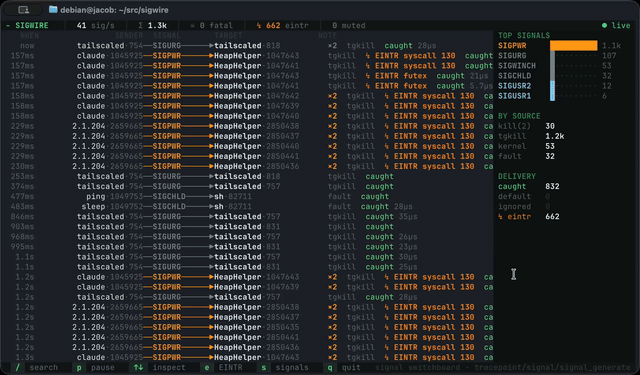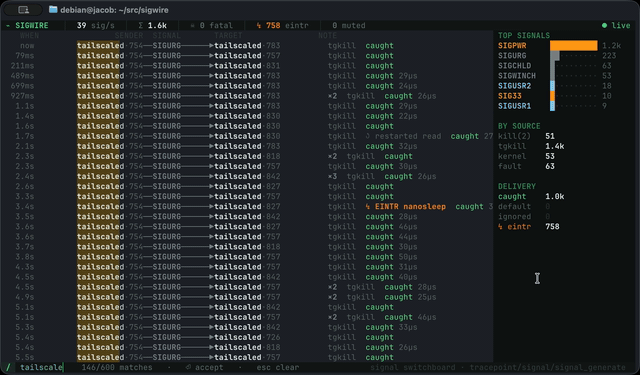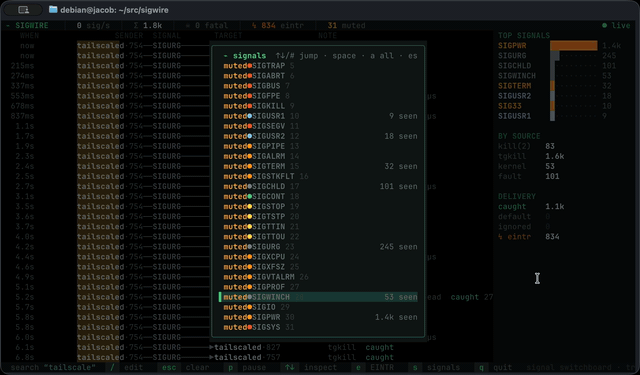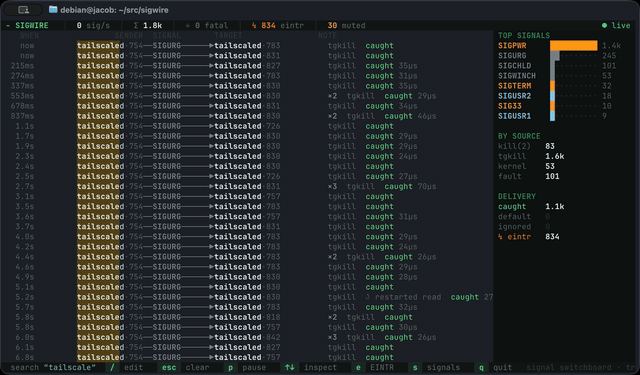
sigwire preview

sigwire

GitHubyeet-src/sigwire

Live kernel signal observability tool using eBPF tracepoints to stream every signal raised on a Linux host, showing sender, target, disposition,…

debuggersdynamic-analysis-sandboxingforensics+2
1611 month ago
santamon preview

santamon

GitHub0x4d31/santamon

Lightweight macOS detection agent built on Santa’s Endpoint Security telemetry.

defensive-toolsincident-responseintrusion-detection+2
1159 months ago
CVE-2024-4577 preview

CVE-2024-4577

GitHubahmetramazank/cve-2024-4577

Demonstrates exploitation of CVE-2024-4577, a PHP CGI RCE on Windows, including attack steps, reverse shell deployment, and ransomware simulation…

educationexploitationforensics+5
1 year ago
ARTLAS preview

ARTLAS

GitHubmthbernardes/artlas

Apache Real Time Logs Analyzer System

incident-responseintrusion-detectionlog-analysis+3
1255 years ago
iLEAPP preview

iLEAPP

GitHubabrignoni/ileapp

Parses iOS and iPadOS forensic extractions into HTML, TSV, timeline, KML, and LAVA reports with modular artifact discovery and encrypted iTunes…

digital-forensicsforensicsincident-response+3
1.3k2h 28m ago
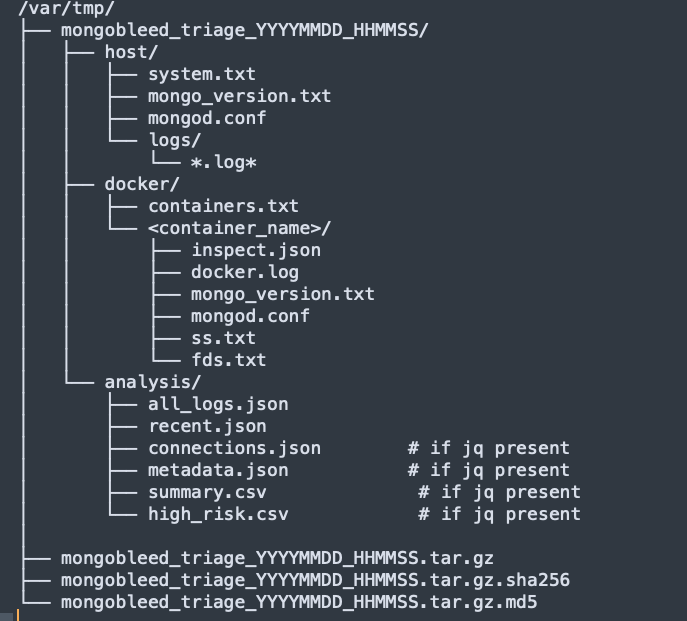
MongoBleed-DFIR-Triage-Script-CVE-2025-14847 preview

MongoBleed-DFIR-Triage-Script-CVE-2025-14847

GitHubjemhadar/mongobleed-dfir-triage-script-cve-2025-14847

The script focuses on safe artifact acquisition first, followed by optional on-host analysis, and produces a portable, hashed forensic archive…

container-securitydatabase-securitydigital-forensics+5
8 months ago
matano preview

matano

GitHubmatanolabs/matano

Open source security data lake for threat hunting, detection & response, and cybersecurity analytics at petabyte scale on AWS

cloud-securityincident-responselog-analysis+1
1.7k1 year ago
OSSEM preview

OSSEM

GitHubotrf/ossem

Community-driven project for documenting, standardizing, and modeling security event logs to improve detection analytics and data normalization…

curated-resourceseducationlog-analysis+1
1.3k3 years ago
DeTTECT preview

DeTTECT

GitHubrabobank-cdc/dettect

Detect Tactics, Techniques & Combat Threats

defensive-toolsincident-responseintrusion-detection+4
2.3k5 days ago
proxynotshell-IOC-Checker preview

proxynotshell-IOC-Checker

GitHubrjsudlow/proxynotshell-ioc-checker

Script to check for IOC's created by ProxyNotShell (CVE-2022-41040 & CVE-2022-41082)

forensicsincident-responseioc-management+3
53 years ago
fastnetmon preview

fastnetmon

GitHubpavel-odintsov/fastnetmon

Very fast DDoS sensor with sFlow/Netflow/IPFIX/SPAN support

anomaly-detectionincident-responselog-analysis+5
3.7k16 days ago
monitor preview

monitor

GitHubbetterdb-inc/monitor

Real-time monitoring and slowlog analysis for Valkey and Redis databases with anomaly detection, ACL auditing, and Prometheus metrics export.

anomaly-detectiondatabase-securitylog-analysis
1.3k2h 26m ago
Previous123456Next