

BLT
 owasp/blt
Monorepo of OWASP Bug Logging Tool projects: crowd-sourced vulnerability reporting, bug bounty workflows, CVE namespace, autopatching, and security…
curated-resourcesdevsecopseducation+7
owasp/bltMonorepo of OWASP Bug Logging Tool projects: crowd-sourced vulnerability reporting, bug bounty workflows, CVE namespace, autopatching, and security…
 jivoi/awesome-osint
😱 A curated list of amazingly awesome OSINT
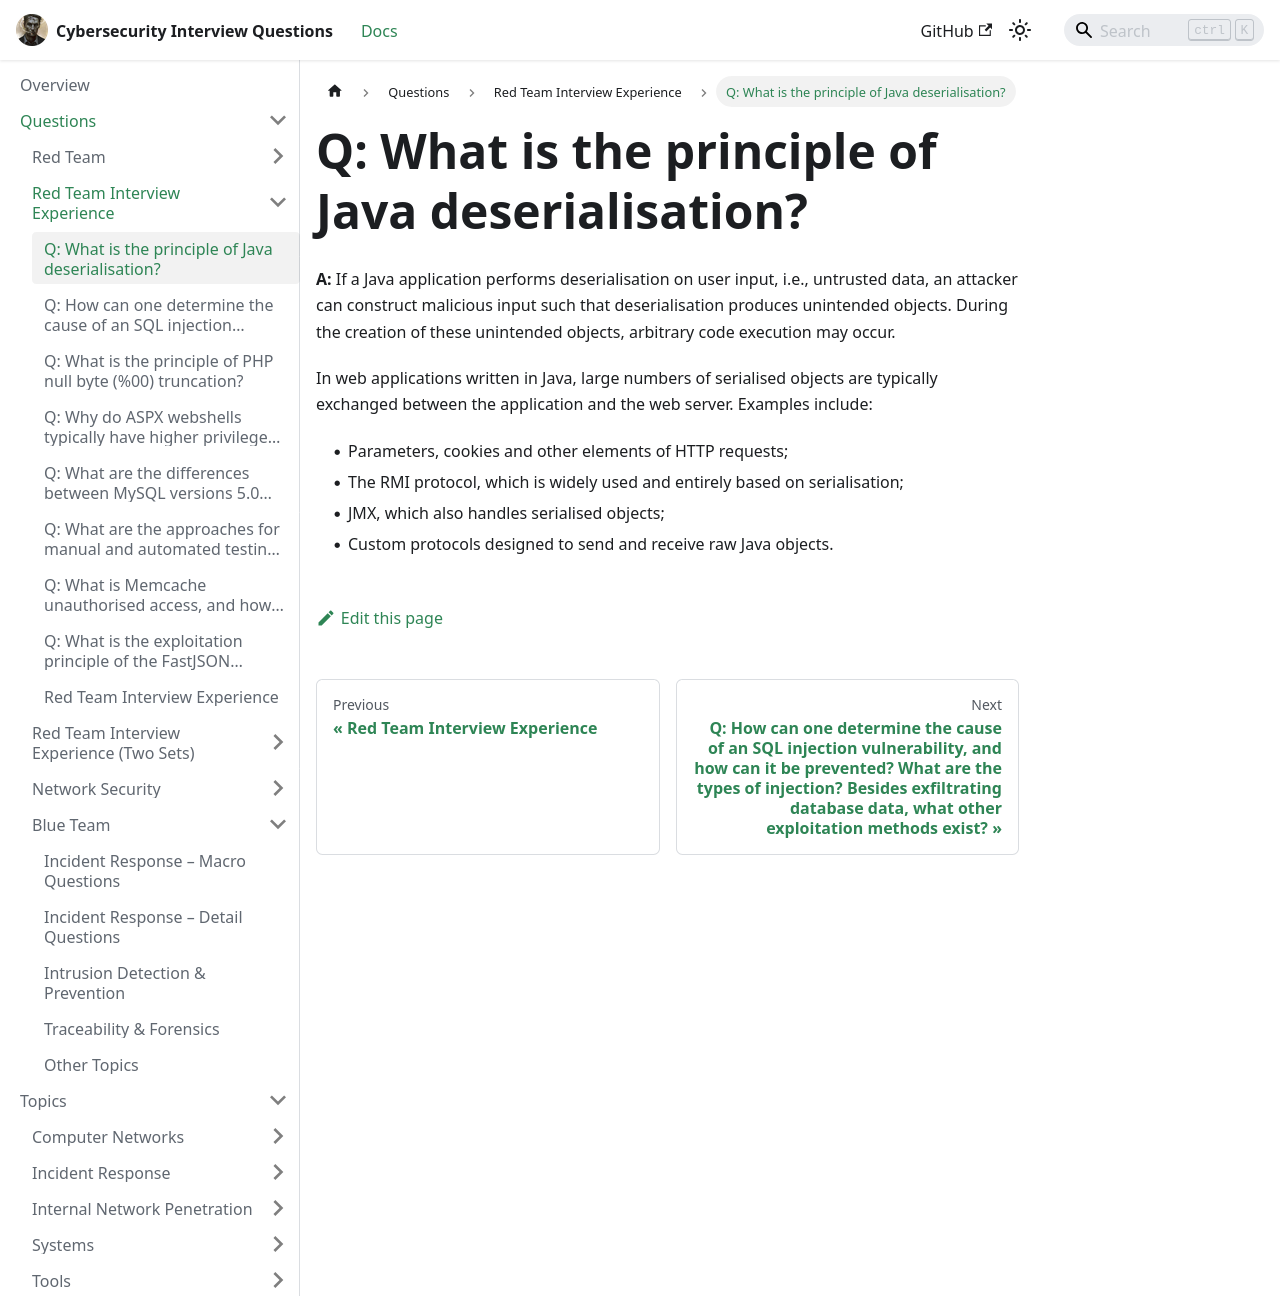 excalibra/cybersecurity-interview-questions
Curated collection of 200+ cybersecurity interview questions and answers covering Red Team, Blue Team, Web Security, Incident Response, and network…
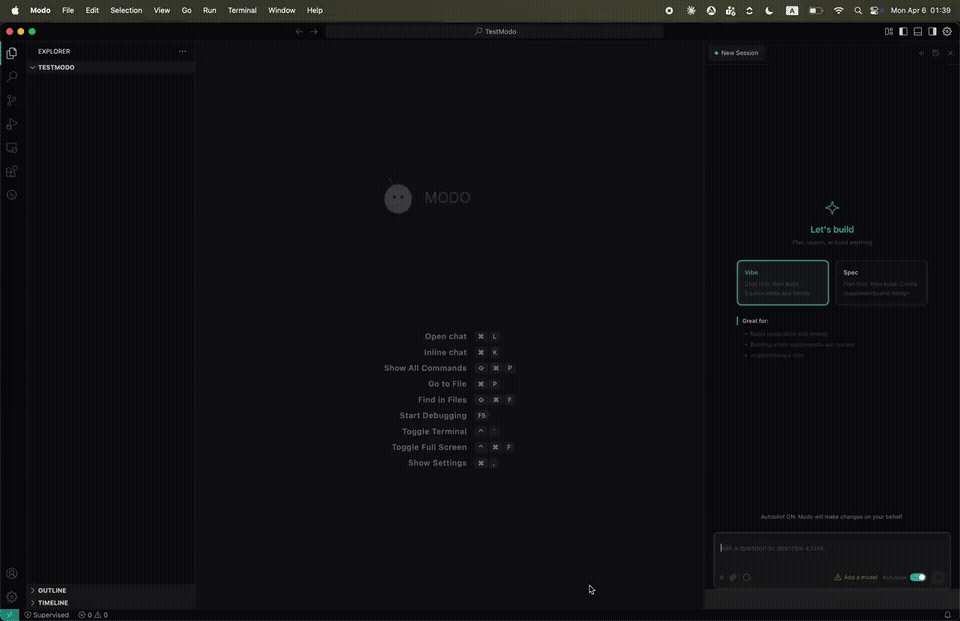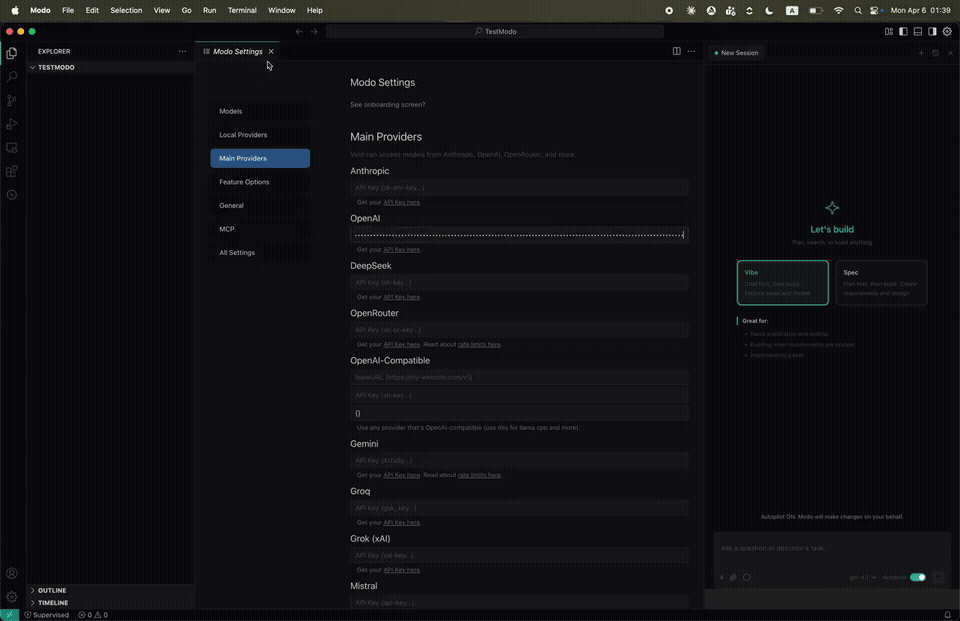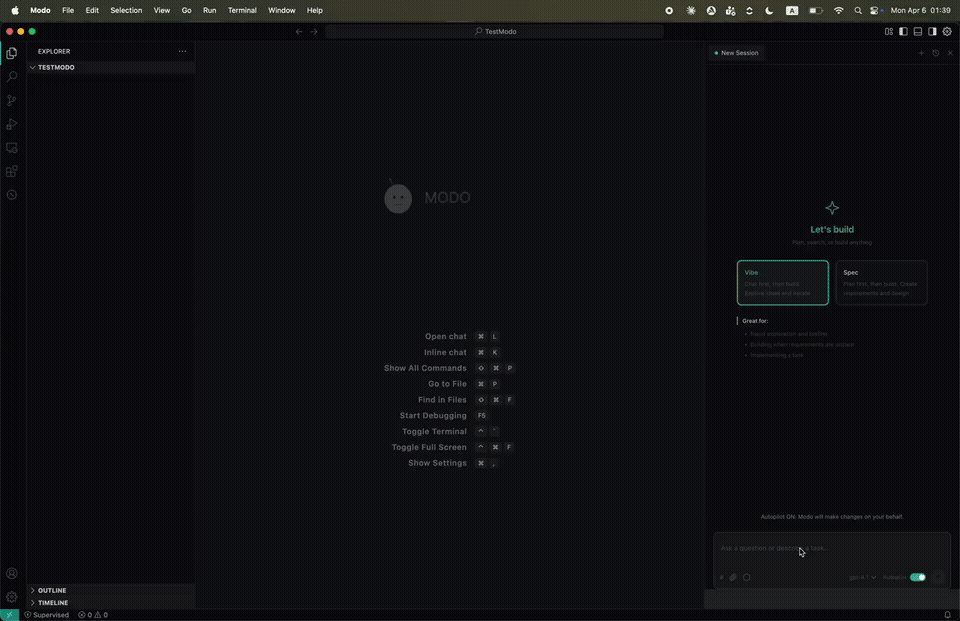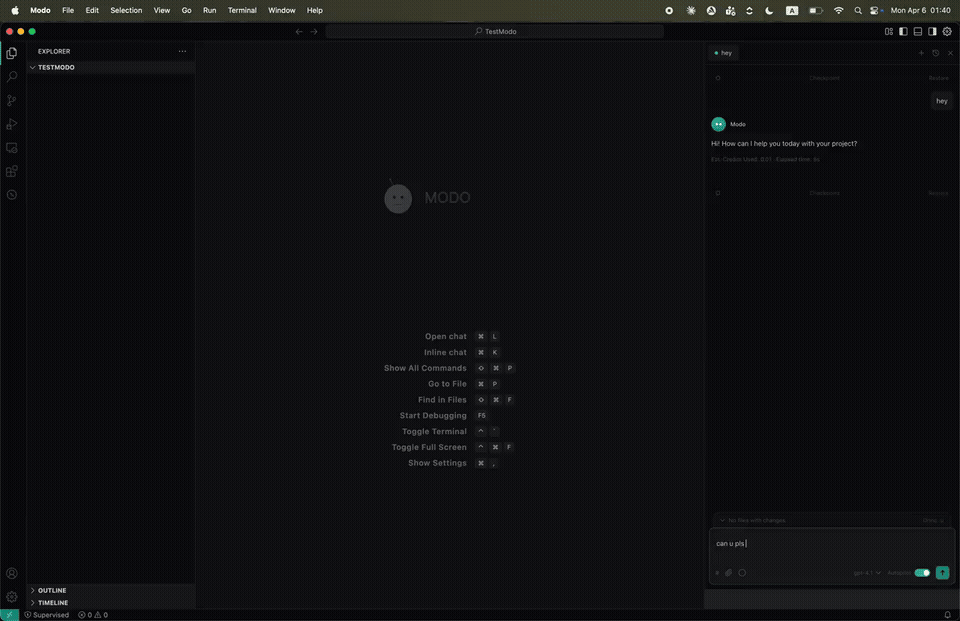 mohshomis/modo
Curated collection of cybersecurity learning resources, CTF writeups, research papers, and practical labs for hands-on skill development across web…
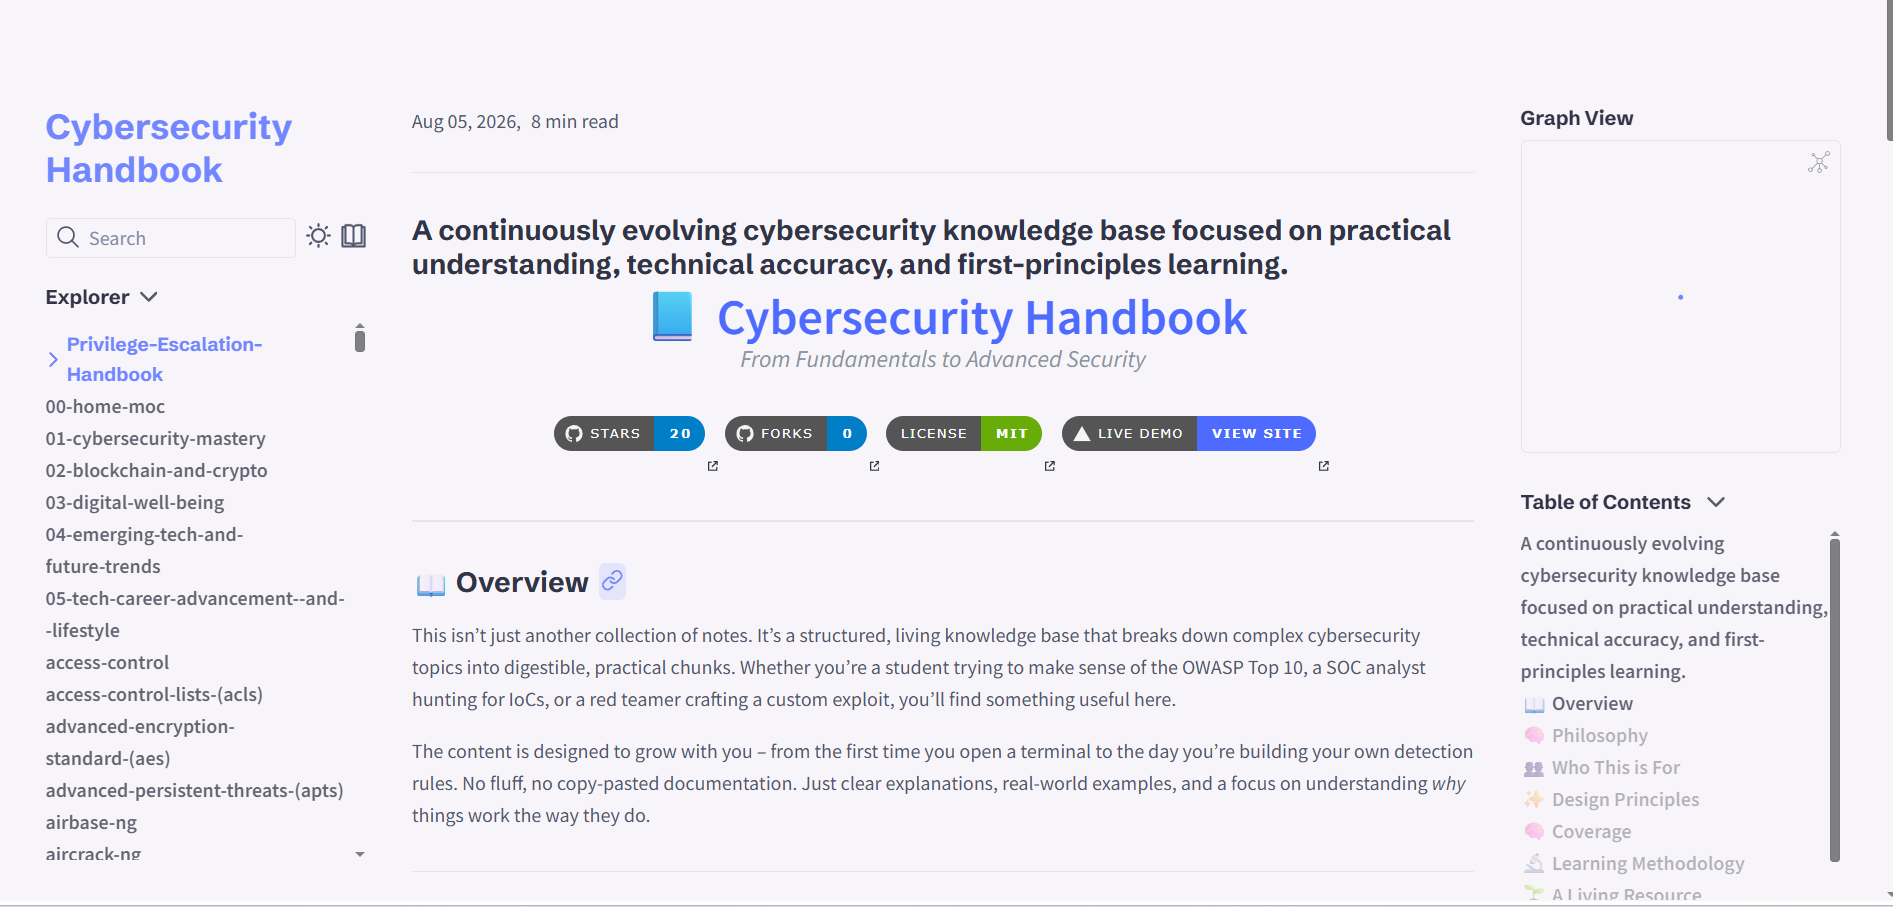 priyanshu-rawa/cybersecurity-handbook
Open-source cybersecurity knowledge base with 400+ notes, labs, and cheat sheets covering offense, defense, cryptography, cloud, and forensics.
 mister-iks/pcybox-attackgraph
Open source browser lab to build a simulated infrastructure, watch an attack move through it, and check whether your defense works.
 selinuxproject/selinux-notebook
Comprehensive open-source book on SELinux covering kernel components, userspace libraries, policy toolchain, and policy language. Includes build…
 ransomleak/training-application-security
Interactive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…
 owasp/wstg
The Web Security Testing Guide is a comprehensive Open Source guide to testing the security of web applications and web services.
 securitytemplates/sectemplates
Open source templates you can use to bootstrap your security programs
 rshipp/awesome-malware-analysis
Defund the Police.
 brodsbytes/cyberpup
A free, open-source cybersecurity app for non techy people.
 hacker0x01/hacker101
Source code for Hacker101.com - a free online web and mobile security class.
 r-s0n/ars0n-framework
Modular bug bounty hunting framework automating reconnaissance, subdomain enumeration, and vulnerability scanning with an educational focus to help…
 reddelexc/hackerone-reports
Curated collection of top HackerOne bug bounty reports organized by vulnerability type and program, with scripts to fetch, deduplicate, and rank…
 lirantal/awesome-nodejs-security
Curated directory of Node.js security tools, static analyzers, vulnerability scanners, and educational resources covering OWASP Top 10, supply chain…
 iknowjason/awesome-cloudsec-labs
Awesome free cloud native security learning labs. Includes CTF, self-hosted workshops, guided vulnerability labs, and research labs.