
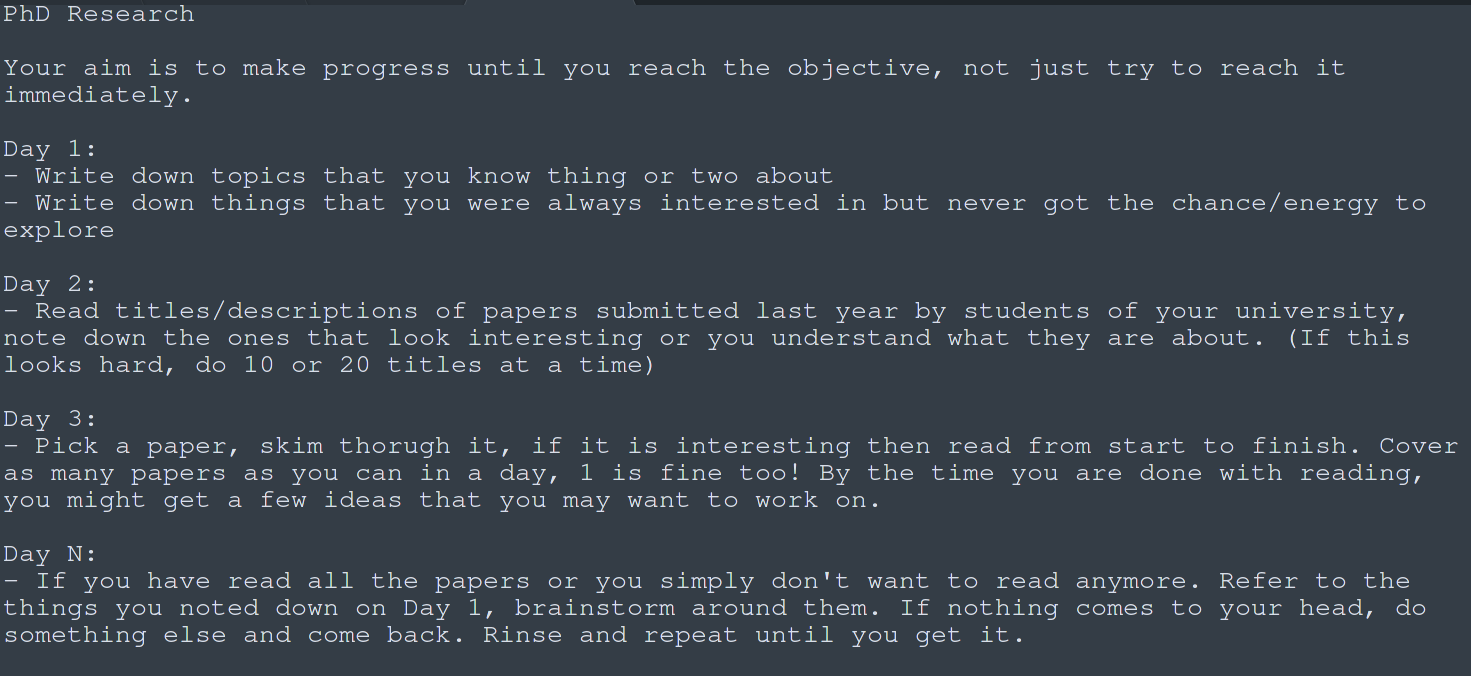
be-a-hacker
 s0md3v/be-a-hacker
roadmap for a self-taught hacker
curated-resourceseducationlearning-paths-courses+6
s0md3v/be-a-hackerroadmap for a self-taught hacker
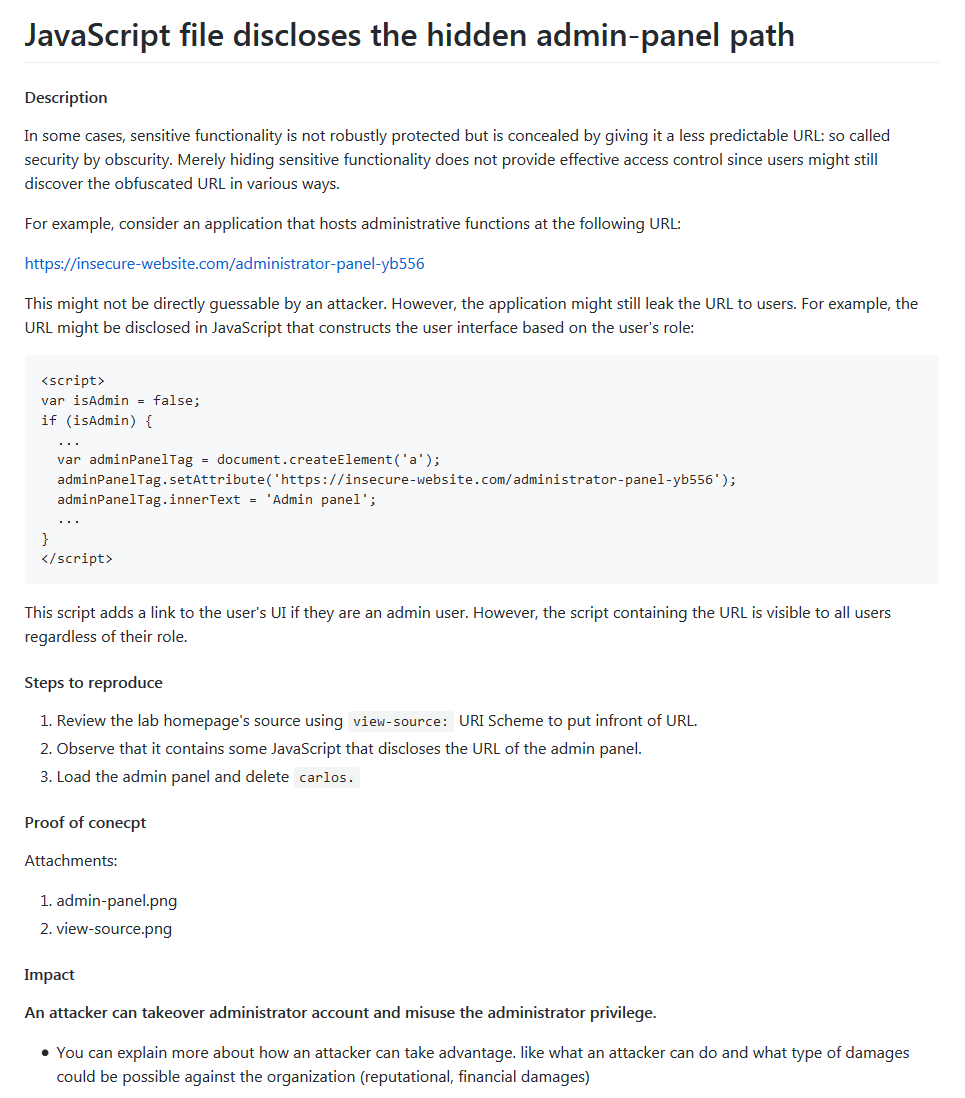 bittentech/bug-bounty-beginner-roadmap
This is a resource factory for anyone looking forward to starting bug hunting and would require guidance as a beginner.
 cyb3rmik3/kql-threat-hunting-queries
A repository of KQL queries focused on threat hunting and threat detecting for Microsoft Sentinel & Microsoft XDR (Former Microsoft 365 Defender).
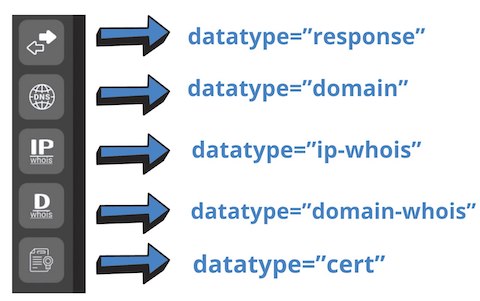 netlas-io/netlas-cookbook
The goal of this guide is very simple - to teach anyone interested in cyber security, regardless of their knowledge level, how to make the most of…
 webbreacher/obsidian-osint-templates
These templates are suggestions of how the Obsidian notetaking tool can be used during an OSINT investigation. The example data in those files should…
 bc-security/beginners-guide-to-obfuscation
Hands-on red-team obfuscation workshop teaching AMSI bypass, ETW evasion, and payload obfuscation with PowerShell, Visual Basic, and C# to evade…
 nickvourd/windows-local-privilege-escalation-cookbook
Windows Local Privilege Escalation Cookbook
 zealraj/cybersecurity-books
Here you will get awesome collection of mostly all well-known and usefull cybersecurity books from beginner level to expert for all cybersecurity…
 ralireza/android-security-teryaagh
Android security guides, roadmap, docs, courses, write-ups, and teryaagh.
 harsh-bothra/securityexplained
SecurityExplained is a new series after the previous learning challenge series #Learn365. The aim of #SecurityExplained series is to create…
 nebulock-inc/agentic-threat-hunting-framework
ATHF is a framework for agentic threat hunting - building systems that can remember, learn, and act with increasing autonomy.
 r-s0n/ars0n-framework
Modular bug bounty hunting framework automating reconnaissance, subdomain enumeration, and vulnerability scanning with an educational focus to help…
 dievus/powershellforpentesters
Course repository for PowerShell for Pentesters Course
 pinksawtooth/how_to_become_a_malware_analyst
Curated guide to becoming a malware analyst, covering essential knowledge, reverse engineering, analysis tools, and LLM-assisted learning with…
 cyber-courses/cyber-library
Community-maintained Markdown knowledge base covering cybersecurity foundations, offensive and defensive practice, governance, threat intelligence,…
 redteamguides/redteamguides.github.io
Red Team Guides
 mister-iks/pcybox-attackgraph
Open source browser lab to build a simulated infrastructure, watch an attack move through it, and check whether your defense works.
 jigerjain/interview_tips
Summary of Cyber Security interview questions I have been through, hope this helps