
static_asm
 mahmoudimus/static_asm
Header-only C++2x compile-time assembler for x86/x86-64 instruction encoding
binary-analysiscode-analysiseducation+6
3118h 48m ago
mahmoudimus/static_asmHeader-only C++2x compile-time assembler for x86/x86-64 instruction encoding
 owasp/cheatsheetseries
The OWASP Cheat Sheet Series was created to provide a concise collection of high value information on specific application security topics.
 anpa1200/aidebug
Evidence-focused malware reverse engineering with deep PE/.NET inspection, Ghidra reconstruction, AI cross-checks, YARA, and ELF debugging
 gmh5225/awesome-llvm-security
Curated collection of LLVM security resources covering binary lifting, code obfuscation, static analysis, symbolic execution, sanitizers, and…
 owasp/mastg
Comprehensive OWASP guide for mobile app security testing, reverse engineering, and verifying MASVS/MASWE weaknesses through static, dynamic, and…
 owasp/fiasse
A Framework for Integrating Application Security into Software Engineering (FIASSE) using the Securable Software Engineering Model (SSEM)
 owasp/ocsd
OWASP Certified Secure-Software Developer
 sylwia-budzynska/codeql-workshop
Take first steps in CodeQL for Python by writing a query to find CVE-2024-32022

 owasp/owasp-scs
OWASP Smart Contract Security (SCS) Project
 lirantal/awesome-nodejs-security
Curated directory of Node.js security tools, static analyzers, vulnerability scanners, and educational resources covering OWASP Top 10, supply chain…
 trailofbits/testing-handbook
Trail of Bits Testing Handbook - appsec.guide
 roninforge/roninforge-hono
Cursor plugin for Hono v4 (TypeScript edge web framework). 59 LLM regressions with BAD/CORRECT pairs. Pinned to hono ^4.12.19 (>= 4.9.7 for…
 roninforge/roninforge-angularjs-migration
AngularJS 1.x -> Angular 18 migration guidance for GitHub Copilot. Source-of-truth repo for…
 viralmaniar/vulnvault
Developer-focused knowledge base of application security vulnerabilities with insecure vs secure code examples, prevention guidance, and OWASP/CWE…
 owasp/secure-coding-practices-quick-reference-guide
The Secure Coding Practices Quick-reference Guide from OWASP
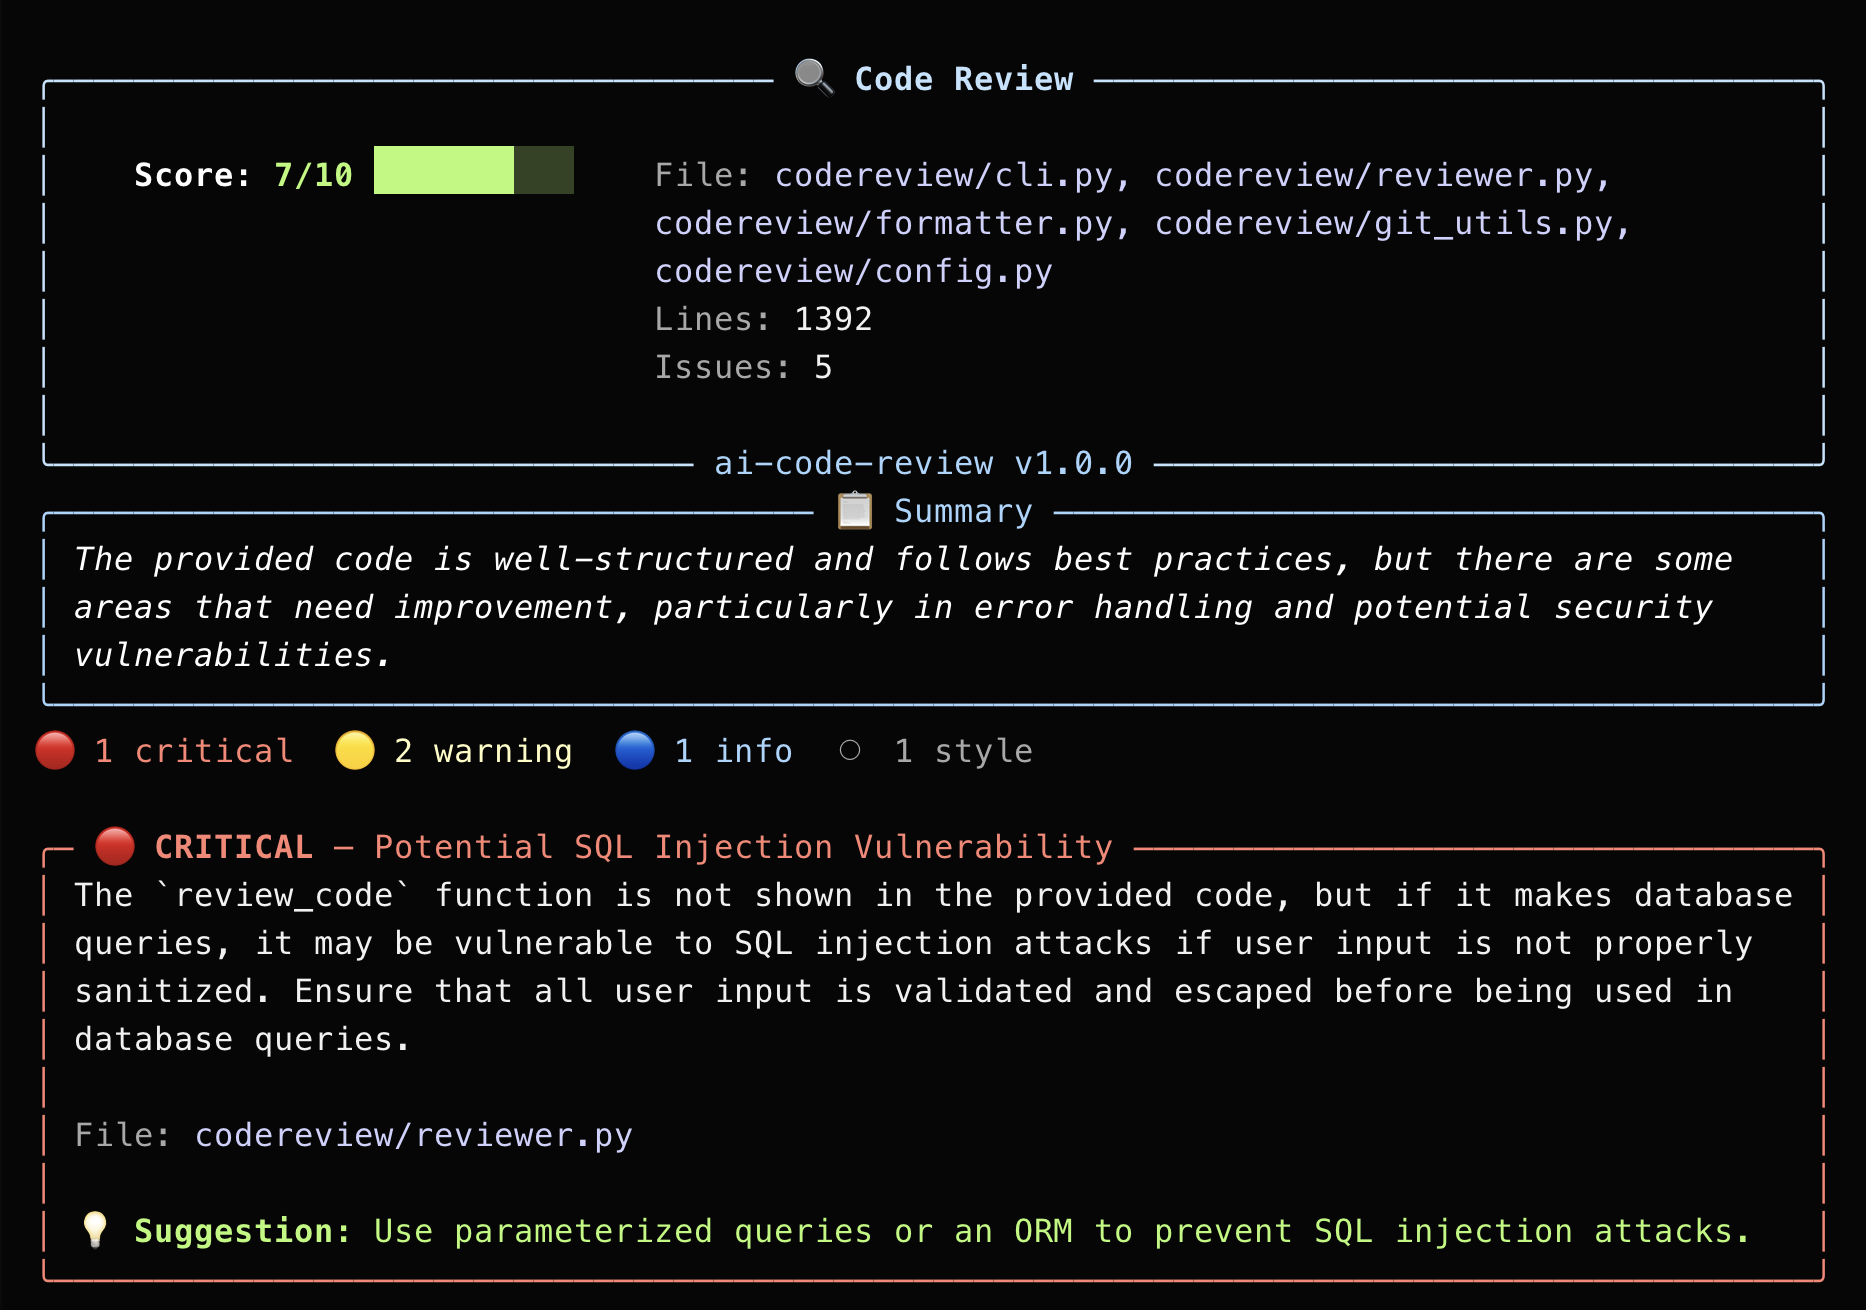 jaydendancer12/ai-code-review
AI-powered CLI tool that reviews code for security vulnerabilities, bugs, and anti-patterns using LLMs. Supports local and cloud providers, git…
 peterhackz/zyrox
Zyrox: LLVM based, compile-time obfuscator plugin.