Information-Security-Tasks

Curated infosec knowledge base of practitioner notes, methodologies, and daily-updated CVE, news, and tool digests organized by offensive, defensive,…

Curated infosec knowledge base of practitioner notes, methodologies, and daily-updated CVE, news, and tool digests organized by offensive, defensive,…

List of CyberSecurity Resources and some different Sub-Domains of CyberSecurity

Hello, aspiring hackers! 🕵️♂️ Here’s a list of 500+ Free TryHackMe rooms to kickstart your cybersecurity journey. These rooms are absolutely free,…

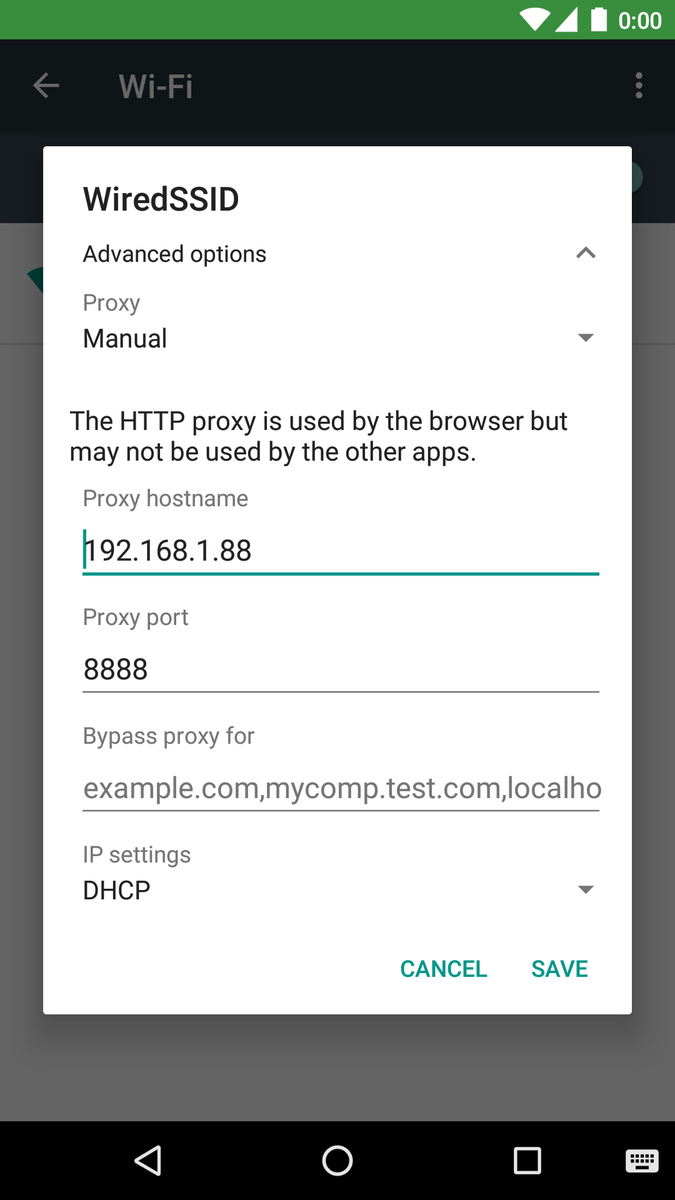
Step-by-step guide to intercepting Android and iOS HTTP/HTTPS traffic with Charles Proxy, covering SSL proxying, CA certificate installation, and…

Jekyll-based pentesting knowledge base with methodology guides, cheatsheets, tool indexes, certification roadmaps, and curated practice lab and CTF…

A deep look at some recon methodologies and web-application vulnerabilities of my interest where I will merge all my notes gathered from books,…

eLearnSecurity Junior Penetration Tester (eJPT) v2 Notes

Community-maintained Markdown knowledge base covering cybersecurity foundations, offensive and defensive practice, governance, threat intelligence,…

Open source browser lab to build a simulated infrastructure, watch an attack move through it, and check whether your defense works.

Atomic web vulnerability labs. One OWASP flaw per app — minimal Flask + Docker, intentionally broken for hands-on study with Burp Suite.

Curated guide to becoming a malware analyst, covering essential knowledge, reverse engineering, analysis tools, and LLM-assisted learning with…

Curated list of threat detection and hunting resources: detection rules, SIEM and log analysis tools, endpoint/network monitoring, datasets,…

:computer:🛡️ A curated collection of awesome resources, tools, and other shiny things for cybersecurity blue teams.

Curated directory of threat intelligence sources, feeds, frameworks, tools, and research for SOC/CTI teams—covering IOCs, STIX/TAXII formats, and…

Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…

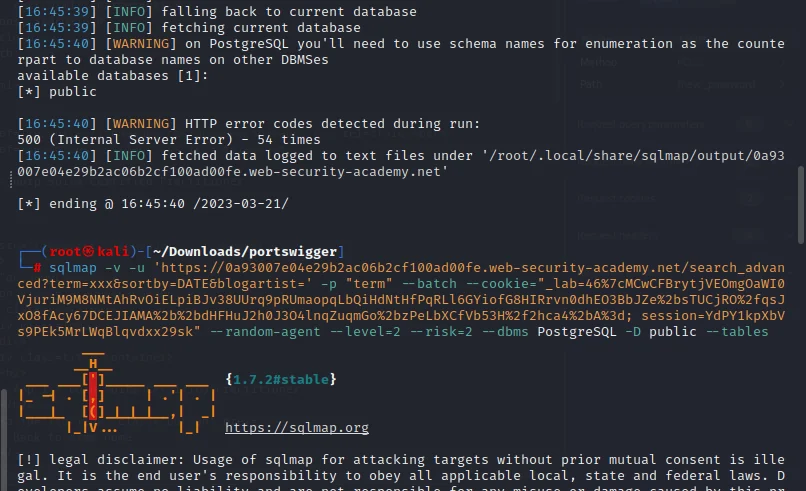
Practical study notes and walkthroughs for PortSwigger Academy labs, covering web vulnerabilities, payloads, enumeration, and BSCP exam strategies.

Curated bug-bounty methodology library with runbooks, recon/fuzz playbooks, checklists, and CLI helpers for target scoping, cert enumeration, and…

CTF writeups and teaching scripts for web security, bug bounty techniques, and network forensics, with blank-value versions for active practice.