metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…

📦 Make security testing of K8s, Docker, and Containerd easier.

Advanced MSSQL penetration testing tool for lateral movement, command execution, NTLM relay, and brute-force attacks via linked servers and multiple…

Practical MSSQL penetration testing cheat sheet covering enumeration, linked-server pivoting, privilege escalation, persistence, and command…

Module-based AWS exploitation framework for red team testing and blue team analysis. Emulates attack patterns in the AWS control plane with unique UA…

Vendor-neutral cloud security testing guide with structured phases for enumeration, privilege escalation, lateral movement, and post-exploitation…

110 offensive-security one-liners for authorized testing and CTFs, grouped by category and kill-chain step.

R2S is a comprehensive exploitation and post-exploitation framework targeting the Next.js React Server Components vulnerability (CVE-2025-55182). It…

Tools and Techniques for Red Team / Penetration Testing

Nishang - Offensive PowerShell for red team, penetration testing and offensive security.

My Notes about Penetration Testing

Windows-native penetration testing swiss army knife for lateral movement, credential access, data exfiltration, and vulnerability scanning across…

Fast, zero-dependency credential testing tool in Go. Brute force SSH, MySQL, PostgreSQL, Redis, MongoDB, SMB, and 20+ protocols. Hydra alternative…

HTTP/HTTPS interception proxy for testing Windows authentication mechanisms, supporting NTLM, Kerberos, pass-the-hash, pass-the-ticket and relay…

Firecat is a penetration testing tool that allows you to punch reverse TCP tunnels out of a compromised network.

This tool can be used during internal penetration testing to dump Windows credentials from an already-compromised host. It allows one to dump SYSTEM,…

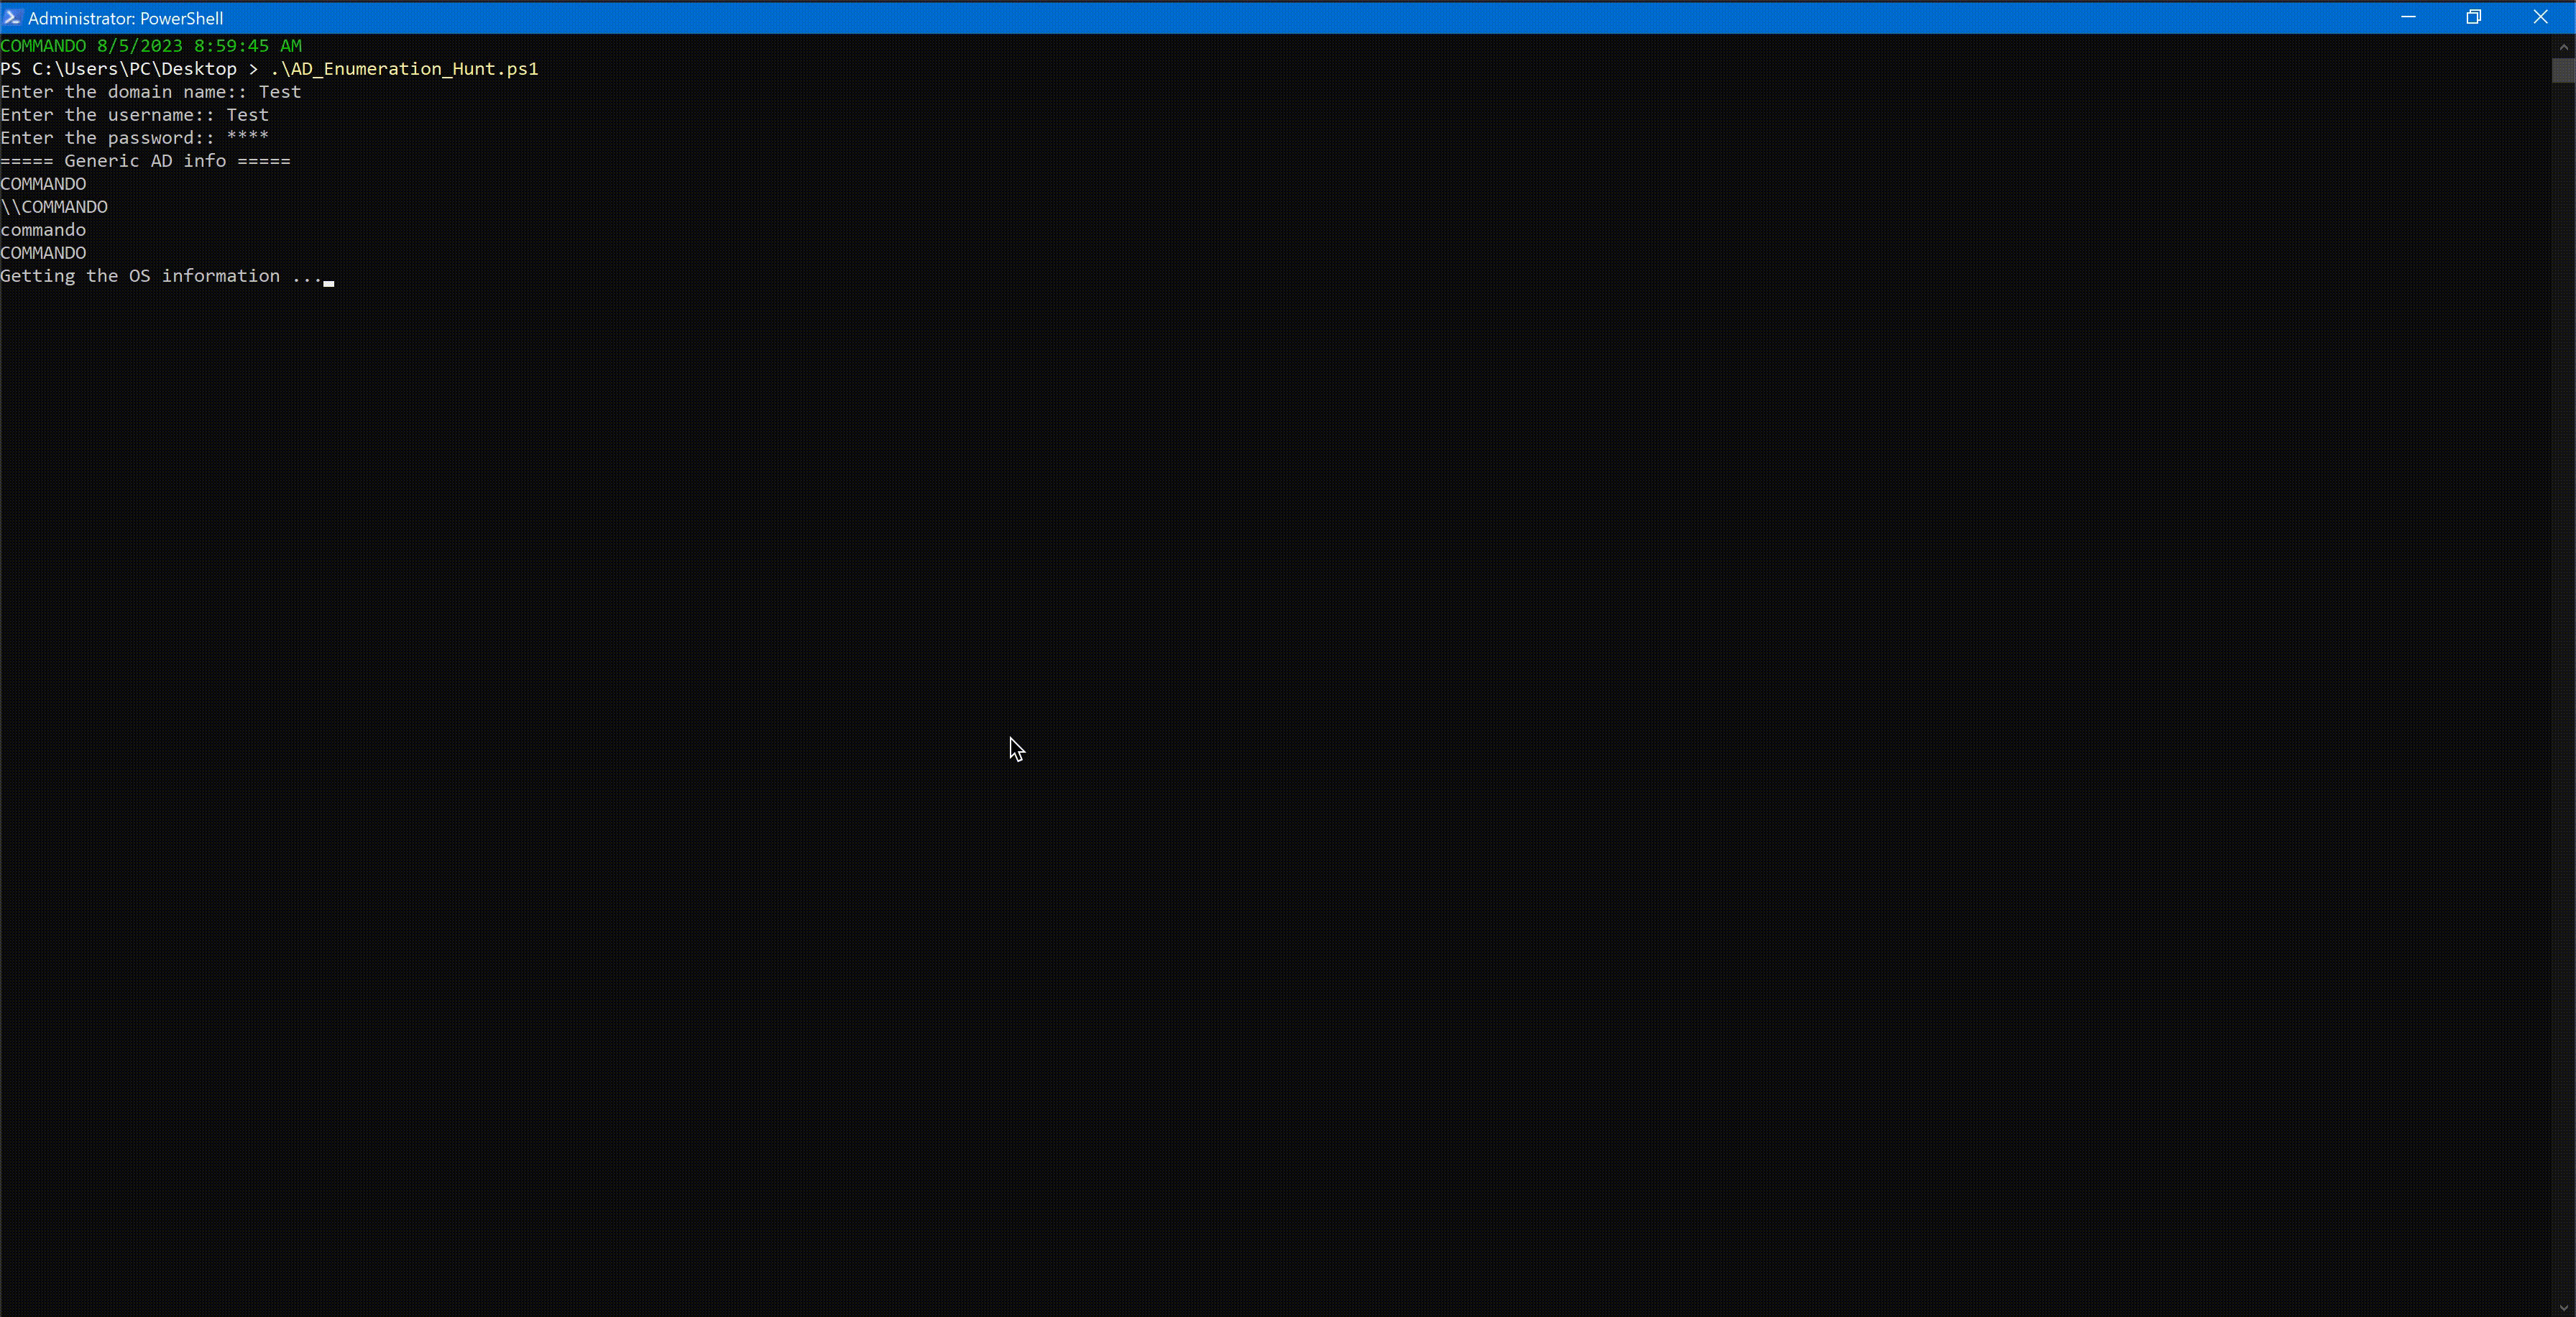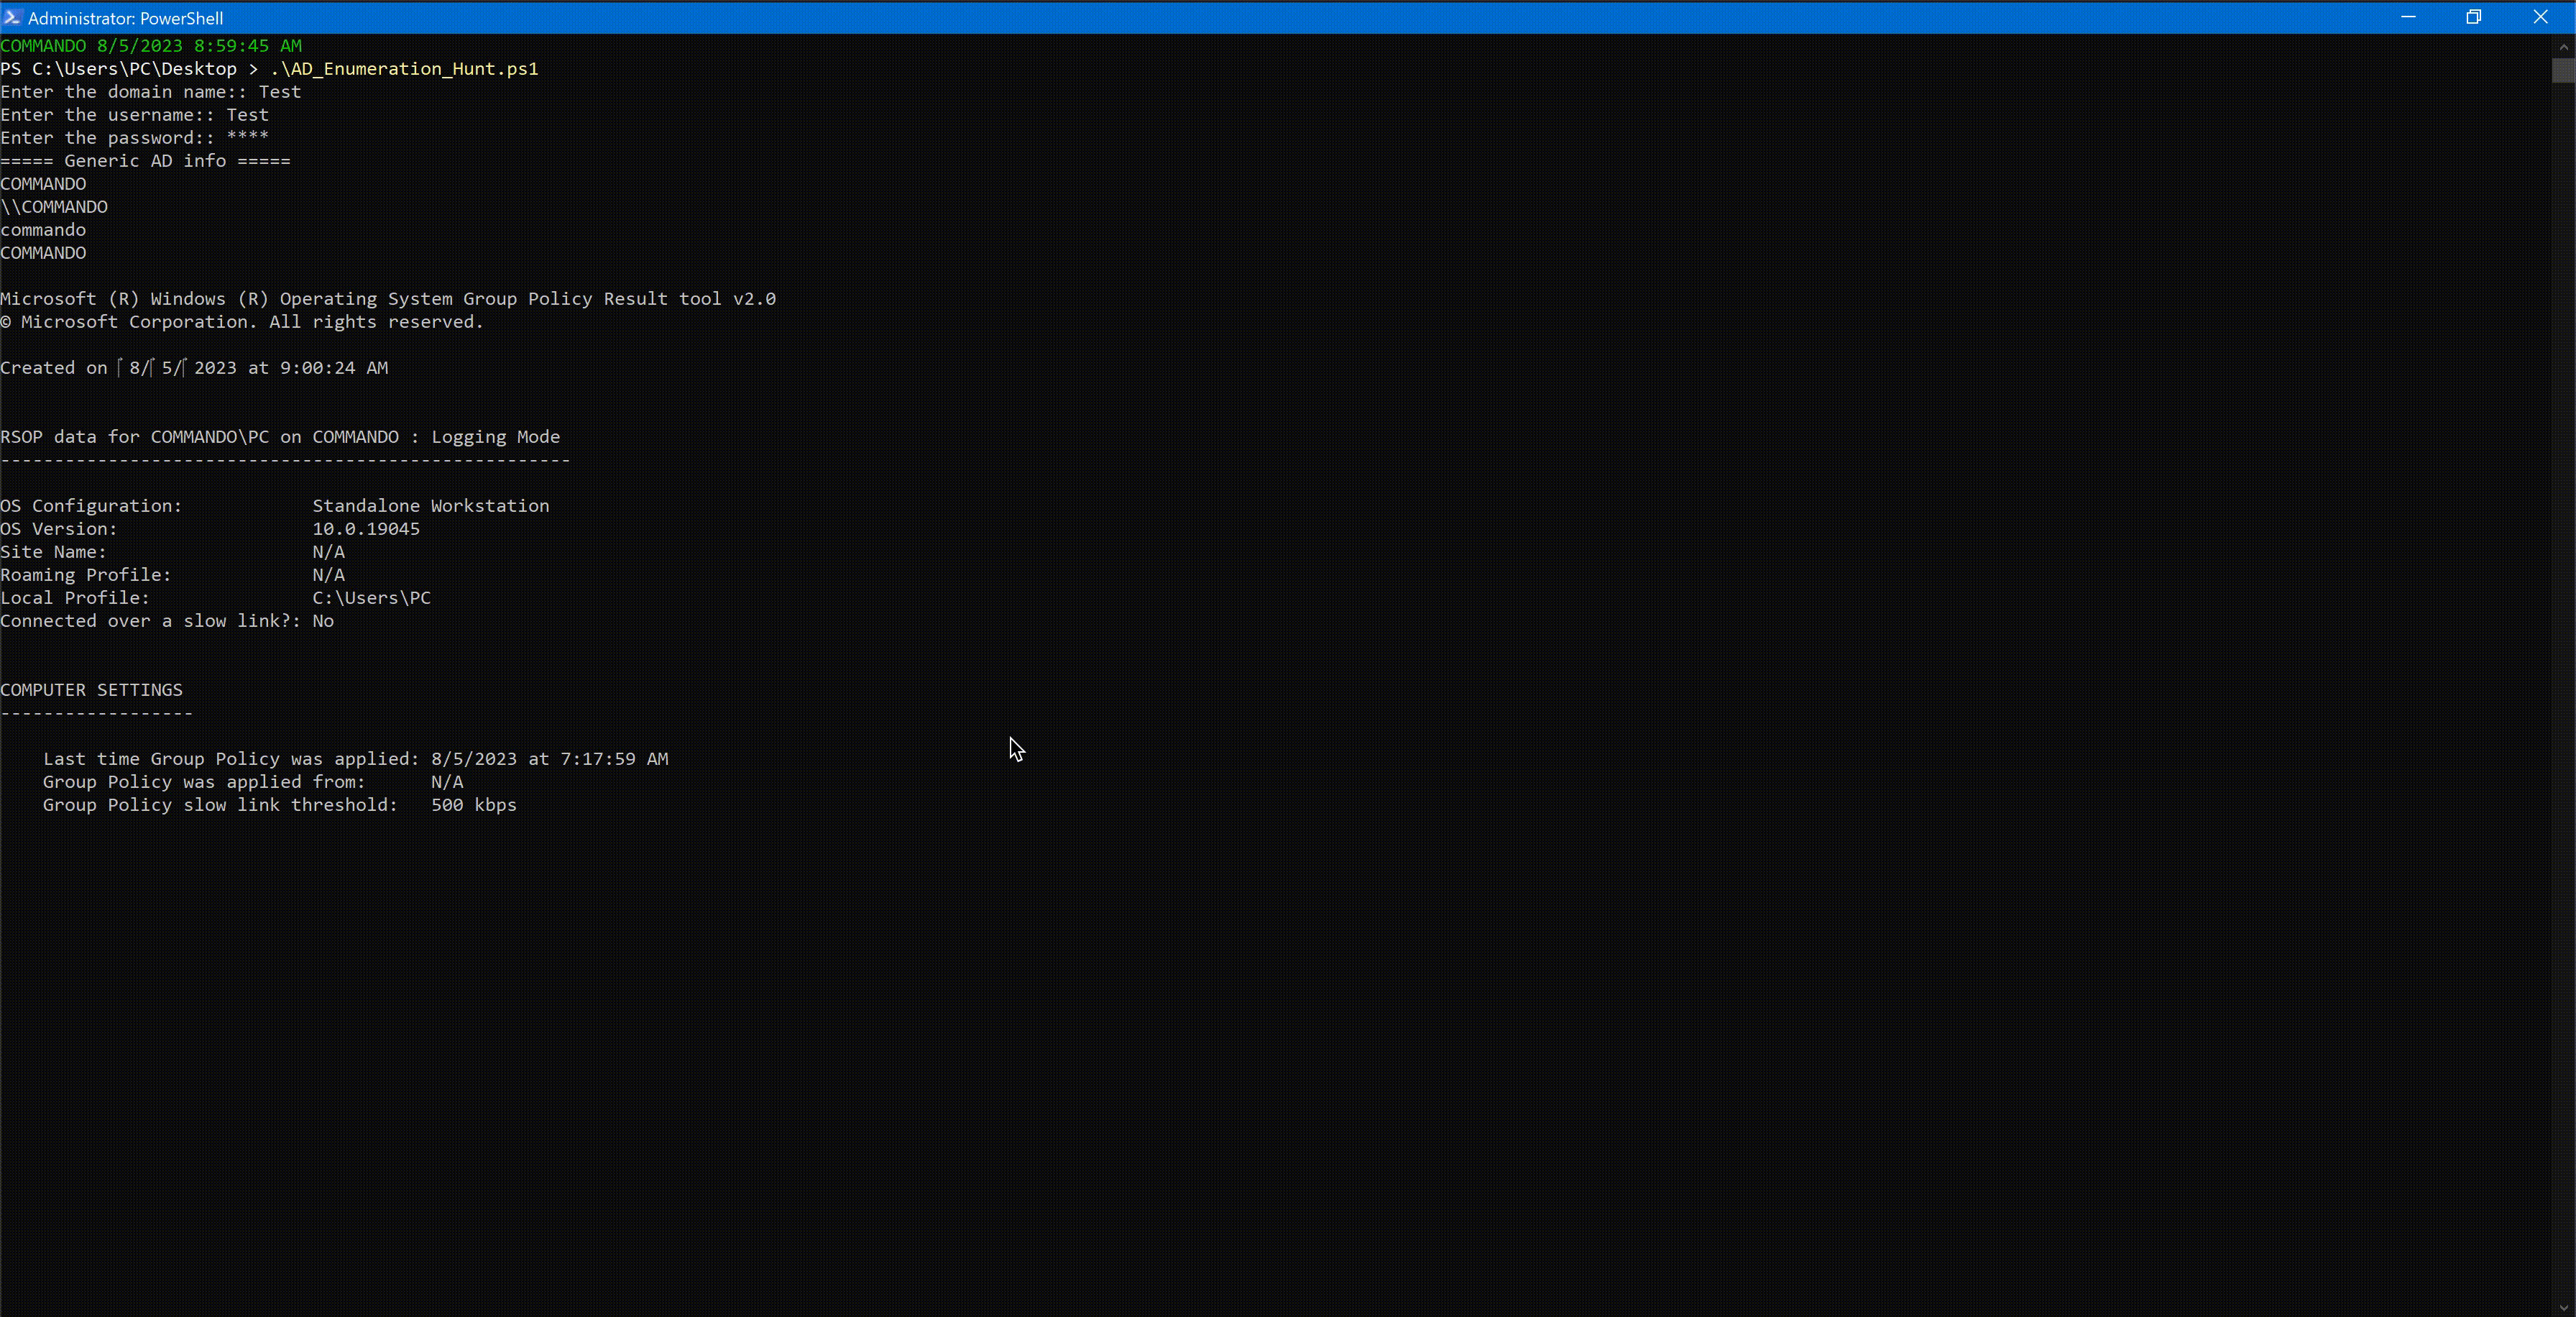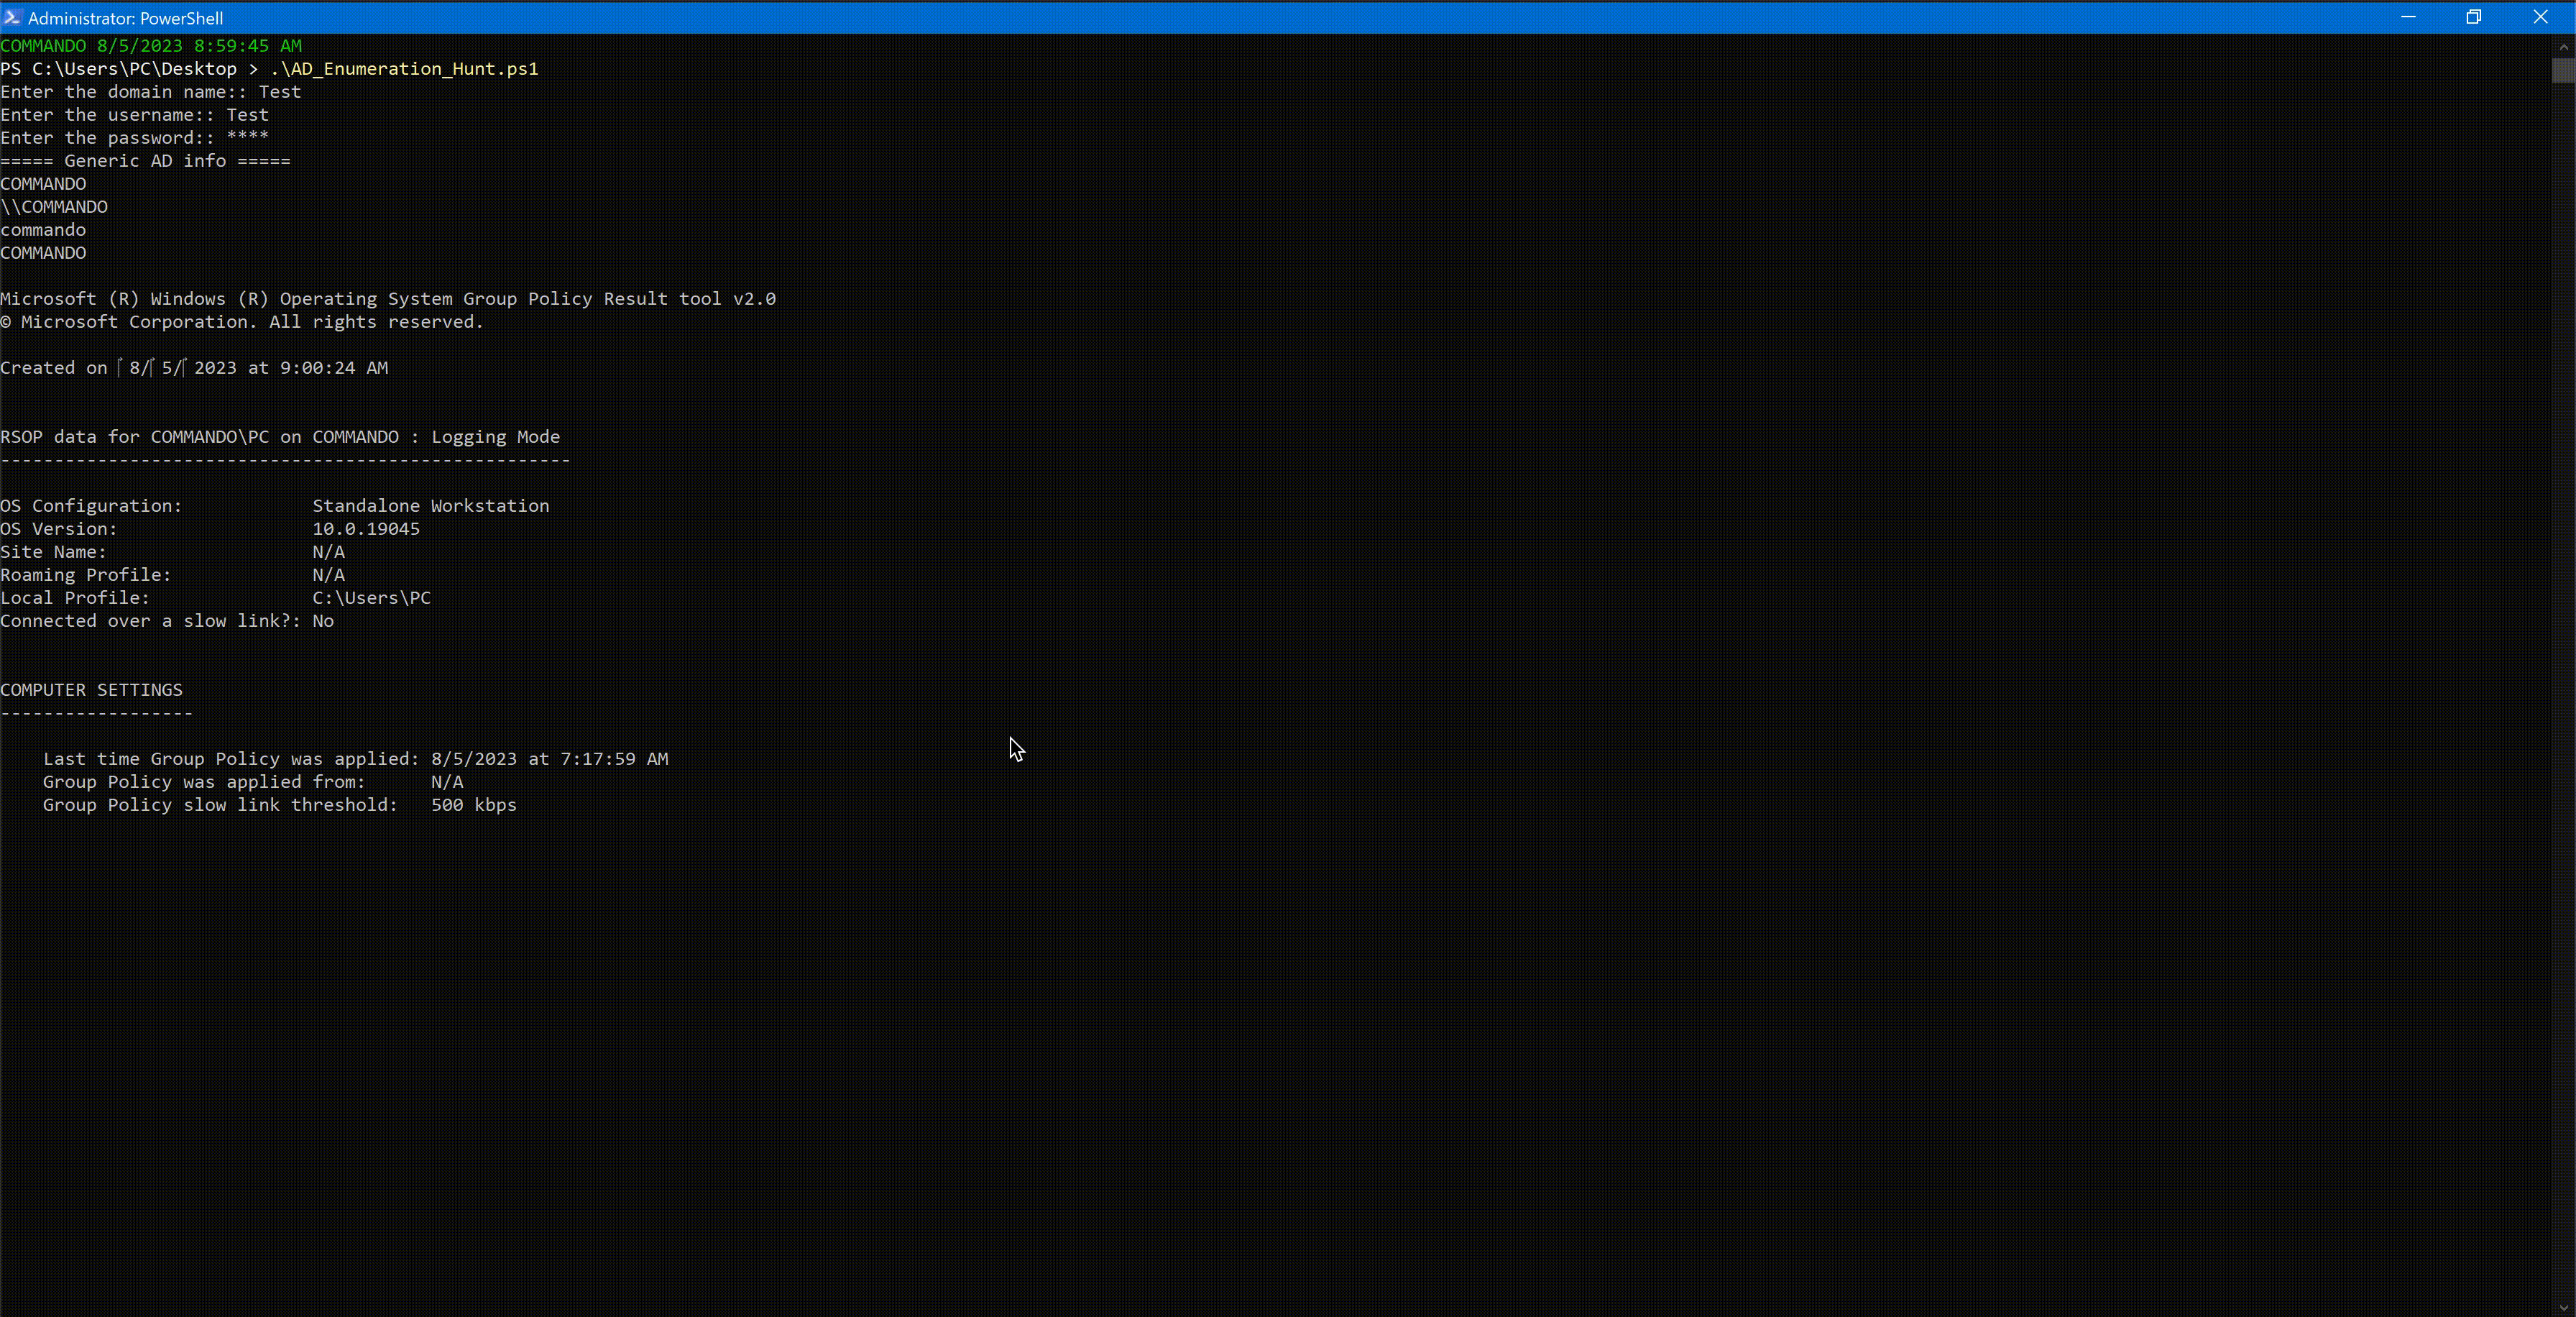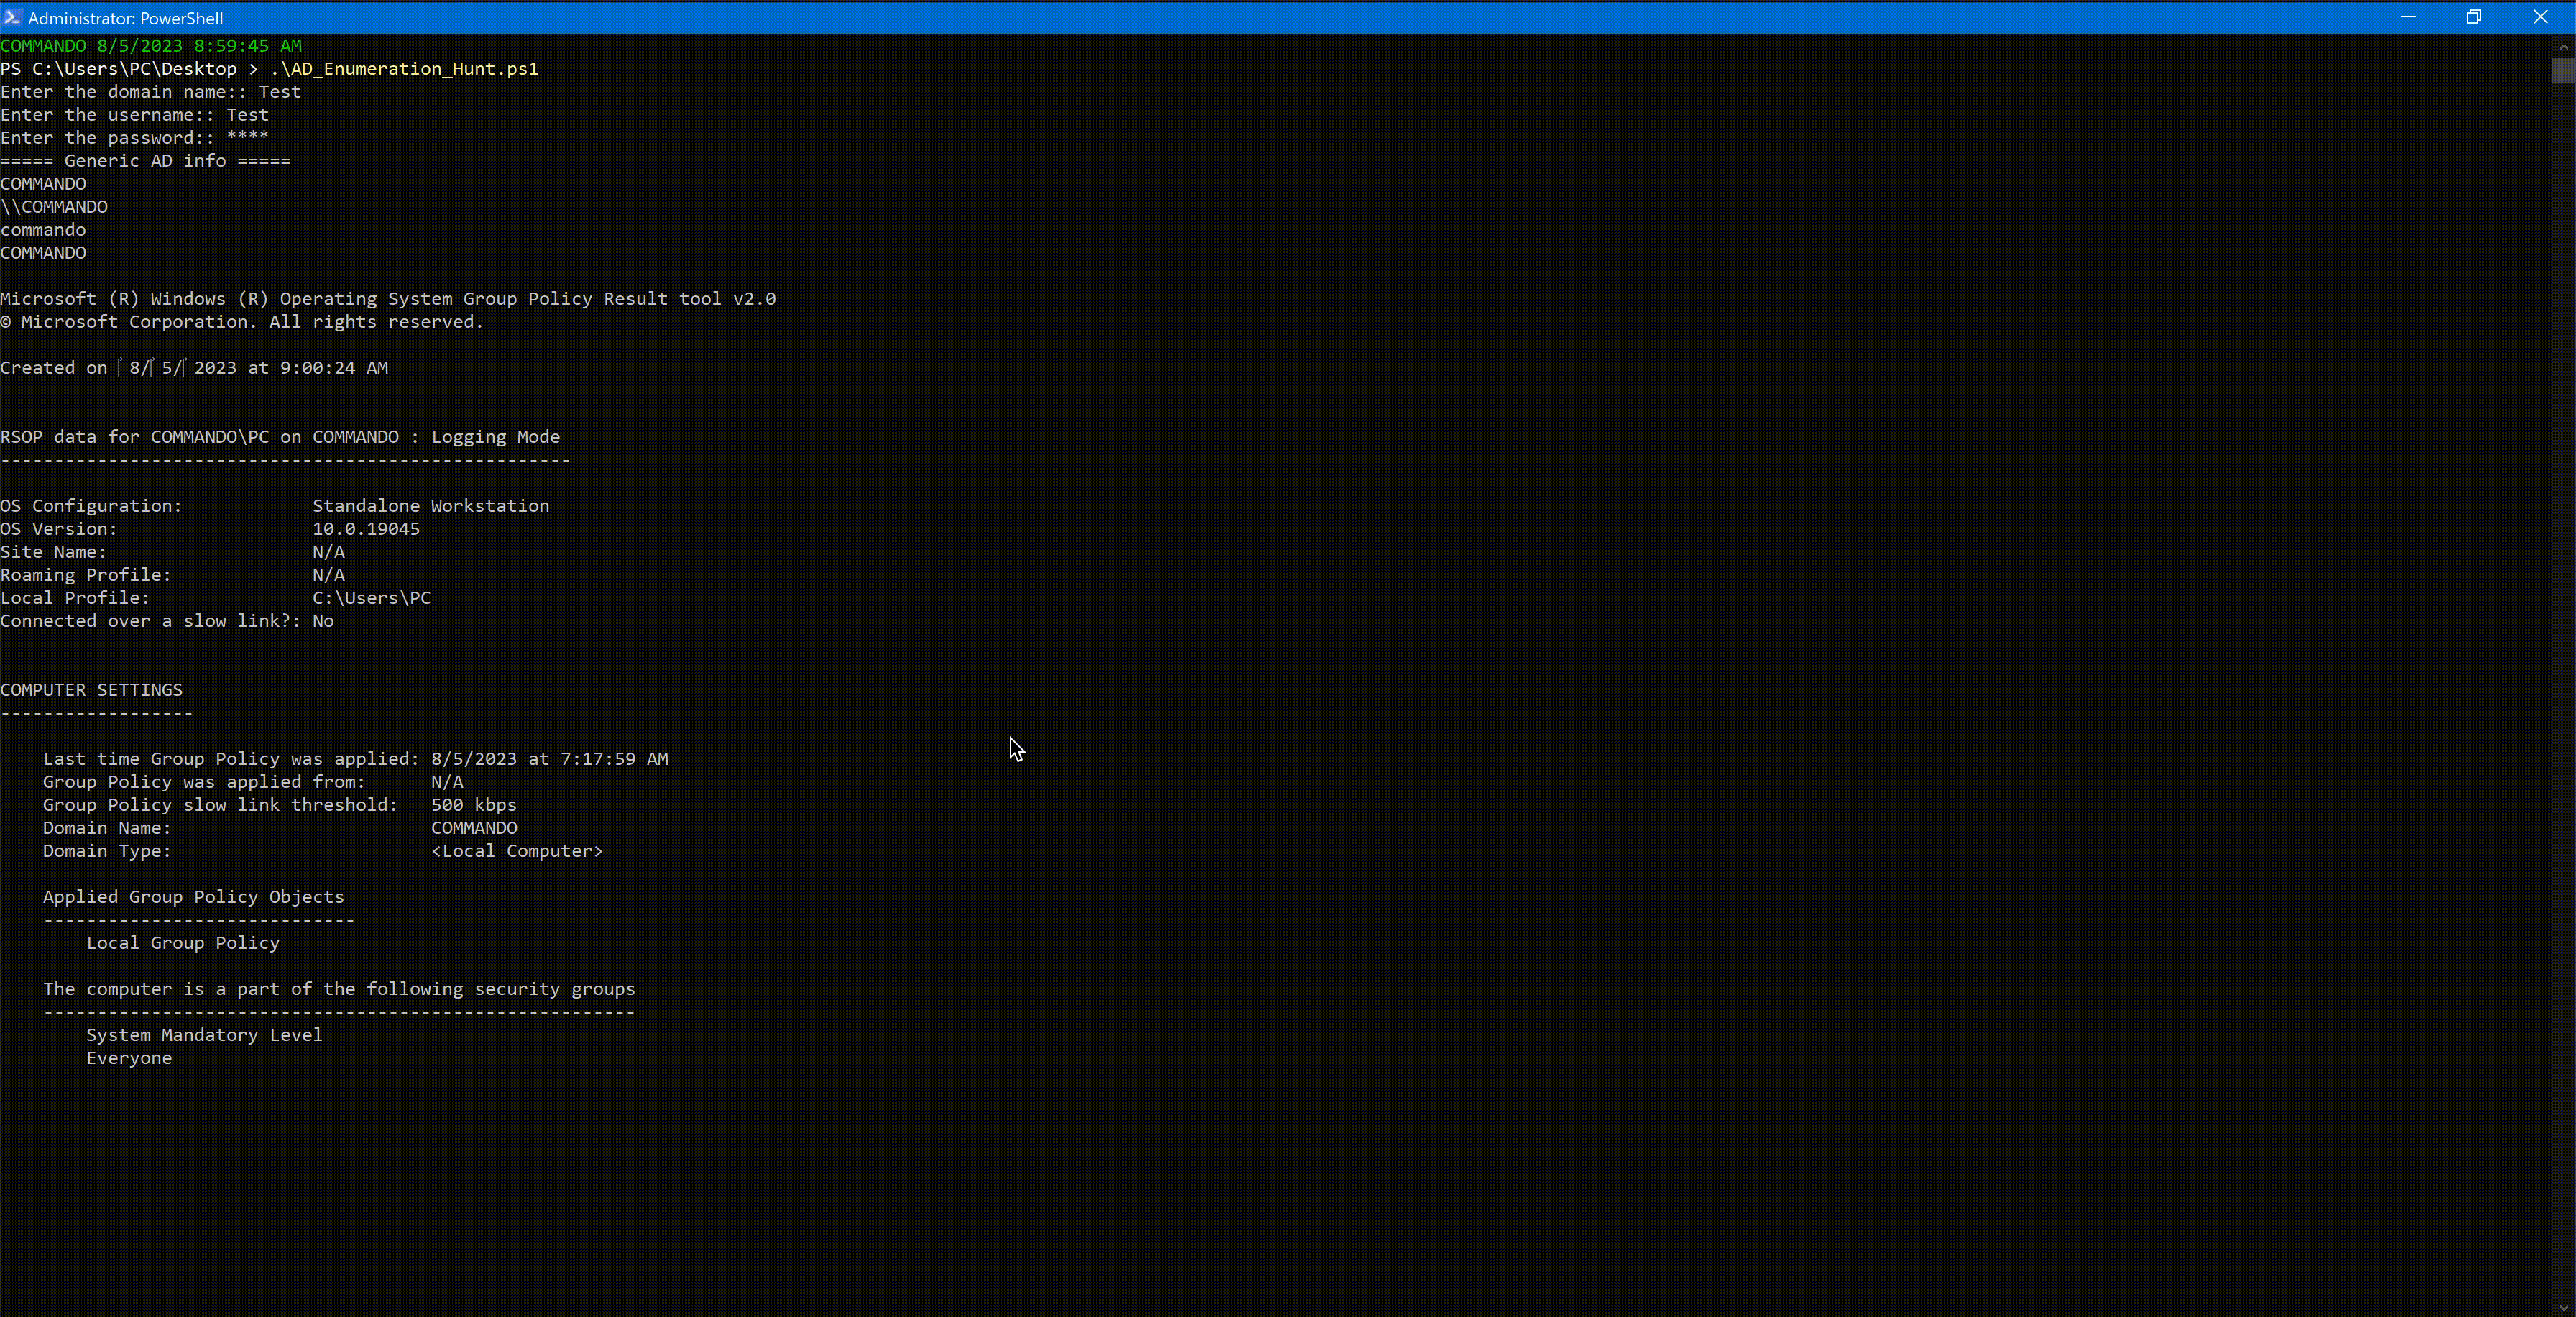
PowerShell toolkit for Active Directory penetration testing, featuring domain/user/group enumeration, trust relationship analysis, RDP configuration,…