
Archived
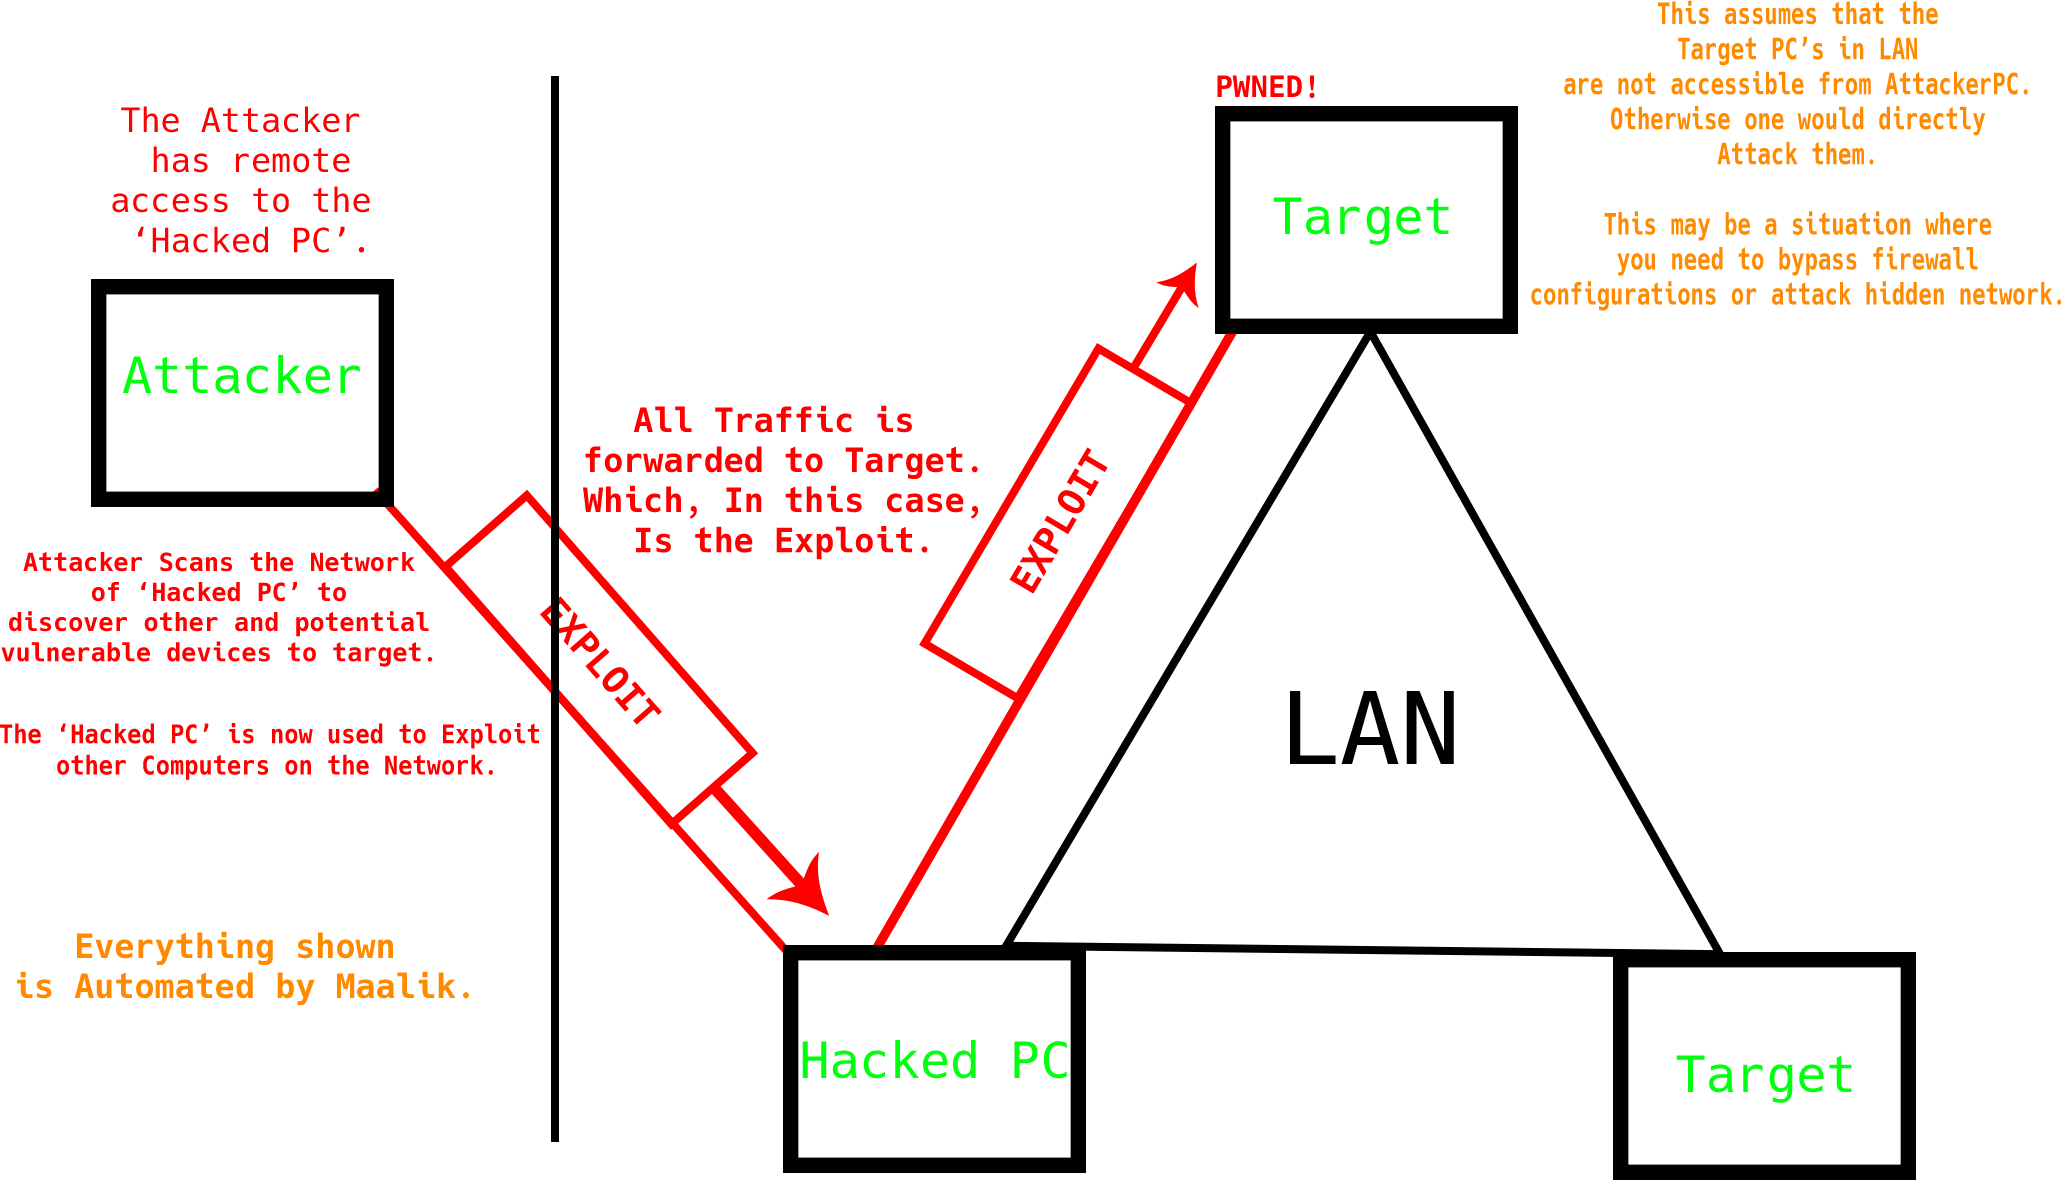
maalik
 quantumcore/maalik
Feature-rich Post Exploitation Framework with Network Pivoting capabilities.
command-and-controlexploitationlateral-movement+6
93
 bittersecurity/decepticon
Autonomous LLM red team agent that plans and executes full attack chains—recon, exploitation, privilege escalation, lateral movement and C2—inside an…
 wh0amitz/sharpadws
Active Directory reconnaissance and exploitation for Red Teams via the Active Directory Web Services (ADWS).
 zeronetworks/rpcfirewall
Windows RPC firewall that audits, detects, and blocks malicious remote procedure calls to prevent lateral movement, reconnaissance, and exploitation…
 synacktiv/ouned
The OUned project automating Active Directory Organizational Units ACL exploitation through gPLink poisoning
 nccgroup/chuckle
An automated SMB relay exploitation script.
 ad0nis/ntlm_relay_gat
Automates NTLM relay exploitation using ntlmrelayx.py for SMB share enumeration, shell execution, secrets dumping, and MSSQL command execution via…
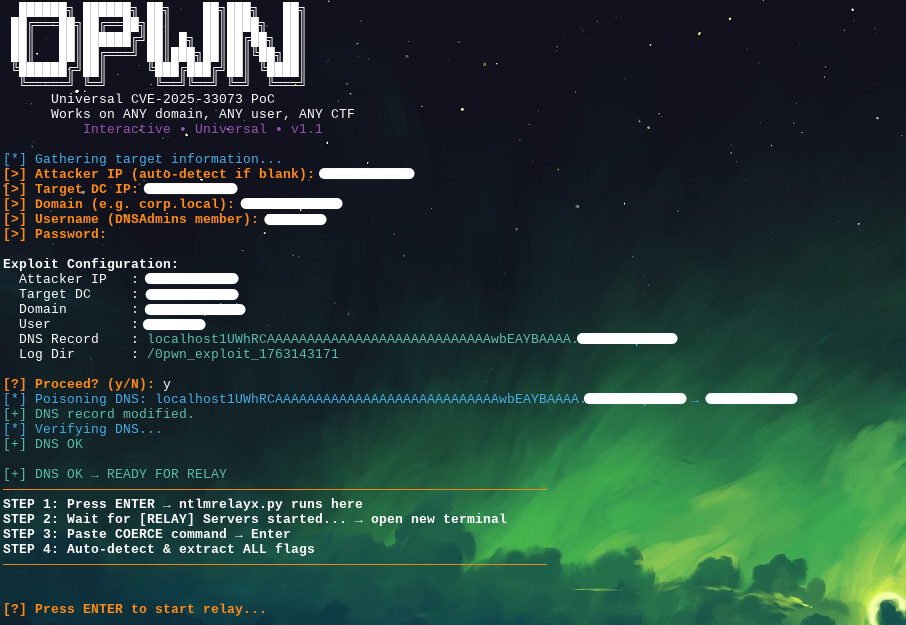 uziii2208/cve-2025-33073
Universal exploitation tool for CVE-2025-33073 targeting Windows Domain Controllers with DNSAdmins privileges and WinRM enabled.
 grines/scour
Module-based AWS exploitation framework for red team testing and blue team analysis. Emulates attack patterns in the AWS control plane with unique UA…
 safebreach-labs/eventlogin-cve-2025-29969
Exploitation of CVE-2025-29969
 tomerpeled92/cve
Curated repository of CVEs with PoCs, articles, and detailed descriptions for vulnerability research and exploitation.
 cyb3rmaddy/cve-2023-23397-report
An exploitation demo of Outlook Elevation of Privilege Vulnerability
 cobbr/sharpsploit
SharpSploit is a .NET post-exploitation library written in C#
 cube0x0/krbrelay
Kerberos relay framework for Windows environments enabling authentication relay, privilege escalation, and lateral movement via LDAP, SMB, HTTP, and…
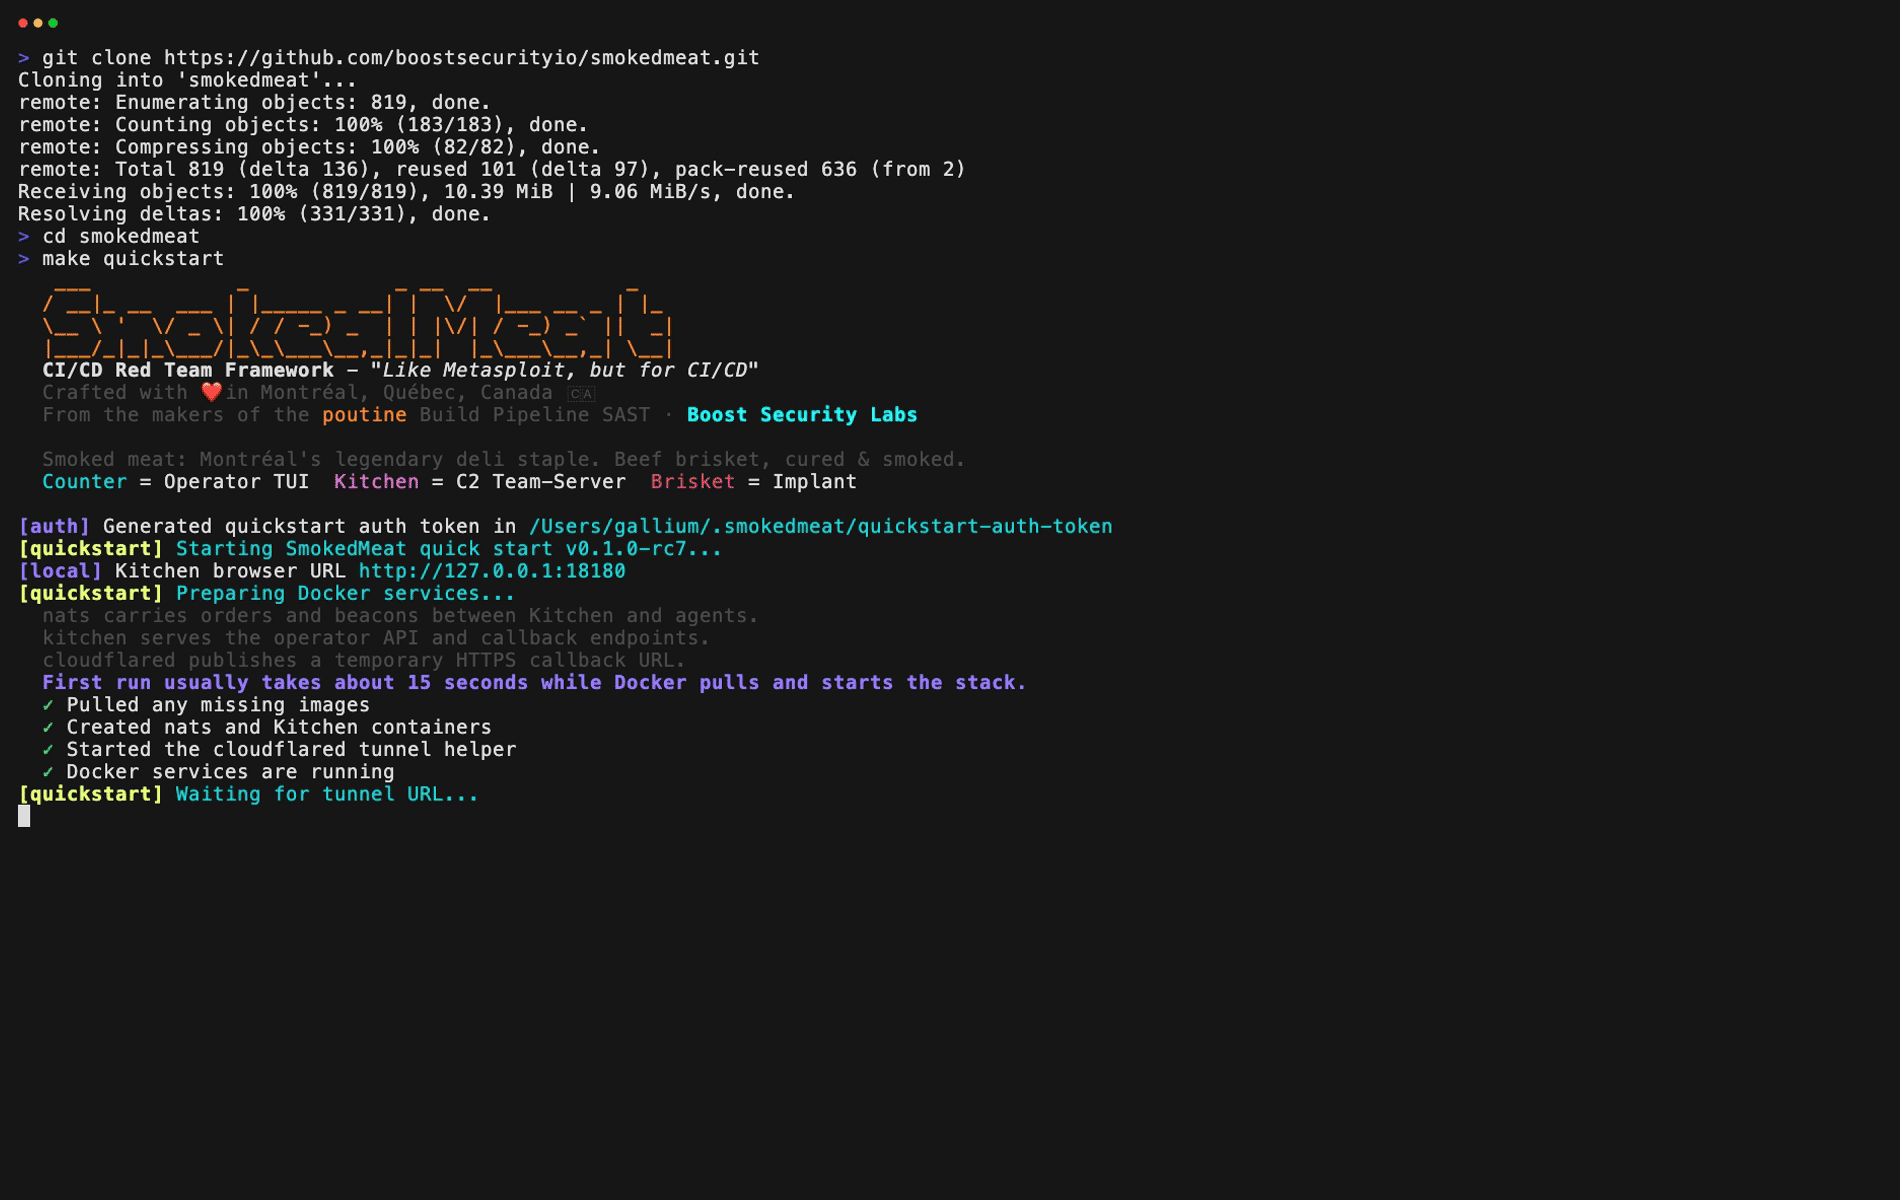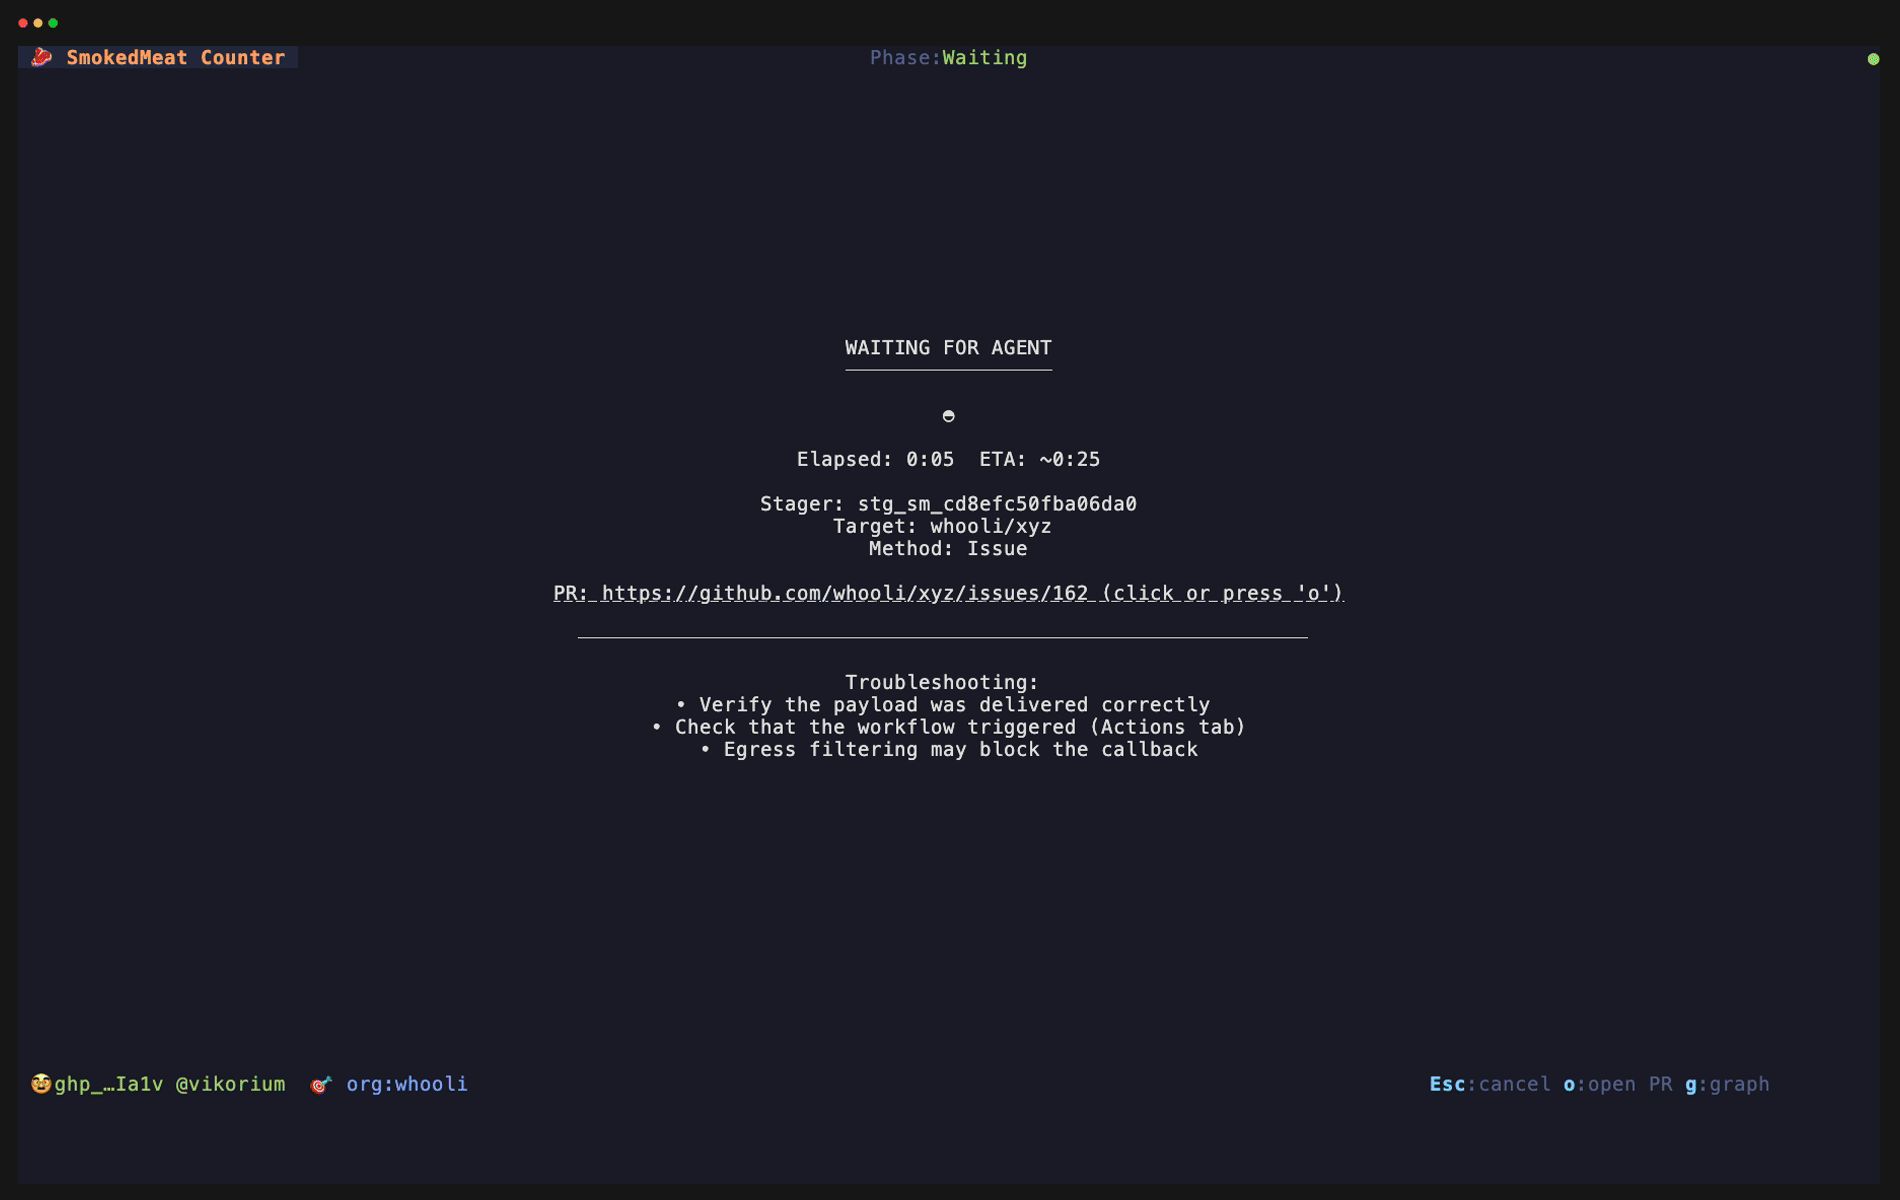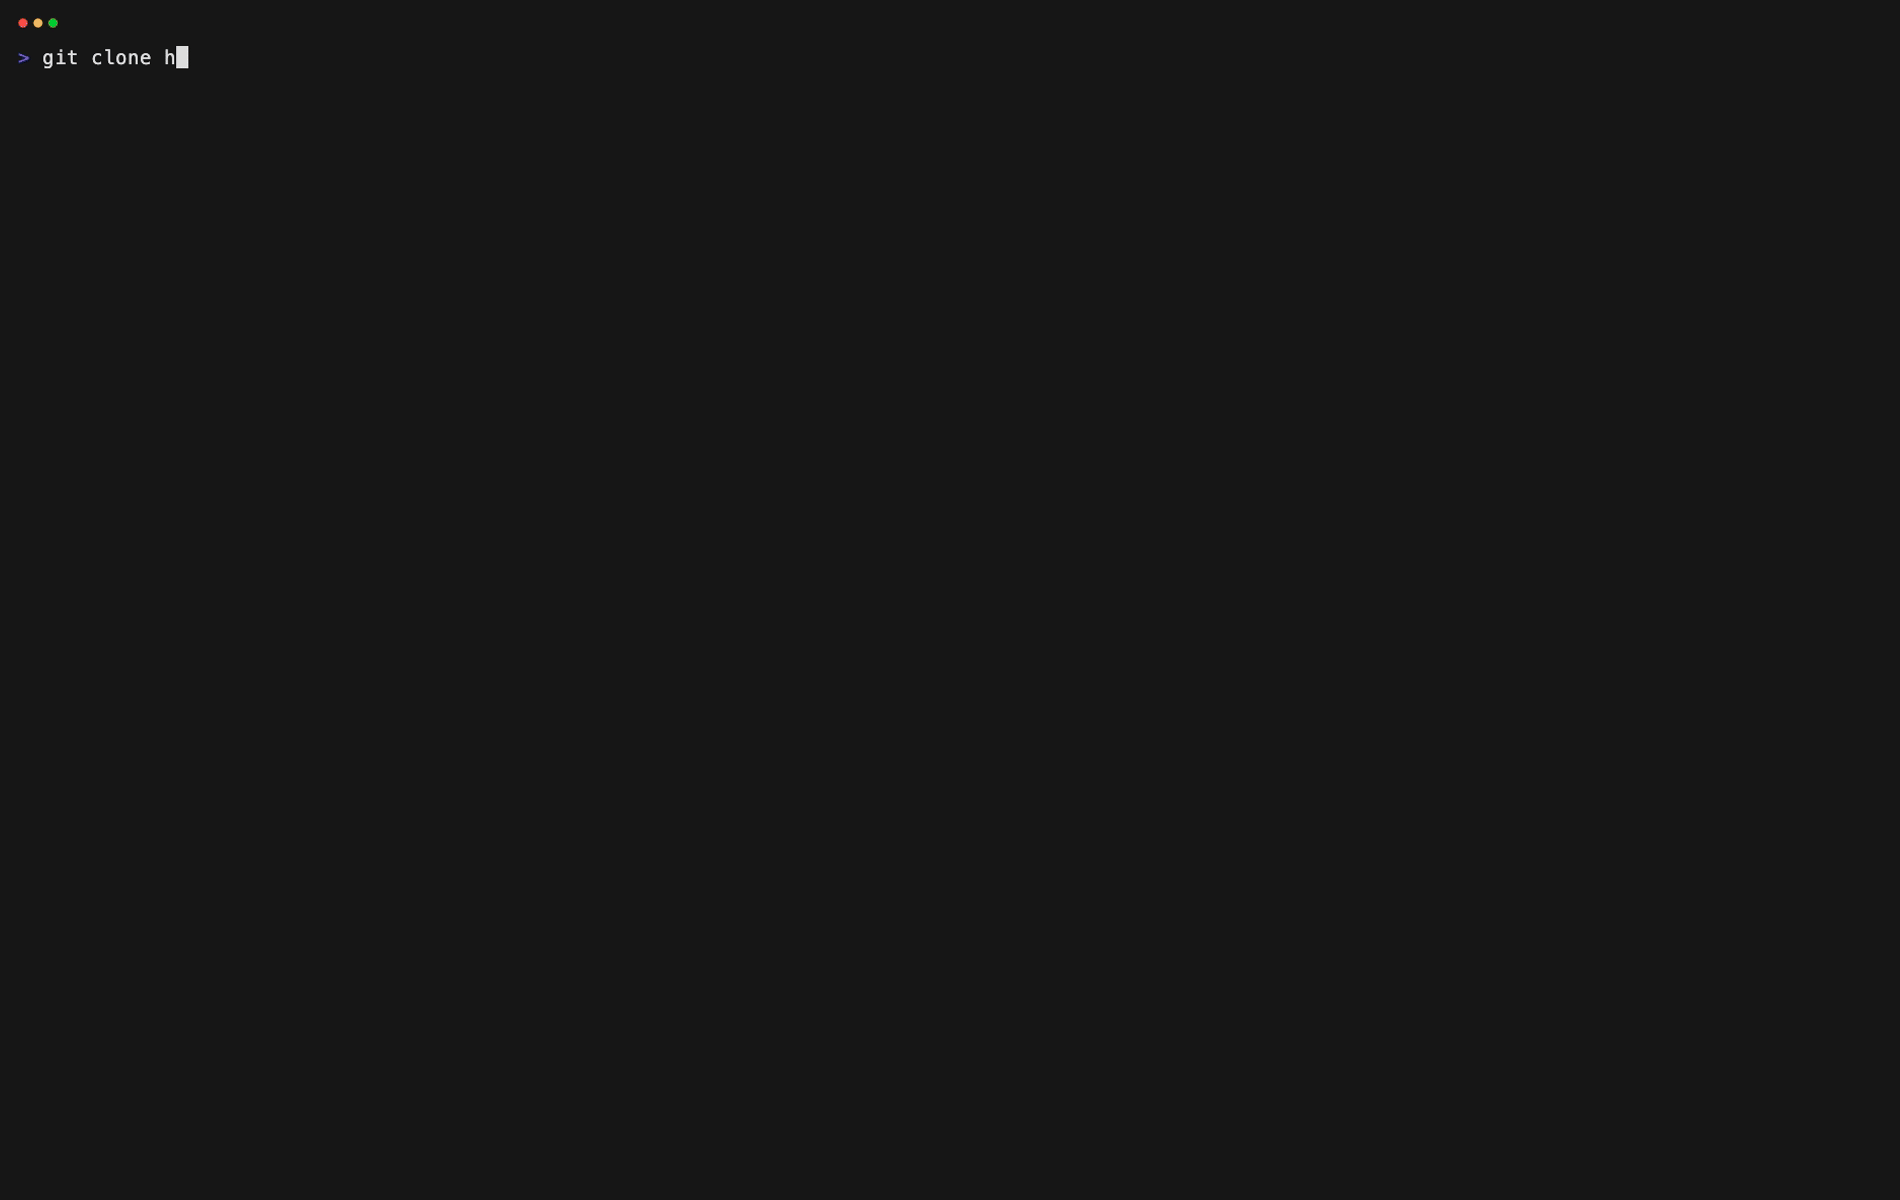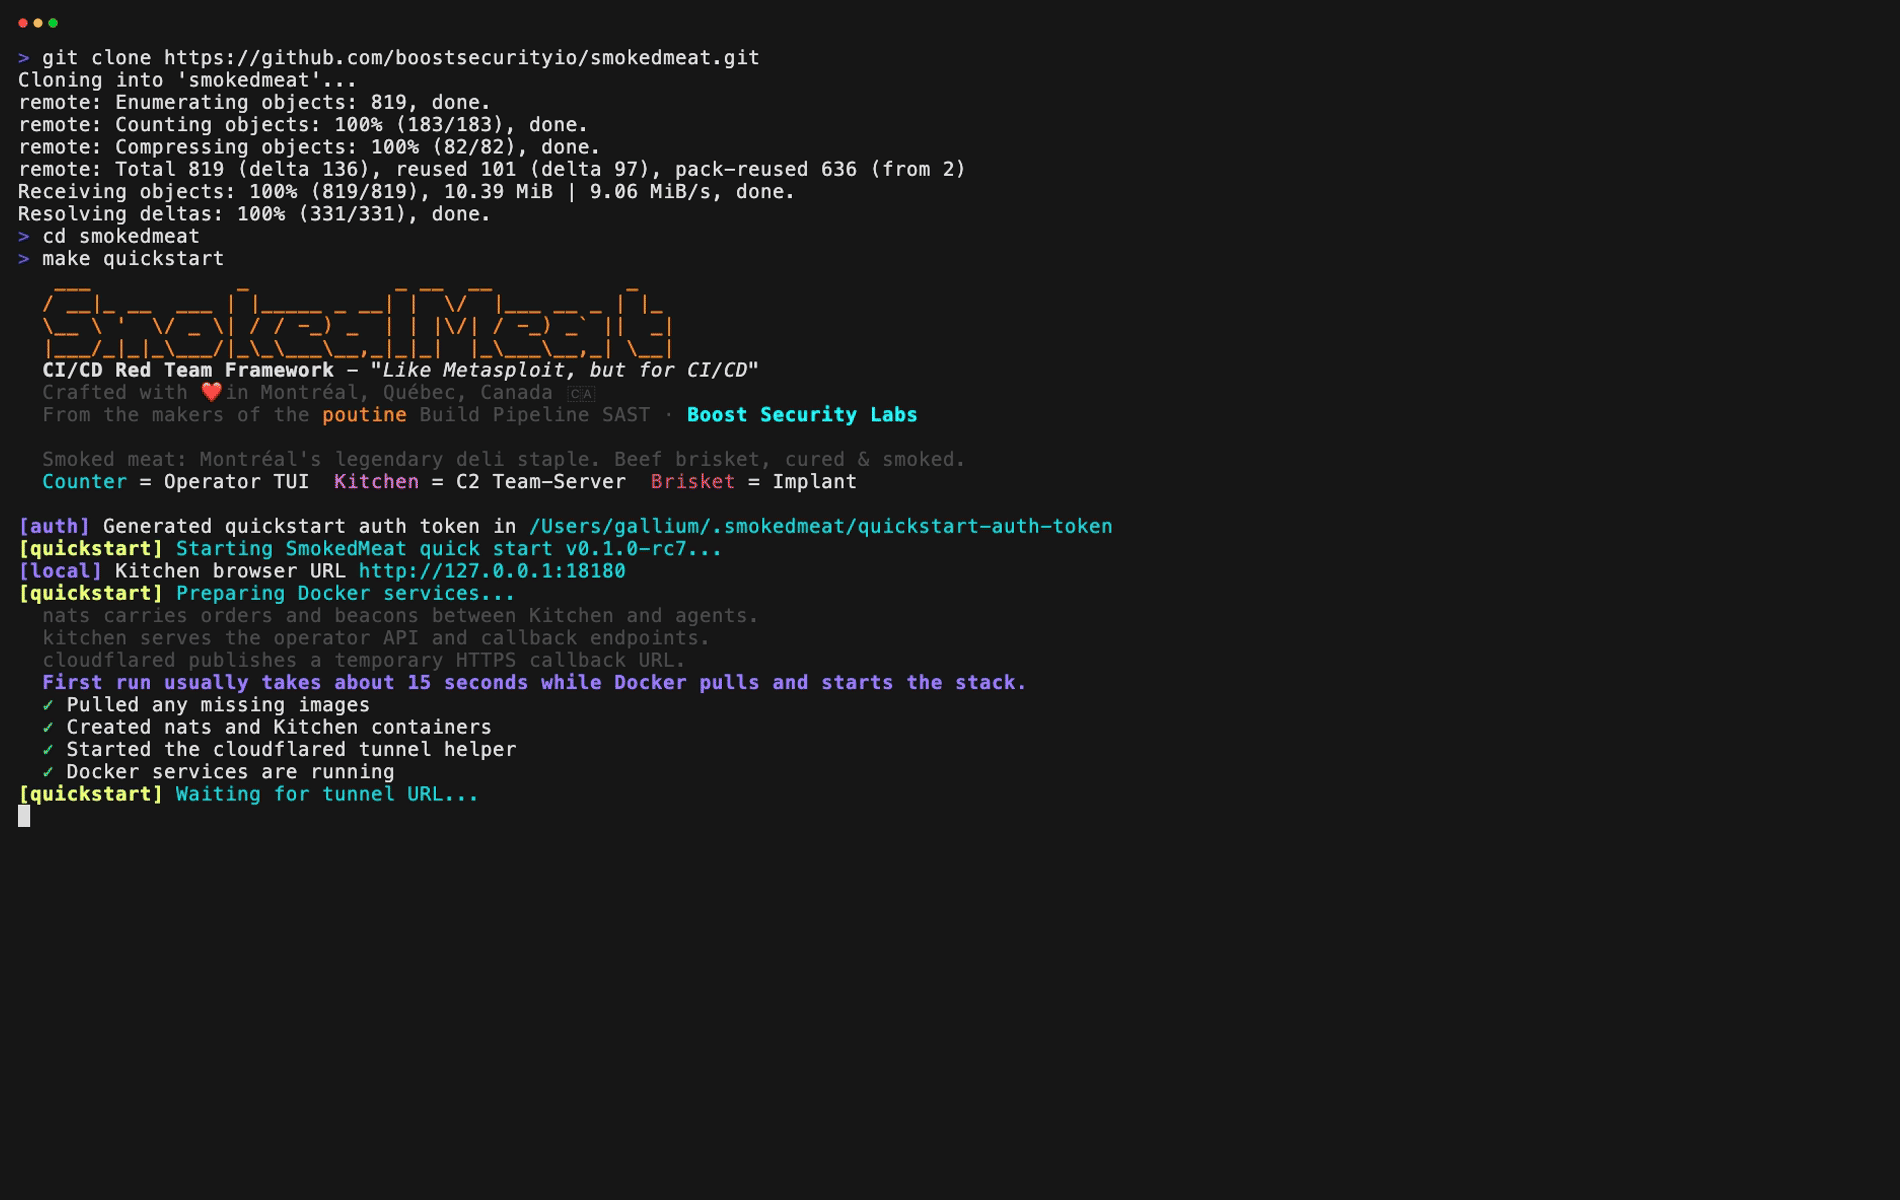 boostsecurityio/smokedmeat
A CI/CD Red Team Framework for demonstrating Build Pipeline security risks.
 xforcered/sqlrecon
A C# MS SQL toolkit designed for offensive reconnaissance and post-exploitation.
 synacktiv/sccmsqlclient
MSSQL client for SCCM environments, enabling reconnaissance, remote PowerShell execution on managed clients, and extraction of sensitive secrets such…
 josephtlucas/vger
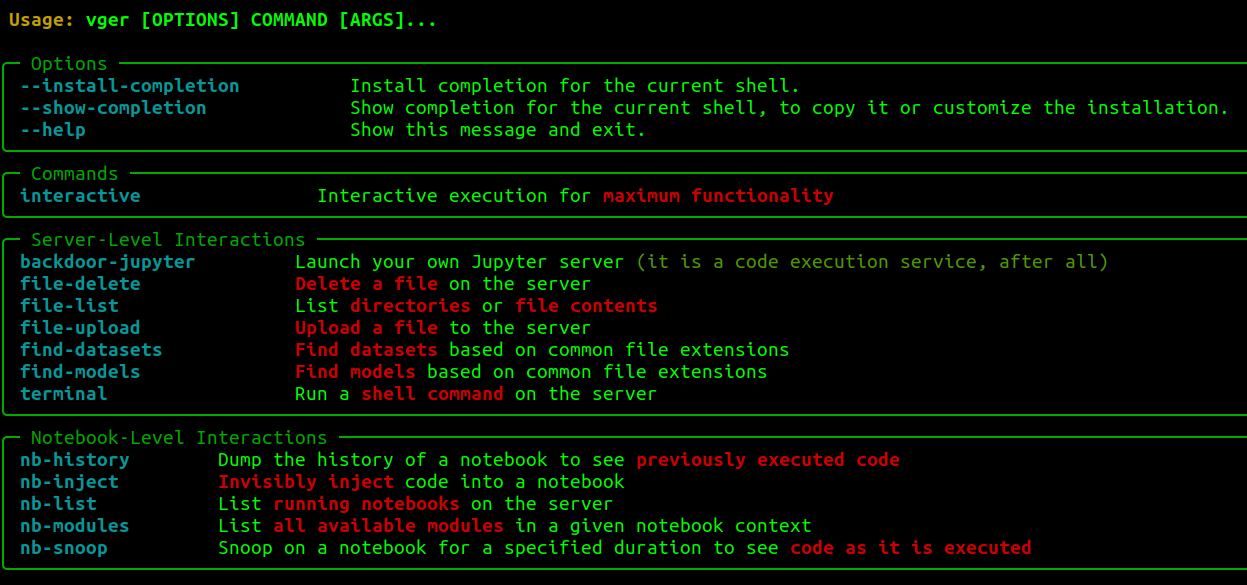
An interactive CLI application for interacting with authenticated Jupyter instances.