
GTFOBLookup
 nccgroup/gtfoblookup
Offline command line lookup utility for GTFOBins (https://github.com/GTFOBins/GTFOBins.github.io), LOLBAS (https://github.com/LOLBAS-Project/LOLBAS),…
information-gatheringlateral-movementpenetration-testing+3
nccgroup/gtfoblookupOffline command line lookup utility for GTFOBins (https://github.com/GTFOBins/GTFOBins.github.io), LOLBAS (https://github.com/LOLBAS-Project/LOLBAS),…
 blue0x1/nimux
Pure-Nim network enumeration and remote execution toolkit for authorized security assessments. Supports SMB, LDAP, Kerberos, WinRM, database clients,…
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
 zimedev/certipy-merged
Tool for Active Directory Certificate Services enumeration and abuse
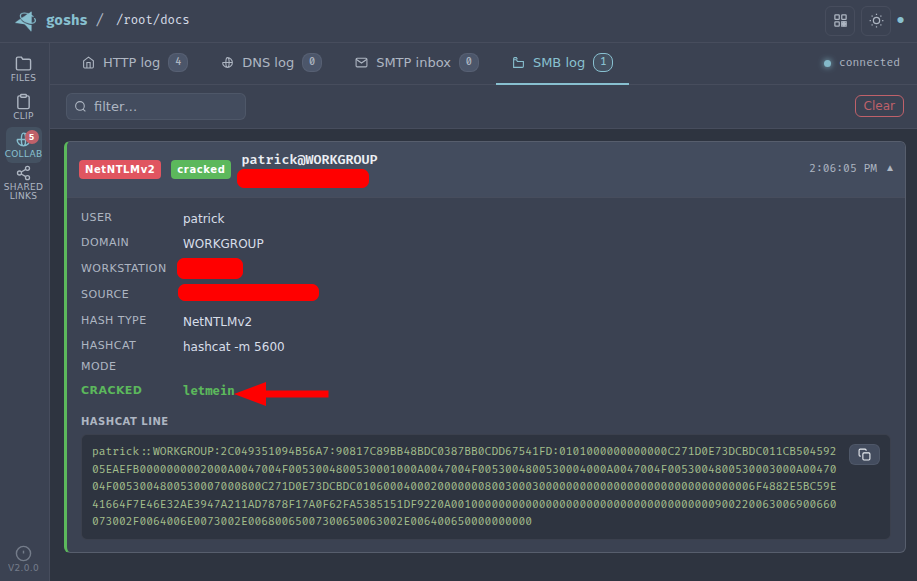 a-poc/redteam-tools
Tools and Techniques for Red Team / Penetration Testing
 ropnop/kerbrute
A tool to perform Kerberos pre-auth bruteforcing
 jobroche/credcrack
A fast and stealthy credential harvester
 punk-security/smbeagle
SMBeagle - Fileshare auditing tool.
 praetorian-inc/brutus
Fast, zero-dependency credential testing tool in Go. Brute force SSH, MySQL, PostgreSQL, Redis, MongoDB, SMB, and 20+ protocols. Hydra alternative…
 dievus/lnkbomb
Malicious shortcut generator for collecting NTLM hashes from insecure file shares.
 baptisterajaut/radmin-vpn-linux
Run Radmin VPN on Linux via Wine — custom driver, TAP bridge, zero packet loss
 charlesgargasson/cve-2024-32002
Exploit for CVE-2024-32002, a Git RCE vulnerability that uses recursive submodule cloning and symlinks to execute arbitrary commands on Windows and…
 n1nj4sec/pupy
Pupy is an opensource, cross-platform (Windows, Linux, OSX, Android) C2 and post-exploitation framework written in python and C
 seastorm/puttyrider
Hijack Putty sessions in order to sniff conversation and inject Linux commands.
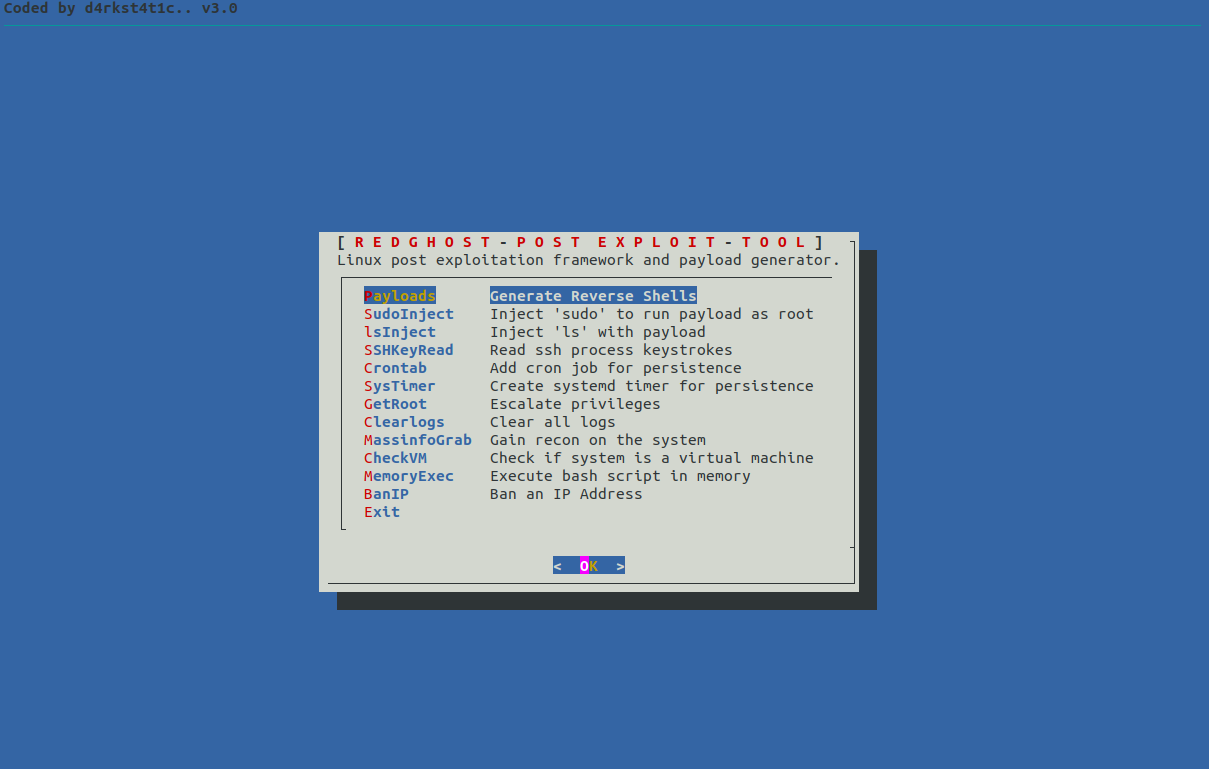 d4rk007/redghost
Linux post exploitation framework written in bash designed to assist red teams in persistence, reconnaissance, privilege escalation and leaving no…
 mythicagents/thanatos
Mythic C2 agent targeting Linux and Windows hosts written in Rust
 alessandroz/pupy
Pupy is an opensource, multi-platform (Windows, Linux, OSX, Android), multi function RAT (Remote Administration Tool) mainly written in python. It…
 voidsecsoftwares/voidsyscall
Cross-platform syscall-powered implant & C2 — direct syscalls (Win), raw syscalls (Linux), HTTPS/DNS/ICMP channels. No winapi layer.