
Active-Directory-Exploitation-Cheat-Sheet
 s1ckb0y1337/active-directory-exploitation-cheat-sheet
A cheat sheet that contains common enumeration and attack methods for Windows Active Directory.
curated-resourceseducationexploitation+5
s1ckb0y1337/active-directory-exploitation-cheat-sheetA cheat sheet that contains common enumeration and attack methods for Windows Active Directory.
 bittersecurity/decepticon
Autonomous LLM red team agent that plans and executes full attack chains—recon, exploitation, privilege escalation, lateral movement and C2—inside an…
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 samugit83/redamon
Autonomous AI red team framework that chains reconnaissance, exploitation, and post-exploitation into a single pipeline, then triages findings,…
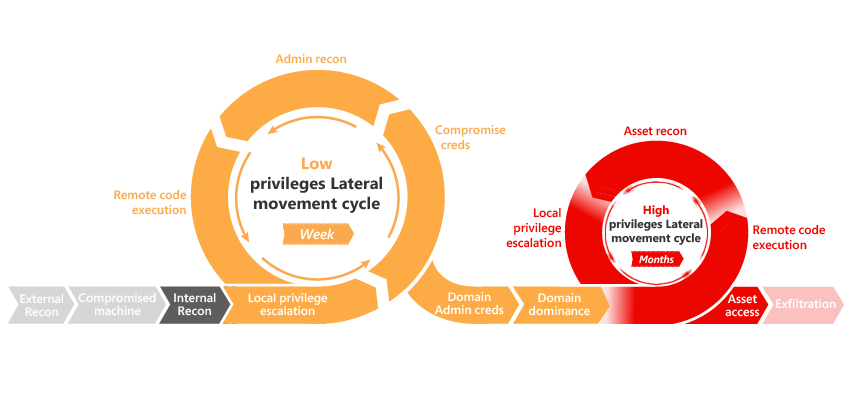 integration-it/active-directory-exploitation-cheat-sheet
A cheat sheet that contains common enumeration and attack methods for Windows Active Directory.
 s3n4t0r-0x0/apts-adversary-simulation
This repository contains detailed adversary simulation APT campaigns targeting various critical sectors. Each simulation includes custom tools, C2…
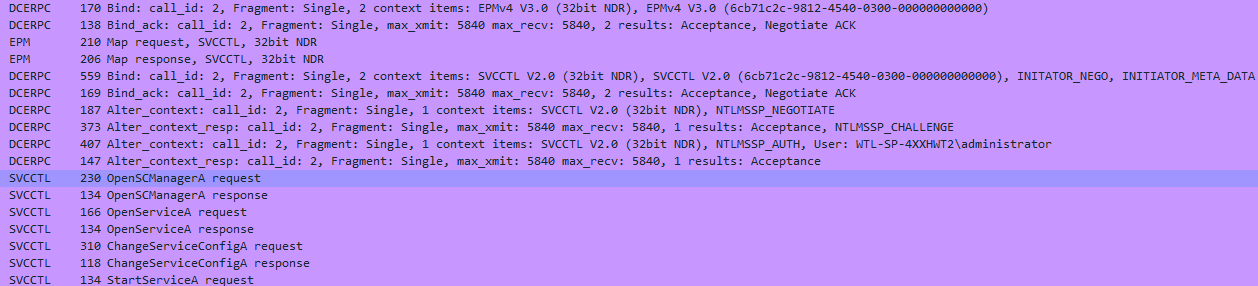 mr-un1k0d3r/scshell
Fileless lateral movement tool that relies on ChangeServiceConfigA to run command
 reverseclabs/sharpgpoabuse
SharpGPOAbuse is a .NET application written in C# that can be used to take advantage of a user's edit rights on a Group Policy Object (GPO) in order…
 arvanaghi/sessiongopher
SessionGopher is a PowerShell tool that uses WMI to extract saved session information for remote access tools such as WinSCP, PuTTY, SuperPuTTY,…
 ad-security/ad_miner
AD Miner is an Active Directory audit tool that leverages cypher queries to crunch data from the #Bloodhound graph database to uncover security…
 redsiege/wmimplant
This is a PowerShell based tool that is designed to act like a RAT. Its interface is that of a shell where any command that is supported is…
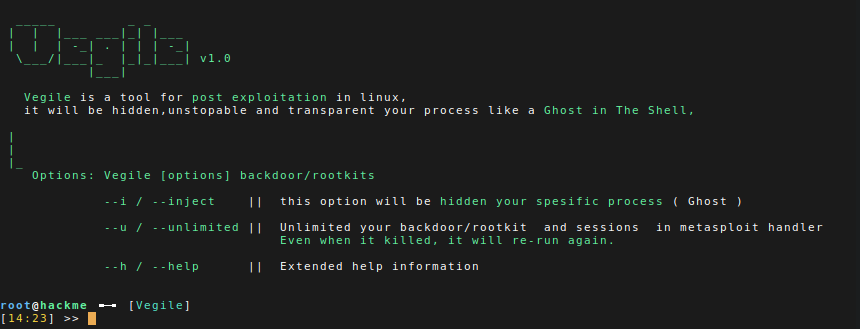 screetsec/vegile
This tool will setting up your backdoor/rootkits when backdoor already setup it will be hidden your spesisifc process,unlimited your session in…
 med0x2e/gadgettojscript
A tool for generating .NET serialized gadgets that can trigger .NET assembly load/execution when deserialized using BinaryFormatter from JS/VBS/VBA…
 gellin/teamviewer_permissions_hook_v1
A proof of concept injectable C++ dll, that uses naked inline hooking and direct memory modification to change your TeamViewer permissions.
 mvelazc0/purplesharp
PurpleSharp is a C# adversary simulation tool that executes adversary techniques with the purpose of generating attack telemetry in monitored Windows…
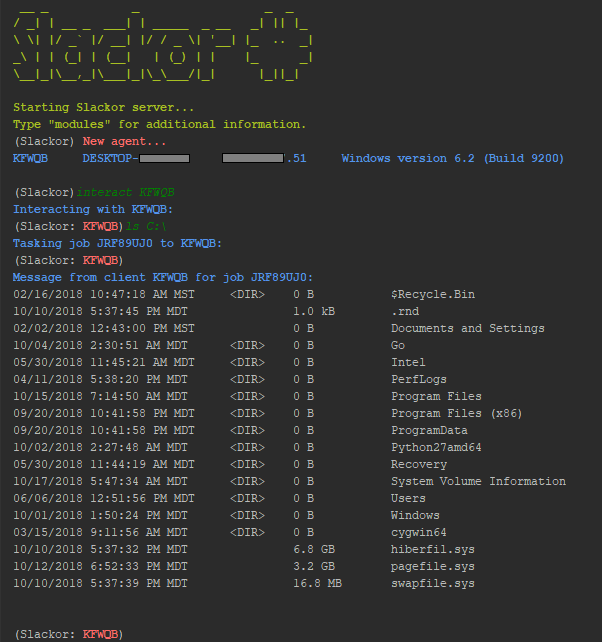 coalfire-research/slackor
A Golang implant that uses Slack as a command and control server
 slowerzs/thievingfox
Post-exploitation credential harvesting toolkit that injects into password managers and Windows utilities to capture credentials via DLL proxying,…
 petercunha/goat
🐐 GoAT (Golang Advanced Trojan) is a trojan that uses Twitter as a C&C server