
SharpCollection
 flangvik/sharpcollection
Nightly builds of common C# offensive tools, fresh from their respective master branches built and released in a CDI fashion using Azure DevOps…
curated-resourcesexploitationlateral-movement+6
3.0k
flangvik/sharpcollectionNightly builds of common C# offensive tools, fresh from their respective master branches built and released in a CDI fashion using Azure DevOps…
 infosecn1nja/ad-attack-defense
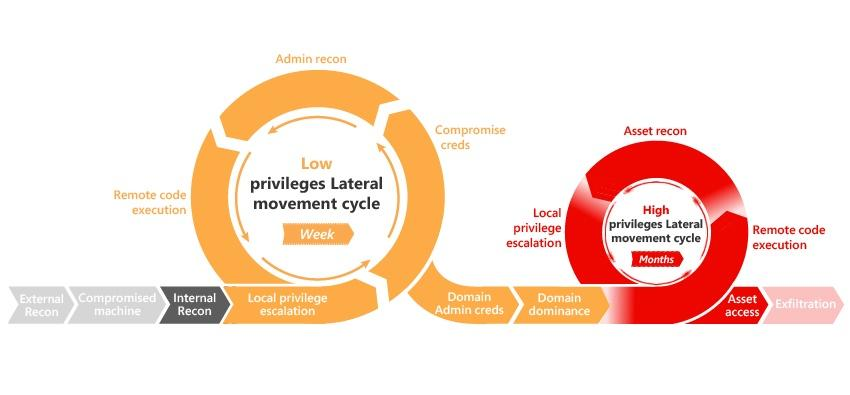
Attack and defend active directory using modern post exploitation adversary tradecraft activity
 lgandx/responder
Responder is a LLMNR, NBT-NS and MDNS poisoner, with built-in HTTP/SMB/MSSQL/FTP/LDAP rogue authentication server supporting NTLMv1/NTLMv2/LMv2,…
 hackerschoice/thc-tips-tricks-hacks-cheat-sheet
Various tips & tricks
 guardicore/monkey
Infection Monkey - An open-source adversary emulation platform
 samugit83/redamon
Autonomous AI red team framework that chains reconnaissance, exploitation, and post-exploitation into a single pipeline, then triages findings,…
 fuzzysecurity/powershell-suite
My musings with PowerShell
 cdk-team/cdk
📦 Make security testing of K8s, Docker, and Containerd easier.
 k8gege/ladon
Ladon大型内网渗透扫描器,PowerShell、Cobalt Strike插件、内存加载、无文件扫描。含端口扫描、服务识别、网络资产探测、密码审计、高危漏洞检测、漏洞利用、密码读取以及一键GetShell,支持批量A段/B段/C段以及跨网段扫描,支持URL、主机、域名列表扫描等。网络资产探测32…
 netspi/powerupsql
PowerUpSQL: A PowerShell Toolkit for Attacking SQL Server
 integration-it/active-directory-exploitation-cheat-sheet
A cheat sheet that contains common enumeration and attack methods for Windows Active Directory.
 s3n4t0r-0x0/apts-adversary-simulation
This repository contains detailed adversary simulation APT campaigns targeting various critical sectors. Each simulation includes custom tools, C2…
 subat0mik/misconfiguration-manager
Misconfiguration Manager is a central knowledge base for all known Microsoft Configuration Manager tradecraft and associated defensive and hardening…
 jm33-m0/emp3r0r
Self‑healing Gossip Mesh C2 with Assisted Peer Discovery, Cross-Platform BOF Execution, and Scriptable Agents.
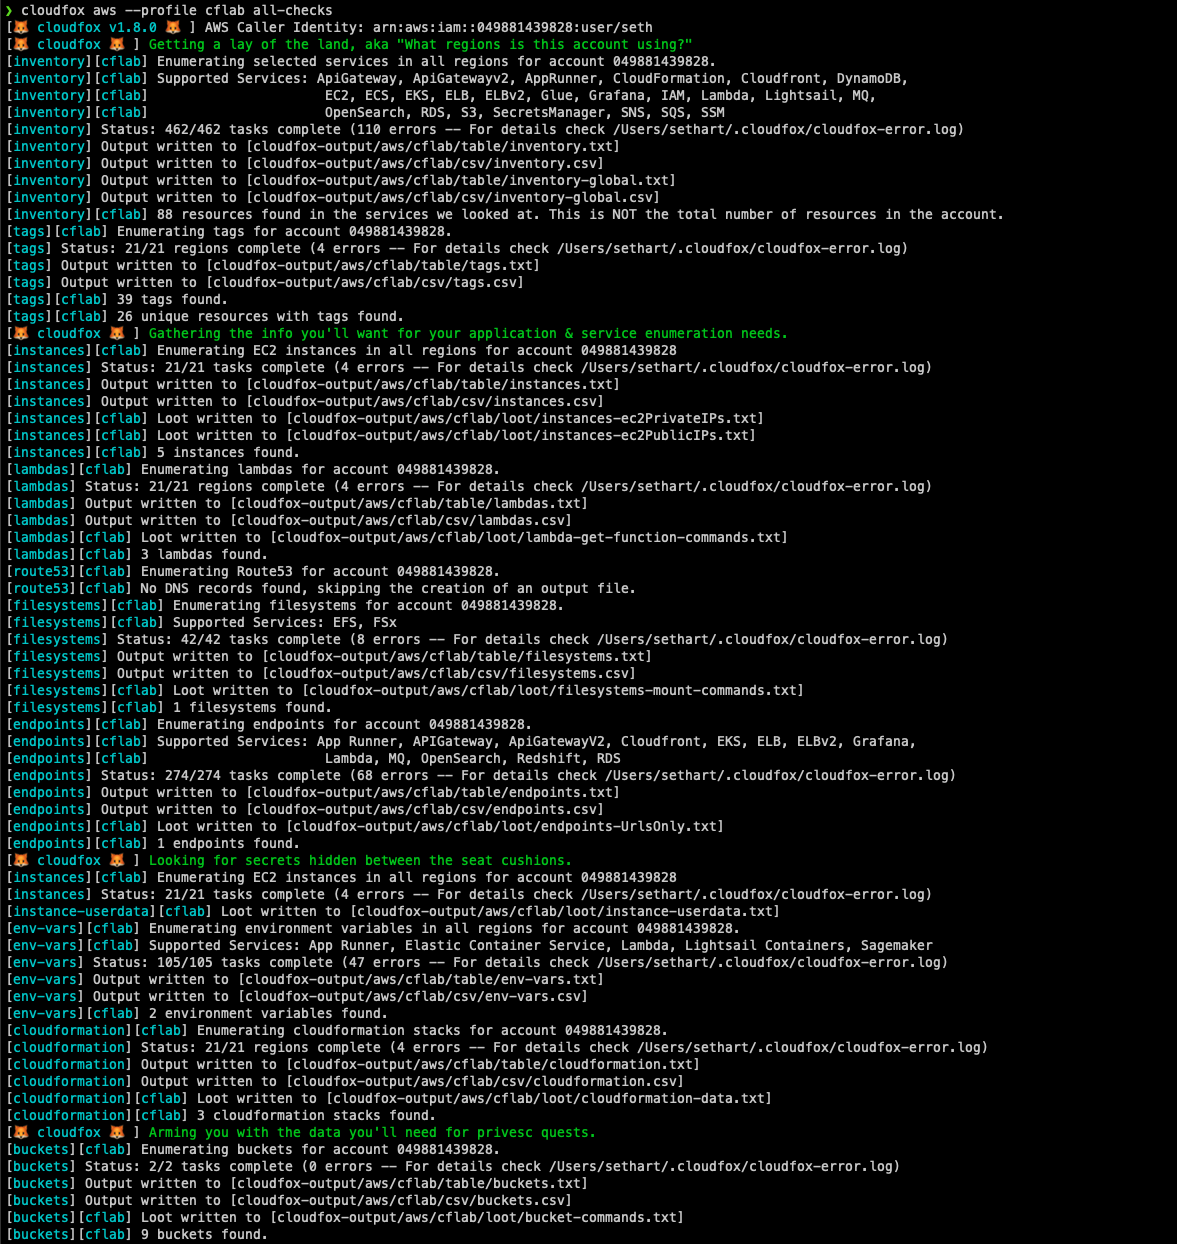 bishopfox/cloudfox
Automating situational awareness for cloud penetration tests.
 specterops/sharphound
Collects Active Directory object metadata, group memberships, sessions, ACLs, and trusts to feed BloodHound attack-path mapping for security…
 ropnop/kerbrute
A tool to perform Kerberos pre-auth bruteforcing
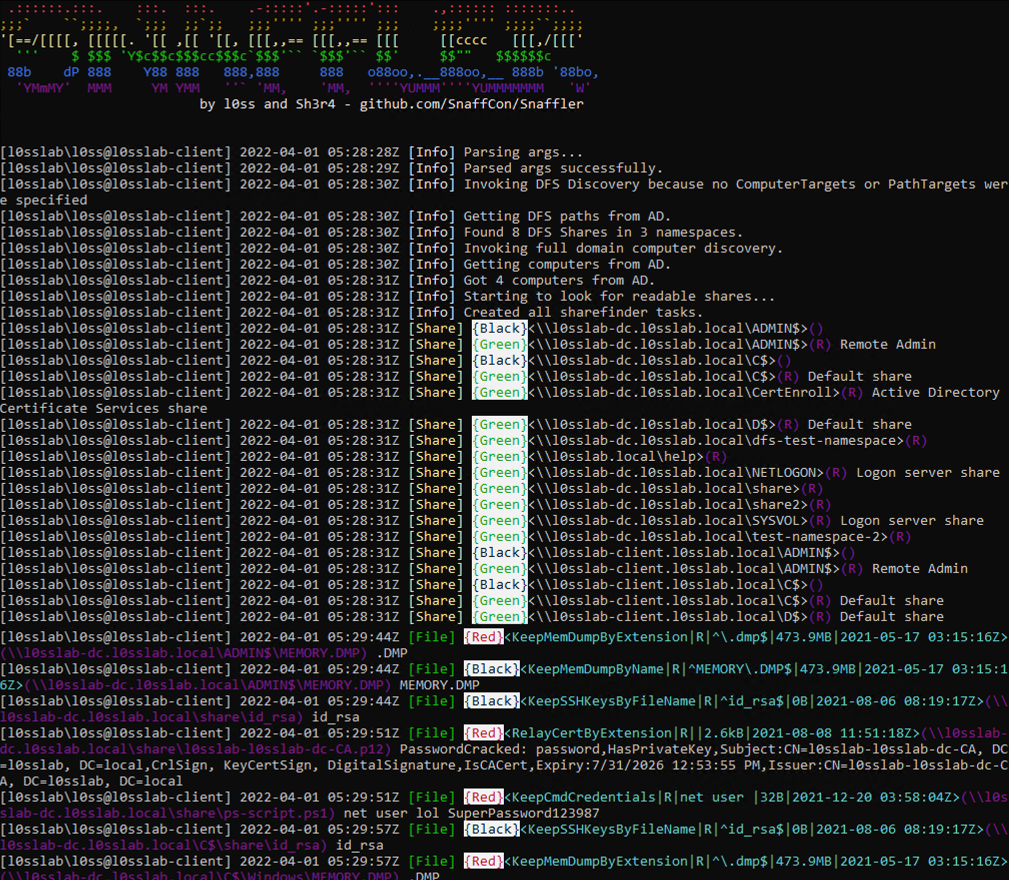 snaffcon/snaffler
a tool for pentesters to help find delicious candy, by @l0ss and @Sh3r4 ( Twitter: @/mikeloss and @/sh3r4_hax )