
Awesome-Redteam
 threekiii/awesome-redteam
一个攻防知识库。A knowledge base for red teaming and offensive security.
command-and-controlcurated-resourceseducation+9
4.4k
threekiii/awesome-redteam一个攻防知识库。A knowledge base for red teaming and offensive security.
 aniket2912/internal-network-penetration-testing
Educational module on internal network penetration testing: methodology, attack vectors, enumeration, exploitation, privilege escalation, and…
 capture0x/adstrike
AI-powered modular Active Directory red-team framework for authorized penetration testing, AD enumeration, attack-path analysis, Kerberos/ADCS…
 bittersecurity/decepticon
Autonomous LLM red team agent that plans and executes full attack chains—recon, exploitation, privilege escalation, lateral movement and C2—inside an…
 kypvas/ad_attack_architecture
Active Directory Attack Architecture Map Comprehensive Pentest Reference — From Recon to Domain Dominance
 kypvas/red-team-map
Red Team Operations Architecture Map Comprehensive Operator Reference — From Infrastructure to Impact
 stillbigjosh/kube-reaper
Scans Kubernetes clusters from any identity, flags dangerous permissions, and chains them into multi-step escalation paths to cluster compromise.
 hac01/azure-pentesting-suite
Go toolkit for authorized Azure security assessments: enumerates subscriptions and resources, audits misconfigurations, and attacks public Blob…
 ustayready/thunderstorm
A collector and derivation engine. It maps your environment, evaluates effective permissions and trust, and writes a complete attack graph as a…
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
 hkenzokimura/cve-2021-1675
Educational proof-of-concept for PrintNightmare (CVE-2021-1675/34527) with simulated non-functional payload, attack flow analysis, MITRE mapping,…
 portbuster1337/atlas
Cross-platform network execution toolkit (SMB/Kerberos/WMI/LDAP/DCSync) built on TrustedSec's Titanis - NetExec-style workflow in C#
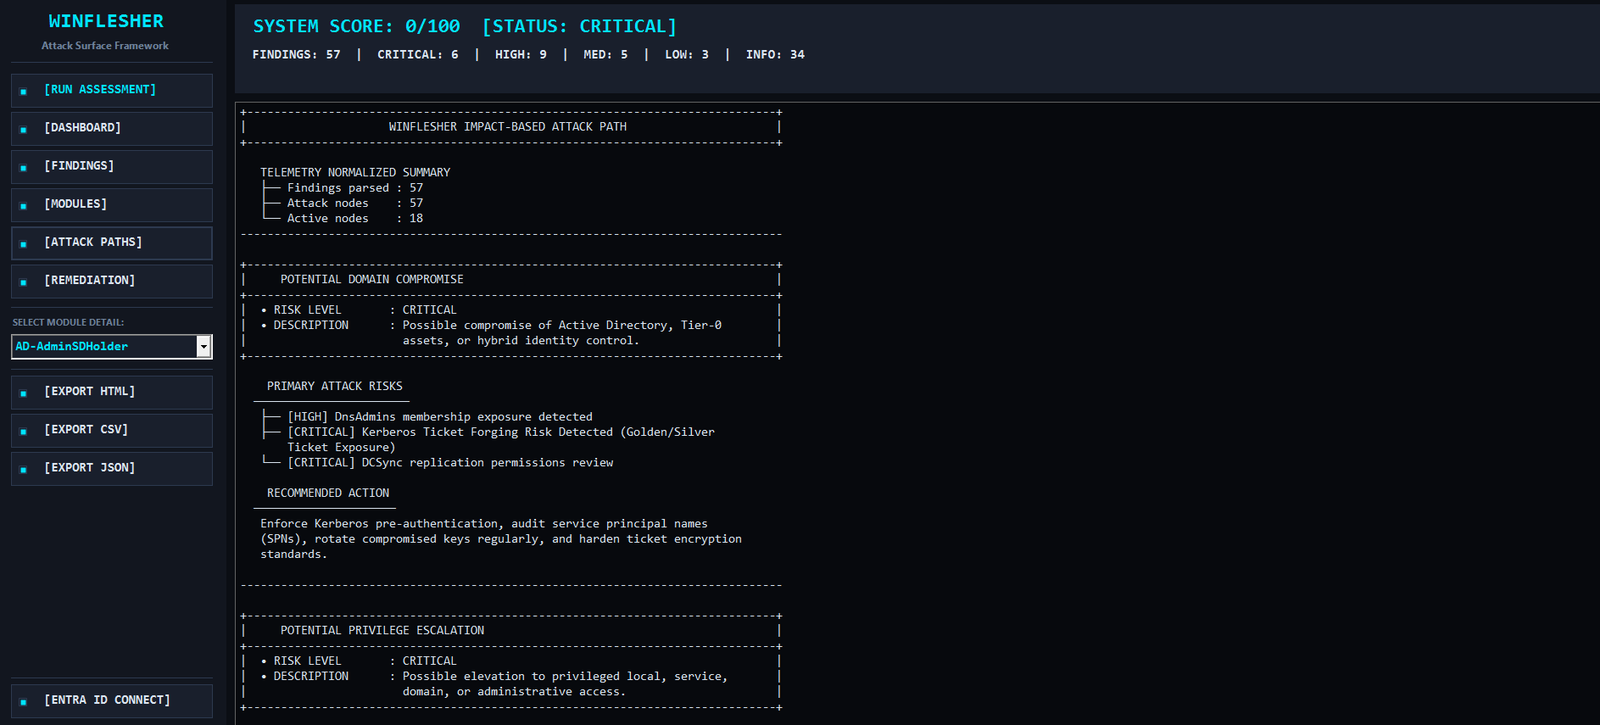 mindsflee/winflesher
Automated attack surface assessment framework for Active Directory and local infrastructures, correlating vulnerabilities with attack paths to domain…
 kaleth4/cve-2026-20180
In-depth technical analysis of Cisco ISE RCE vulnerabilities, including exploitation techniques, evasion methods, and remediation strategies for…
 specterops/sharphound
Collects Active Directory object metadata, group memberships, sessions, ACLs, and trusts to feed BloodHound attack-path mapping for security…
 wattocyber/oscp-notes-2026
OSCP notes vault + exam cockpit dashboard: merged technique notes, variable-filled command decks, machines, creds, and runbook for exam day. MIT.
 wattocyber/offensive-one-liners
110 offensive-security one-liners for authorized testing and CTFs, grouped by category and kill-chain step.
 squidsec/bloodbash
Offline AD/Entra attack-path analyzer for SharpHound/AzureHound JSON. Surfaces prioritized privilege escalation, credential, and misconfiguration…