

ConfluenceC2
 dagowda/confluencec2
This is a project aimed to make every other Saas product a C2, confluence is just the beginning.
command-and-controldata-exfiltrationlateral-movement+9
21
dagowda/confluencec2This is a project aimed to make every other Saas product a C2, confluence is just the beginning.
 b3rt1ng/koi
Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
 squidsec/bloodbash
Offline AD/Entra attack-path analyzer for SharpHound/AzureHound JSON. Surfaces prioritized privilege escalation, credential, and misconfiguration…
 eladshamir/rpc-backdoor
A basic emulation of an "RPC Backdoor"
 skelsec/aardwolf
Asynchronous RDP client for Python (headless)
 deepinstinct/dcomuploadexec
DCOM Lateral movement POC abusing the IMsiServer interface - uploads and executes a payload remotely
 synacktiv/ouned
The OUned project automating Active Directory Organizational Units ACL exploitation through gPLink poisoning
 cobbr/elite
Elite is the client-side component of the Covenant project. Covenant is a .NET command and control framework that aims to highlight the attack…
 melardev/xeytanwin32-rat
WORK IN PROGRESS. RAT written in C++ using Win32 API
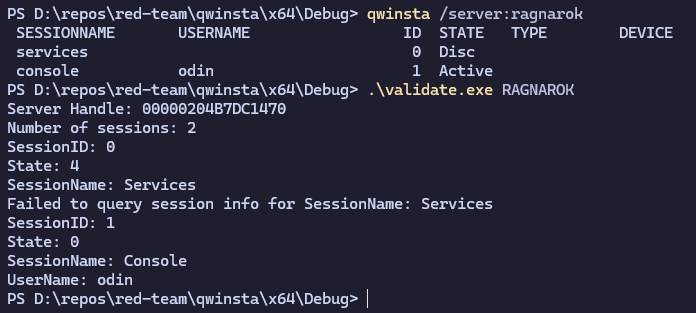 0xv1n/remotesessionenum
Remotely Enumerate sessions using undocumented Windows Station APIs
 pswalia2u/cve-2025-24071_poc
Rust-based proof-of-concept that generates Windows Library (.library-ms) files with configurable network paths to demonstrate CVE-2025-24071 NTLM…
 vignesh-hp/lockbit-ransomware-analysis
Threat intelligence and incident response case study on LockBit ransomware exploiting CVE-2023-4966 (Citrix Bleed).
 p1rat3r00t/why-so-serious-sam
PoC malware that uses exploit CVE-2021-36934 (improper ACLs on shadow copies) using a fileless red team method on Windows 10/11 with LOLBins,…
 samugit83/redamon
Autonomous AI red team framework that chains reconnaissance, exploitation, and post-exploitation into a single pipeline, then triages findings,…
 xm0kht4r/av-edr-killer
AV/EDR processes termination by exploiting a vulnerable driver (BYOVD)
 octoberfest7/dscourier_bof
BOF POC of the DSCourier project / invoking WinGet via COM
 edu0x01/hack-tools
Project that brings together several pentest tools
 dviros/excalibur
Excalibur is an Eternalblue exploit payload based "Powershell" for the Bashbunny project.