

HorusEye
 omar-tamerr/horuseye
AI-Powered Active Directory Attack Platform
defensive-toolsinformation-gatheringlateral-movement+6
omar-tamerr/horuseyeAI-Powered Active Directory Attack Platform
 spellshift/realm
Cross-platform adversary emulation framework with a Rust implant, GraphQL teamserver, and Eldritch DSL for automated, scalable red team operations…
 threekiii/awesome-redteam
一个攻防知识库。A knowledge base for red teaming and offensive security.
 aniket2912/internal-network-penetration-testing
Educational module on internal network penetration testing: methodology, attack vectors, enumeration, exploitation, privilege escalation, and…
 capture0x/adstrike
AI-powered modular Active Directory red-team framework for authorized penetration testing, AD enumeration, attack-path analysis, Kerberos/ADCS…
 kr0no/bloodhound-shell
An interactive command-line shell for BloodHound API.
 bittersecurity/decepticon
Autonomous LLM red team agent that plans and executes full attack chains—recon, exploitation, privilege escalation, lateral movement and C2—inside an…
 karmanya03/overthrone
All-Rust Active Directory exploitation framework: LDAP/SMB/Kerberos enumeration, attack-graph pathfinding, Kerberoasting, NTLM relay, ticket forging,…
 kypvas/ad_attack_architecture
Active Directory Attack Architecture Map Comprehensive Pentest Reference — From Recon to Domain Dominance
 kypvas/red-team-map
Red Team Operations Architecture Map Comprehensive Operator Reference — From Infrastructure to Impact
 stillbigjosh/kube-reaper
Scans Kubernetes clusters from any identity, flags dangerous permissions, and chains them into multi-step escalation paths to cluster compromise.
 hac01/azure-pentesting-suite
Go toolkit for authorized Azure security assessments: enumerates subscriptions and resources, audits misconfigurations, and attacks public Blob…
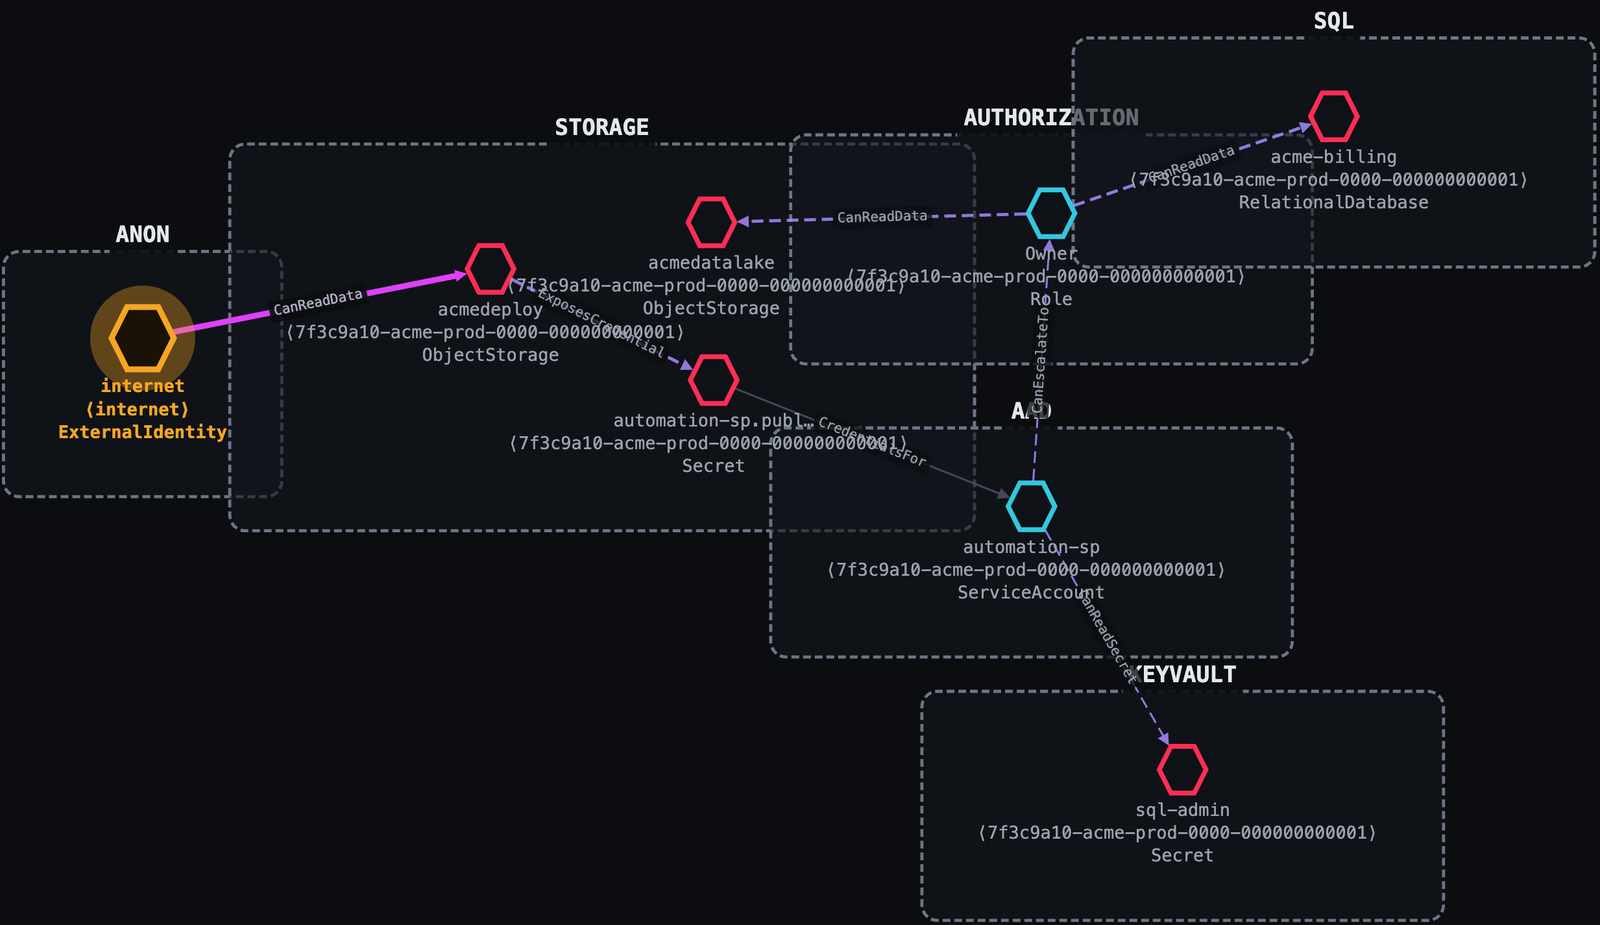 ustayready/thunderstorm
A collector and derivation engine. It maps your environment, evaluates effective permissions and trust, and writes a complete attack graph as a…
 bardlaudian/cve-2025-24071
Dependency-free Python PoC generator for CVE-2025-24071 that crafts a malicious .library-ms file in a ZIP to trigger Windows Explorer NTLM hash…
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
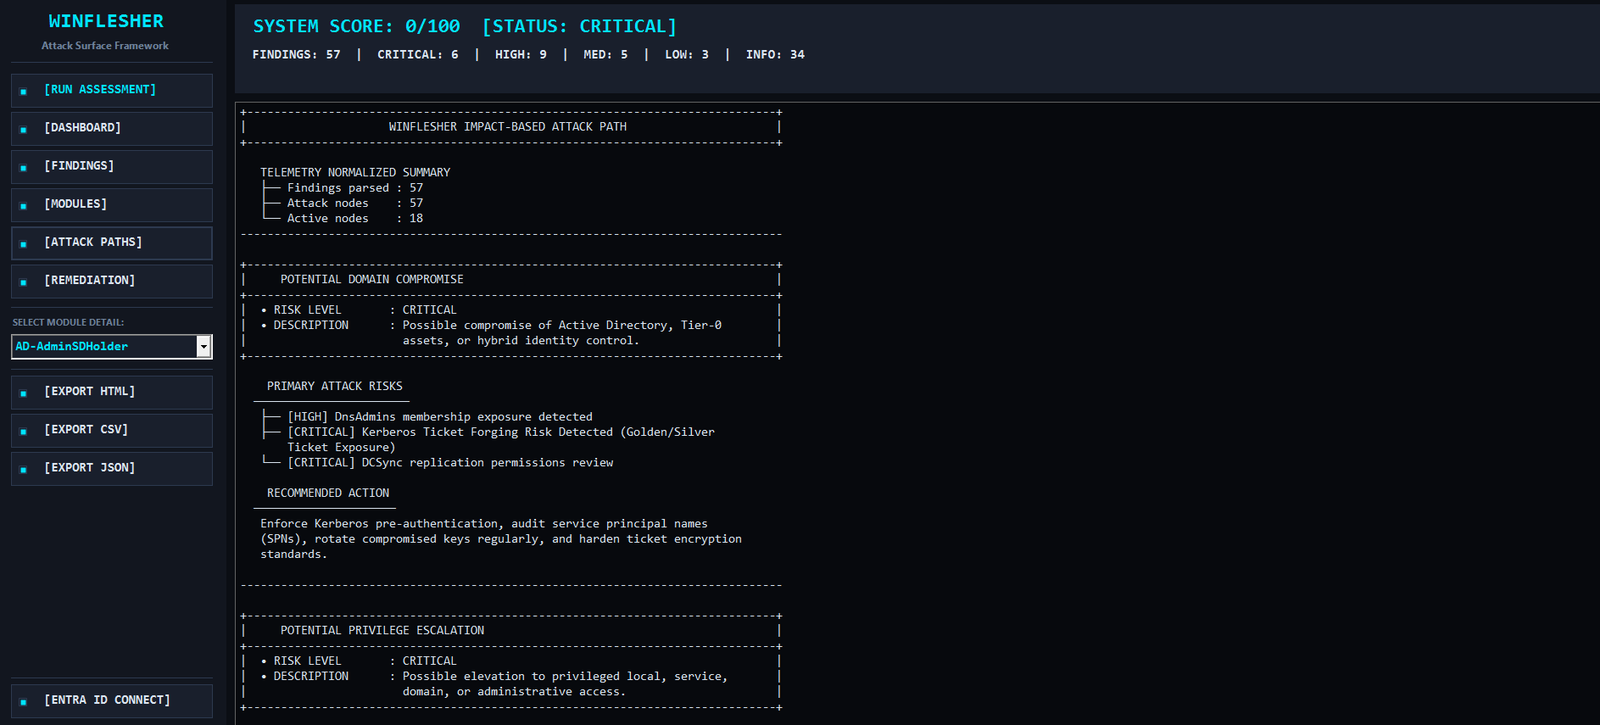 mindsflee/winflesher
Automated attack surface assessment framework for Active Directory and local infrastructures, correlating vulnerabilities with attack paths to domain…
 kaleth4/cve-2026-20180
In-depth technical analysis of Cisco ISE RCE vulnerabilities, including exploitation techniques, evasion methods, and remediation strategies for…
 specterops/sharphound
Collects Active Directory object metadata, group memberships, sessions, ACLs, and trusts to feed BloodHound attack-path mapping for security…