

Heroinn
 b23r0/heroinn
A cross platform C2/post-exploitation framework.
command-and-controldata-exfiltrationlateral-movement+8
b23r0/heroinnA cross platform C2/post-exploitation framework.
 bishopfox/sliver
Adversary Emulation Framework
 mandiant/gopacket
A complete Go port of Impacket - 63 CLI tools and 24 libraries for Windows & Active Directory protocol attacks, compiled to a single dependency-free…
 adityatelange/evil-winrm-py
Execute commands interactively on remote Windows machines using the WinRM protocol (just faster)
 lgandx/responder
Responder is a LLMNR, NBT-NS and MDNS poisoner, with built-in HTTP/SMB/MSSQL/FTP/LDAP rogue authentication server supporting NTLMv1/NTLMv2/LMv2,…
 squidsec/bloodbash
Offline AD/Entra attack-path analyzer for SharpHound/AzureHound JSON. Surfaces prioritized privilege escalation, credential, and misconfiguration…
 purpleailab/decepticon
Autonomous Hacking Agent for Red Team
 mythicagents/xenon
A Mythic agent for Windows written in C
 sp00kyskelet0n/py-rdp-patcher
Python script that patches the termsrv.dll file on Windows to enable multiple concurrent RDP sessions, supporting Windows 10 versions 1703 through…
 b3rt1ng/koi
Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
 gentilkiwi/mimikatz
A little tool to play with Windows security
 cube0x0/krbrelay
Kerberos relay framework for Windows environments enabling authentication relay, privilege escalation, and lateral movement via LDAP, SMB, HTTP, and…
 med0x2e/sigflip
SigFlip is a tool for patching authenticode signed PE files (exe, dll, sys ..etc) without invalidating or breaking the existing signature.
 qwqdanchun/dcrat
A simple remote tool in C#.
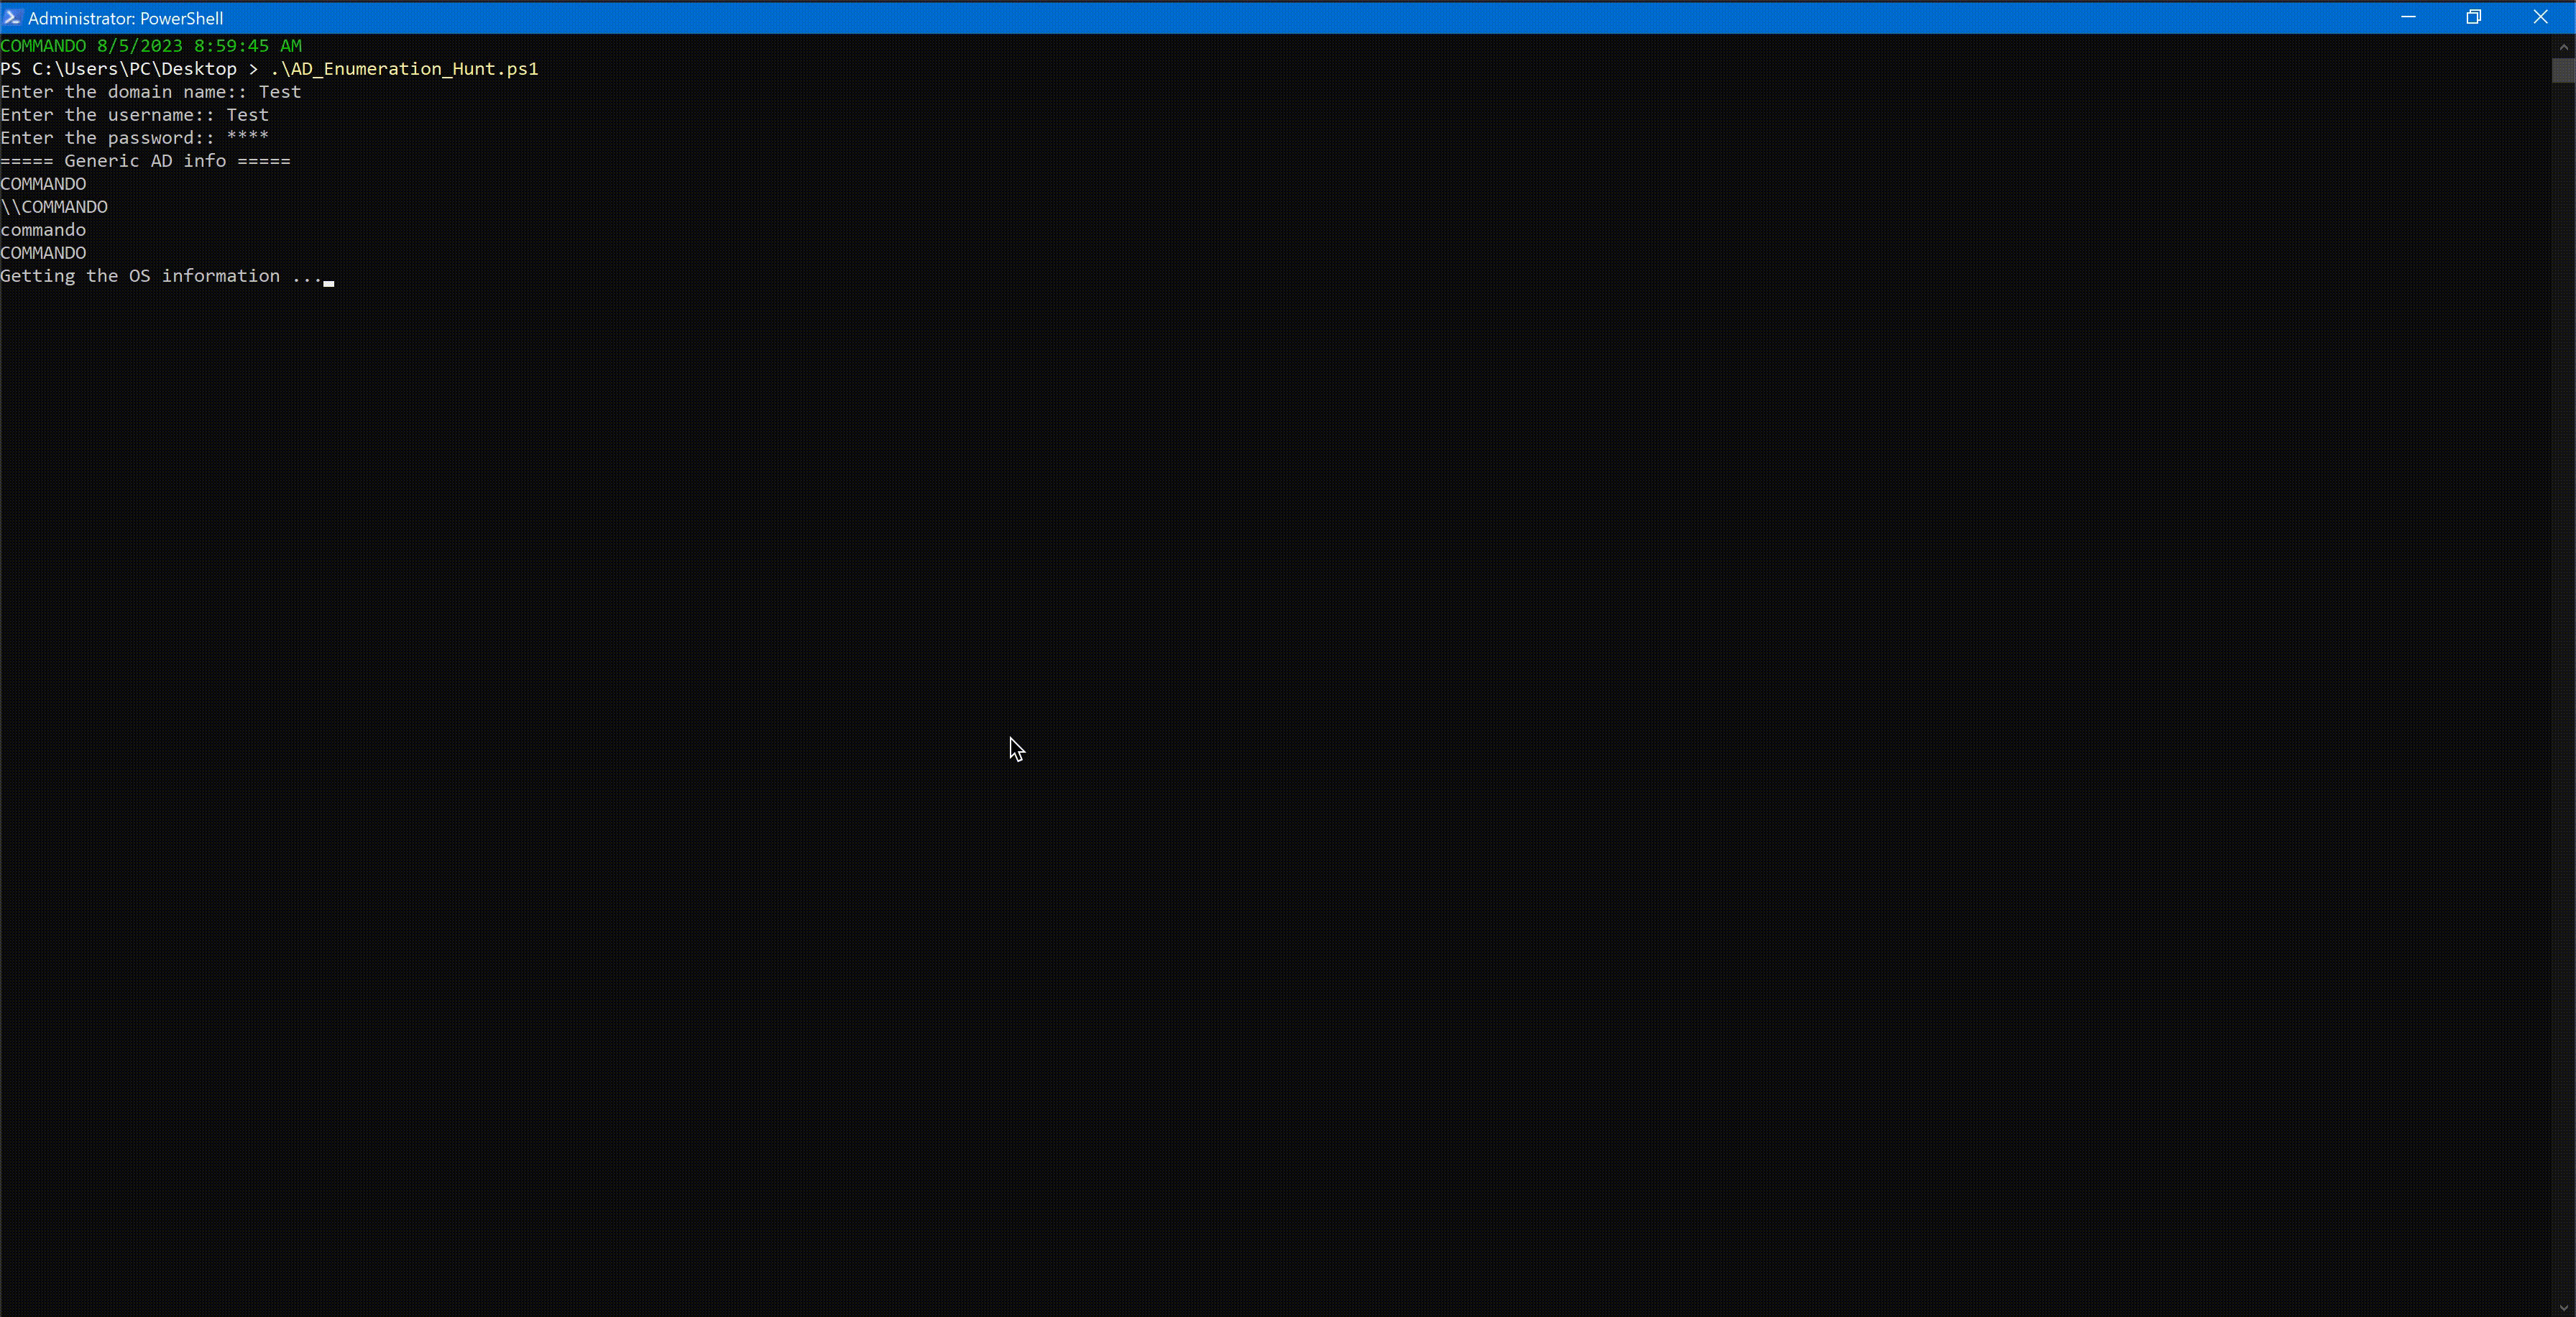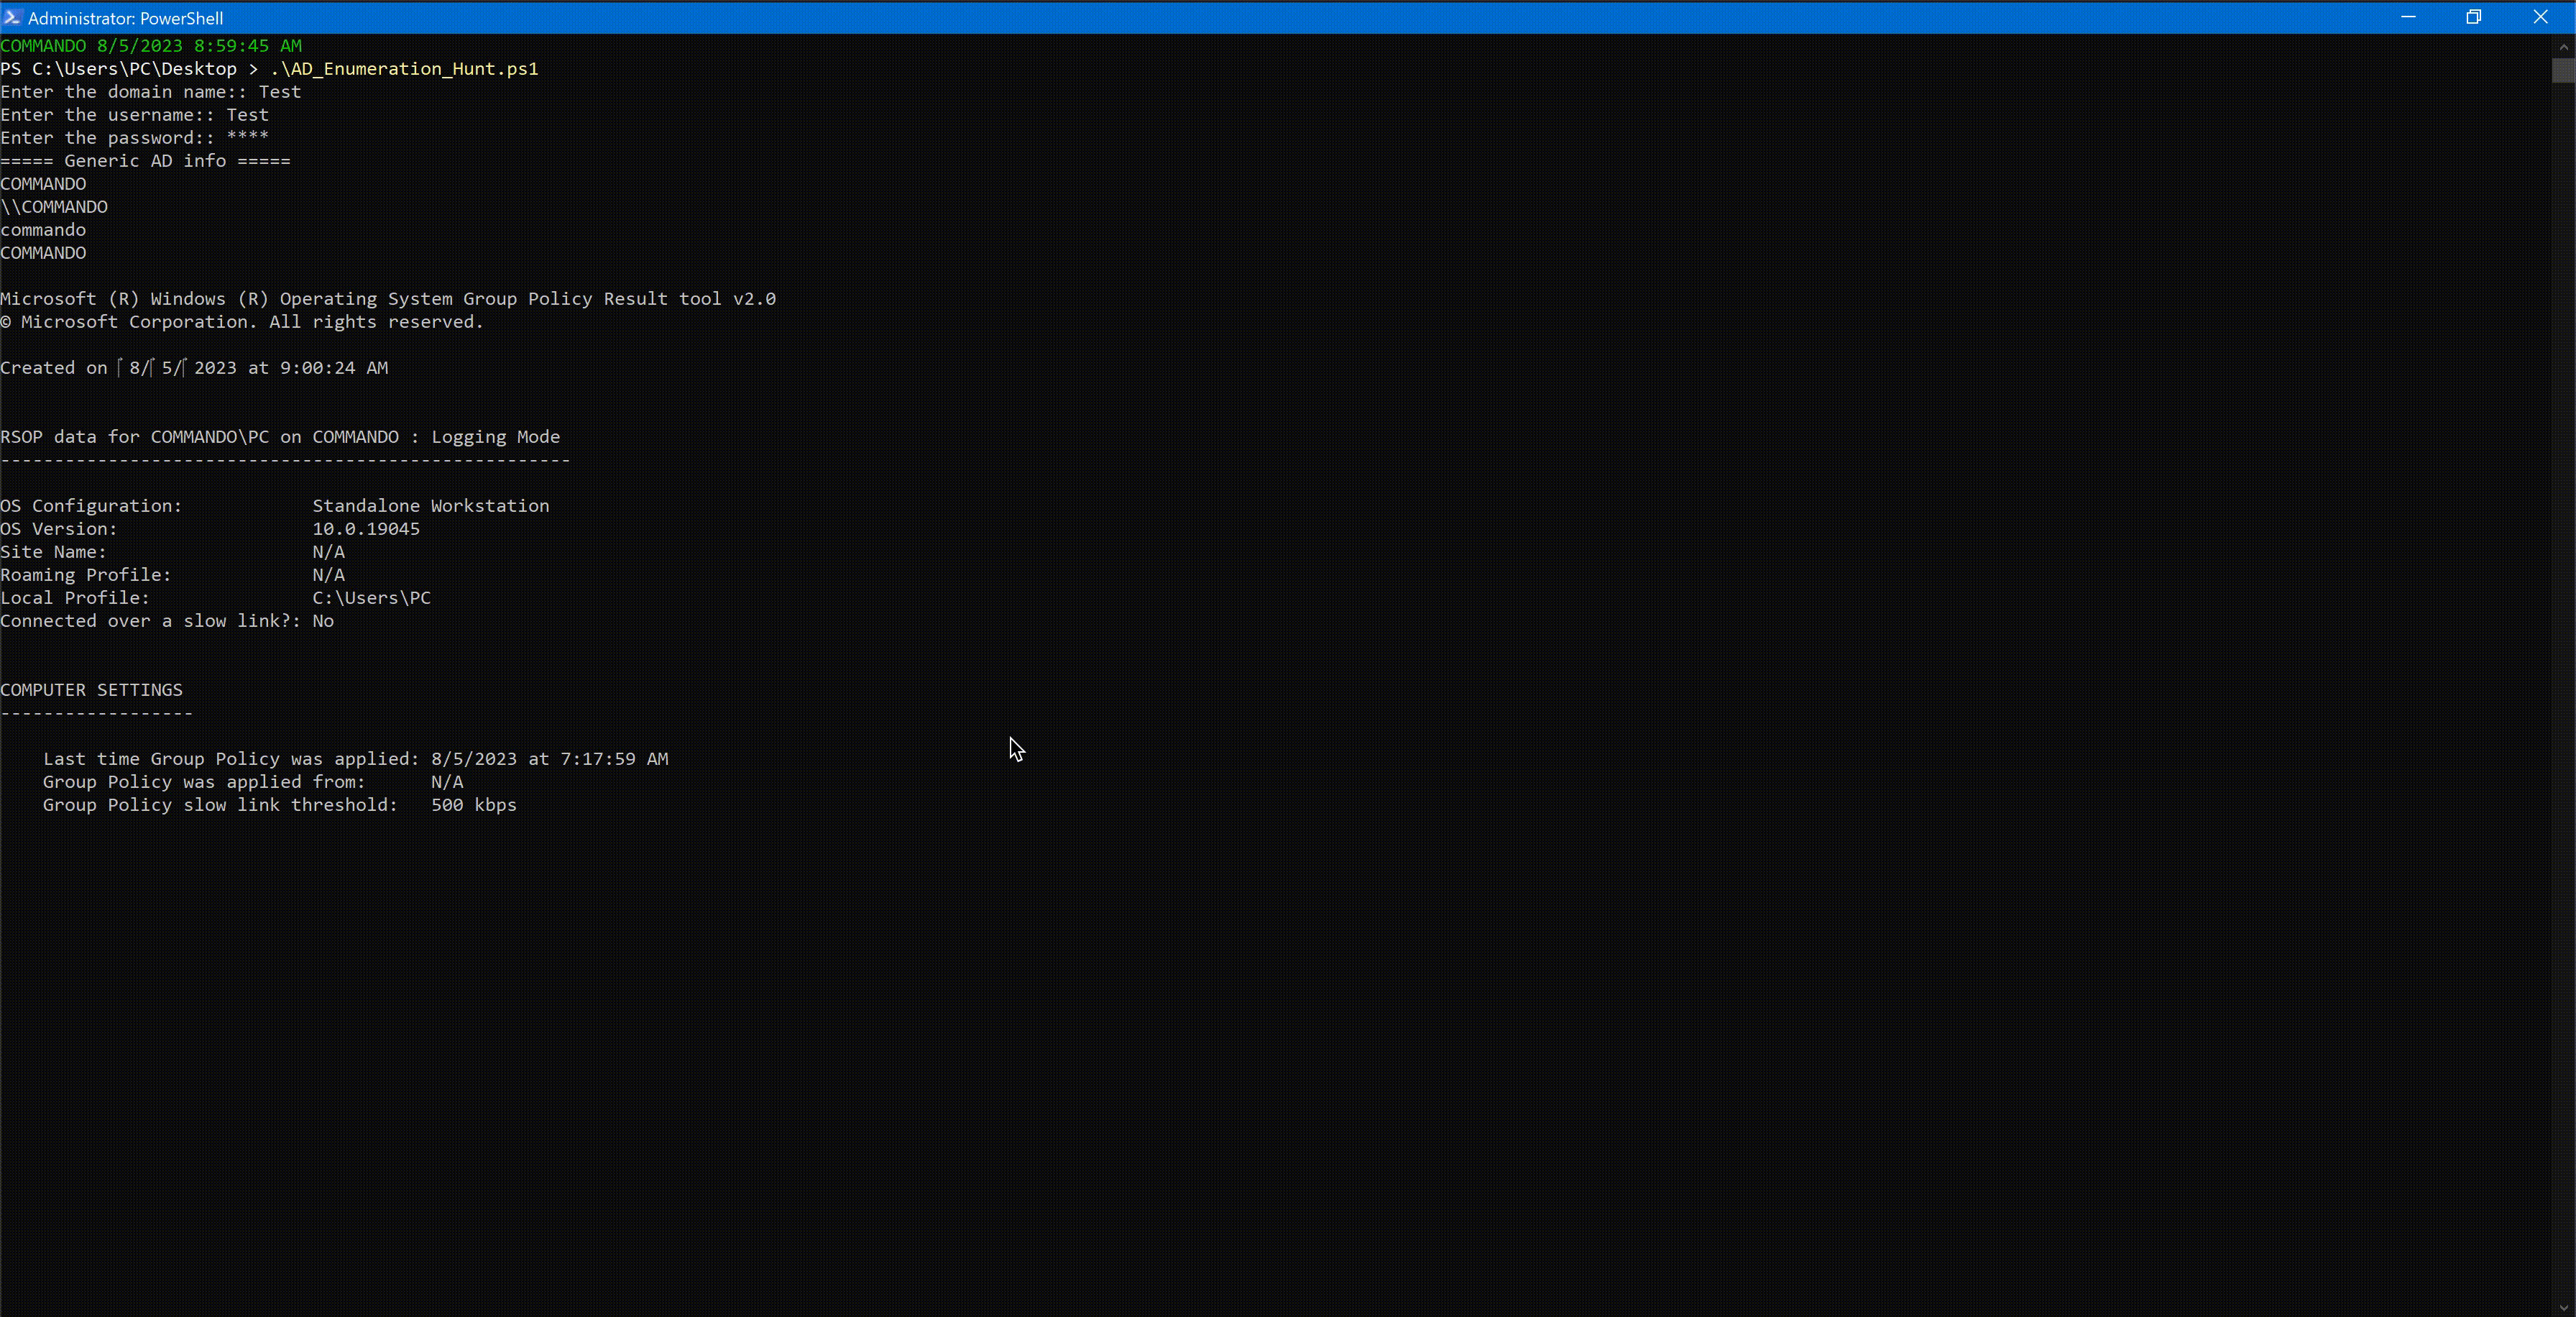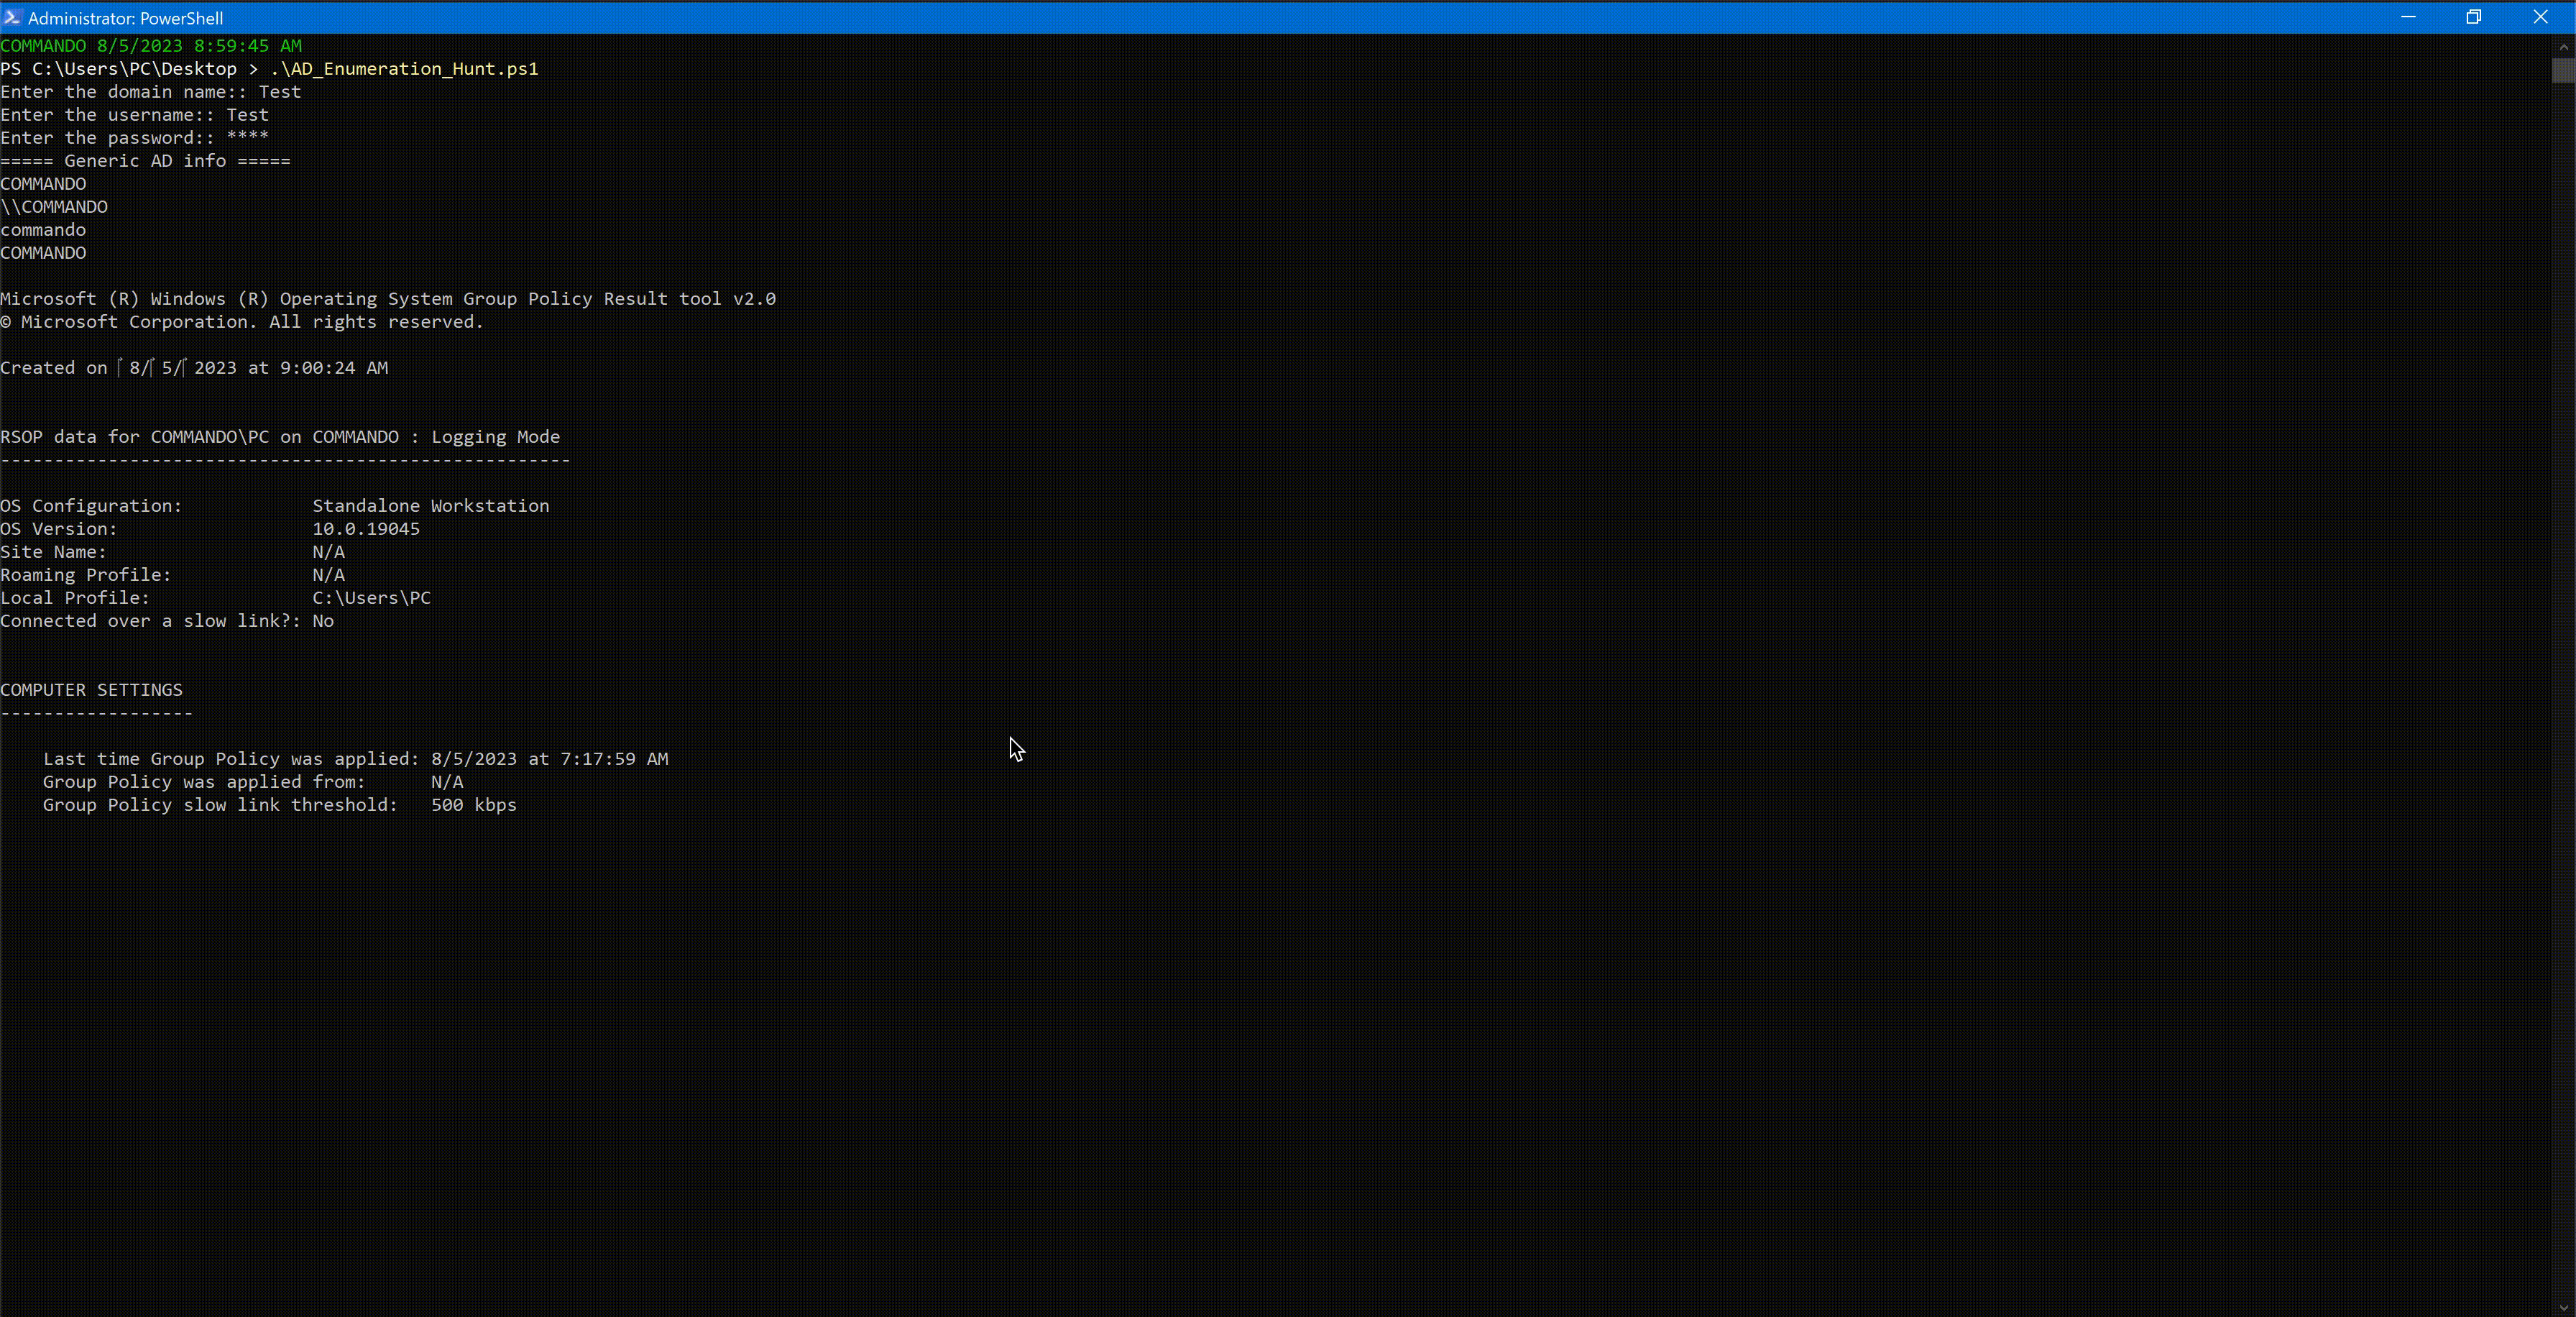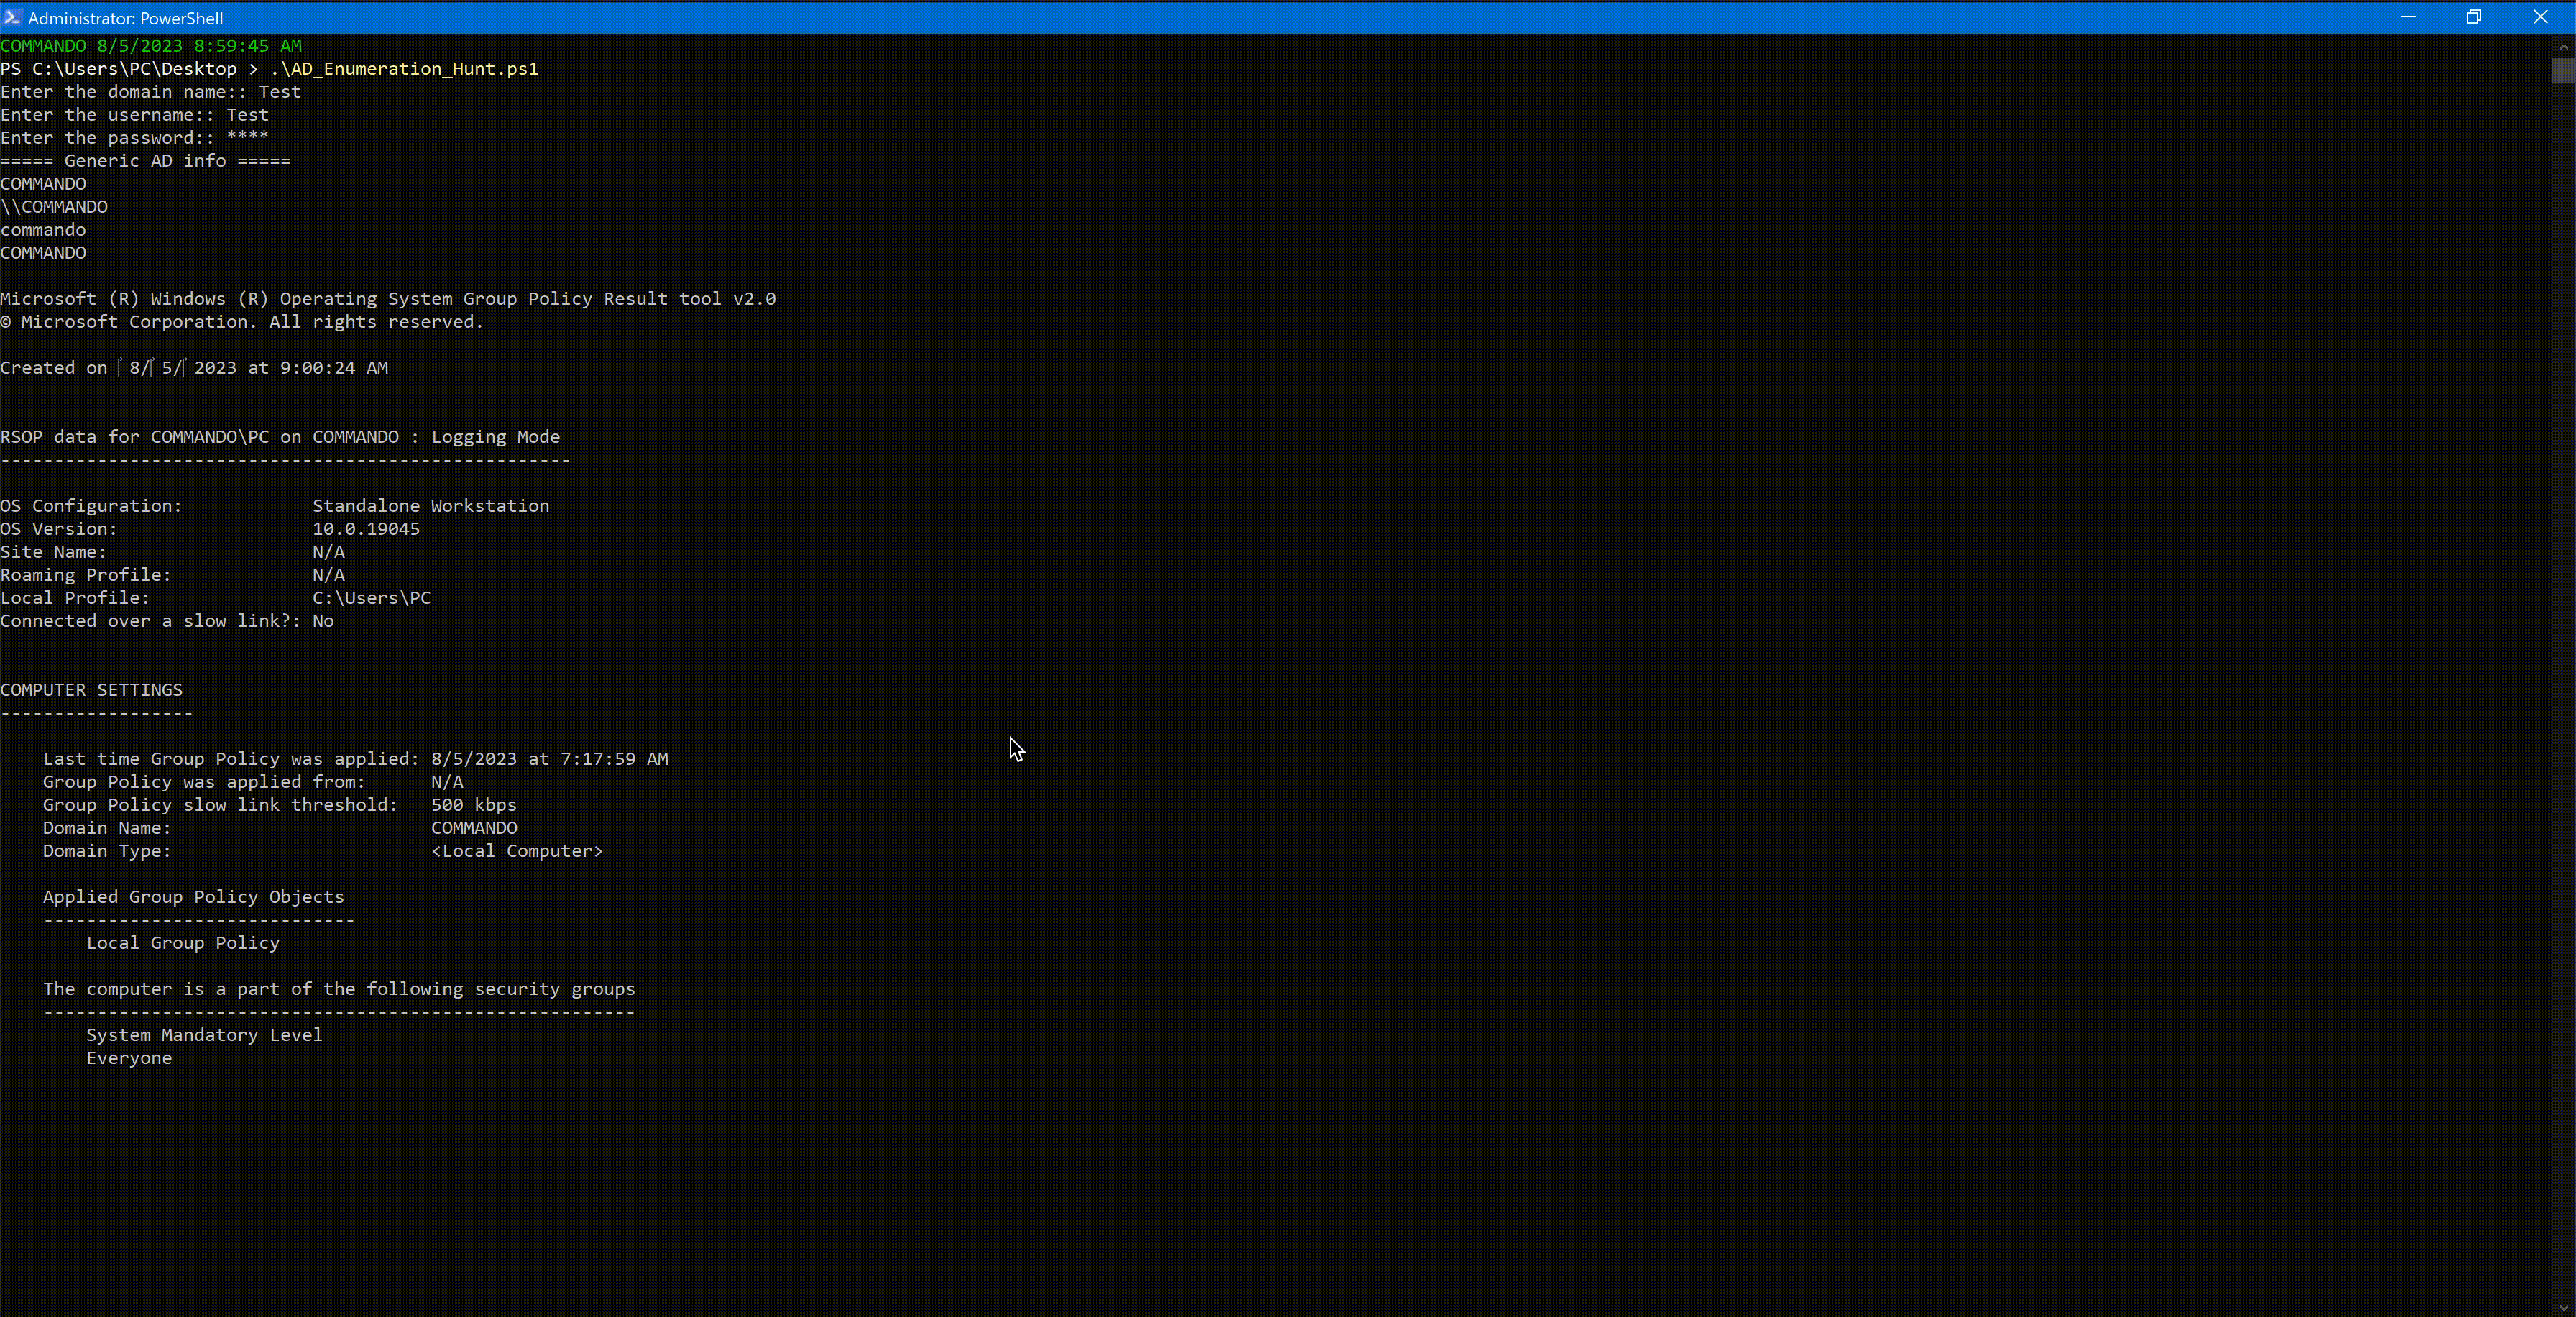 alperenugurlu/ad_enumeration_hunt
PowerShell toolkit for Active Directory penetration testing, featuring domain/user/group enumeration, trust relationship analysis, RDP configuration,…
 praetorian-inc/wasmforge
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
 portbuster1337/atlas
Cross-platform network execution toolkit (SMB/Kerberos/WMI/LDAP/DCSync) built on TrustedSec's Titanis - NetExec-style workflow in C#