NimSyscallPacker
Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…

Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…

CVE-2025-49144 PoC for security researchers to test and try.

Simple POC library to execute arbitrary calls proxying them via NdrServerCall2 or similar

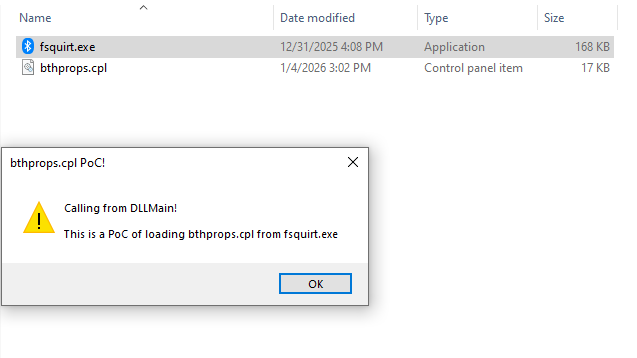
PoC for generating bthprops.cpl module designed to be loaded by Fsquirt.exe LOLBin

My experiments in weaponizing Nim (https://nim-lang.org/)

Comprehensive analysis and proof-of-concept for CVE-2025-6218 - WinRAR path traversal RCE vulnerability affecting versions 7.11 and earlier

7-Zip through 21.07 on Windows allows privilege escalation and command execution when a file with the .7z extension is dragged to the Help>Contents…

CVE-2022-25943

Proof-of-concept exploit for CVE-2026-0828, a BYOVD vulnerability in Safetica ProcessMonitorDriver.sys allowing unprivileged termination of…

A Linux kernel rootkit in Rust using a custom made type-2 hypervisor, eBPF XDP and TC programs

CVE-2021-3493 OverlayFS privilege escalation exploit framework with advanced red team features. Includes persistence mechanisms, post-exploitation…

Proof-of-concept for CVE-2024-37726: local privilege escalation in MSI Center via arbitrary file overwrite using symlink/junction attacks and OpLock…

KERUI K259 5MP Wi-Fi (Tuya Smart Security Camera) contains a code execution vulnerability

Proof-of-concept exploit for CVE-2024-31771 demonstrating arbitrary file write in TotalAV via symbolic link attack, enabling DLL planting and SYSTEM…

RustyWater represents the main payload and the backbone of the entire adversarial operation in Static Kitten group attacks.

PoC for CVE-2026-58635: Windows Narrator Braille Local Privilege Escalation

Local Privilege Escalation in HP Support Assistant

This tool demonstrates the application of fundamental physics discoveries to cybersecurity.