
CVE-2023-41898_Lab
 lazybear8372/cve-2023-41898_lab
Walk through CVE-2023-41898: exploit an unvalidated deep link in Home Assistant Android to load arbitrary URLs in a privileged WebView and leak a…
android-securityeducationlabs-practice+2
lazybear8372/cve-2023-41898_labWalk through CVE-2023-41898: exploit an unvalidated deep link in Home Assistant Android to load arbitrary URLs in a privileged WebView and leak a…
 chrisneagu/ftc-skystone-dark-angels-romania-2020
NOTICE This repository contains the public FTC SDK for the SKYSTONE (2019-2020) competition season. If you are looking for the current season's FTC…
 zinja-coder/damn-vulnerable-android-components
An intentionally vulnerable Android Application to demonstrate various vulnerabilities that airses in Android Components.
 nagendrapittu/cve-2021-521-exploit
Lab Exploit (CVE-2021-521): App uses Java reflection to access Android system components, retrieving a list of all installed apps. Reflection…
 gitamans/zygoteexploitdemo
Educational demonstration of CVE-2024-31317 Zygote Injection Vulnerability on Android
 nvisium-jack-mannino/owasp-goatdroid-project
*This project is no longer maintained* OWASP GoatDroid is a fully functional and self-contained training environment for educating developers and…
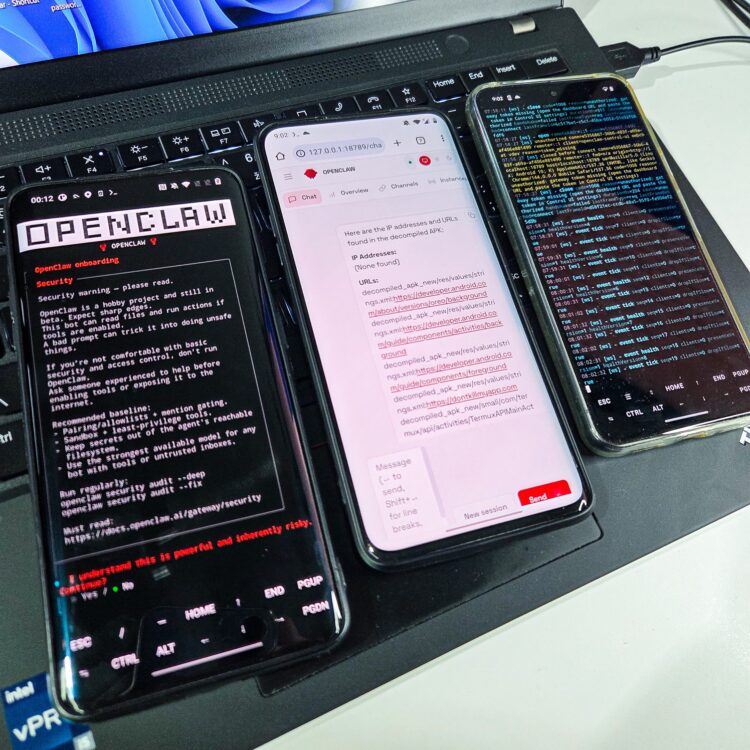 androidmalware/openclaw_termux
How to Install OpenClaw on an Android Phone and Control It via WhatsApp
 0xbinder/android-kernel-exploitation-lab
This lab guides you through setting up an environment to explore CVE-2019-2215, a critical Android kernel vulnerability in the binder subsystem.
 vinh0212/cve-2024-23700
PoC for CVE-2024-23700, Android slient privilege escalation allow to read/write contacts, SMS, calendar, call log and voicemail, make outgoing calls…
 rewanthtammana/damn-vulnerable-bank
Intentionally vulnerable Android banking app for practicing mobile security testing, featuring root detection, anti-debugging, SSL pinning, and…
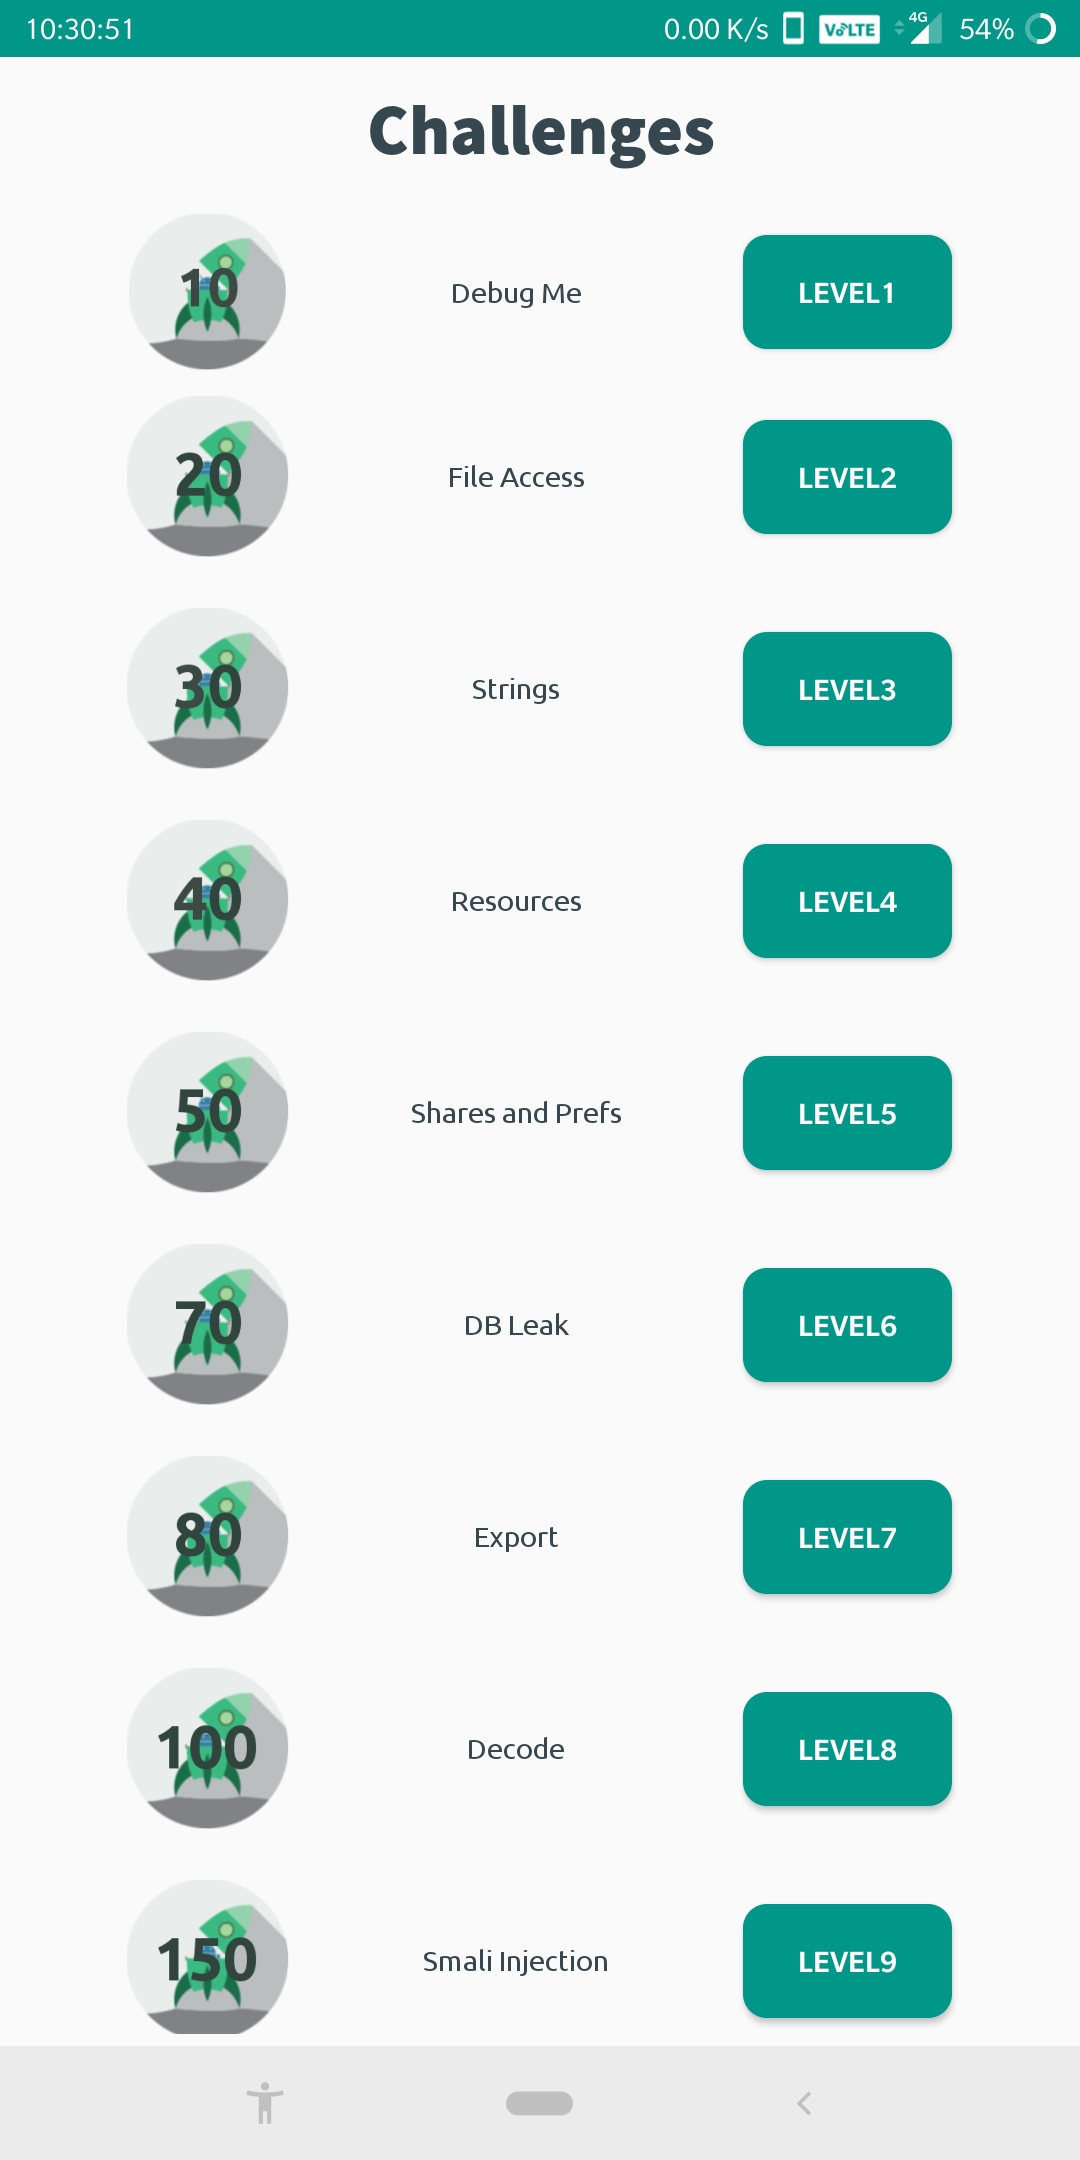 abhi-r3v0/evabs
An open source Android application that is intentionally vulnerable so as to act as a learning platform for Android application security beginners.
 v3ng4mxv1p3r/mobile-drop-device-soc-detection
End-to-end simulation of detecting a root-less Android Drop Device (Casper) using Wazuh SIEM to capture Layer 7 attacks like Shellshock…
 vaib25vicky/awesome-mobile-security
An effort to build a single place for all useful android and iOS security related stuff. All references and tools belong to their respective owners.…
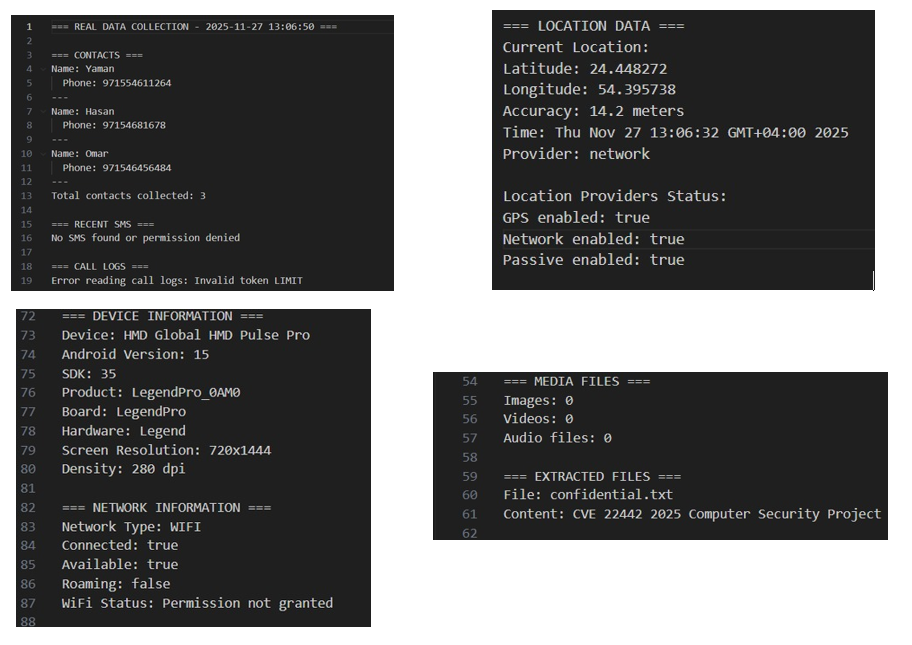 hasan-al-hussein/android-workprofile-exploit
Controlled defensive analysis of CVE-2025-22442 work-profile provisioning, policy timing, and enterprise isolation.
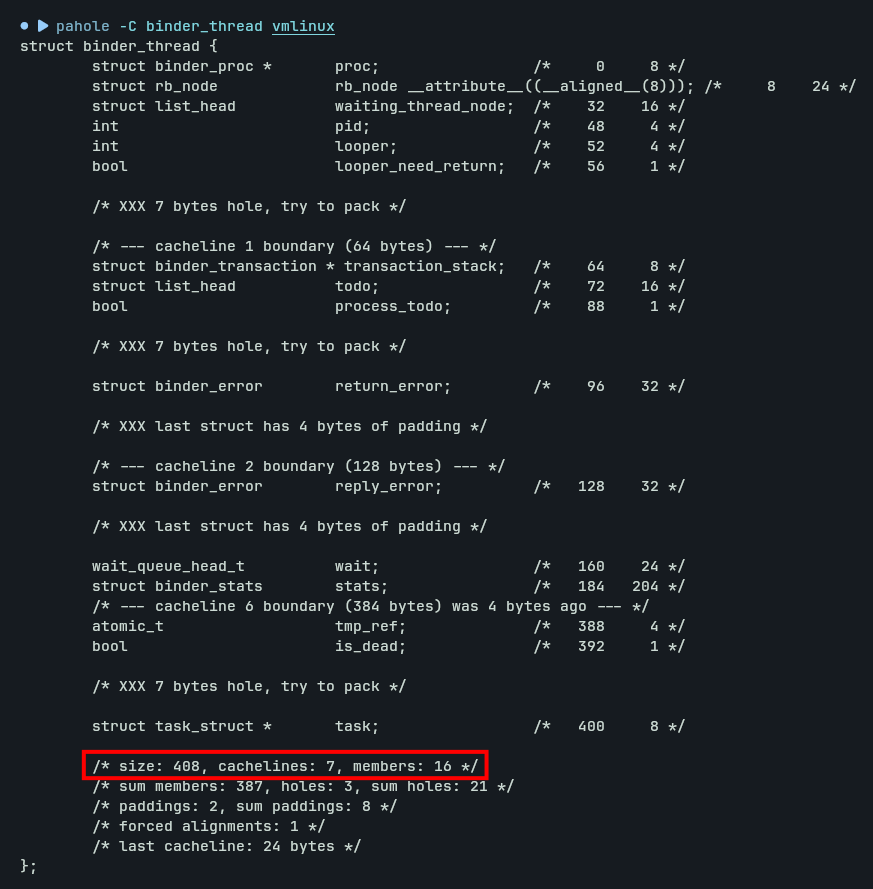 0xbinder/cve_2019_2215
Proof-of-concept LPE exploit for Android Binder UAF that uses iovec spraying and addr_limit overwrite to achieve arbitrary kernel read/write.
 cloudfuzz/android-kernel-exploitation
Hands-on workshop for learning Android kernel vulnerability analysis and exploitation, with Docker-based build environment and practical exercises.
 nictjh/threatdemos
Comprehensive Android security vulnerability demonstrations featuring CVE-2017-13156 (Janus), broadcast receiver exploitation, external storage…
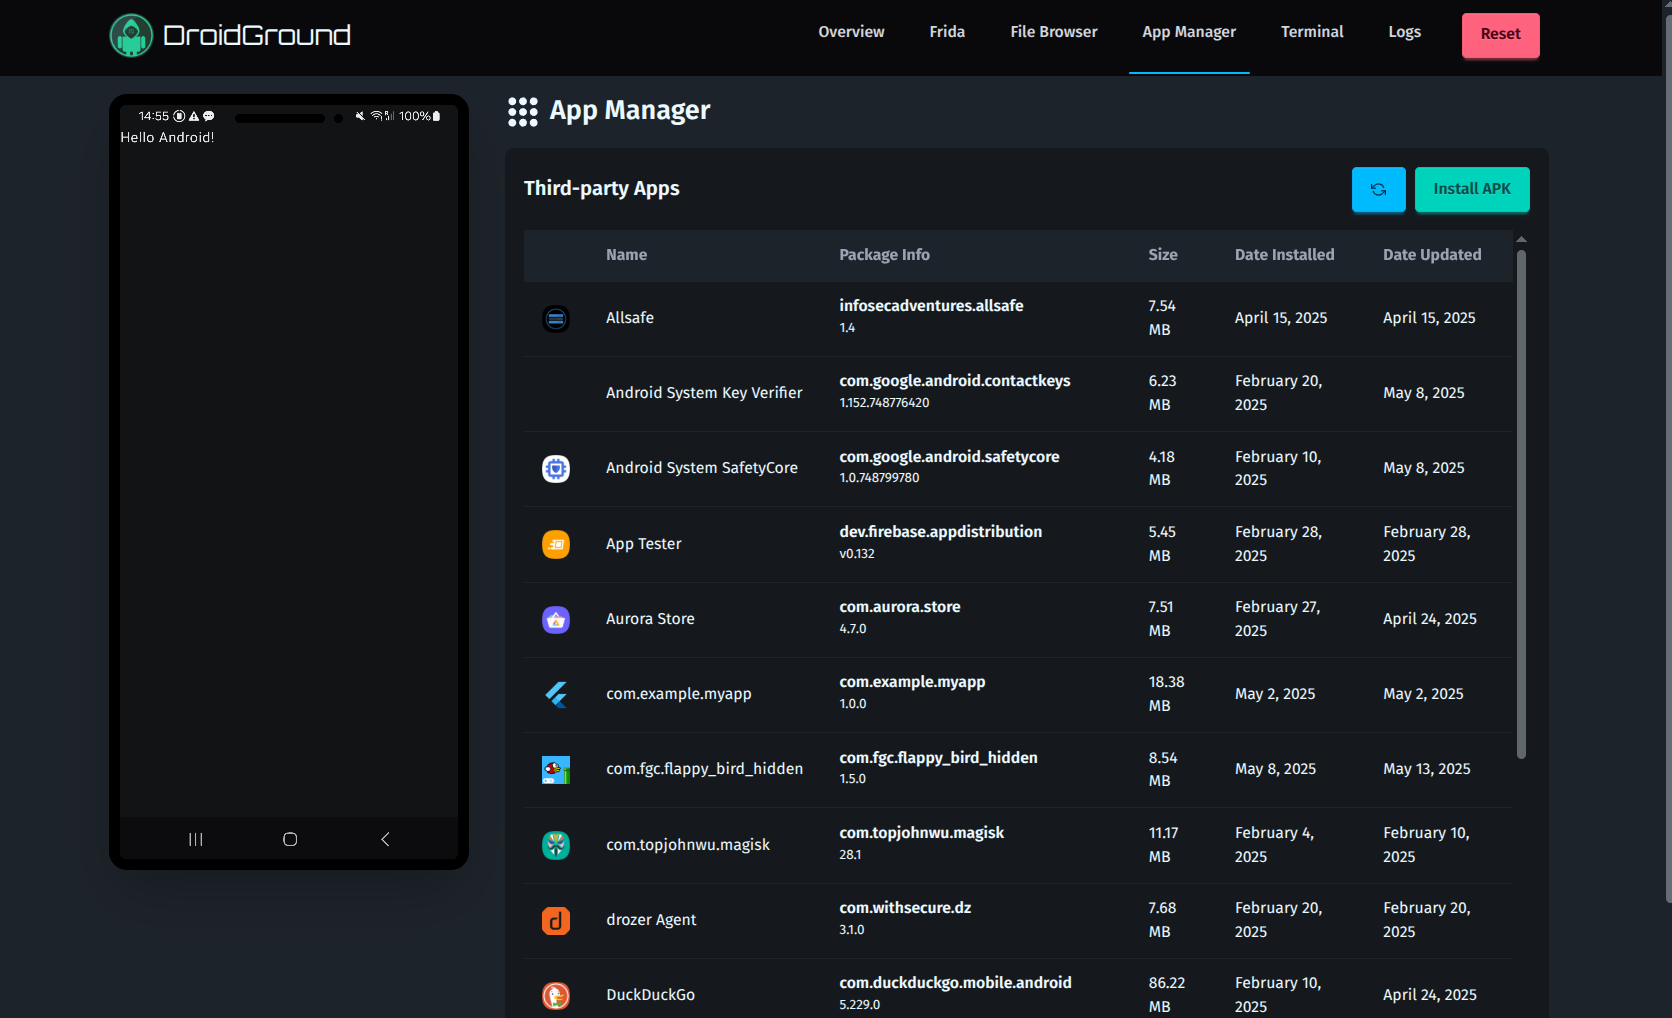 secforce/droidground
A flexible playground for Android CTF challenges.