ethical-hacking-CVE-2011-2523

Ethical Hacking Assessment | Practical vulnerability testing of vsftpd 2.3.4 backdoor (CVE-2011-2523) on Metasploitable2 using Kali Linux & Metasploit

Ethical Hacking Assessment | Practical vulnerability testing of vsftpd 2.3.4 backdoor (CVE-2011-2523) on Metasploitable2 using Kali Linux & Metasploit

build-script for CVE-2024-46507 and CVE-2024-46508

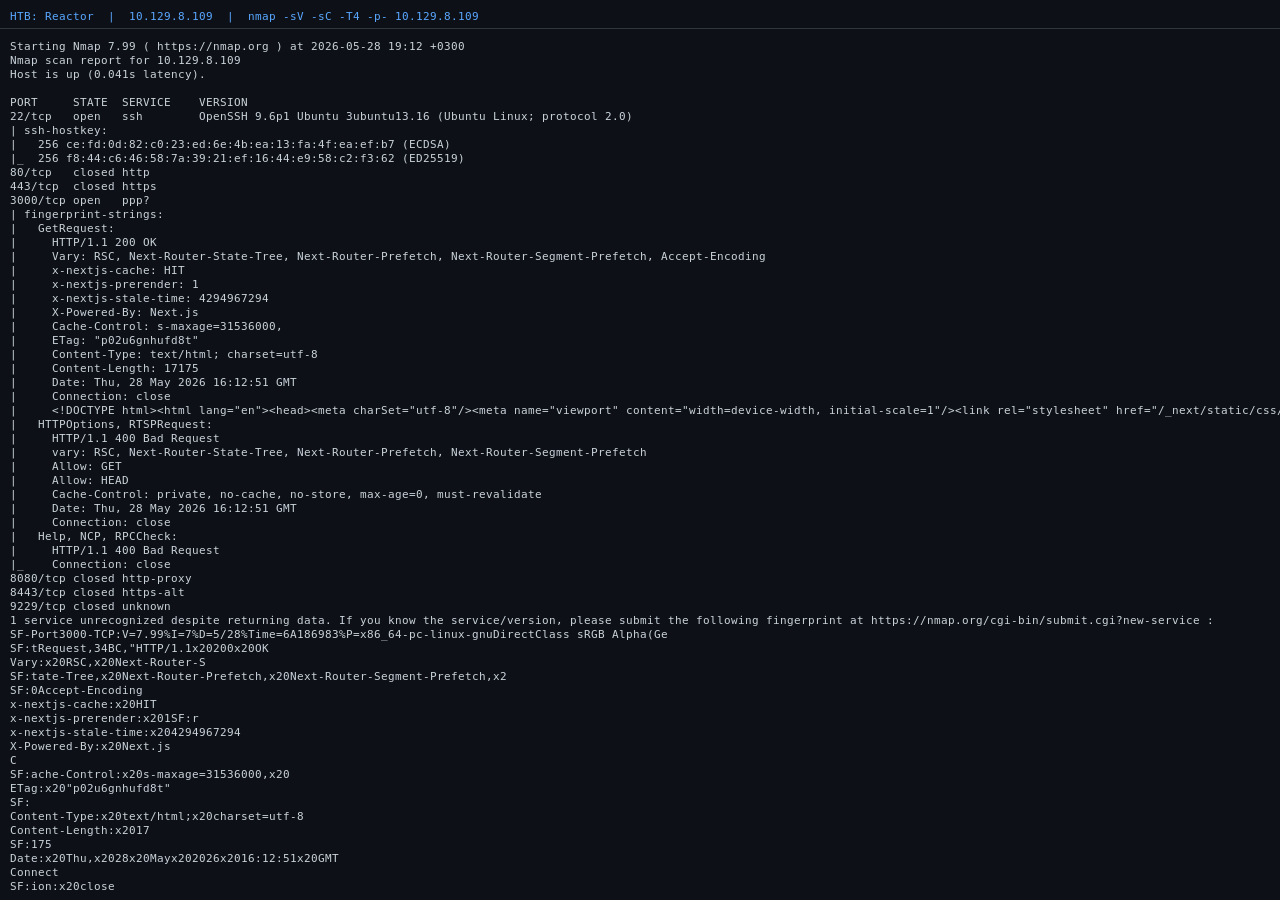
Full walkthrough of HTB's Reactor machine — exploit CVE-2025-55182 to gain a shell, then get root via an exposed Node.js debugger. Step-by-step with…

Step-by-step lab walkthrough for exploiting CVE-2018-7600 (Drupalgeddon2) RCE in Drupal 8.5.0, covering attack surface analysis, version…

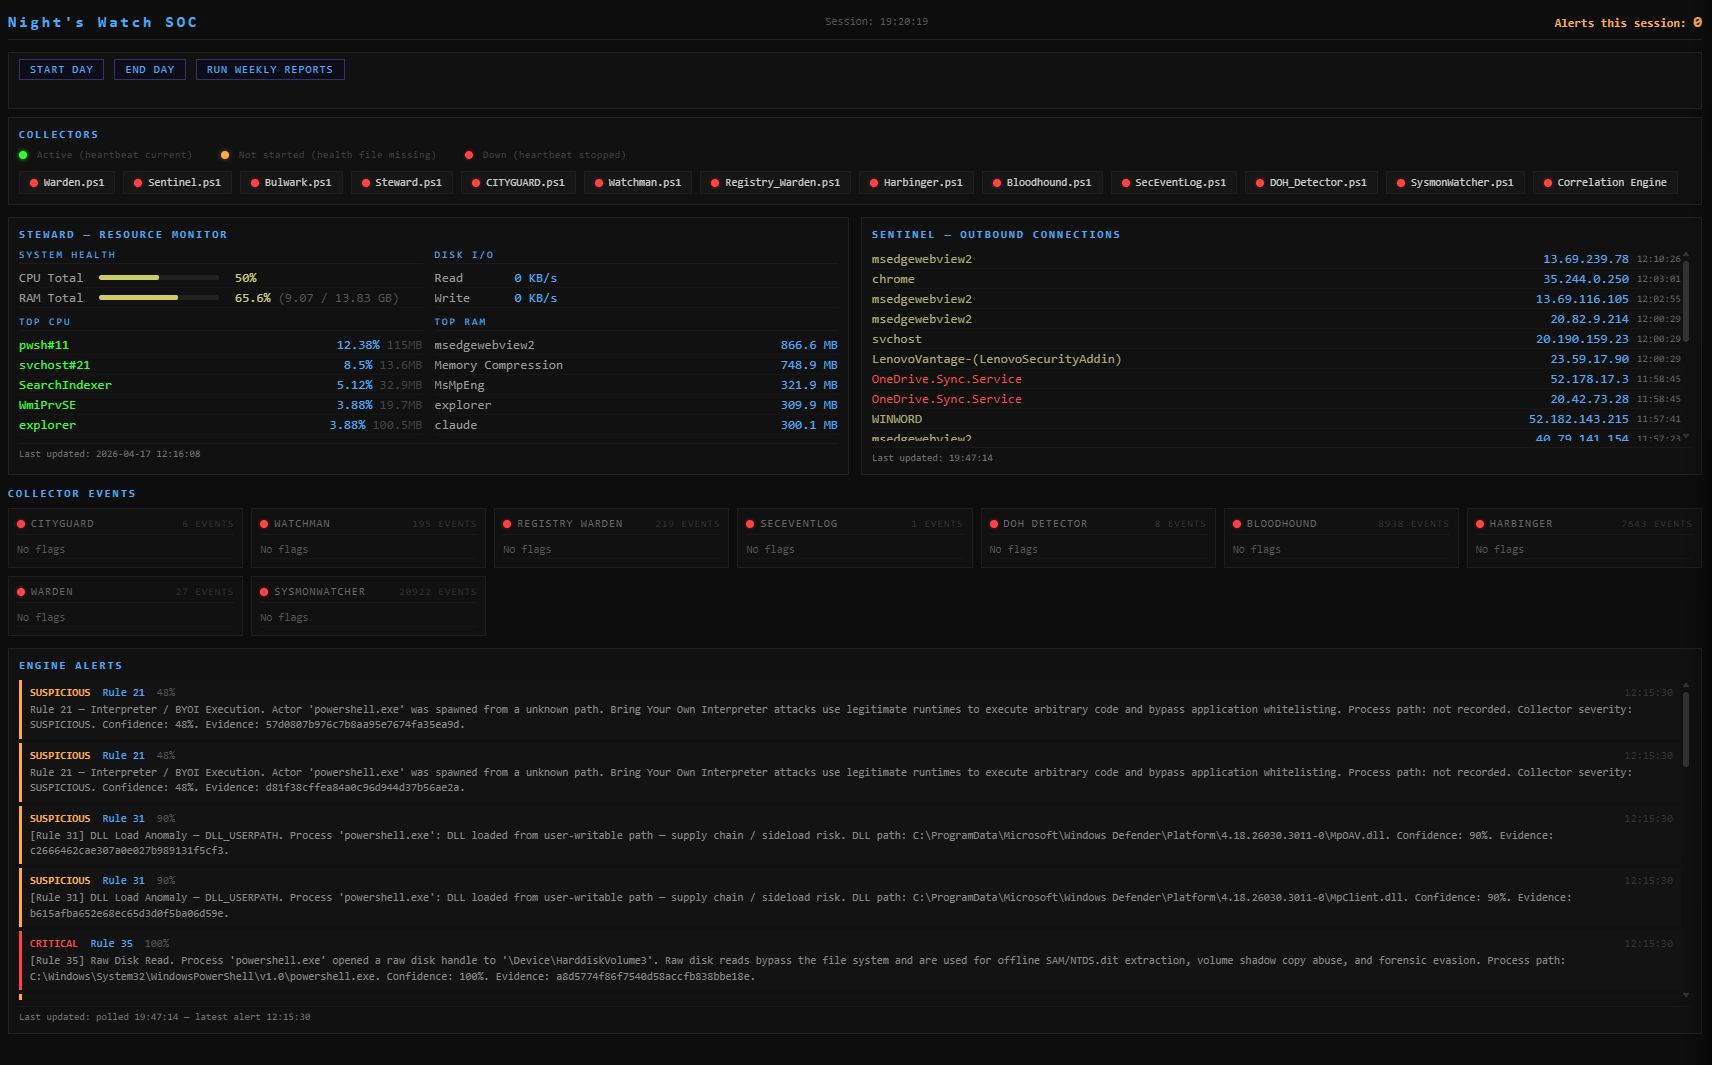
A personal Windows SOC suite built in PowerShell — monitors network connections, resource usage, scheduled tasks and power events with severity…

Auditoría de seguridad y análisis de vulnerabilidades (CVE-2014-3566 y CVE-2010-2333) en la infraestructura de red local y router residencial.

Blue-team SIEM lab: Wazuh 4.7.5 detecting 7 simulated attacks (SSH brute force, Slowloris DoS / CVE-2007-6750, web attacks) with real-time MITRE…

L1 SOC Analysis: OSINT detection and risk validation of publicly exposed MikroTik RouterOS vulnerable to RCE | Tools: Shodan, NIST NVD

Performed a live cybersecurity assessment on a university Linux server. During analysis, active attack activity was identified, including brute-force…

End-to-end simulation of detecting a root-less Android Drop Device (Casper) using Wazuh SIEM to capture Layer 7 attacks like Shellshock…

Real-World Simulation: FTP Service Exploitation (ProFTPD CVE-2015-3306)

Writeup da sala Blue do TryHackMe — exploração do EternalBlue (MS17-010/CVE-2017-0143).

CVE-2008-1930 is a critical improper authentication vulnerability affecting the core cookie integrity mechanism in WordPress version 2.5. It allows…

Test target: fresh Laravel 12 app with Livewire pinned to vulnerable 3.6.3 (CVE-2025-54068) for recon scanning

Traveller is an Easy Linux machine featuring a Joomla 4.2.7 travel booking website vulnerable to CVE-2023-23752, an unauthenticated REST API…

Python exploit class for CVE-2025-58360, an XXE vulnerability in GeoServer's GetMap function enabling arbitrary file read. Includes automated…

Exploitation of a Remote Code Execution vulnerability- (CVE-2024-7954)

A hands-on project demonstrating the setup of virtual security lab, network reconnaissance, and exploitation of CVE-2012-1823.