
dockerized-android
 cybersecsi/dockerized-android
A container-based framework to enable the integration of mobile components in security training platforms
android-securitycontainer-securityeducation+2
187
cybersecsi/dockerized-androidA container-based framework to enable the integration of mobile components in security training platforms
 owasp/mas-crackmes
The MAS Crackmes aka. UnCrackable Apps, a collection of mobile reverse engineering challenges part of the OWASP MAS project.
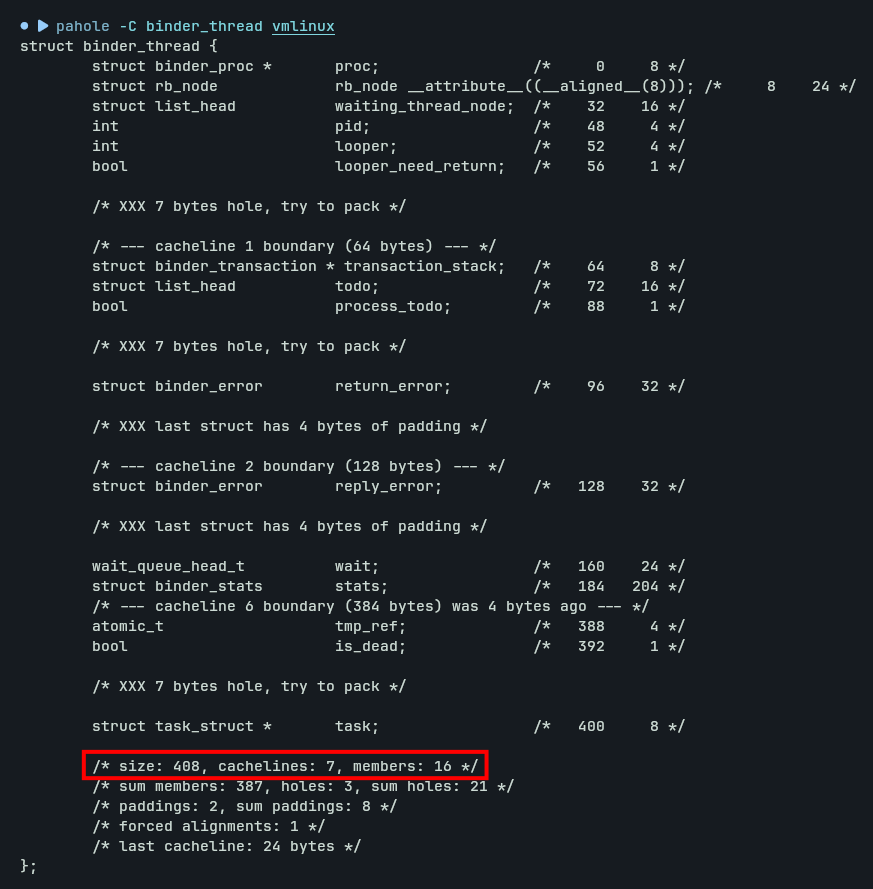 0xbinder/cve_2019_2215
Proof-of-concept LPE exploit for Android Binder UAF that uses iovec spraying and addr_limit overwrite to achieve arbitrary kernel read/write.
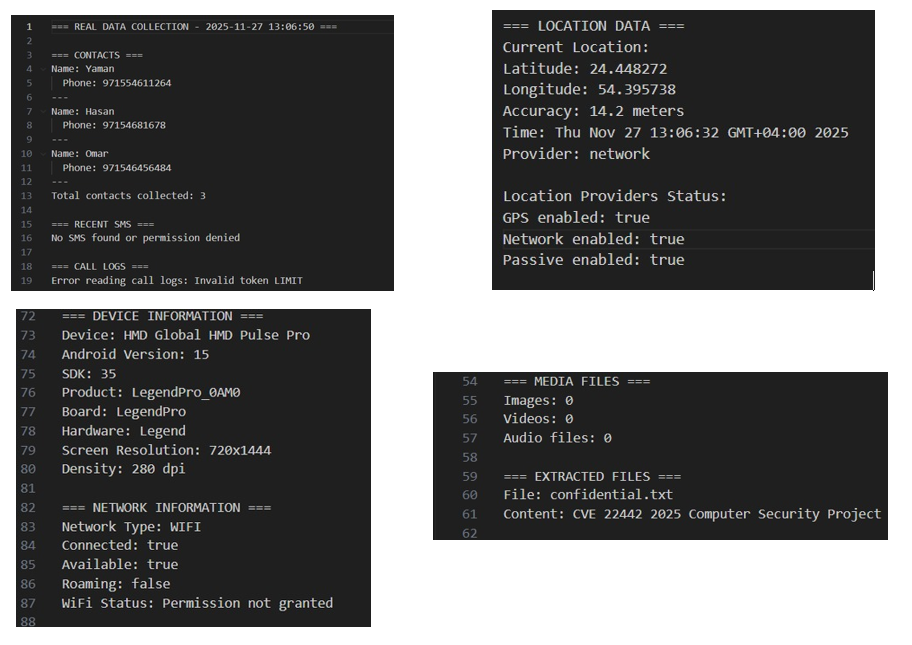 hasan-al-hussein/android-workprofile-exploit
Controlled defensive analysis of CVE-2025-22442 work-profile provisioning, policy timing, and enterprise isolation.
 nagendrapittu/cve-2021-521-exploit
Lab Exploit (CVE-2021-521): App uses Java reflection to access Android system components, retrieving a list of all installed apps. Reflection…
 brnpl/flutter-reverse-engineering-labs
Hands-on challenges for learning how to reverse engineer Flutter applications.
 mobilehackinglab/cve-2026-0047-poc
CVE-2026-0047: Missing permission check in ActivityManagerService.dumpBitmapsProto() — steal UI bitmaps from every running app with zero permissions…
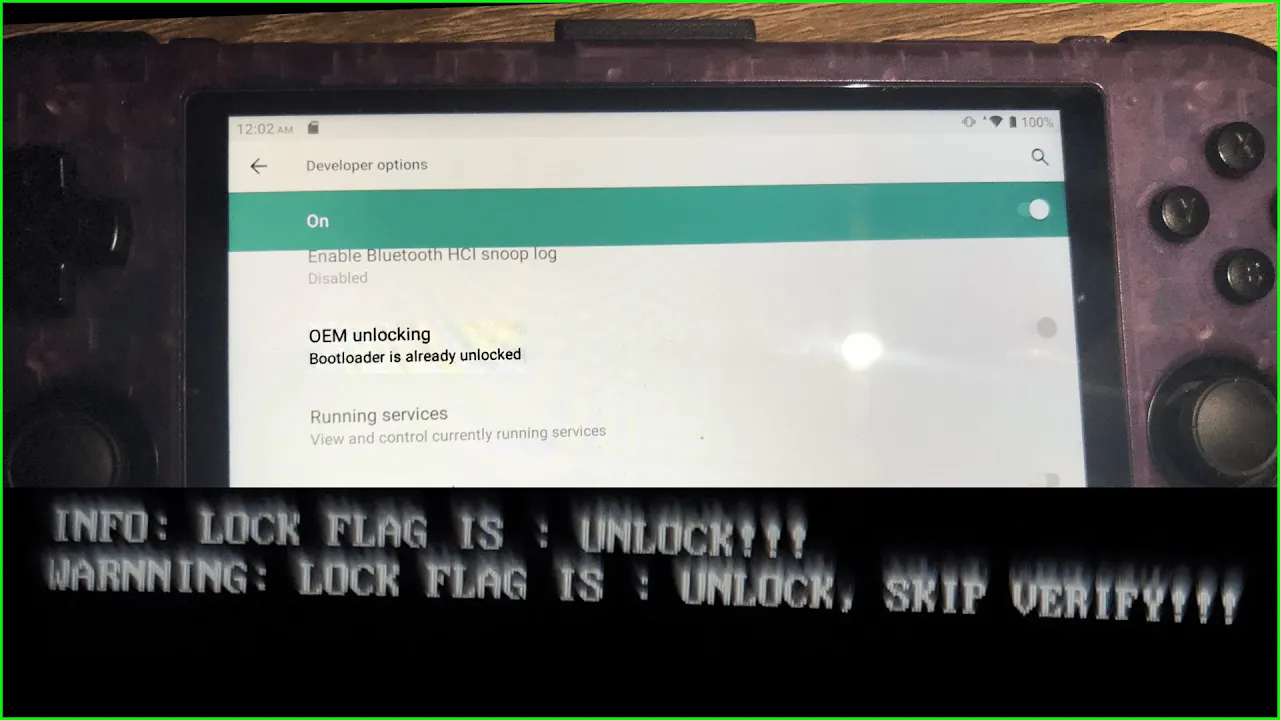 seriousattempts/bootloader_unlock_retroid_pocket_3plus
Bootloader unlock using CVE-2022-38694 for Retroid Pocket 3+
 dhmosfunk/cve-2023-25690-poc
CVE 2023 25690 Proof of concept - mod_proxy vulnerable configuration on Apache HTTP Server versions 2.4.0 - 2.4.55 leads to HTTP Request Smuggling…
 prot0tw/keycloak_cve-2026-18963_poc
This repo is poc of cve-2026-18963. Please use it on legal products (lab, local,...).
 oocyginxoo/cve-2023-25690-poc
CVE 2023 25690 Proof of concept - mod_proxy vulnerable configuration on Apache HTTP Server versions 2.4.0 - 2.4.55 leads to HTTP Request Smuggling…
 chathura123git/ethical-hacking-cve-2011-2523
Ethical Hacking Assessment | Practical vulnerability testing of vsftpd 2.3.4 backdoor (CVE-2011-2523) on Metasploitable2 using Kali Linux & Metasploit
 mrintern/thm_steelmountain_cve-2014-6287
a python3 version of the exploit written for CVE-2014-6287. Useful for completing the "Steel Mountain" room on TryHackMe.com without the use of…
 p0dalirius/awesome-rce-techniques
Awesome list of step by step techniques to achieve Remote Code Execution on various apps!
 mikivirus0/sudoinjection
Sudo Local Privilege Escalation CVE-2025-32463 (Best For Cases Where the shell is not stable to spawn a new root shell)
 th3xace/sudo_killer
A tool designed to exploit a privilege escalation vulnerability in the sudo program on Unix-like systems. It takes advantage of a specific…
 rufflabs/ludus_crushftp_cve-2025-31161
Ansible role deploying a vulnerable CrushFTP 10.8.0 instance on Windows for authorized penetration testing of CVE-2025-31161 authentication bypass.
 lavanya2085/solar-exploiting-log4j
This repository provides a detailed walkthrough of the *Solar Exploiting Log4j room* on TryHackMe, focusing on exploiting the critical Log4Shell…