

cve-2021-42013
 bananoname/cve-2021-42013
Python script to detect and exploit path traversal and remote code execution in Apache 2.4.50 (CVE-2021-42013), with bulk scanning and a Docker lab…
educationexploitationlabs-practice+3
1
bananoname/cve-2021-42013Python script to detect and exploit path traversal and remote code execution in Apache 2.4.50 (CVE-2021-42013), with bulk scanning and a Docker lab…
 pswalia2u/cve-2020-7246
Lab environment and exploit script for CVE-2020-7246, a PHP code injection vulnerability in qdPM 9.1. Includes Docker setup and Python2-based…
 cybersensei-eh/hackviser_labs_cve-2015-3306
This is a customized script to help solve the lab on remote code execution under the CVE-2015-3306 lab.
 jas9reet/cve-2021-42013-lab
Docker-based lab environment for exploiting Apache HTTP Server 2.4.50 path traversal and RCE vulnerability (CVE-2021-42013) with automated exploit…
 flame-11/cve-2025-54068-livewire
Reproducible Docker-based lab for CVE-2025-54068 in Livewire v3.6.3, including a safe PoC exploit chain script for educational vulnerability analysis.
 caihuar/joomla-cve-2015-8562
Docker-based environment for testing Joomla RCE (CVE-2015-8562) with an included Python exploit script for command execution and reverse shells.
 80ottanta80/cve-2024-32019-poc
Bash script for Privilege Escalation via "ndsudo" (Netdata Local Exploit)
 gvmyz/cve-2012-2982_python
PoC Python script as an exercice from tryhackme.
 trax69/cve-2025-55182-poc
Proof of Concept for CVE-2025-55182 ("React2Shell"). A fully dockerized environment demonstrating Remote Code Execution (RCE) via insecure…
 chernandez321/cve-2025-9074-docker-escape
Este script es para uso educativo y en entornos autorizados como HackTheBox. El uso contra sistemas sin permiso explícito es ilegal.
 joker-wiggin/cve-2025-58360-geoserver-xxe
Docker-based lab demonstrating CVE-2025-58360, a critical unauthenticated XXE injection in GeoServer WMS/OWS services. Includes exploit script for…
 eagle-nett/react2shell-poc-cve-2025-55182
Proof-of-concept exploit for CVE-2025-55182 (React2Shell) RCE vulnerability in React Server Components. Includes a scanner for vulnerable hosts and a…
 danielhallbro/cve-2022-36804-bitbucket-rce-analysis
Full-chain reproduction of CVE-2022-36804 (Bitbucket RCE). Includes a Dockerized laboratory, pspy64 monitoring for null-byte injection verification,…
 joaovicdev/exploit-cve-2021-44228
Docker-based educational lab demonstrating Log4Shell (CVE-2021-44228) RCE exploitation with a vulnerable Java application, LDAP redirector, and…
 flame-11/cve-2017-20192-formidable-forms
Reproducible Docker lab for CVE-2017-20192 (Formidable Forms < 2.05.03 stored XSS) with automated PoC script for unauthenticated exploitation and…
 experience-rookie/struts-s2-052-deserialization-rce-lab
Proof-of-Concept exploit for Apache Struts S2-052 (CVE-2017-9805) XML Deserialization Remote Code Execution. Created while solving the INE eWPTX…
 isabbii/poc-apache-cve-2021-41773-infrastructure-lab
Docker-based lab for Apache CVE-2021-41773 path traversal and RCE exploitation with Python exploit script, demonstrating vulnerability analysis and…
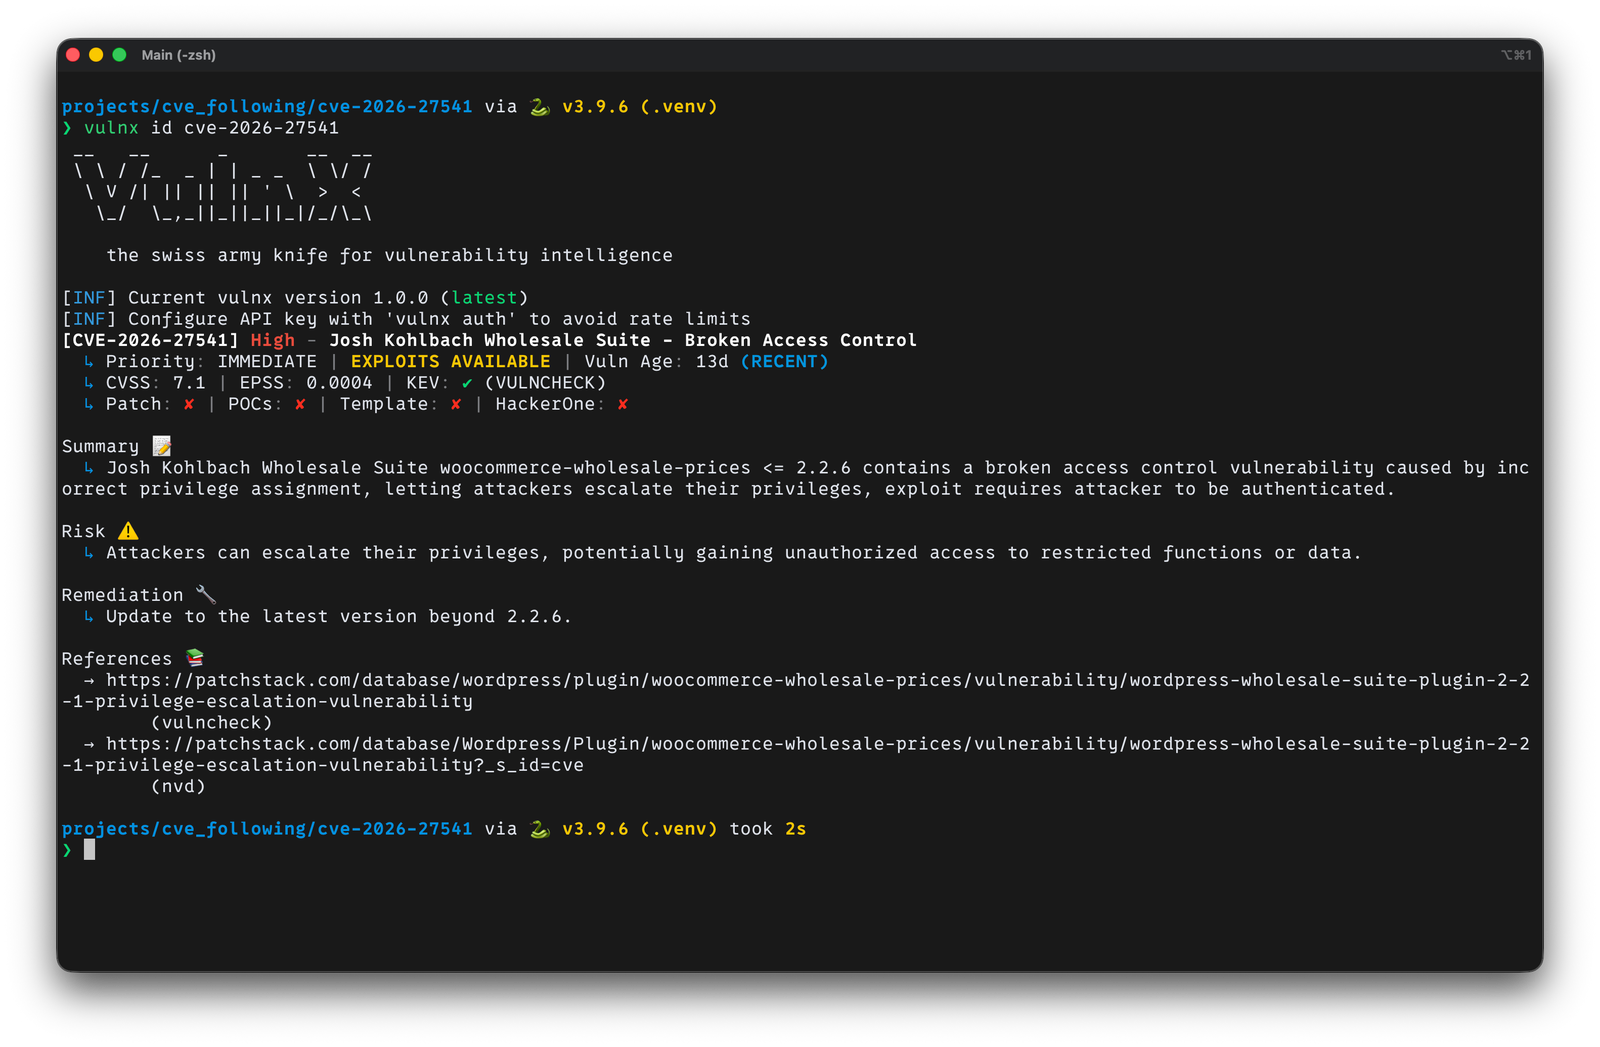 rootdirective-sec/cve-2026-27541-analysis-lab
Docker lab for reproducing CVE-2026-27541, an authenticated privilege escalation in WooCommerce Wholesale Prices. Compares vulnerable and patched…