CVE-2024-10924-Wordpress-Docker

Dockerized exploit environment for CVE-2024-10924, an authentication bypass in WordPress Really Simple Security plugin (versions 9.0.0-9.1.1.1)…

Dockerized exploit environment for CVE-2024-10924, an authentication bypass in WordPress Really Simple Security plugin (versions 9.0.0-9.1.1.1)…

Proof Of Concept for the CVE-2016-10033 (PHPMailer)

WARNING: This is a vulnerable application to test the exploit for the Cacti command injection (CVE-2023-39362). Run it at your own risk!

Docker-based lab environment for exploiting Shellshock (CVE-2014-6271) via CGI scripts, demonstrating remote command injection through crafted HTTP…

Challenge based on CVE-2021-22204 where users send a malicious file to a web application to gain RCE

DHCP exploitation with DynoRoot (CVE-2018-1111)

CVE-2017-0089 Learn more at National Vulnerability Database (NVD) • CVSS Severity Rating • Fix Information • Vulnerable Software Versions • SCAP…

An intentionally vulnerable (CVE-2017-8046) SrpingData REST appl with Swagger Support for pentesting purposes

reproducing an old istio bug

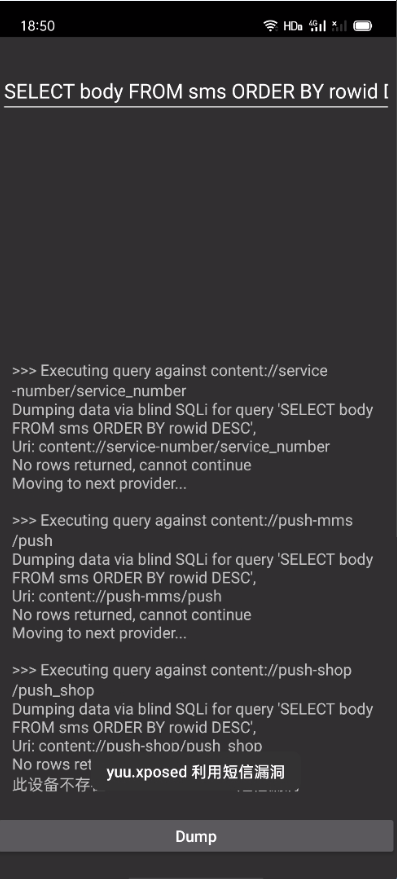
ColorOS短信漏洞,以及用户自救方案

Stereotyped Challenges (2014~2023)

lazy way to create CVE-2023-38831 winrar file for testing

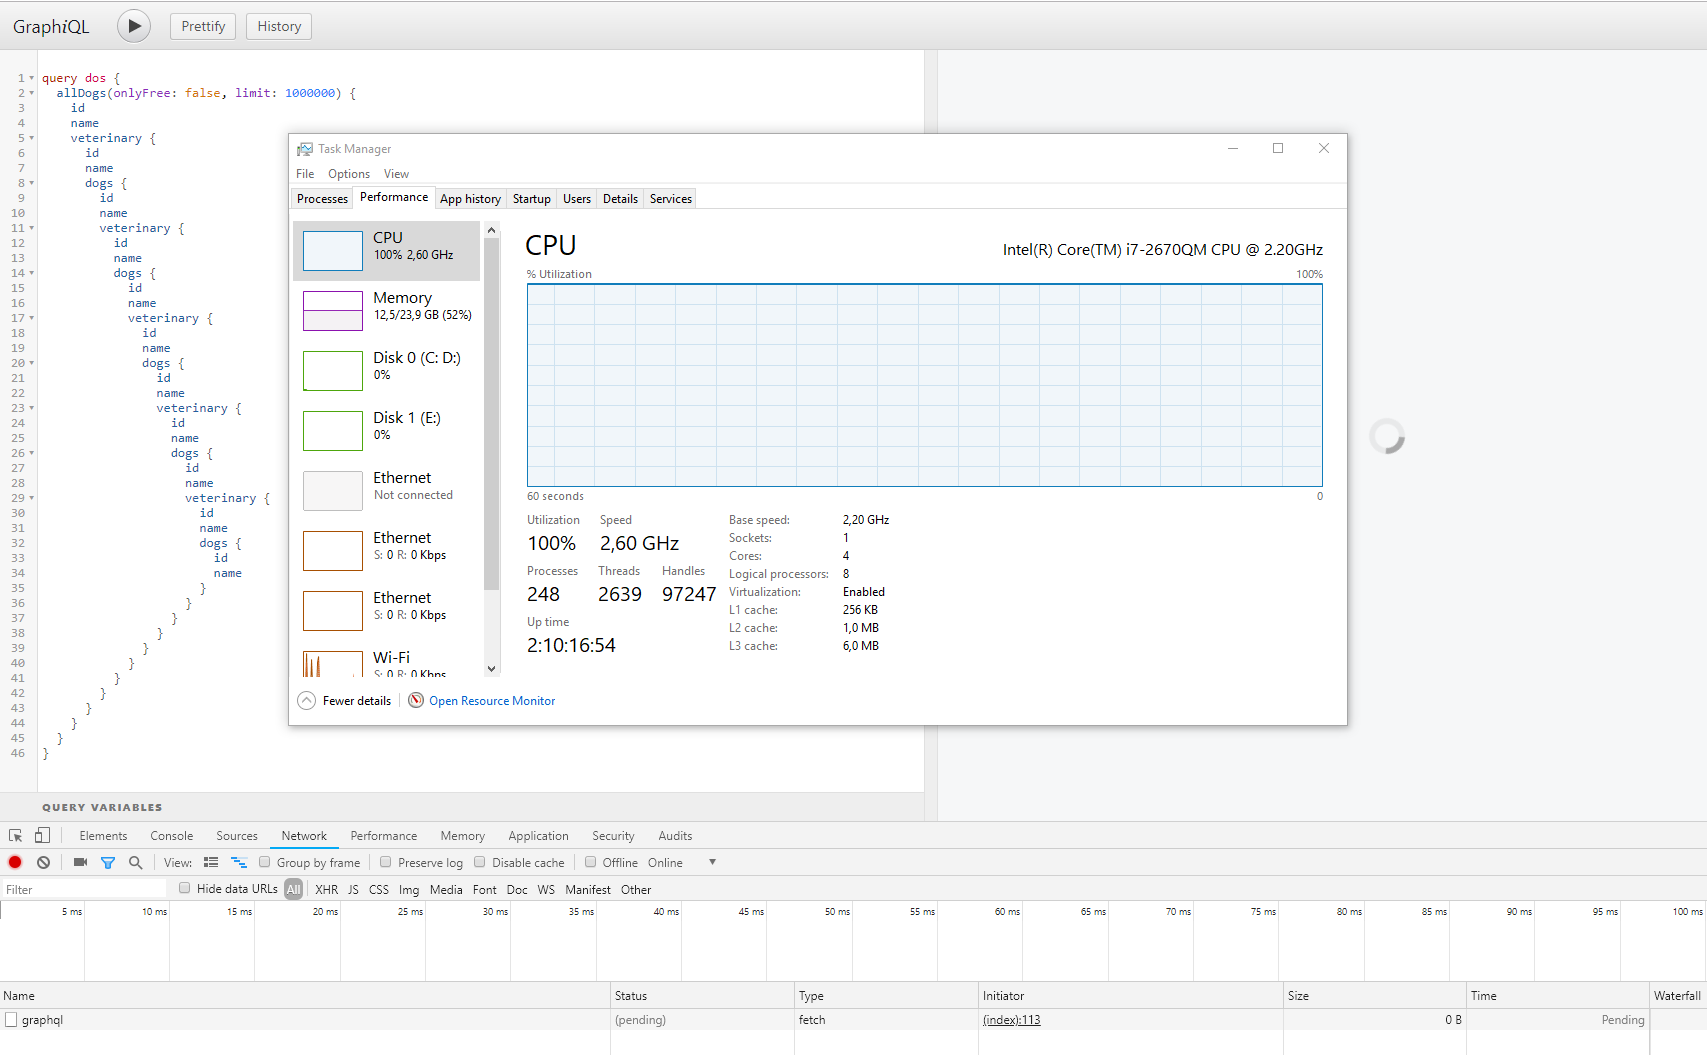
Research on GraphQL from an AppSec point of view.

Scanner for CVE-2024-23897 - Jenkins

Intentionally vulnerable PHP/MariaDB web application for practicing common web security vulnerabilities across multiple difficulty levels in a legal,…

Building 70 Projects ranging from beginner to advanced so anyone can — learn from, build upon, use as a reference, or even copy directly. Owned by my…

Reproduce DeFi hacked incidents using Foundry.

A repository for learning various heap exploitation techniques.