

awesome-connected-things-sec
 v33ru/awesome-connected-things-sec
A Curated list of Security Resources for all connected things
ctfcurated-resourceseducation+9
3.6k
v33ru/awesome-connected-things-secA Curated list of Security Resources for all connected things
 secforce/droidground
A flexible playground for Android CTF challenges.
 b4sith-sec/gu3ssweak
Deliberately vulnerable Android app for mobile security research and bug bounty practice - OWASP Mobile Top 10
 owasp/android-security-masterclass
OWASP hands-on Android security training lab with 78 MASVS/MASTG modules pairing vulnerable, secure, and attacker apps to demonstrate mobile…
 brnpl/flutter-reverse-engineering-labs
Hands-on challenges for learning how to reverse engineer Flutter applications.
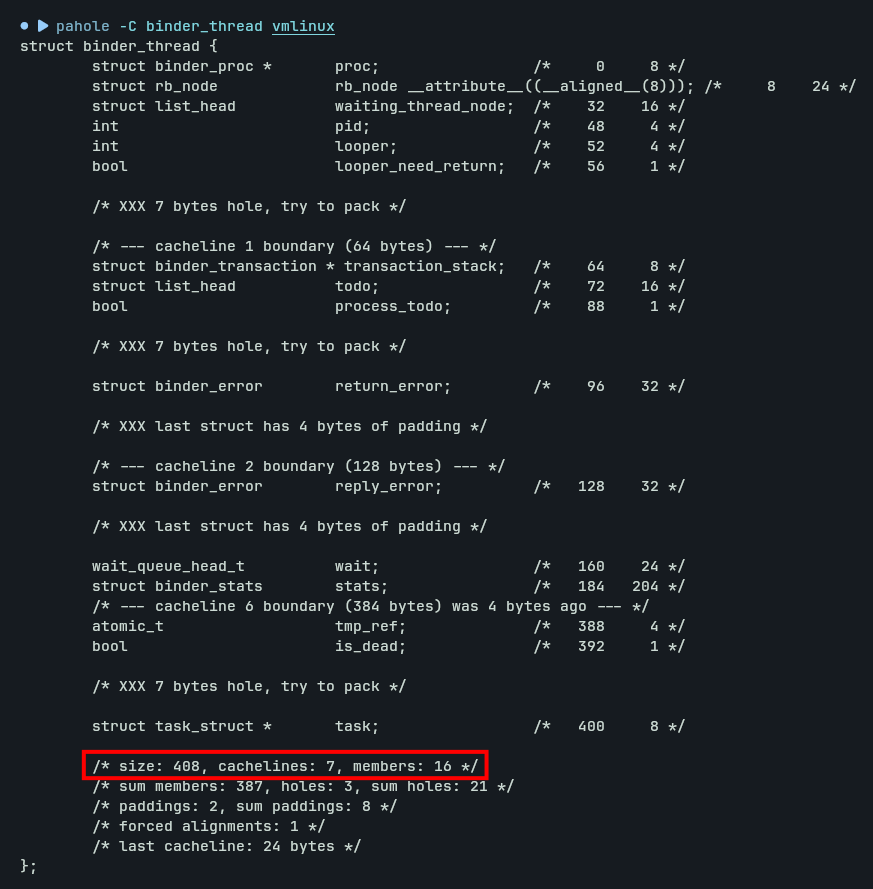 0xbinder/cve_2019_2215
Proof-of-concept LPE exploit for Android Binder UAF that uses iovec spraying and addr_limit overwrite to achieve arbitrary kernel read/write.
 lazybear8372/cve-2023-41898_lab
Walk through CVE-2023-41898: exploit an unvalidated deep link in Home Assistant Android to load arbitrary URLs in a privileged WebView and leak a…
 lazybear8372/cve-2023-31014_lab
Educational Android lab for CVE-2023-31014 implicit intent hijacking
 lazybear8372/cve-2020-23349_lab
Educational Android lab for CVE-2020-23349 in Sina Weibo SDK 4.2.7
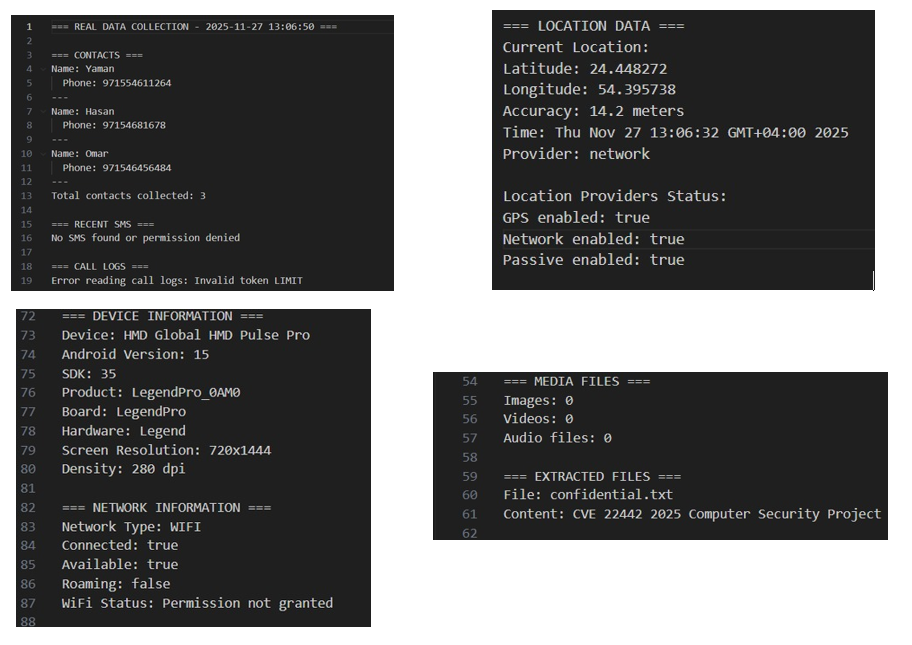 hasan-al-hussein/android-workprofile-exploit
Controlled defensive analysis of CVE-2025-22442 work-profile provisioning, policy timing, and enterprise isolation.
 mythicaltree/cve-2019-2215
Proof-of-concept exploit for CVE-2019-2215 (Bad Binder) targeting Android 10 x86_64 emulator. Designed for isolated kernel exploitation research and…
 qm4rs/cve-2026-0023-update-ownership-poc
Proof-of-concept demonstrating CVE-2026-0023, an Android Update Ownership trust bypass that suppresses the ownership warning during app updates.…
 bfurkanyildiz/android-rce-analizi
Android CVE-2024-0044, 43093, 23706 zafiyet analizi ve PoC lab ortamı
 ralireza/android-security-teryaagh
Android security guides, roadmap, docs, courses, write-ups, and teryaagh.
 vinh0212/cve-2024-23700
PoC for CVE-2024-23700, Android slient privilege escalation allow to read/write contacts, SMS, calendar, call log and voicemail, make outgoing calls…
 mobilehackinglab/cve-2026-0047-poc
CVE-2026-0047: Missing permission check in ActivityManagerService.dumpBitmapsProto() — steal UI bitmaps from every running app with zero permissions…
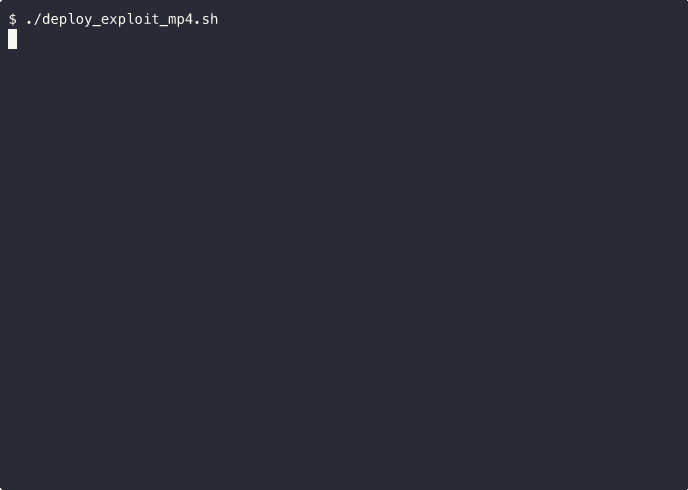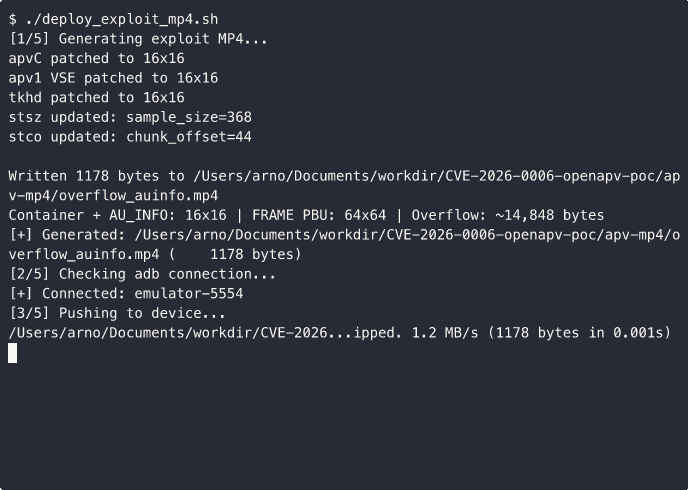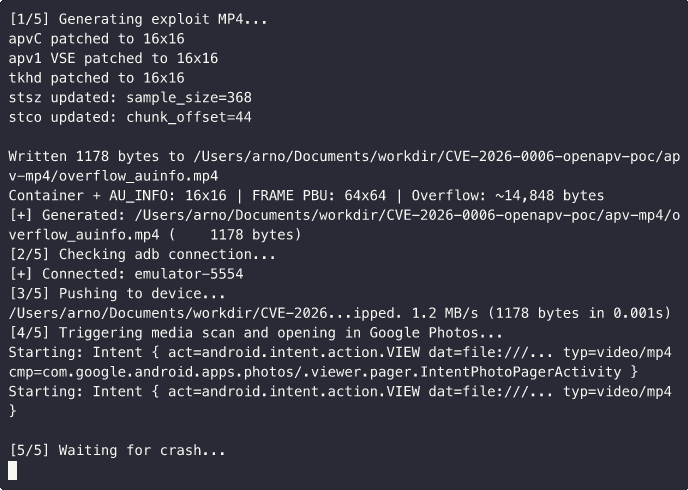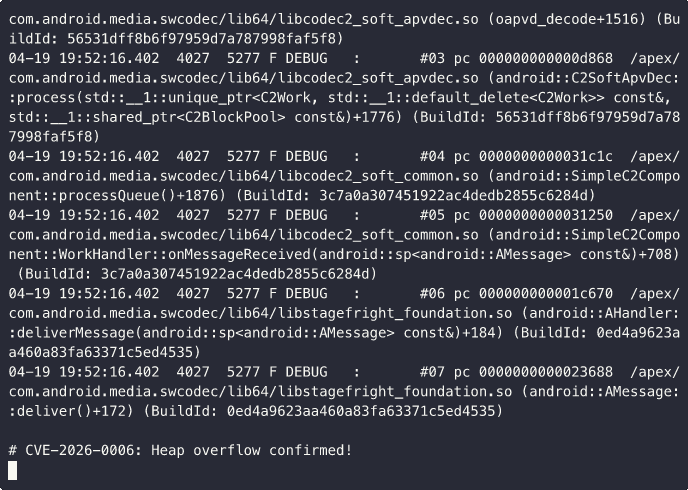 mobilehackinglab/cve-2026-0006-openapv-poc
CVE-2026-0006: Heap buffer overflow PoC for libopenapv (Android APV codec) - CVSS 9.8
 gitamans/zygoteexploitdemo
Educational demonstration of CVE-2024-31317 Zygote Injection Vulnerability on Android