
digital-forensics-lab
 frankwxu/digital-forensics-lab
Free hands-on digital forensics labs for students and faculty
ai-securityctfdigital-forensics+9
3.0k
frankwxu/digital-forensics-labFree hands-on digital forensics labs for students and faculty
 owasp/wrongsecrets-binaries
Source code for the Binaries of OWASP WrongSecrets
 the-art-of-hacking/h4cker
Curated collection of cybersecurity resources, labs, and training materials covering ethical hacking, penetration testing, exploit development,…
 owasp/railsgoat
A vulnerable version of Rails that follows the OWASP Top 10
 abiral-timalsina/cyber-defenders-lab-
My write-ups from CyberDefenders' Blue Team labs, solved using Wireshark. Covers TeamCity RCE (CVE-2024-27198), XSS session hijacking, and…
 alzeaty1/security-writeups
CTF writeups and teaching scripts for web security, bug bounty techniques, and network forensics, with blank-value versions for active practice.
 hamed233/cybersecurity-mastery-roadmap
A comprehensive, step-by-step guide to mastering cybersecurity from beginner to expert level with curated resources, tools, and career guidance
 lazarus0x1337/cve-2026-25632
CVE-2026-25632 — Fix Unsafe JSON Deserialization Leading to Remote Code Execution
 iqx6889/cve-2026-52813-gogs-rce
CVE-2026-52813 (Gogs Path Traversal → Git Hooks RCE) defensive writeup: root-cause & patch analysis, Sigma/SIEM detection rules, IOCs, non-intrusive…
 47cid/wp2shell-lab
Educational PoC + lab for CVE-2026-63030 + CVE-2026-60137: pre-auth SQLi in WordPress core via REST batch-route confusion
 nicholasc03/dns-poisoning-triage-lab
Forensic triage of DNS cache poisoning in legacy hardware. Includes PCAP analysis of 839-byte unsolicited record injections, CVE-2025-40778 mapping,…
 kkaanozturk/hyperos-directory-traversal-analysis
Xiaomi HyperOS AVCodec Medya Framework'ündeki Use-After-Free (CVE-2025-21082) Zafiyetinin Derinlemesine Analizi, Rust Simülasyonu ve İnteraktif Web…
 bilalalshiekh912/incident-response-report-teamcity-compromise-cve-2024-27198-
CyberDefenders JetBrains Lab
 jhatchi/nexacorp-dfir-inc-2026-001
DFIR investigation + 7 Suricata rules on a simulated NexaCorp intrusion (vsftpd 2.3.4 CVE-2011-2523 + MITRE Caldera C2). 4-day solo engagement…
 sentinelxofficial/cve-2026-44963
Detection scripts, patch checker & hardening guide for CVE-2026-44963 (Veeam B&R RCE)
 stevehenderson/lab_xz_backdoor
Some labs looking at the xz backdoor vulnerability (CVE-2024-3094)
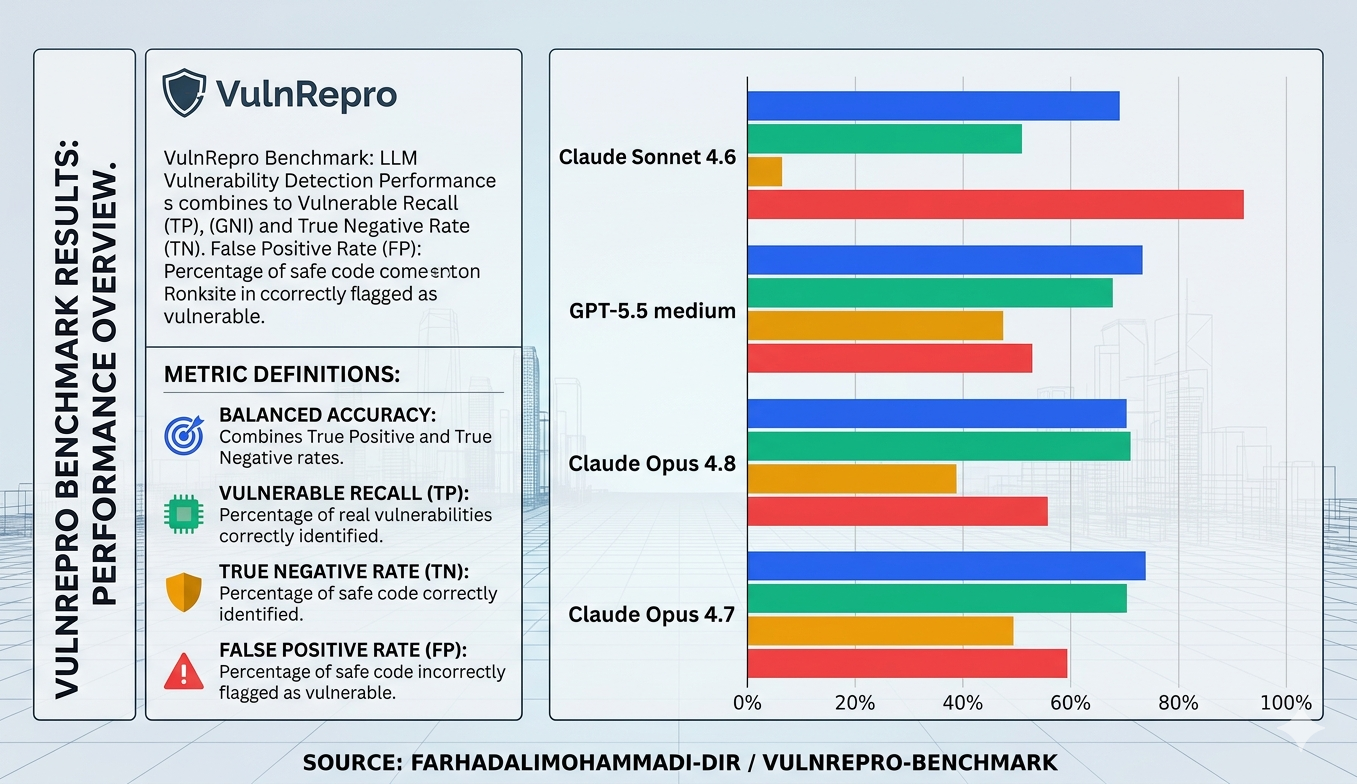 farhadalimohammadi-dir/vulnrepro-benchmark
Benchmark measuring AI models' ability to detect vulnerabilities in source code via real bug bounty cases with balanced recall and false-positive…
 renewablehacking/cve-2020-7598
Educational lab demonstrating CVE-2020-7598 prototype pollution in minimist with a vulnerable Node.js/Express app, exploit payload, and…